arkime
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
defensive-toolsdigital-forensicsforensics+7
arkime/arkimeArkime is an open source, large scale, full packet capturing, indexing, and database system.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 guelfoweb/peframe
PEframe is a open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.
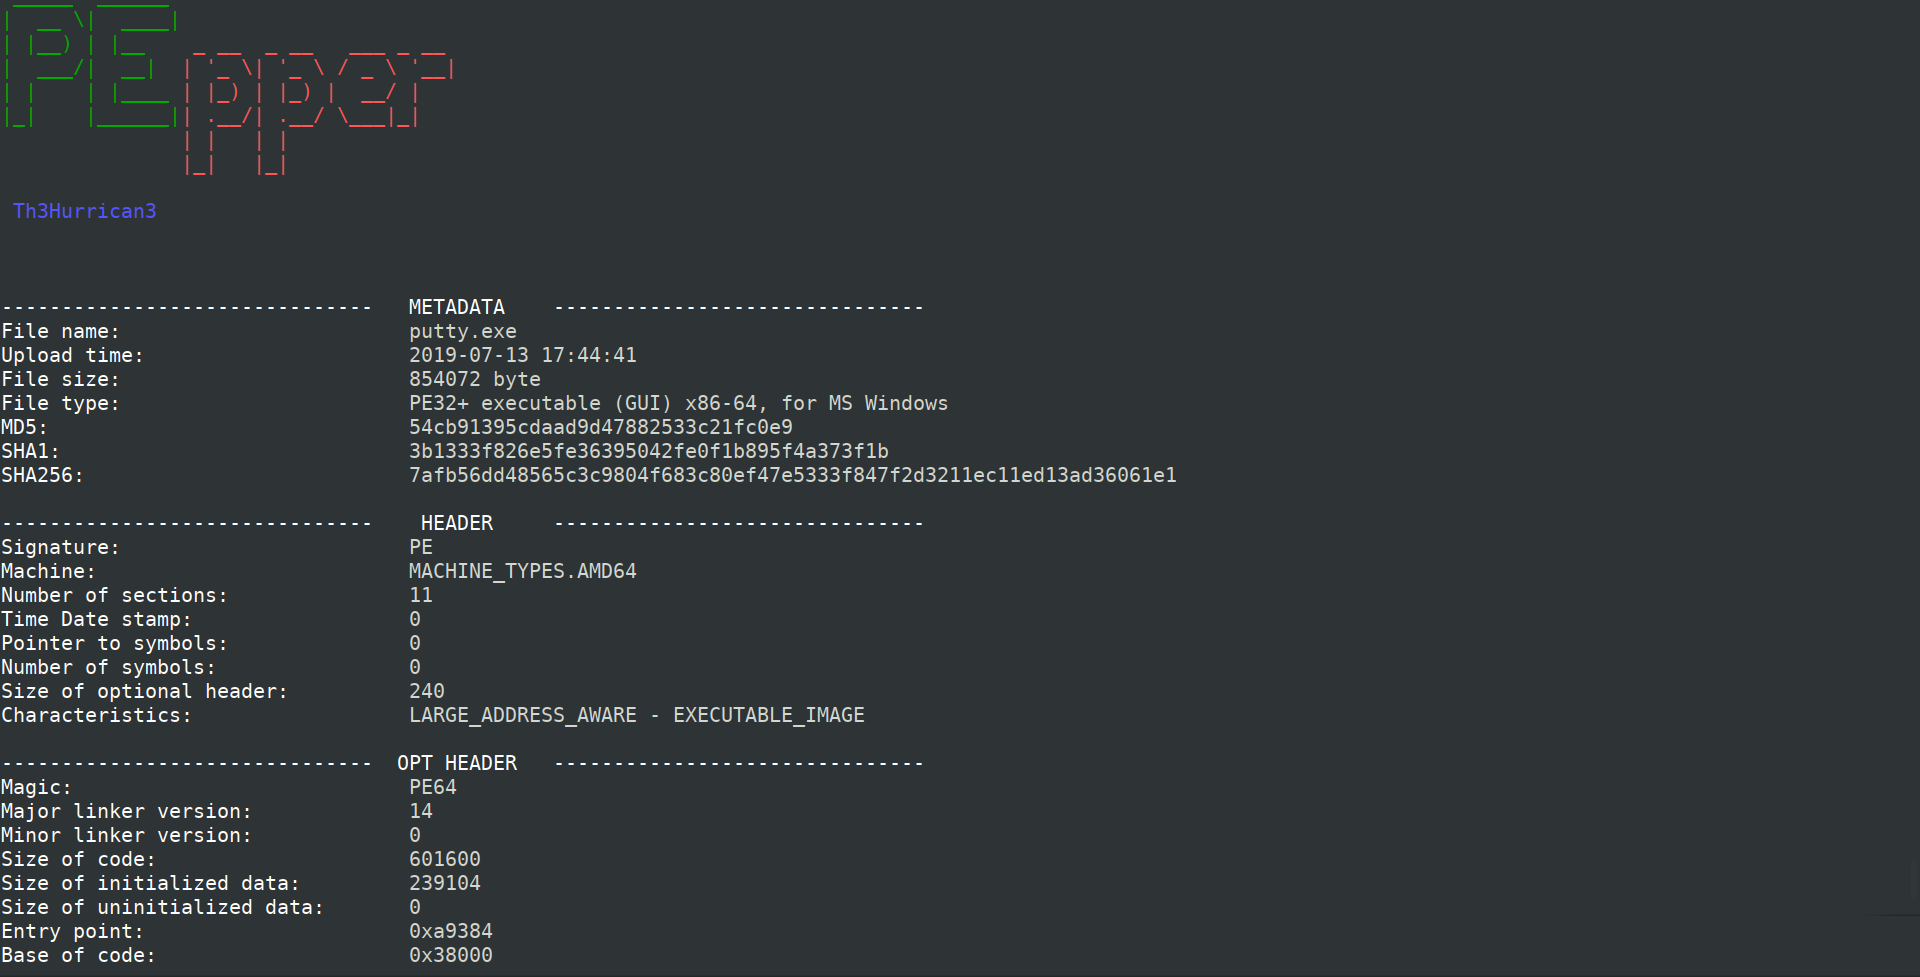 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable
 marcrowproject/bramble
Bramble is a hacking Open source suite.
 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 nowsecure/android-forensics
Open source Android Forensics app and framework
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 rshipp/awesome-malware-analysis
Defund the Police.
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
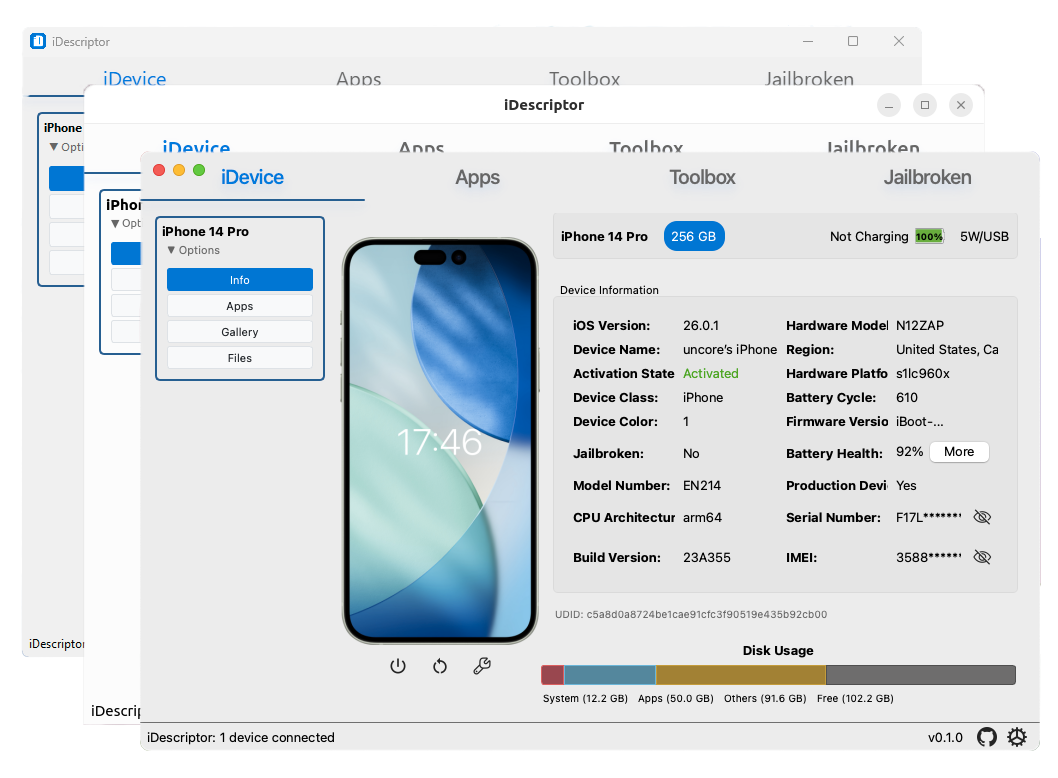 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…