

PAGASUS-PRO
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
android-securitydata-exfiltrationeducation+8
534
thakur2309/pagasus-proPython ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
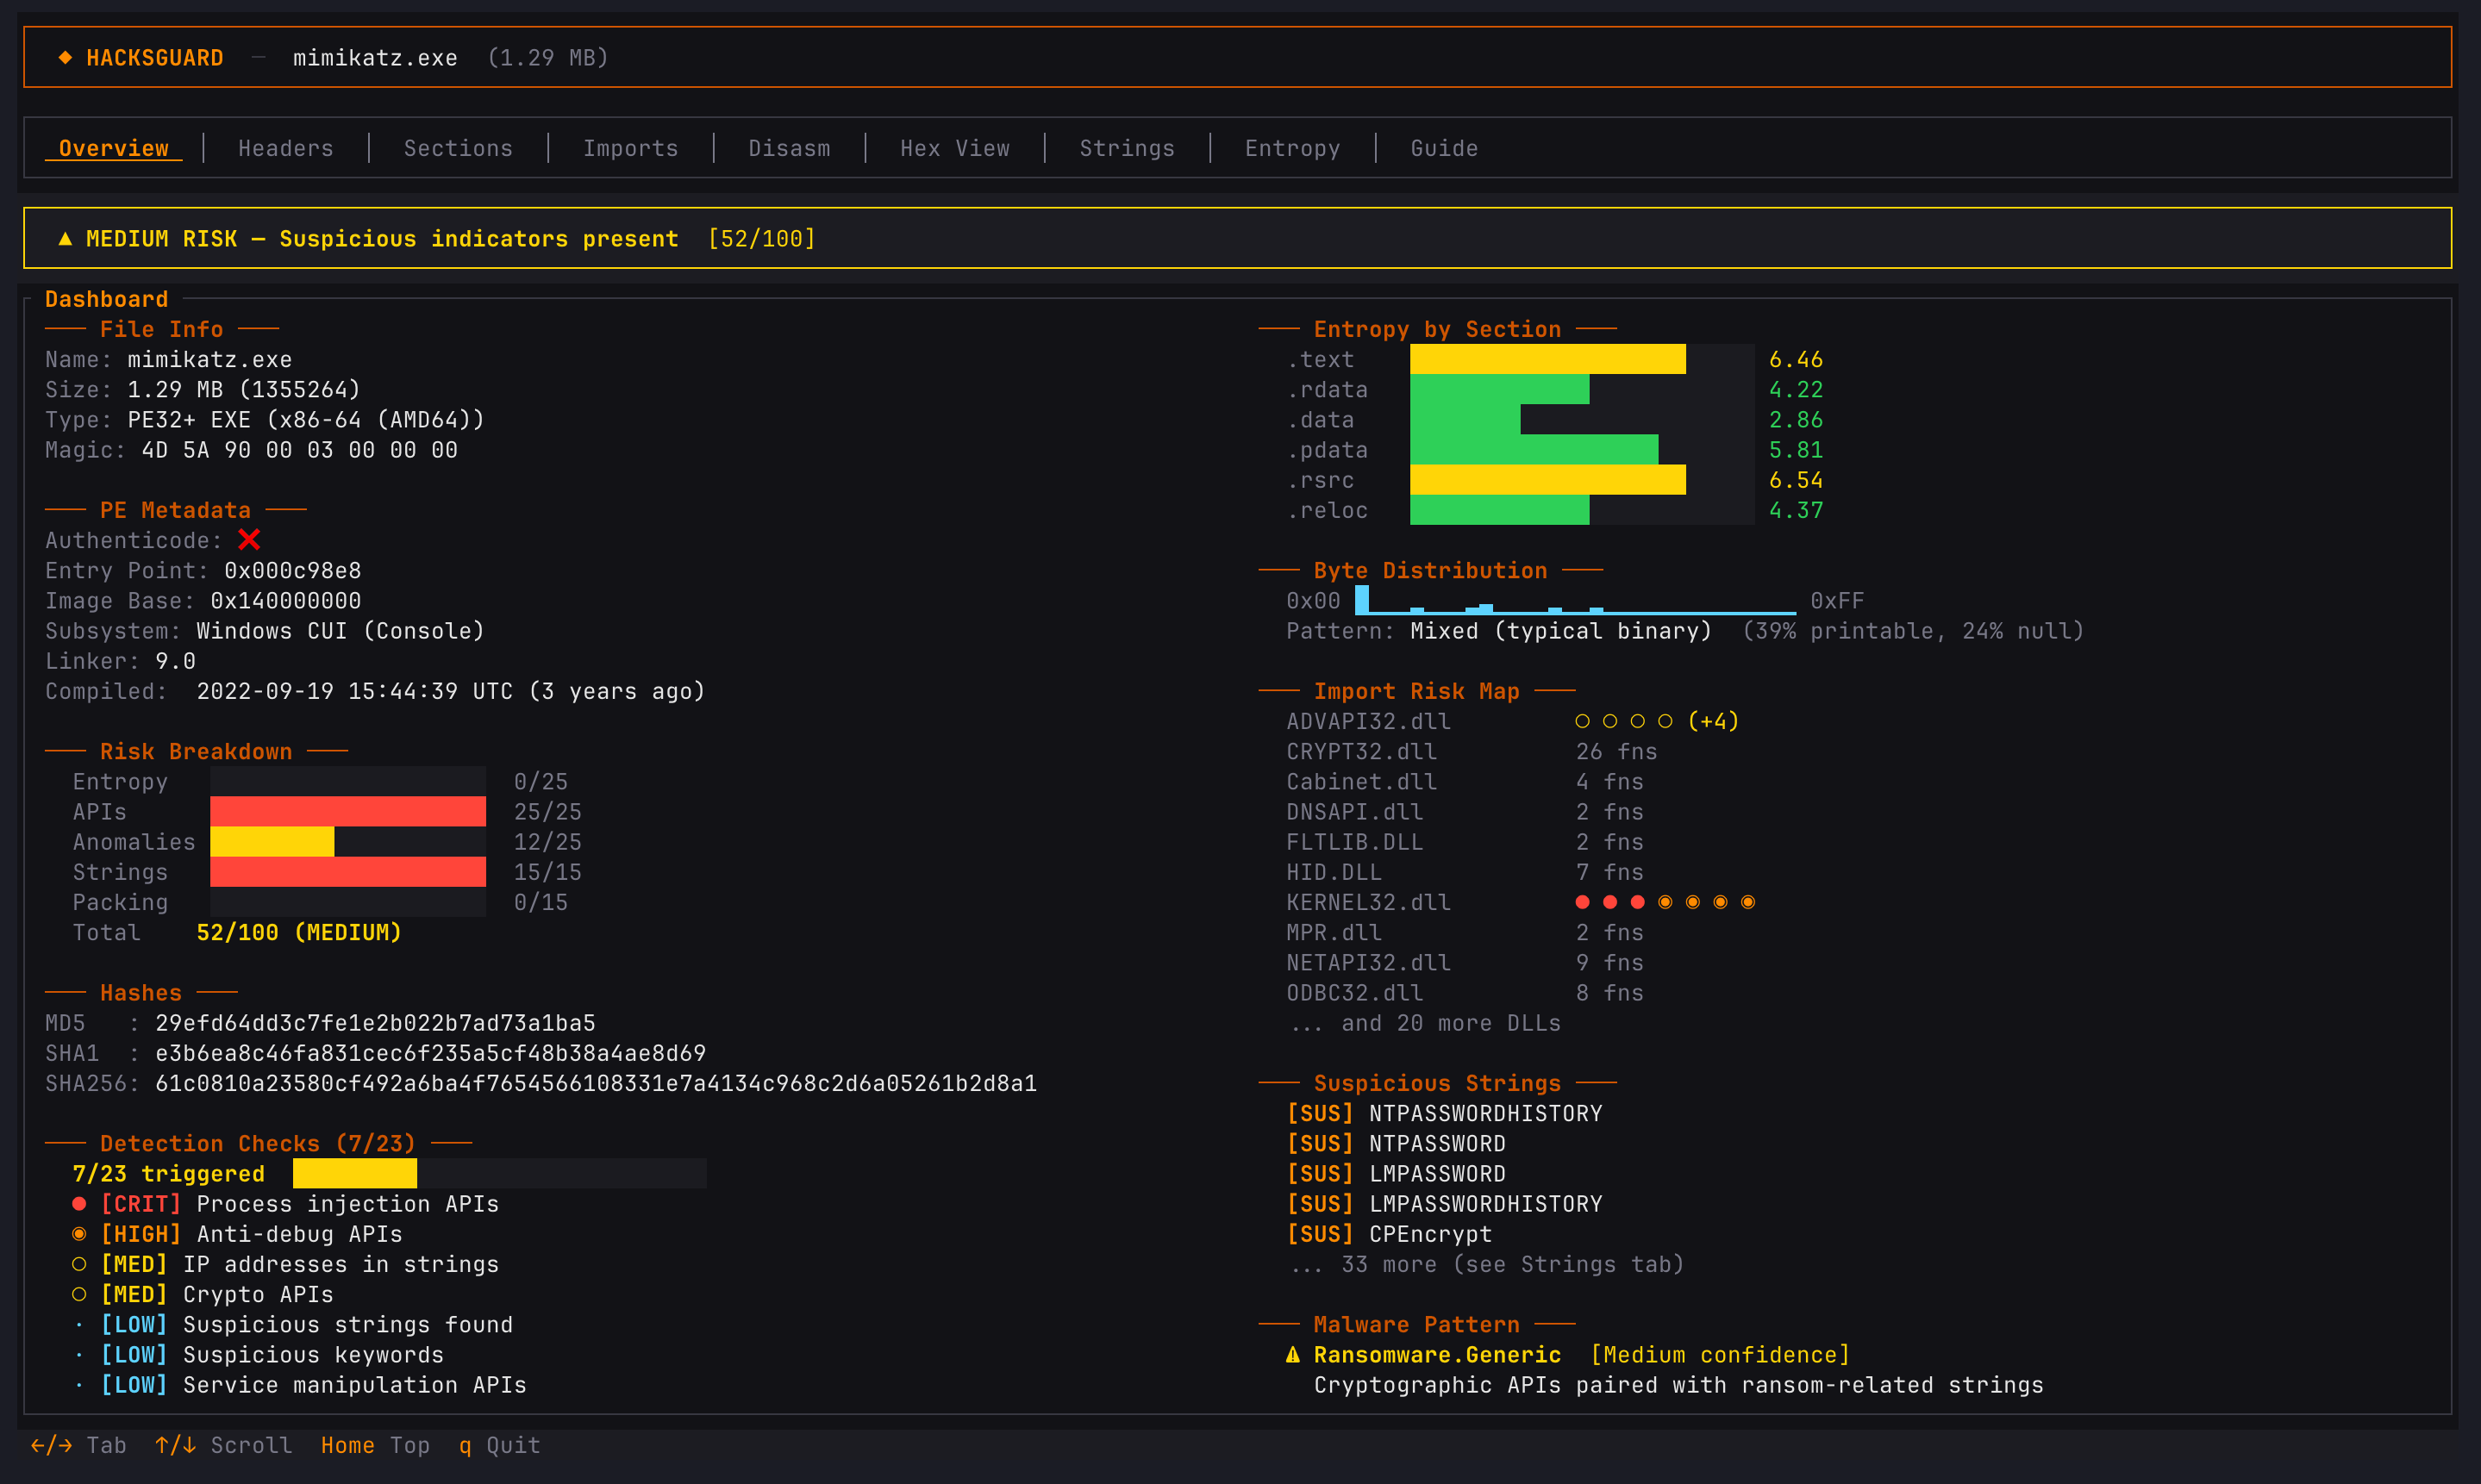 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 aquasecurity/tracee
Linux Runtime Security and Forensics using eBPF
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 target/strelka
Real-time, container-based file scanning at enterprise scale
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 loresuso/psc
the ps utility, with an eBPF twist and container context
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…