radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
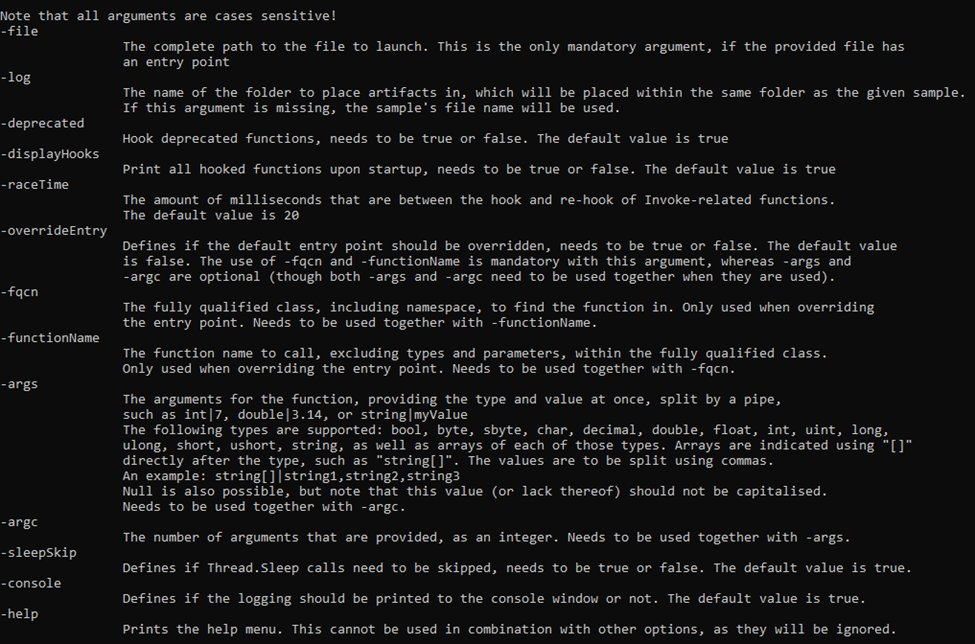 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 donctl/sandy
Release of the sandy framework.
 volatilityfoundation/volatility
An advanced memory forensics framework
 nowsecure/android-forensics
Open source Android Forensics app and framework
 viper-framework/viper
Binary analysis and management framework
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.