

Remote-Access-Trojan-Database
 rainkin1993/remote-access-trojan-database
A database of RAT collected from Internet
curated-resourceseducationforensics+3
161
rainkin1993/remote-access-trojan-databaseA database of RAT collected from Internet
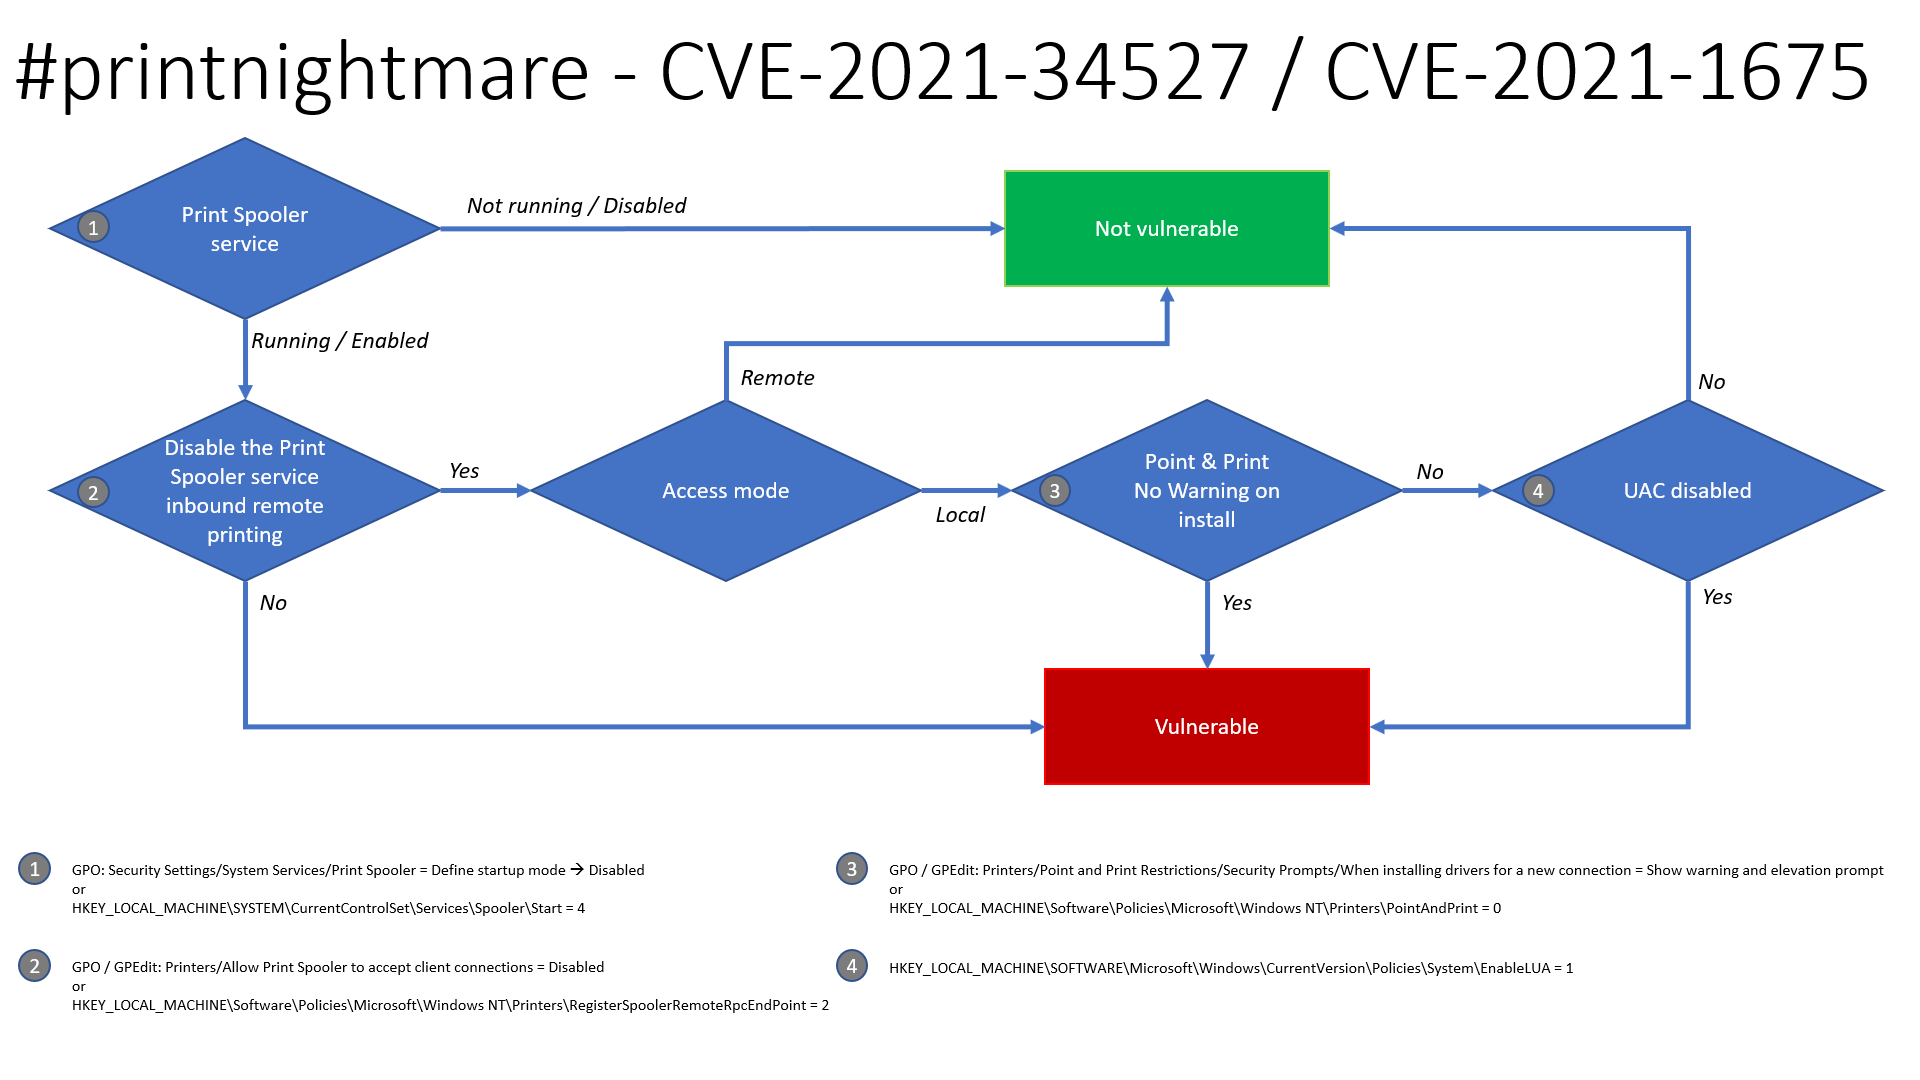 laresllc/cve-2021-1675
CVE-2021-1675 Detection Info
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781
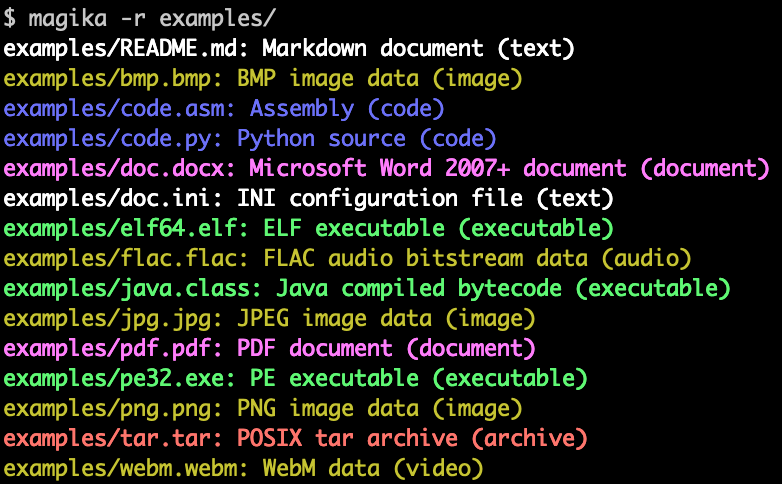 google/magika
Fast and accurate AI powered file content types detection
 cisagov/check-your-pulse
This utility can help determine if indicators of compromise (IOCs) exist in the log files of a Pulse Secure VPN Appliance for CVE-2019-11510.
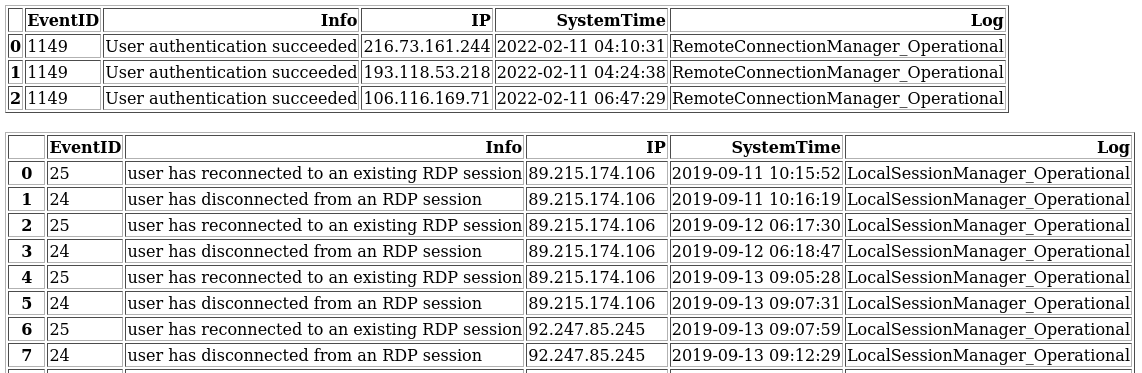 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.

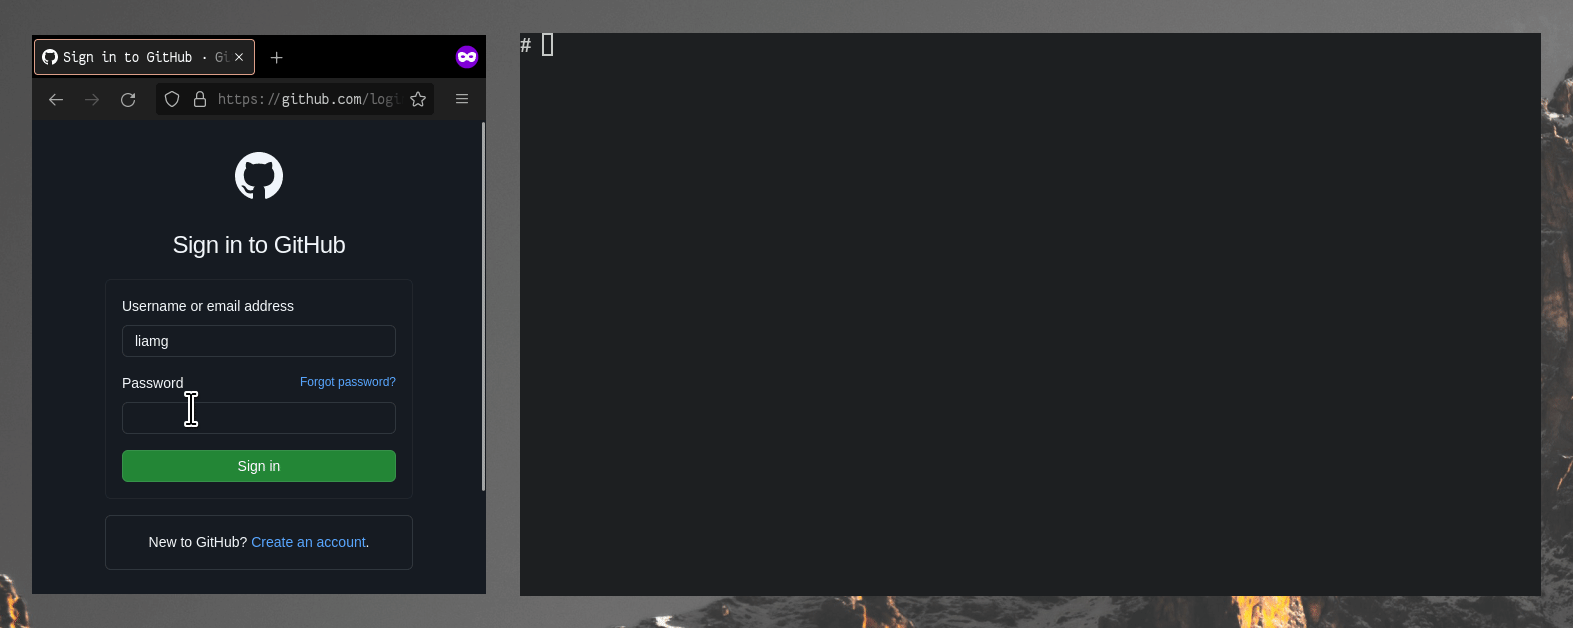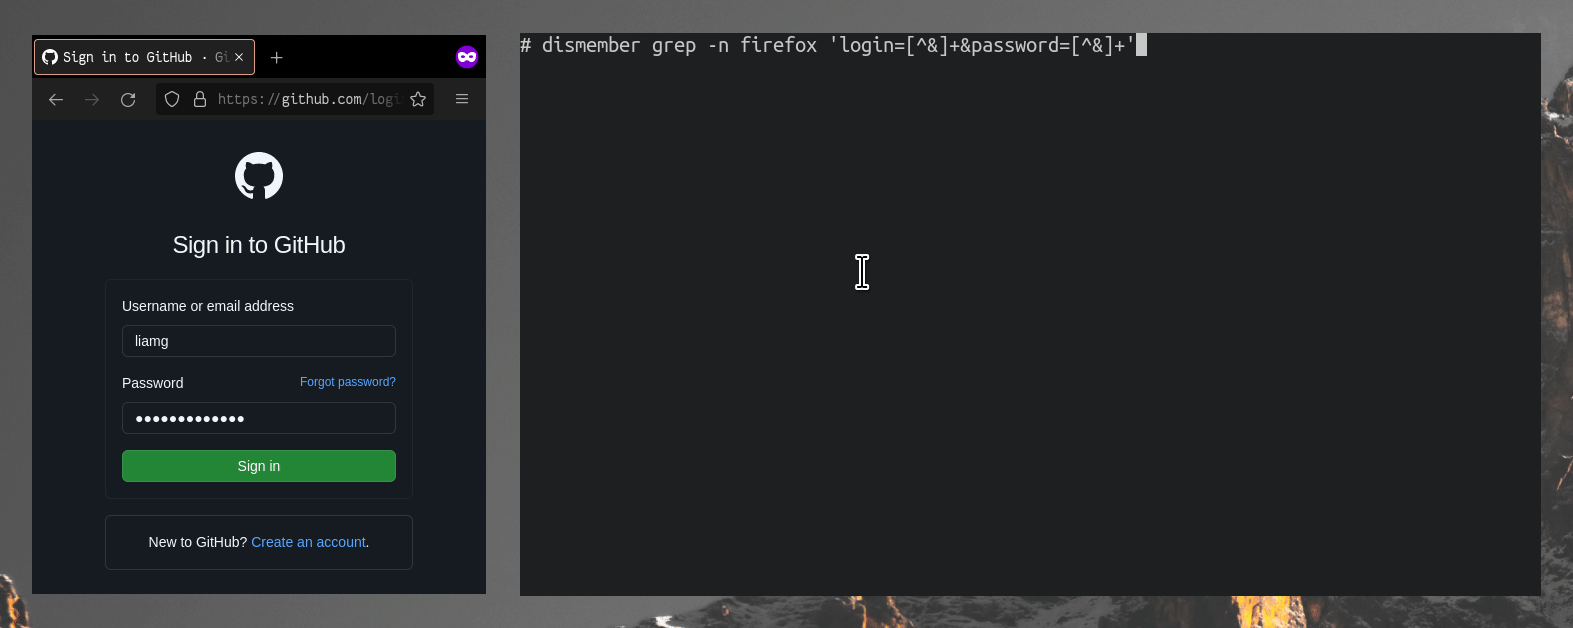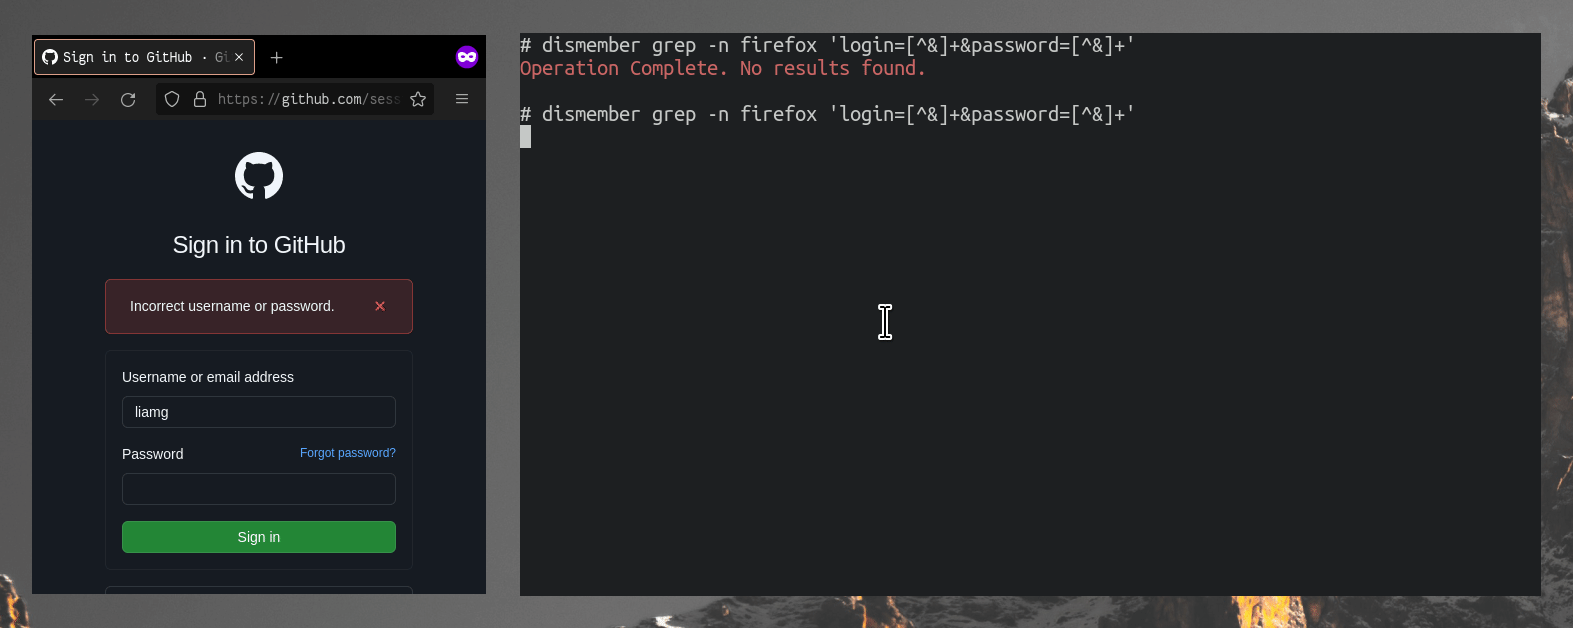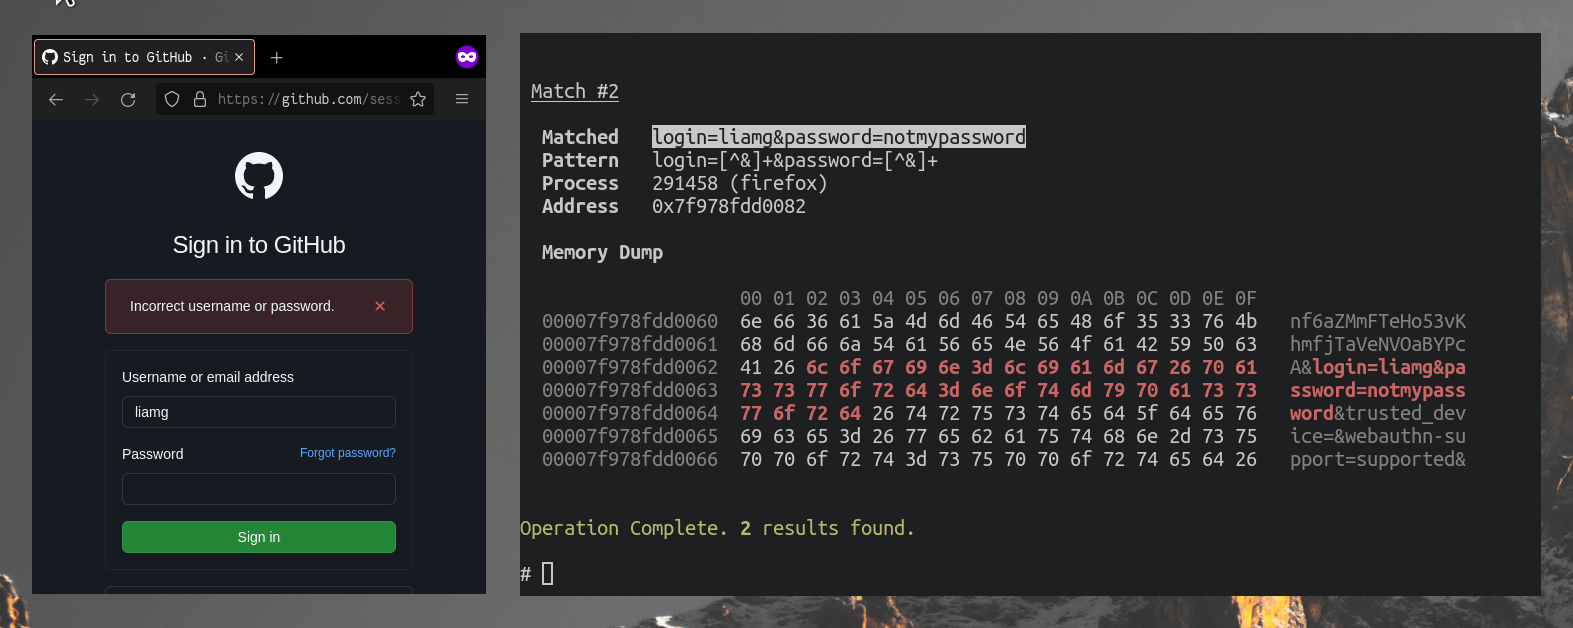 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
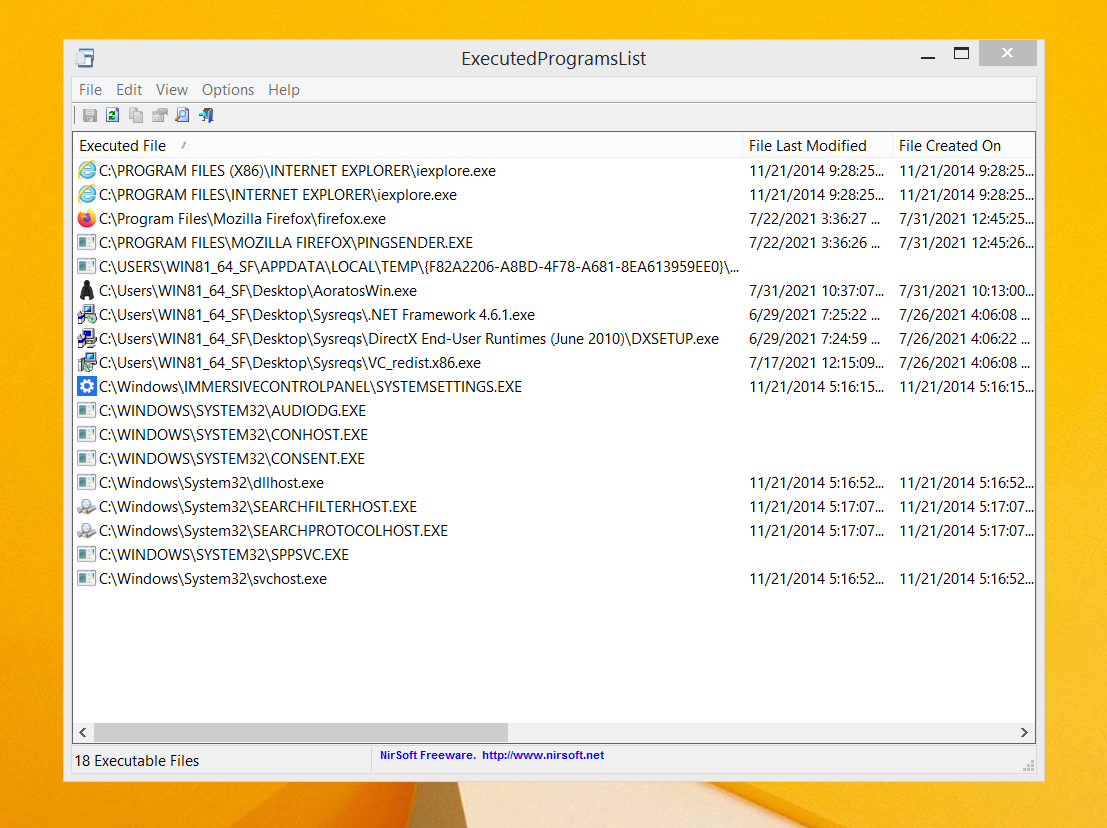 pinoywh1z/aoratoswin
A tool that removes traces of executed applications on Windows OS.
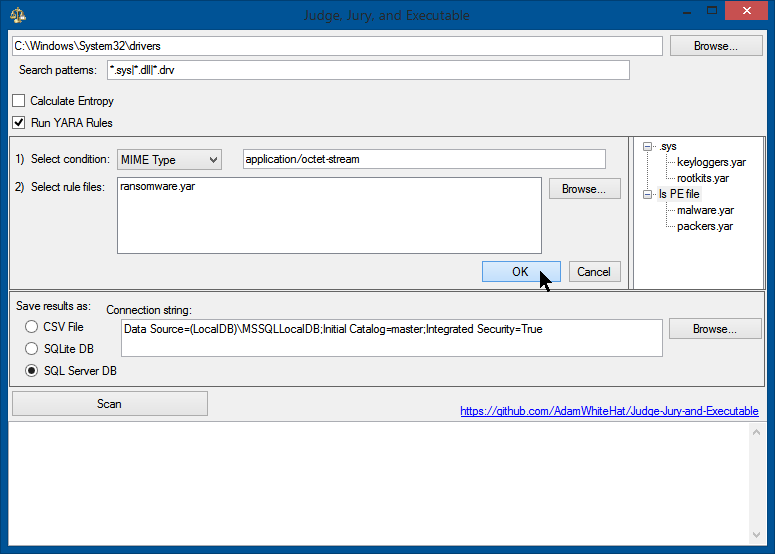 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
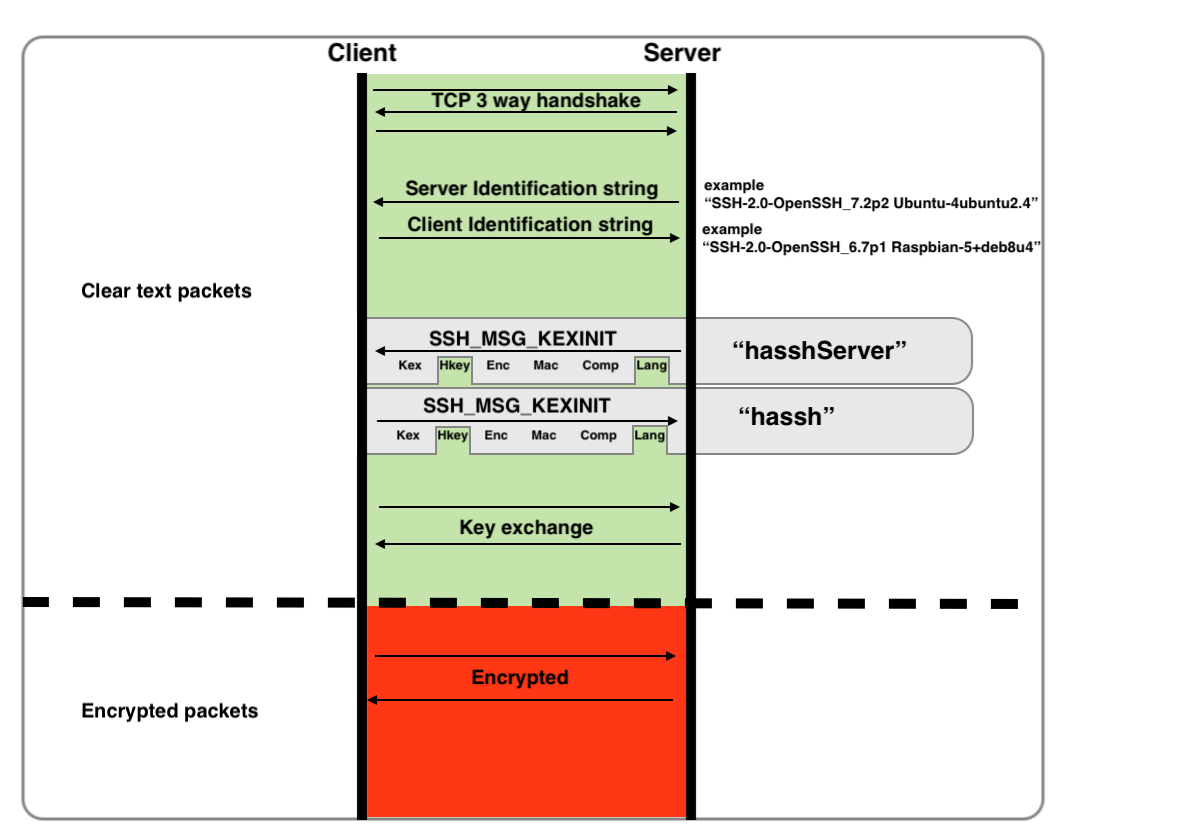 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
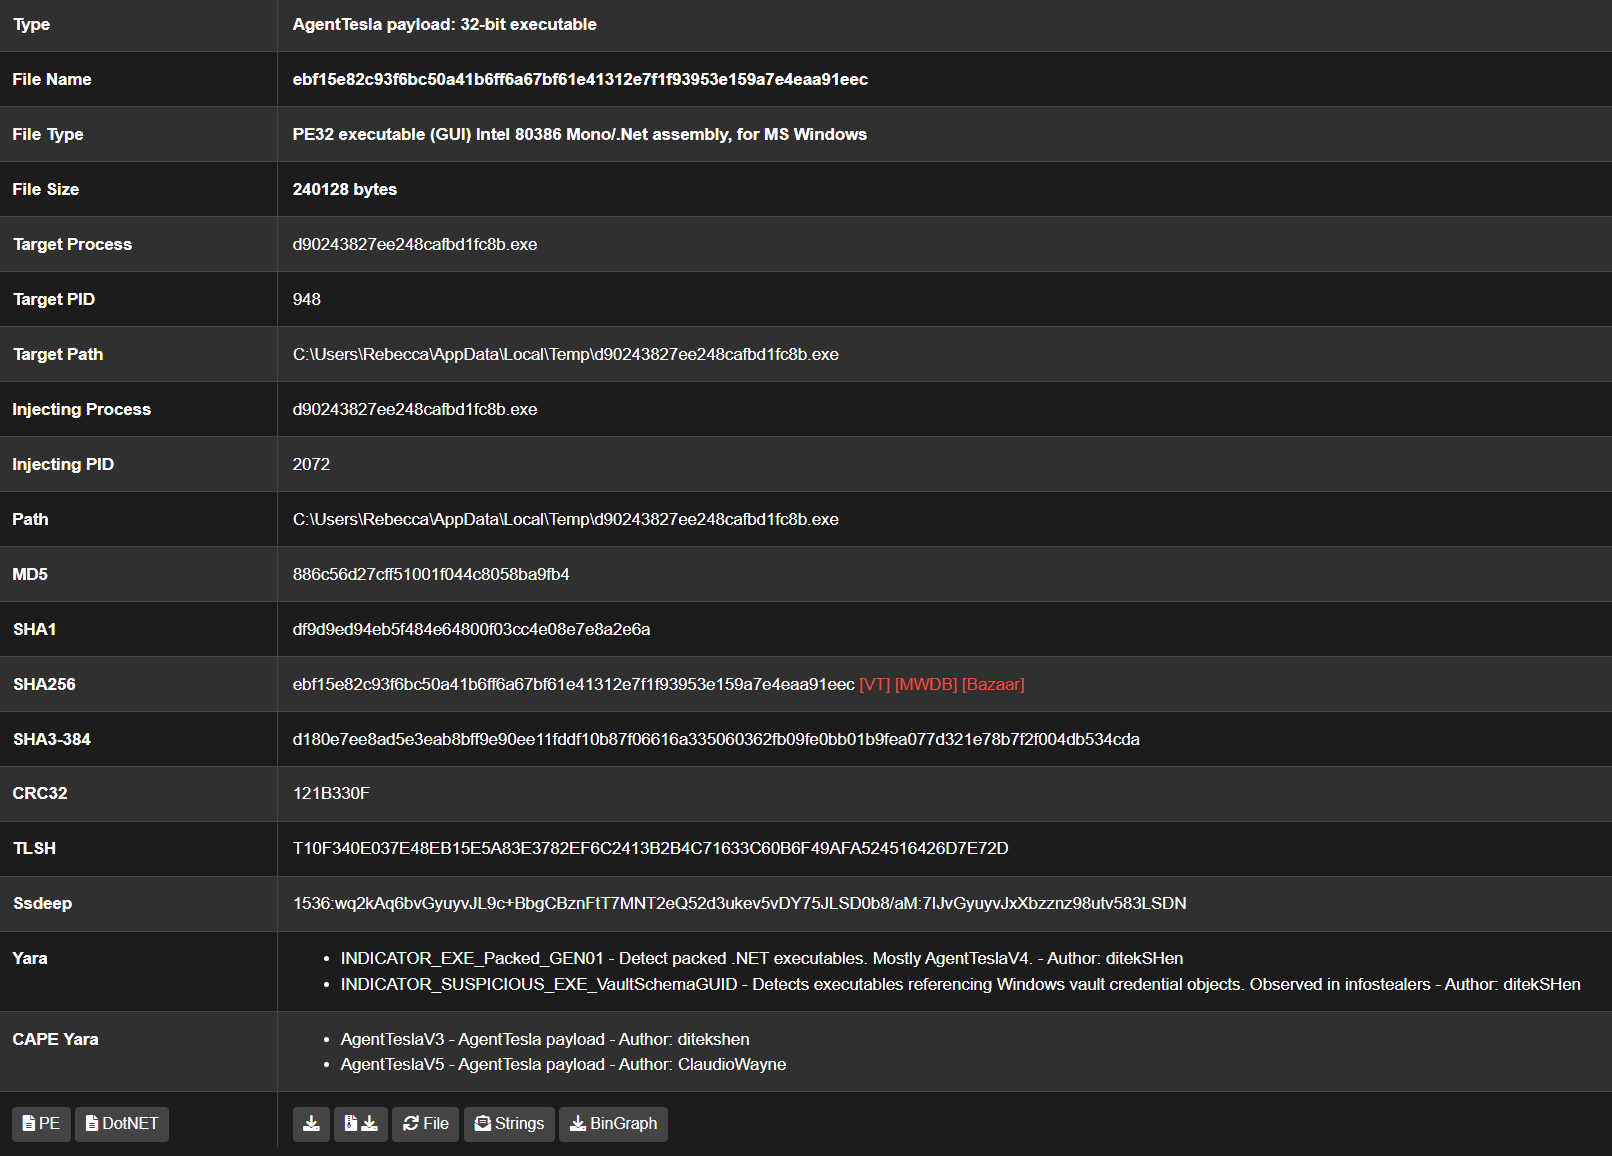 kevoreilly/capev2
Malware Configuration And Payload Extraction
 anjai7/tryhack3m-bricks-heist
TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.