
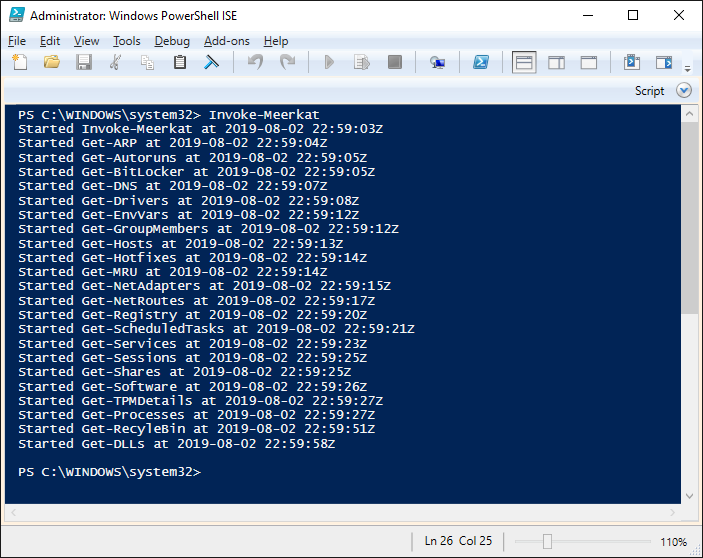
Meerkat
 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
digital-forensicsforensicsincident-response+2
4831 year ago
tonyphipps/meerkatA collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 gmh5225/malwaredb
Curated collection of 961 malware families (1.36 GB) in password-protected ZIP archives, organized by family and type for analysis and research.
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 deadbits/yara-rules
Collection of YARA signatures from individual research
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
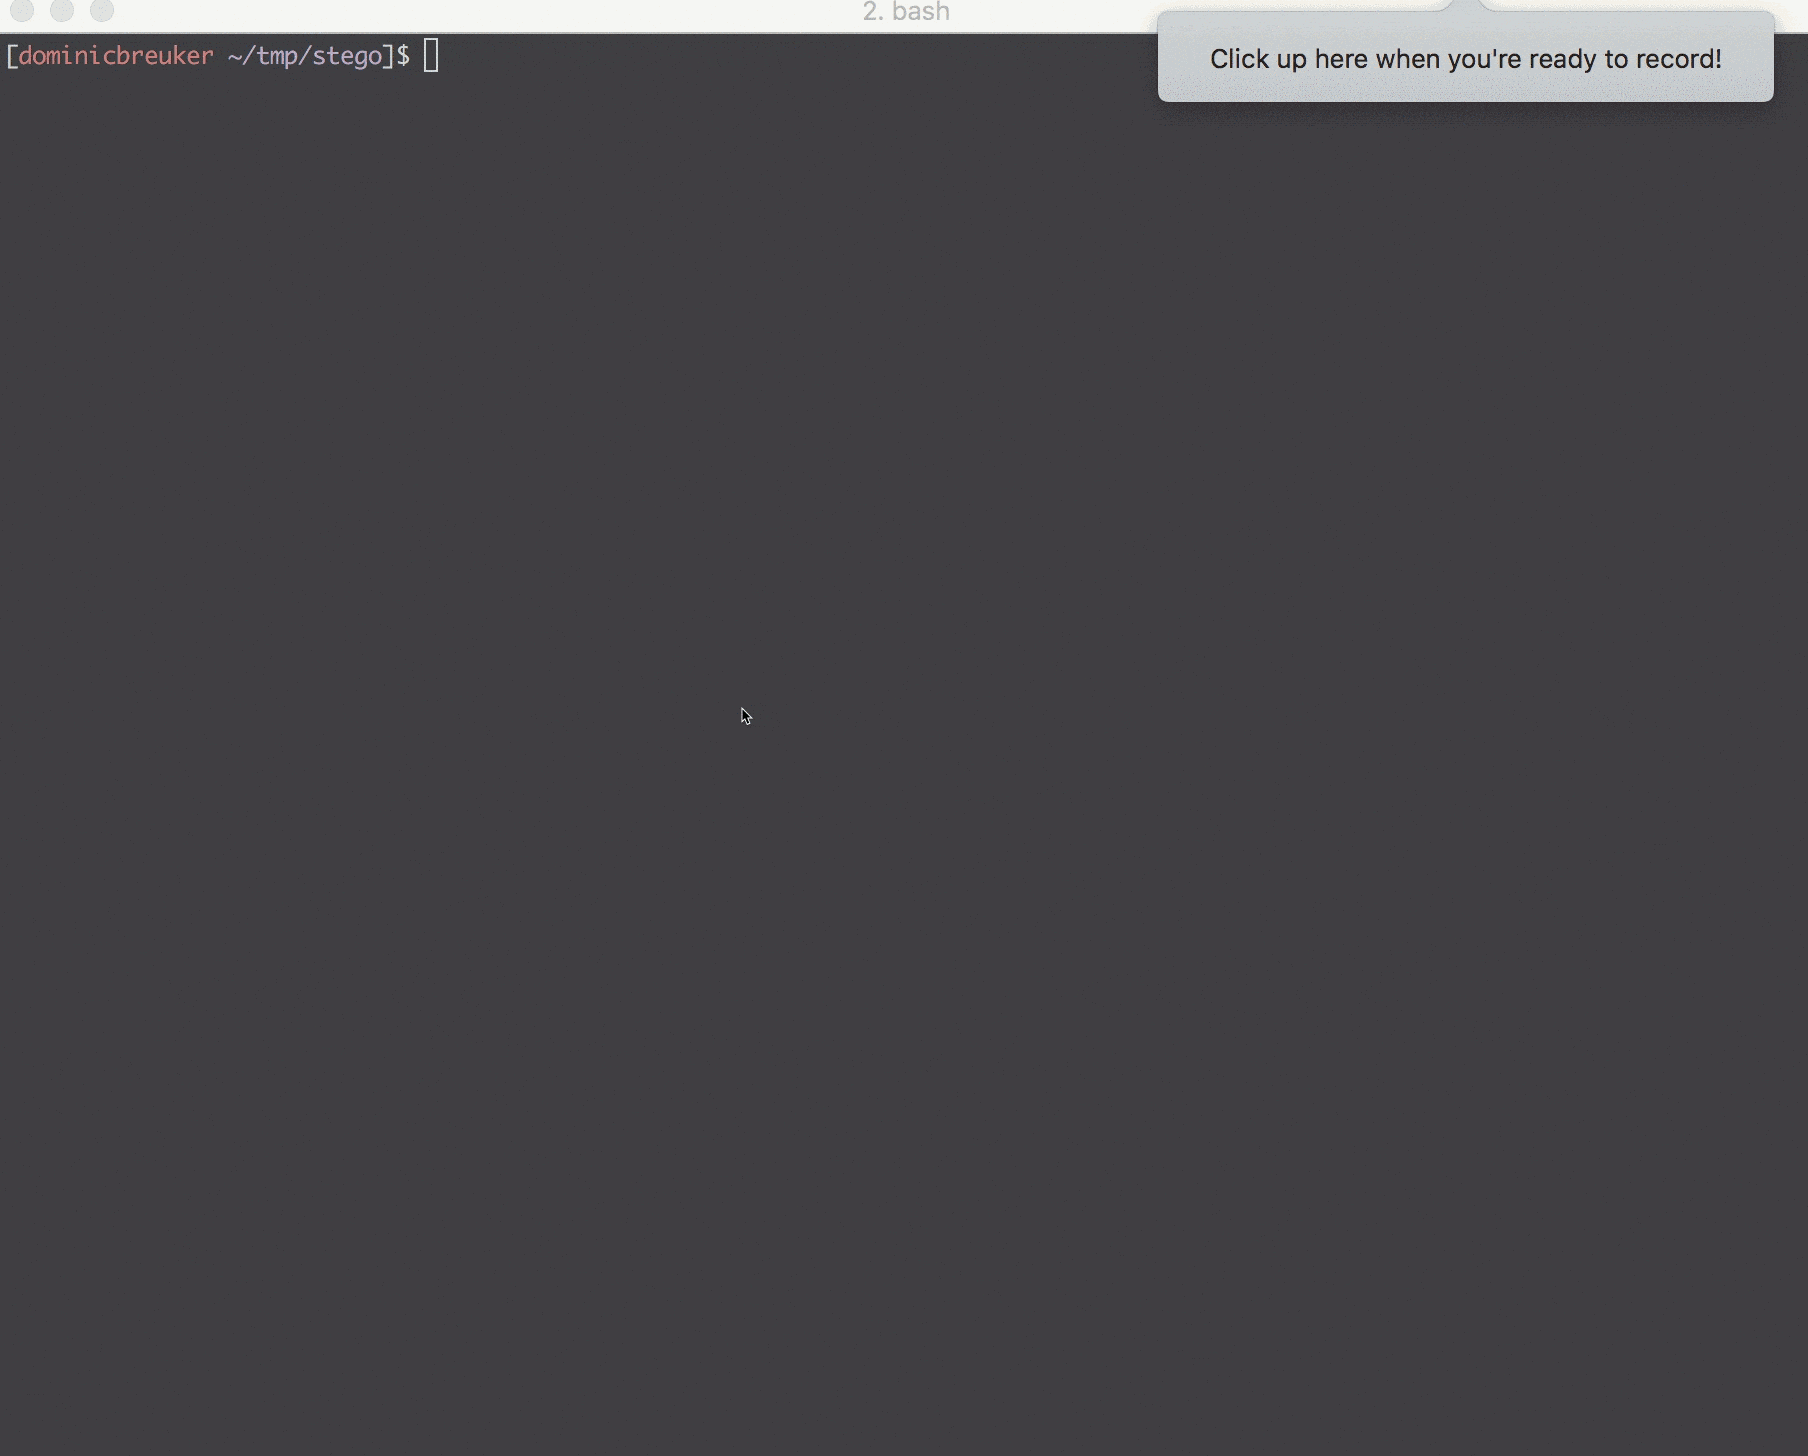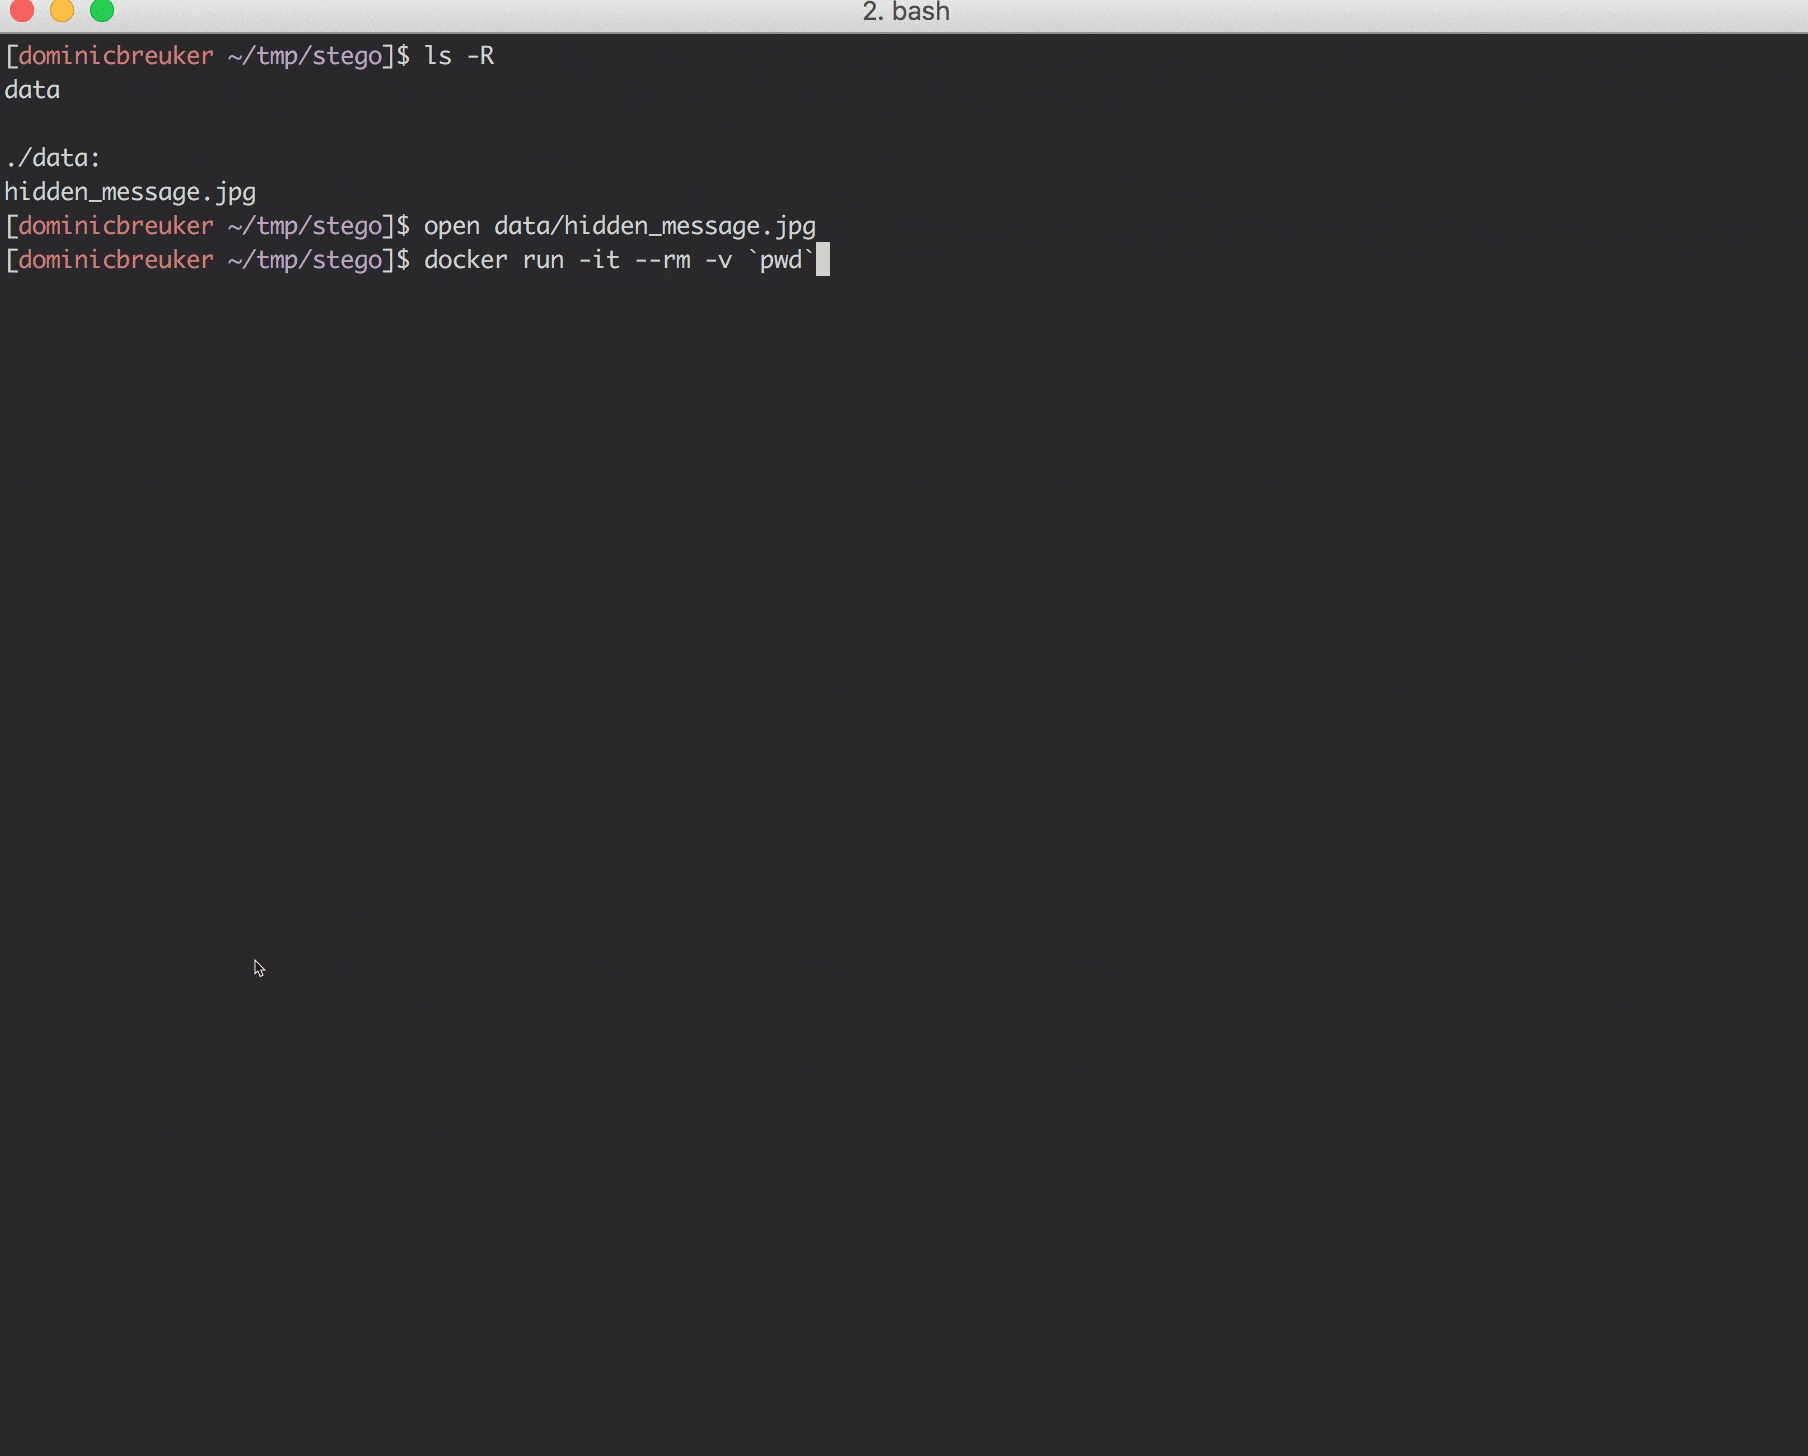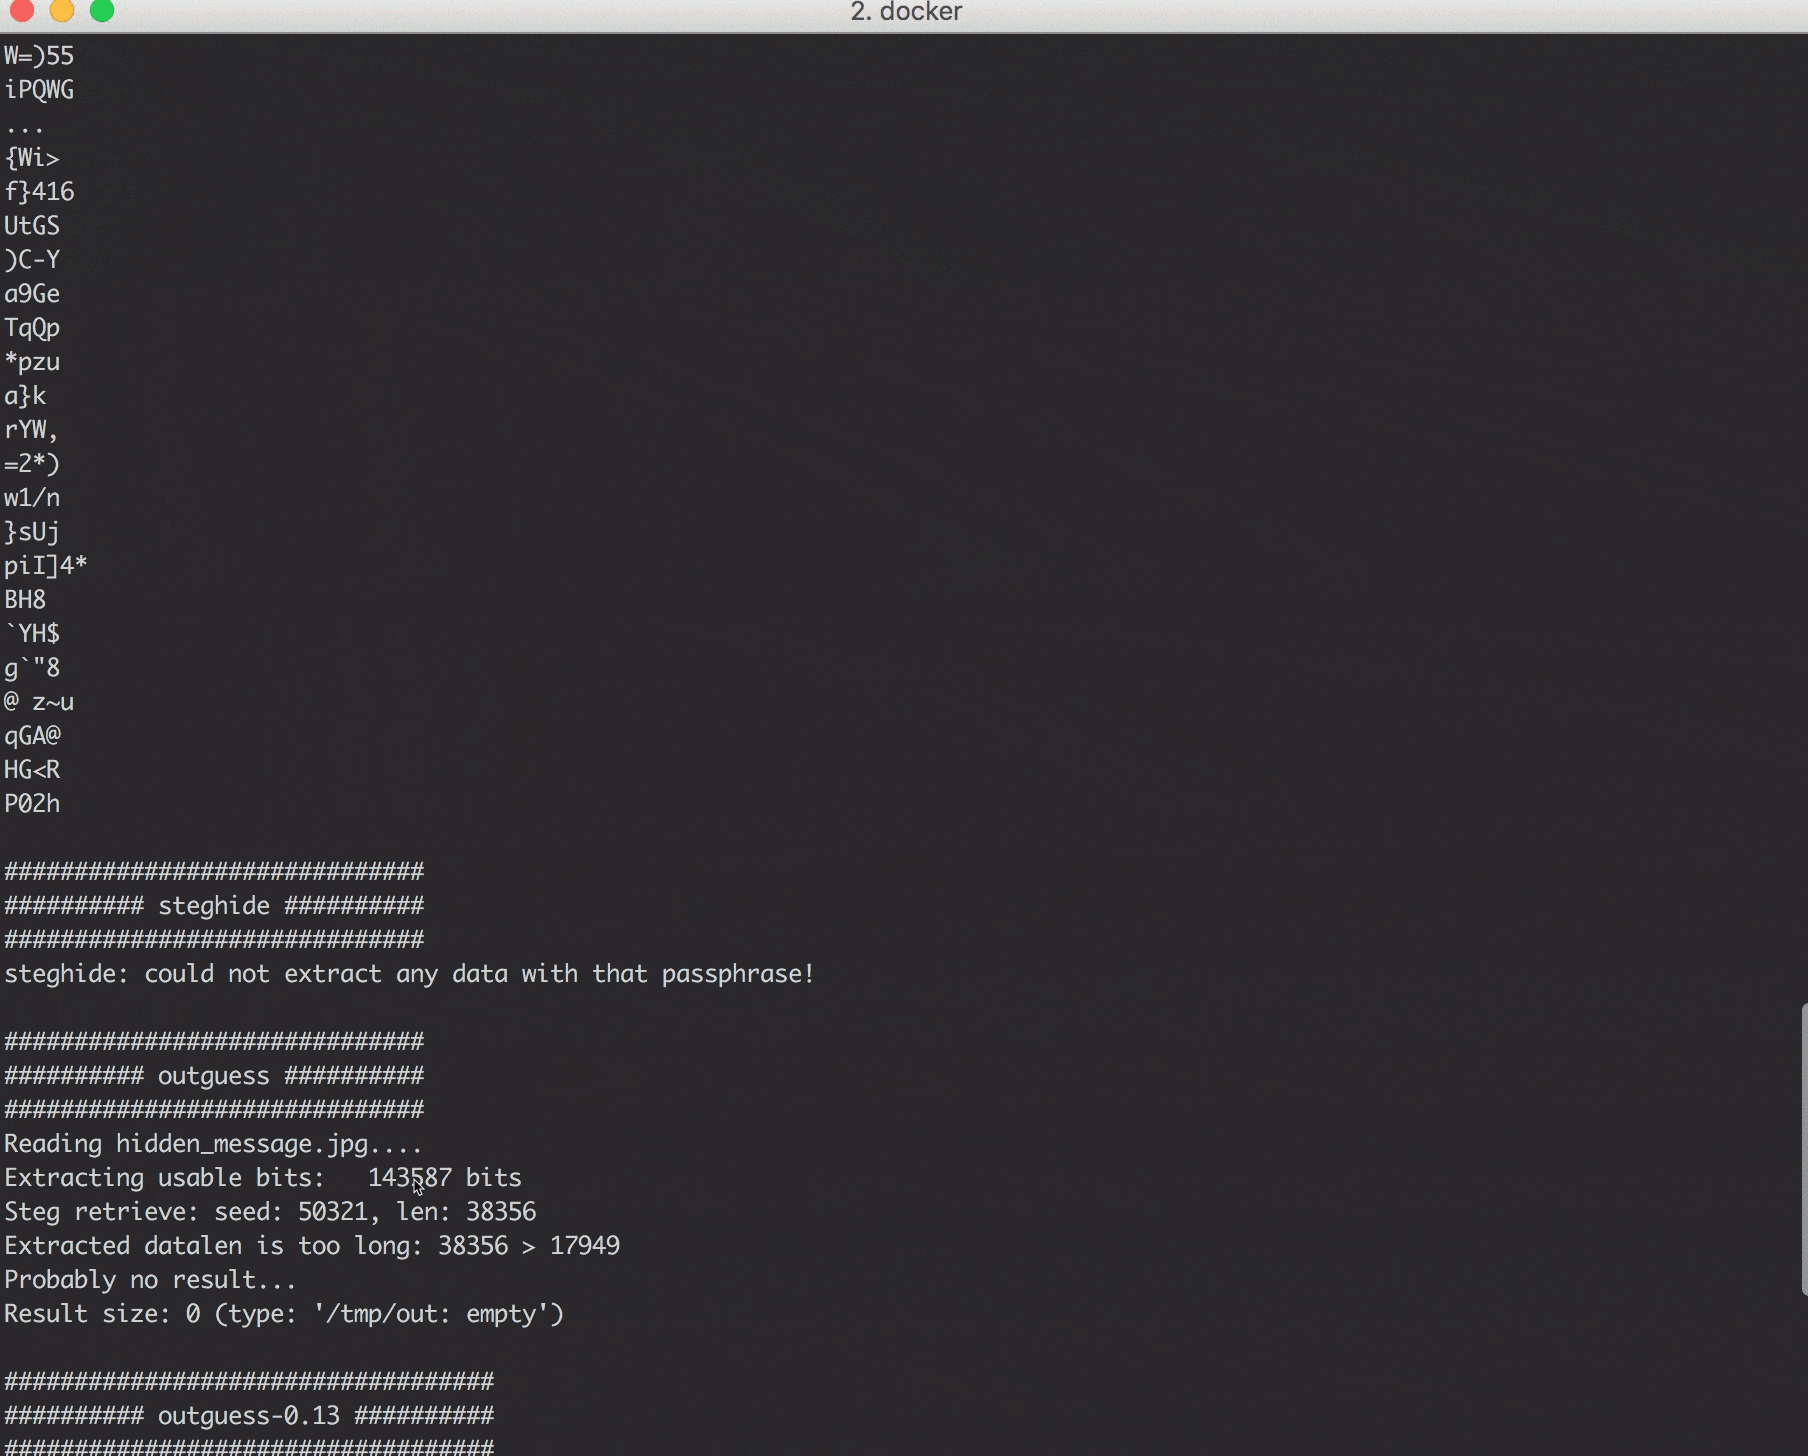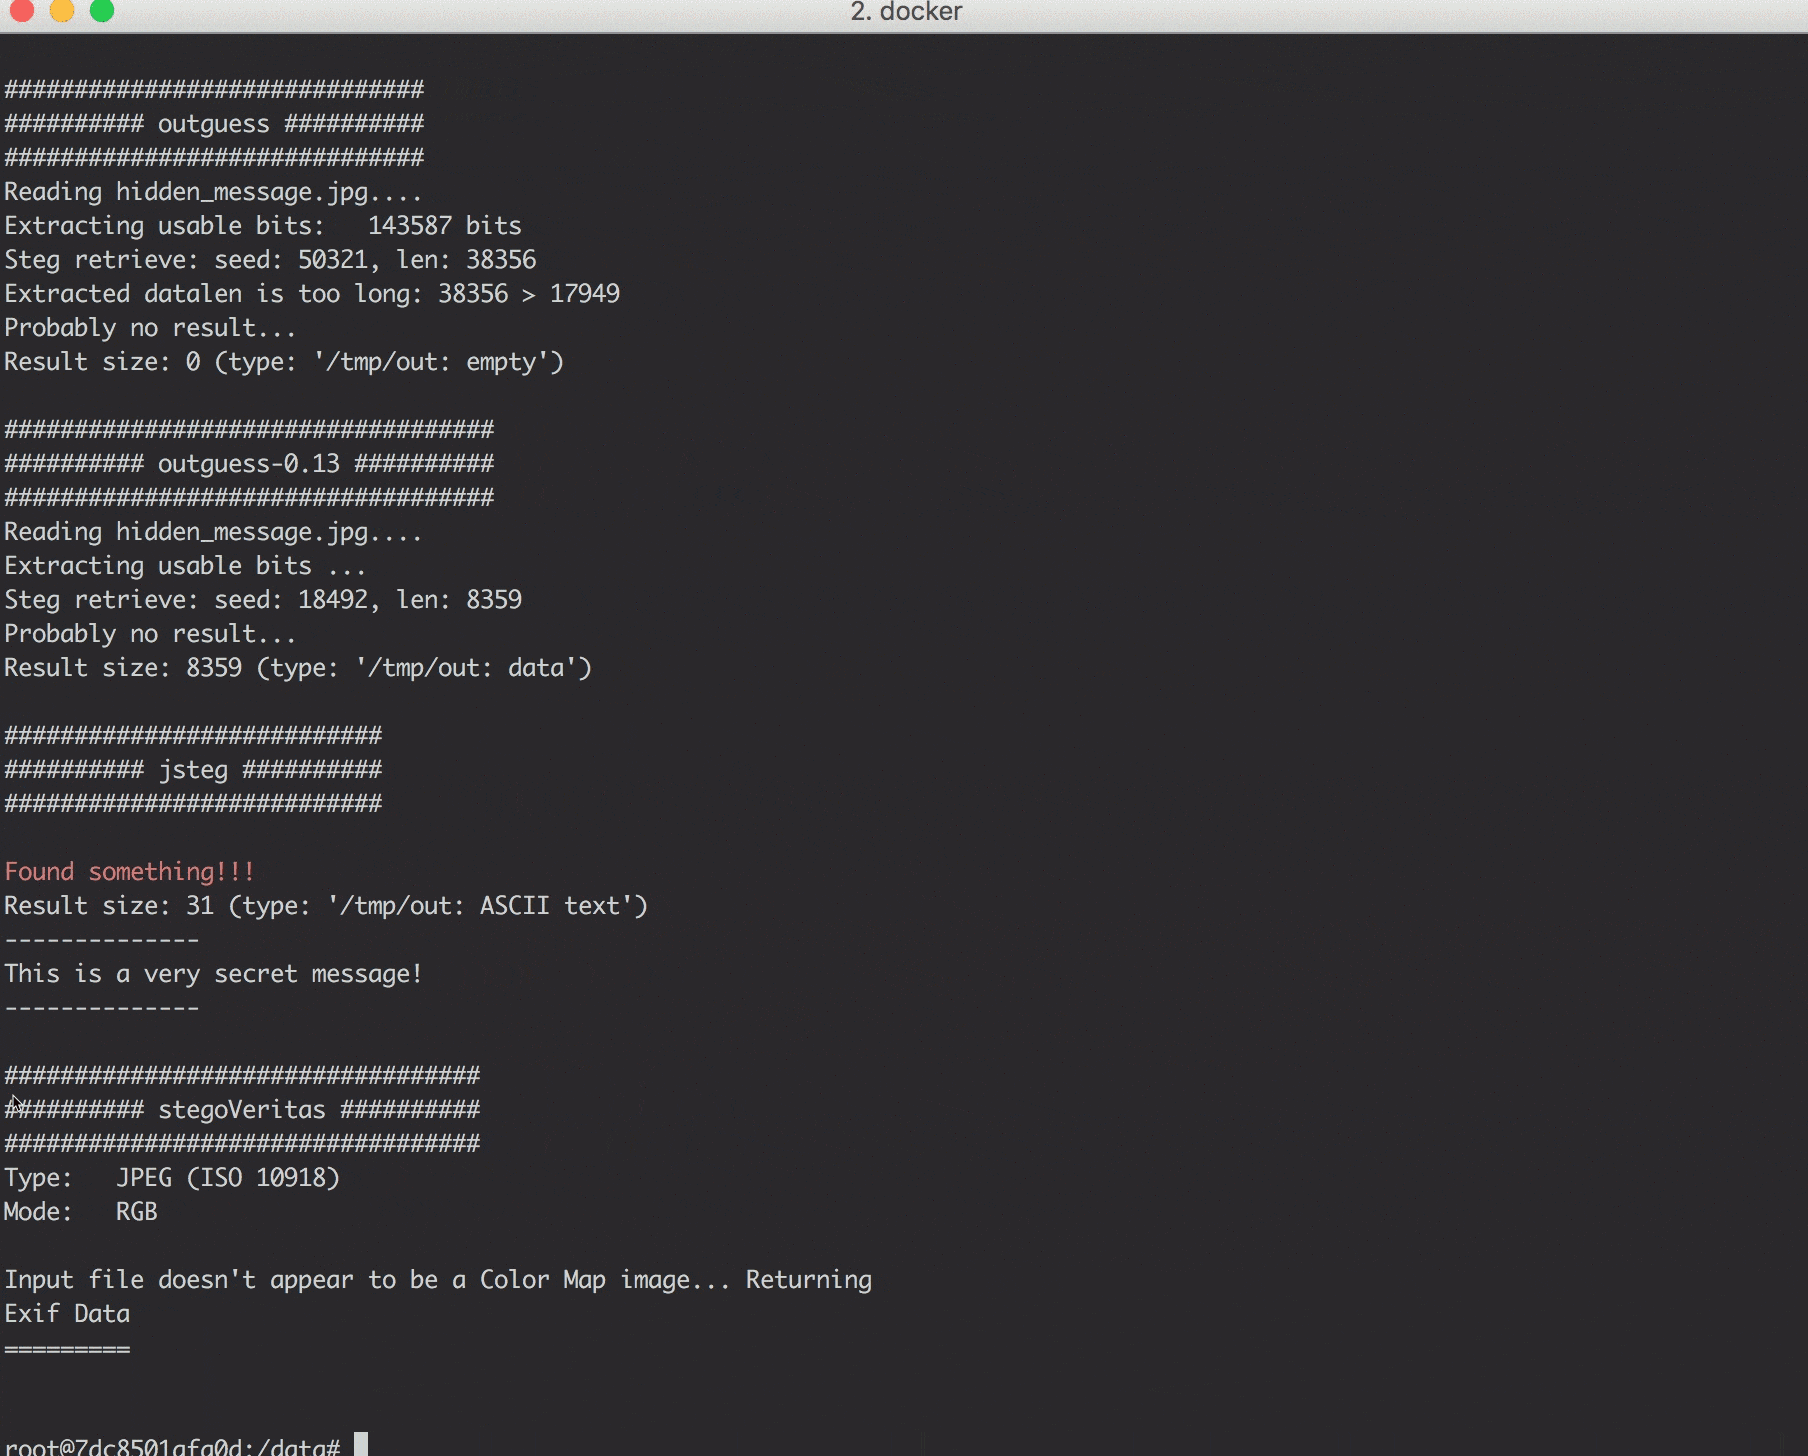 dominicbreuker/stego-toolkit
Collection of steganography tools - helps with CTF challenges
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
 cristianzsh/forensictools
Collection of forensic tools
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…