

mcp-shark
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
ai-securityapi-securityconfiguration-auditing+7
172
mcp-shark/mcp-sharkWireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 mnrkbys/norimaci
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
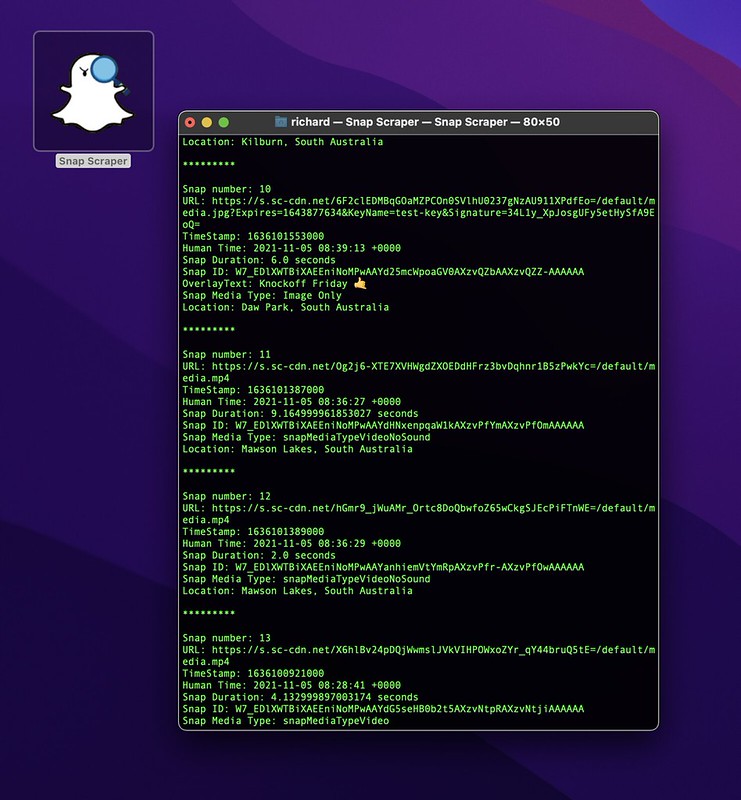 rhematt/snap-scraper
Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 matheuzsecurity/modtracer
Detects hidden Linux kernel rootkits (LKM-based) and restores their visibility using kernel-level inspection techniques for forensic analysis and…
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 mnrkbys/ma2tl
macOS forensic timeline generator using the analysis result DBs of mac_apt
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 grizzzer/cve-2026-42978-poc-research
CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…