
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
947 results
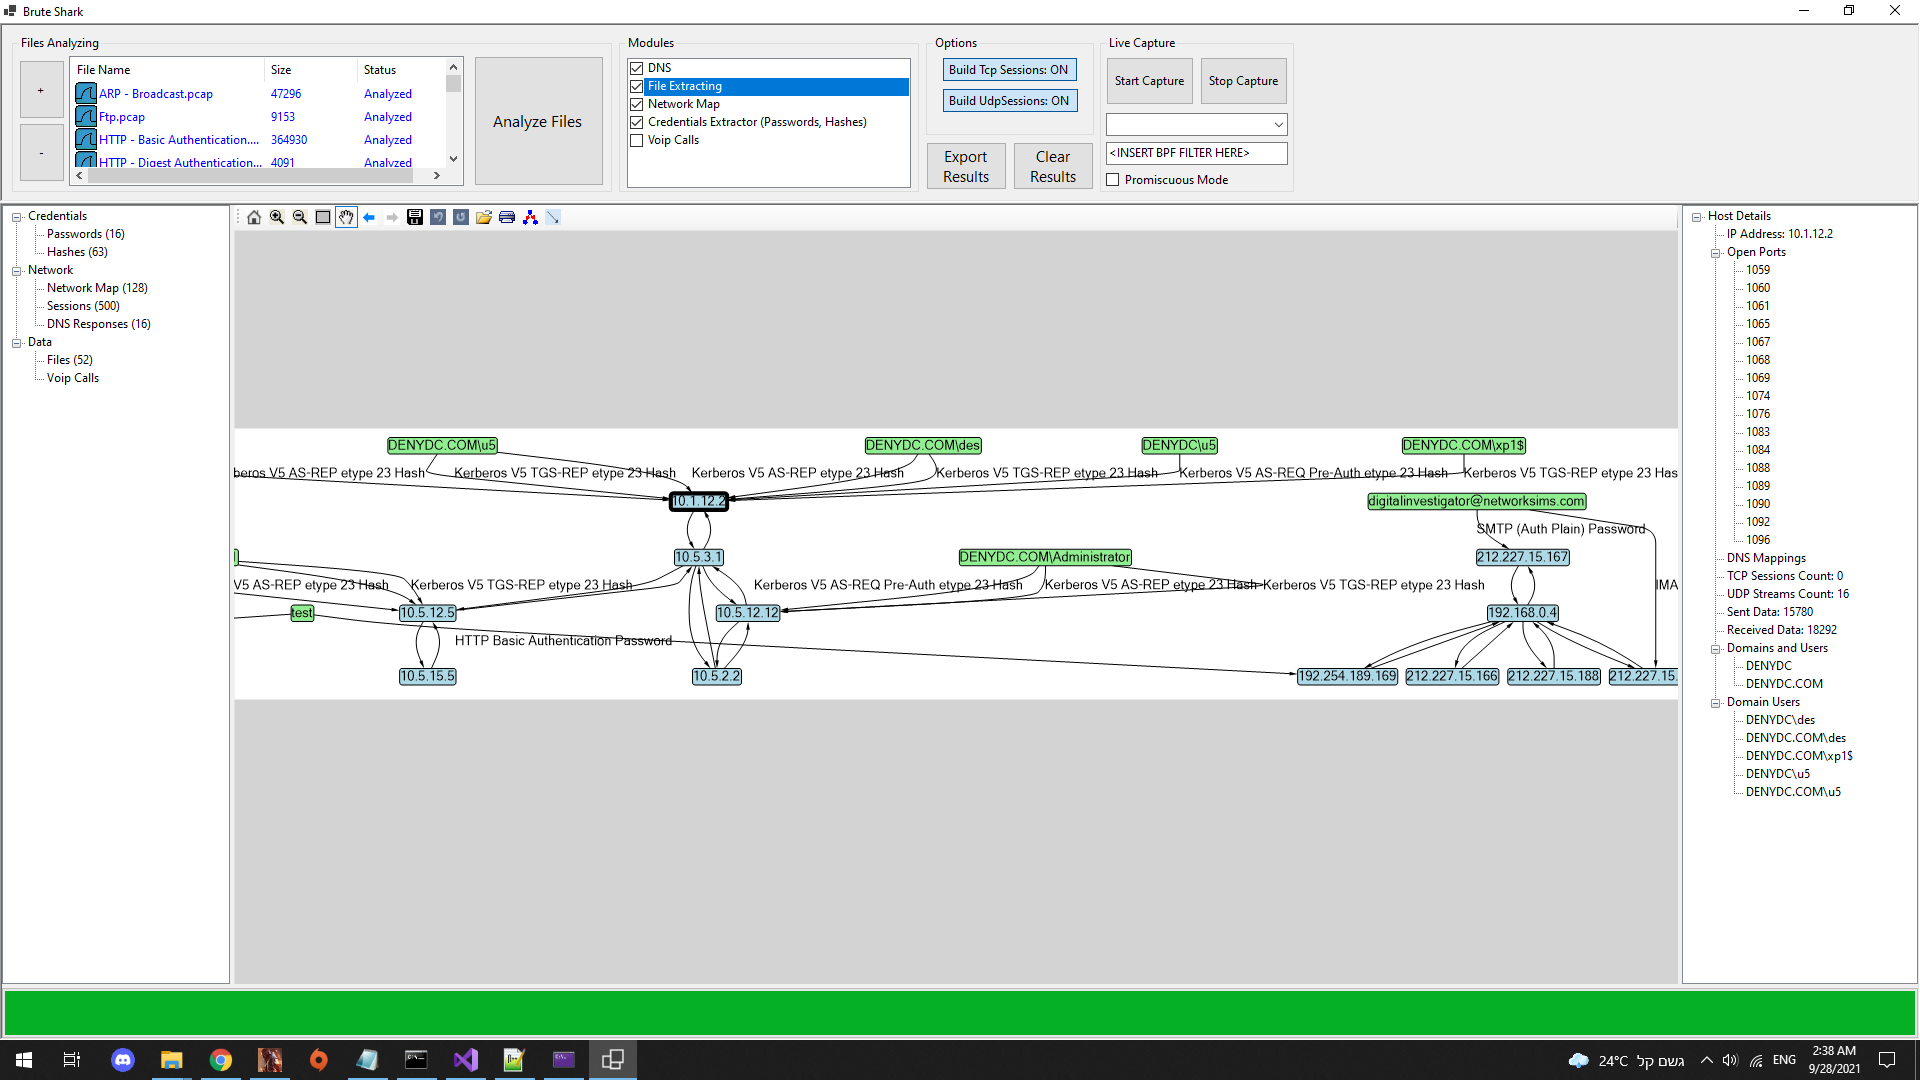
BruteShark preview

BruteShark

GitHubodedshimon/bruteshark

Network Analysis Tool

dns-analysisforensicshash-analysis+4
3.4k5 years ago
android-backup-extractor preview

android-backup-extractor

GitHubnelenkov/android-backup-extractor

Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
android-securitydata-recoveryforensics+1
2.6k3 months ago
mac-monitor preview

mac-monitor

GitHubbrandon7cc/mac-monitor

Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
dynamic-analysis-sandboxingeducationforensics+2
1.4k2 days ago
Noriben preview

Noriben

GitHubrurik/noriben

Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
dynamic-analysis-sandboxingforensicsioc-management+1
1.3k1 month ago
flare-learning-hub preview

flare-learning-hub

GitHubmandiant/flare-learning-hub

Free educational content on reverse engineering and malware analysis from the FLARE team
binary-analysisdebuggerseducation+4
1.4k7 months ago
kunai preview

kunai

GitHubkunai-project/kunai

eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…

container-securitydefensive-toolsforensics+3
1.1k9 days ago
Malware-Exhibit preview

Malware-Exhibit

GitHubalvin-tosh/malware-exhibit

🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…

cryptographycurated-resourceseducation+3
1.2k2 years ago
Malware-analysis-and-Reverse-engineering preview

Malware-analysis-and-Reverse-engineering

GitHubdump-guy/malware-analysis-and-reverse-engineering

Some of my publicly available Malware analysis and Reverse engineering.
binary-analysisctfcurated-resources+8
9602 years ago
refinery preview

refinery

GitHubbinref/refinery

High Octane Triage Analysis

binary-analysiscryptographyforensics+4
8671 day ago
nfstream preview

nfstream

GitHubnfstream/nfstream

NFStream: a Flexible Network Data Analysis Framework.
anomaly-detectioneducationforensics+4
1.2k3 months ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
digital-forensicsforensicsinformation-gathering+3
8567 years ago
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
53214 days ago
PMAT-labs preview

PMAT-labs

GitHubhuskyhacks/pmat-labs

Labs for Practical Malware Analysis & Triage
digital-forensicseducationforensics+3
1.1k7 months ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
4761 day ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4464 years ago
malboxes preview

malboxes

GitHubgosecure/malboxes

Builds malware analysis Windows VMs so that you don't have to.
forensicsmalware-analysis
1.0k5 years ago
gdid-reversal preview

gdid-reversal

GitHubsmtimesiwndr/gdid-reversal

Reverse-engineered analysis of Microsoft's Global Device Identifier (GDID) revealing its generation as a server-assigned MSA Device PUID, storage in…
educationforensicsprivacy+1
7064 months ago
VolWeb preview

VolWeb

GitHubk1nd0ne/volweb

A centralized and enhanced memory analysis platform

digital-forensicseducationforensics+5
5381 month ago
Previous1…345…53Next