
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
275 results
MalConfScan preview

MalConfScan

GitHubjpcertcc/malconfscan

Volatility plugin for extracts configuration data of known malware
digital-forensicsforensicsincident-response+3
4992 years ago
TEx preview

TEx

GitHubguibacellar/tex

Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
digital-forensicsforensicsinformation-gathering+2
3752 years ago
RdpCacheStitcher preview

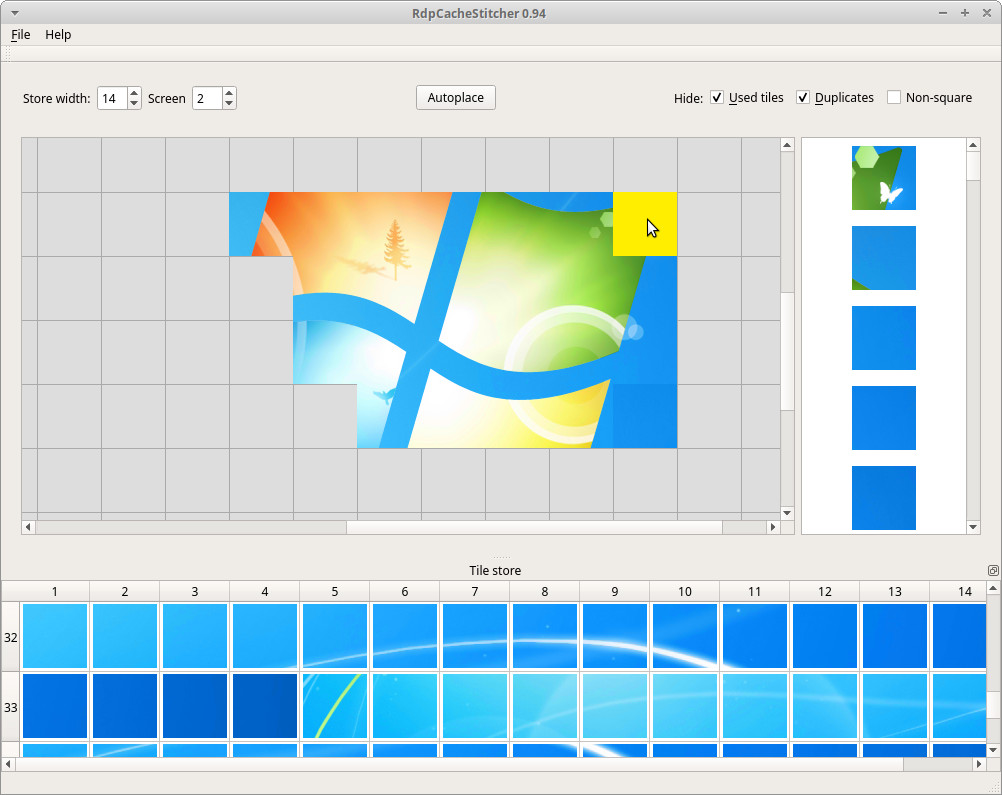
RdpCacheStitcher

GitHubbsi-bund/rdpcachestitcher

RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
data-recoverydigital-forensicsforensics+1
3315 years ago
dumpzilla preview

dumpzilla

GitHubbusindre/dumpzilla

Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
digital-forensicsforensicsinformation-gathering+1
14810 months ago
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

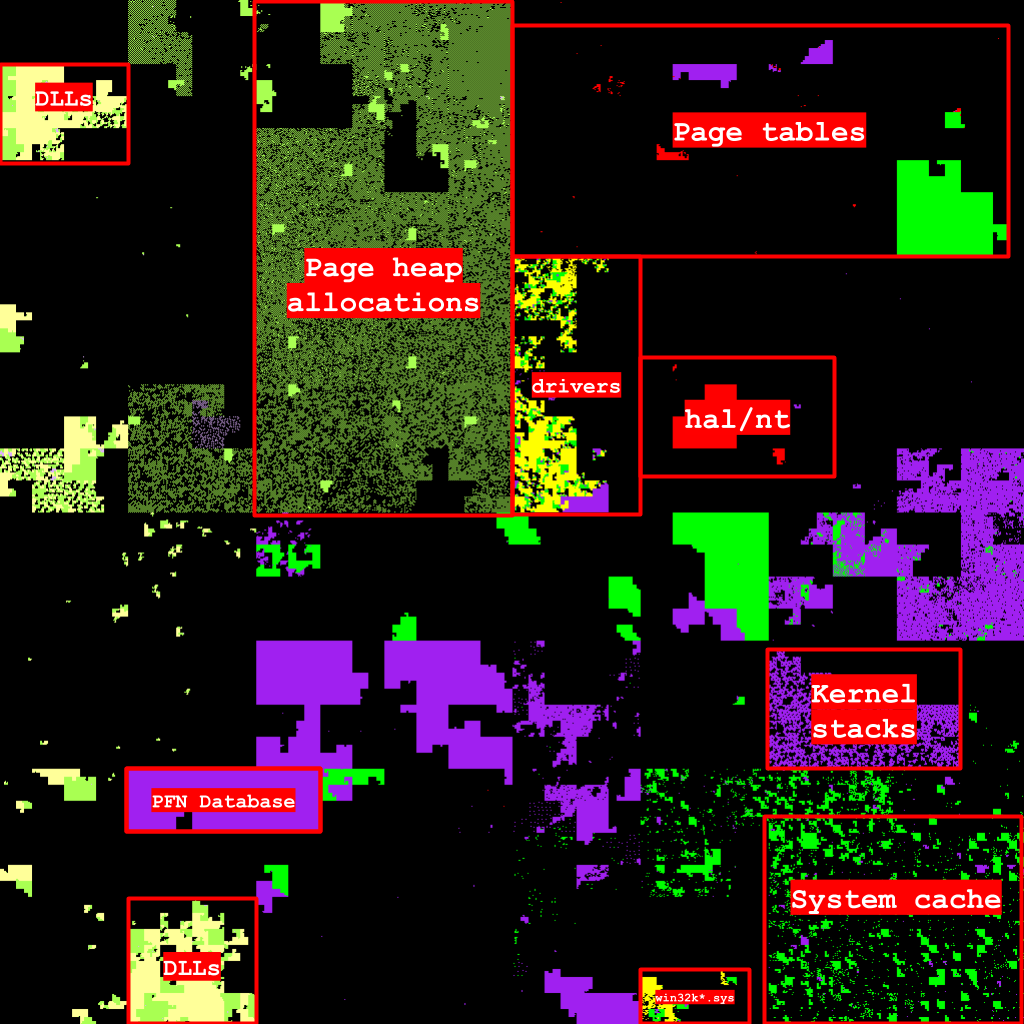
Visualize the virtual address space of a Windows process on a Hilbert curve.
digital-forensicsforensicsmemory-forensics
3085 years ago
pcapinator preview

pcapinator

GitHubmspicer/pcapinator

A tool for processing a lot of pcaps using tshark
forensicsinformation-gatheringnetwork-forensics+2
1553 years ago
HoneyProxy preview

HoneyProxy

GitHubmhils/honeyproxy

This project is now part of @mitmproxy.

forensicsnetwork-securitypacket-sniffing-analysis+3
1969 years ago
xioc preview

xioc

GitHubassafmo/xioc

Extract indicators of compromise from text, including "escaped" ones.
forensicsinformation-gatheringioc-management+3
1636 years ago
yaralyzer preview

yaralyzer

GitHubmichelcrypt4d4mus/yaralyzer

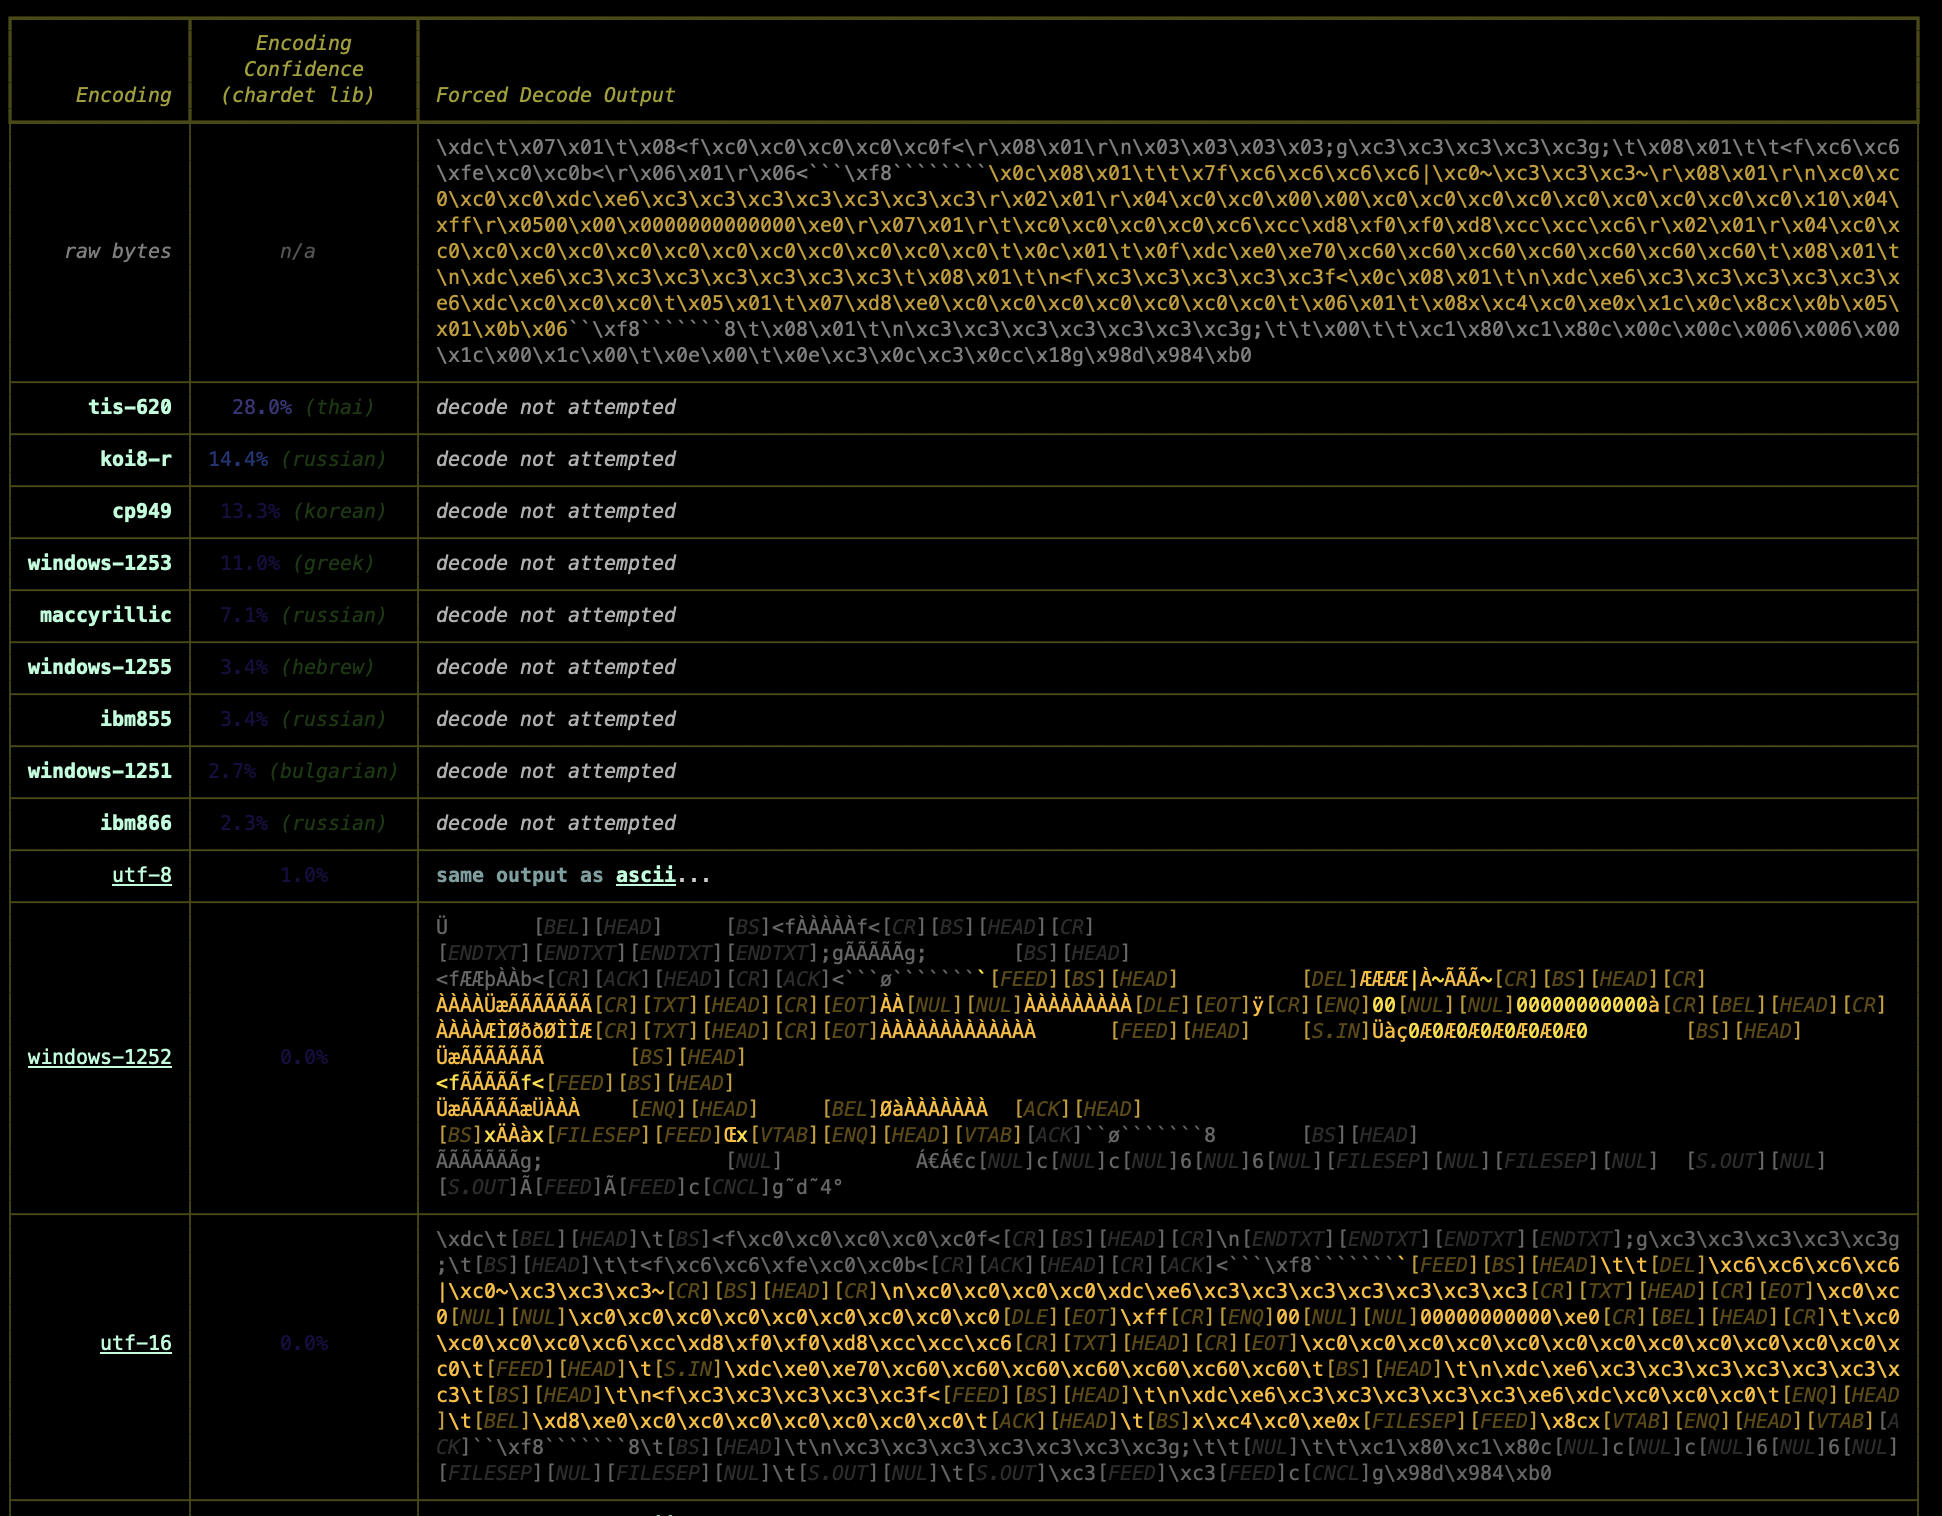
Visually inspect and force decode YARA and regex matches found in both binary and text data with colors. Lots of colors.
binary-analysisforensicsmalware-analysis+1
1529 months ago
LiMEaide preview

LiMEaide

GitHubkd8bny/limeaide

A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.
digital-forensicsforensicsmemory-forensics
1577 years ago
wifi_db preview

wifi_db

GitHubr4ulcl/wifi_db

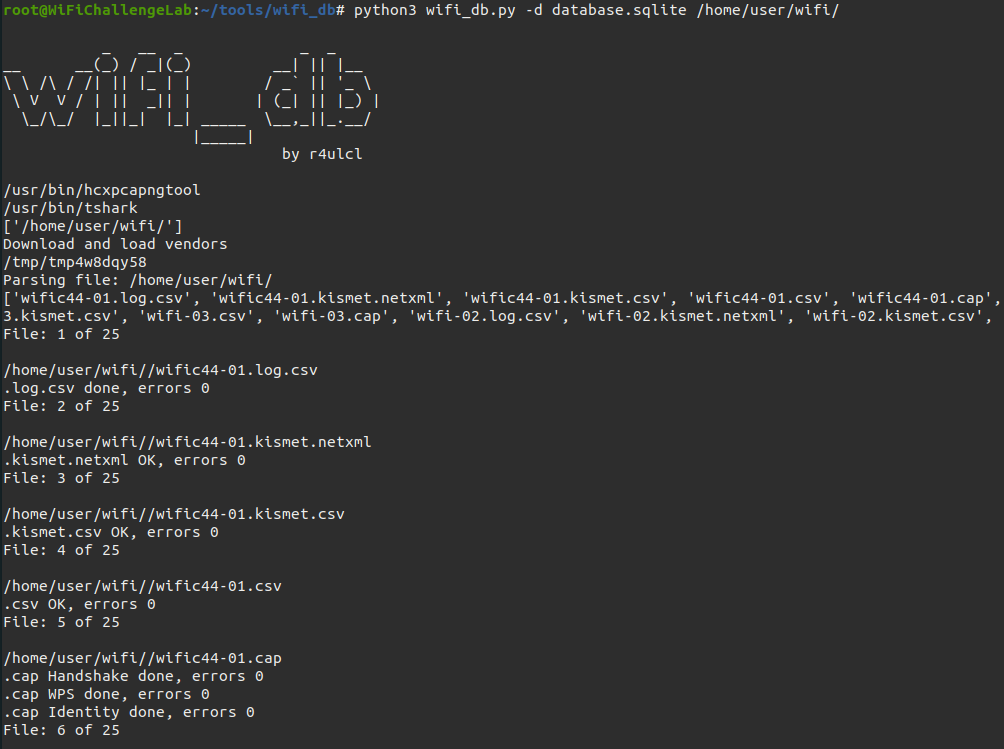
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
forensicsinformation-gatheringpassword-cracking+2
1381 month ago
Fennec preview

Fennec

GitHubabdulrhmanalfaifi/fennec

Artifact collection tool for *nix systems

digital-forensicsforensicsincident-response+3
2202 years ago
mailMeta preview

mailMeta

GitHubgr33nm0nk2802/mailmeta

An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
digital-forensicsemail-securityforensics+2
1755 years ago
MEAT preview

MEAT

GitHubjfarley248/meat

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
data-recoverydigital-forensicsforensics+2
1686 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
RansomCoinPublic preview

RansomCoinPublic

GitHubconcinnity-risks/ransomcoinpublic

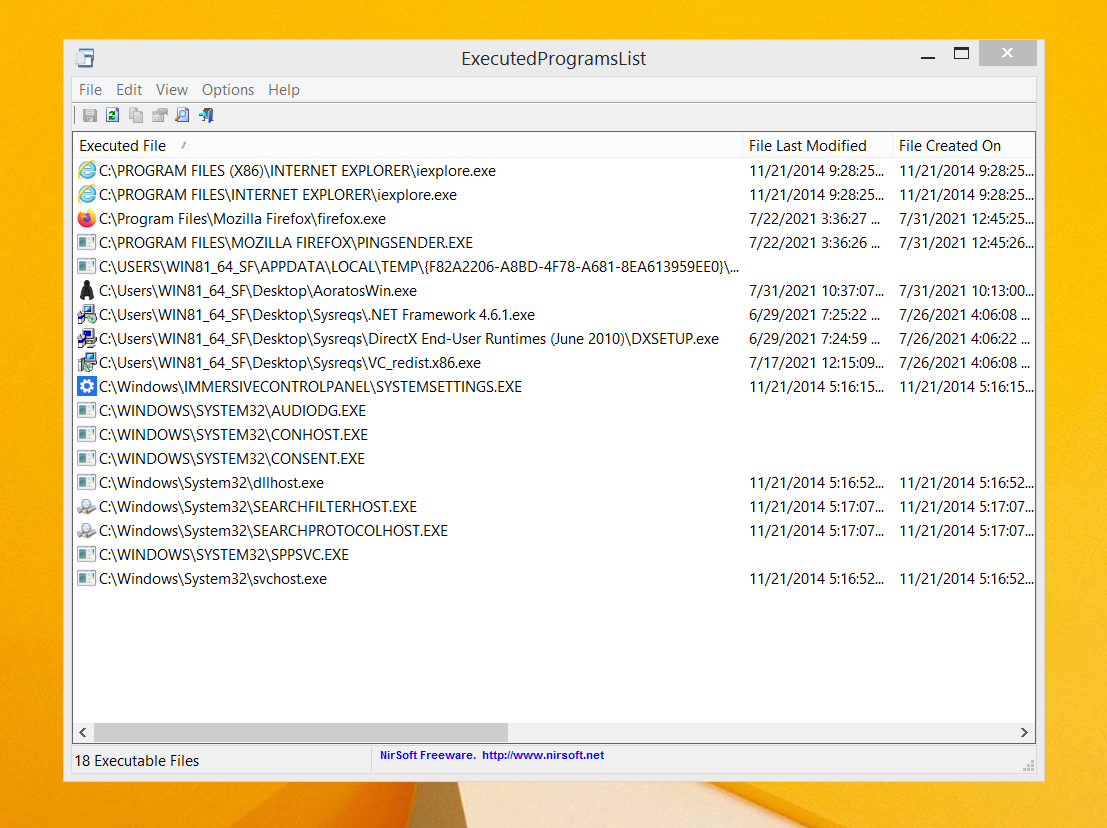
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
cryptographydigital-forensicsforensics+3
565 years ago
AoratosWin preview

AoratosWin

GitHubpinoywh1z/aoratoswin

A tool that removes traces of executed applications on Windows OS.
anti-botdefensive-toolsforensics+1
1194 years ago
memOptix preview

memOptix

GitHubblueteam0ps/memoptix

A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.

digital-forensicsforensicsincident-response+2
983 years ago
Previous1…345…16Next