
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
495 results
freedomfighting preview

freedomfighting

GitHubjusticerage/freedomfighting

A collection of scripts which may come in handy during your freedom fighting activities.
crawlerencryption-decryption-toolsforensics+8
418
3 years ago
EventHorizon preview

EventHorizon

GitHubhullabrian/eventhorizon

Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
defensive-toolseducationforensics+5
567 months ago
vboxdie-cracker preview

vboxdie-cracker

GitHubsinfocol/vboxdie-cracker

VirtualBox Disk Image Encryption password cracker
encryption-decryption-toolsforensicspassword-cracking
3310 years ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

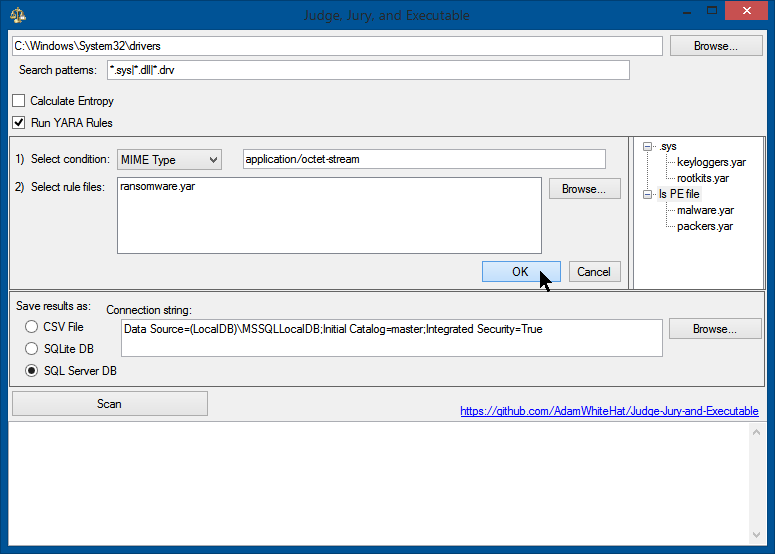
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
855 months ago
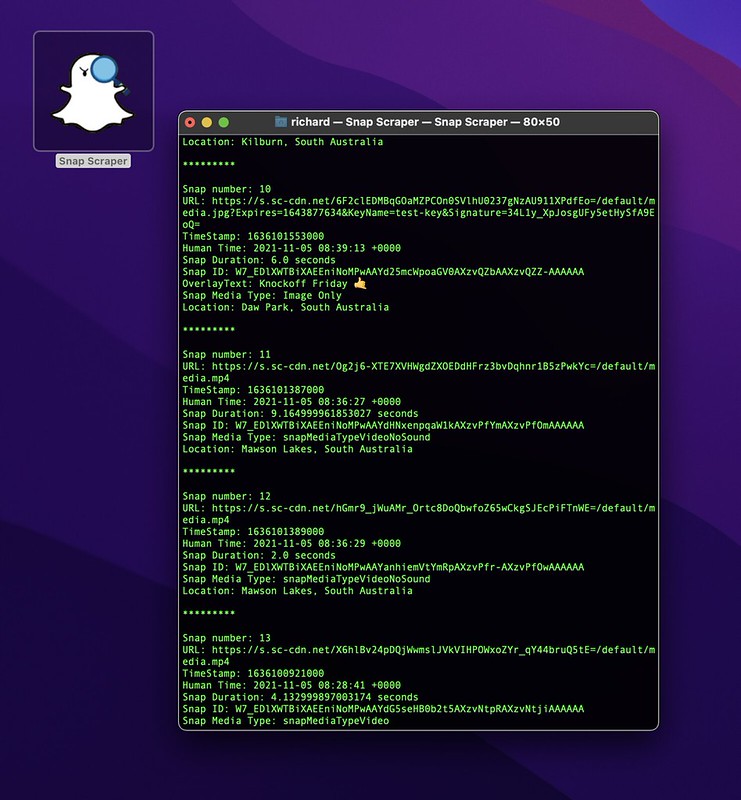
Snap-Scraper preview

Snap-Scraper

GitHubrhematt/snap-scraper

Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.
digital-forensicseducationforensics+3
1153 years ago
ExtractUsnJrnl preview

ExtractUsnJrnl

GitHubjschicht/extractusnjrnl

Tool to extract the $UsnJrnl from an NTFS volume
data-recoverydigital-forensicsdisk-forensics+1
1127 years ago
ReClass.NET preview

ReClass.NET

GitHubreclassnet/reclass.net

More than a ReClass port to the .NET platform.
binary-analysiscode-analysisdebuggers+4
2.2k3 years ago
Audix preview
Archived

Audix

GitHub0x0v1/audix

Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
configuration-auditingdefensive-toolsdigital-forensics+4
11811 months ago
theZoo preview

theZoo

GitHubytisf/thezoo

Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…

curated-resourcesdynamic-analysis-sandboxingeducation+3
13.4k1 day ago
CVE-2021-44228 preview

CVE-2021-44228

GitHubfireeye/cve-2021-44228

OpenIOC rules to facilitate hunting for indicators of compromise
forensicsincident-responseioc-management+3
374 years ago
VolWeb preview

VolWeb

GitHubk1nd0ne/volweb

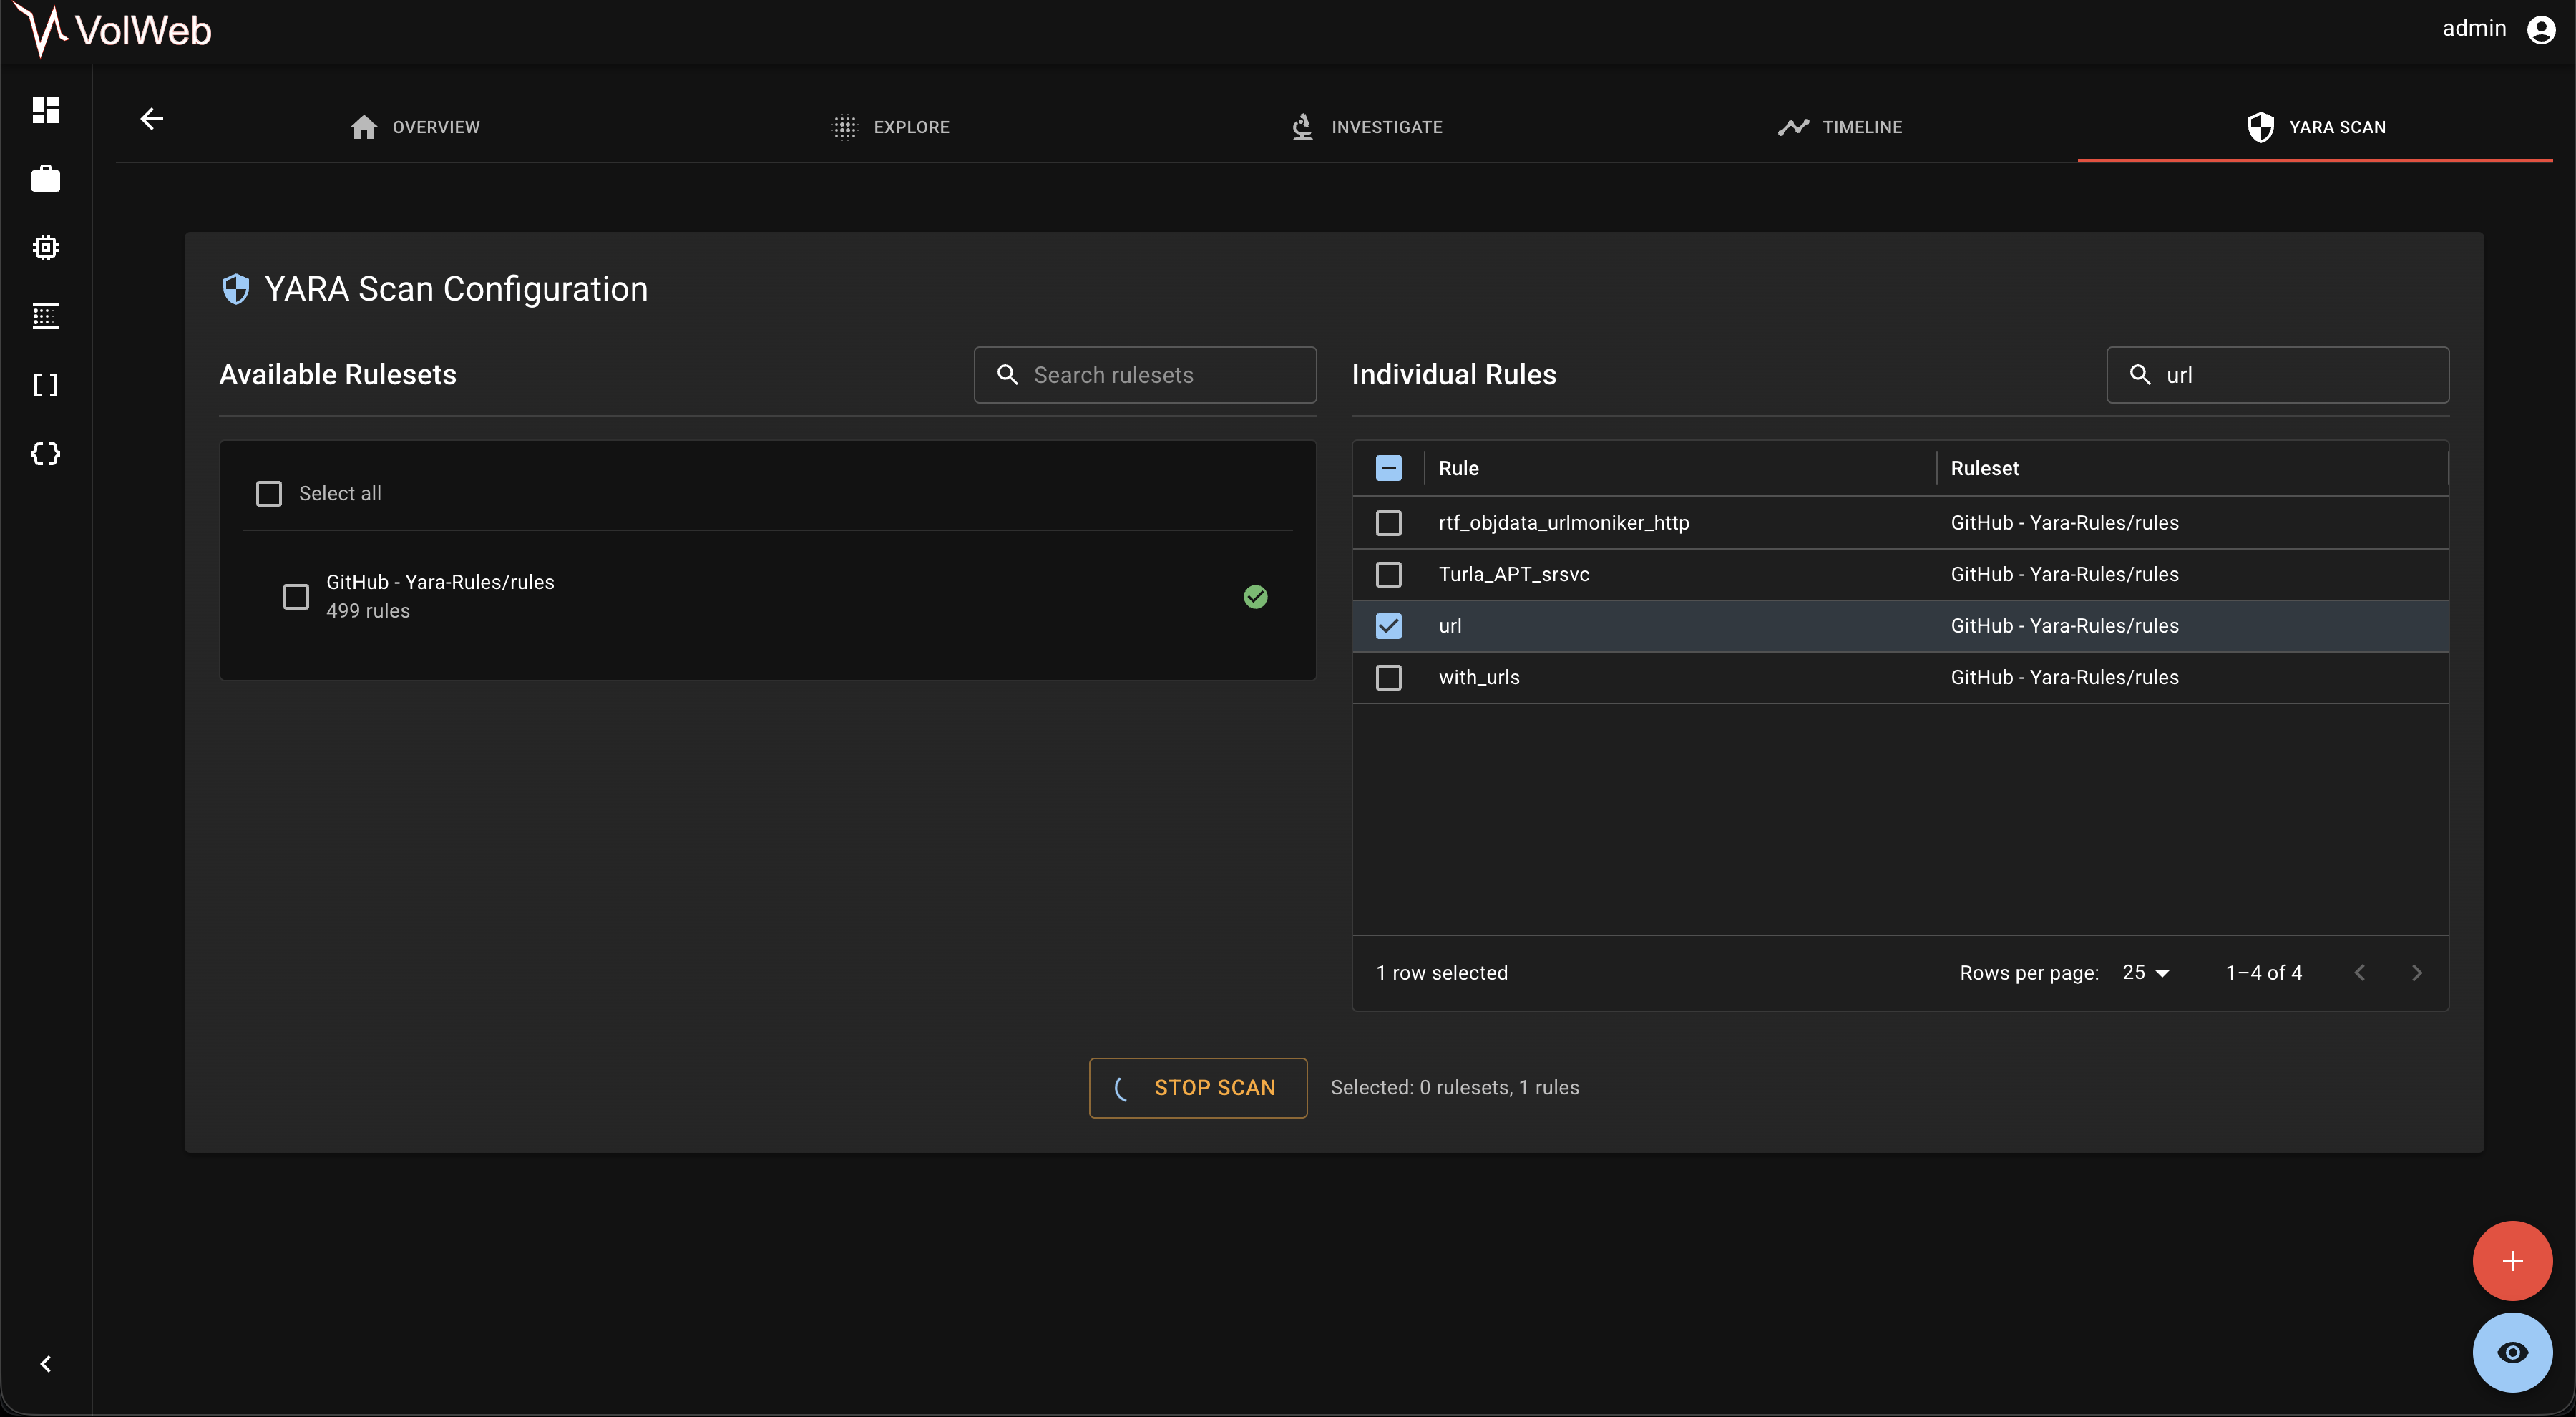
A centralized and enhanced memory analysis platform
digital-forensicseducationforensics+5
5381 month ago
dismember preview

dismember

GitHubliamg/dismember

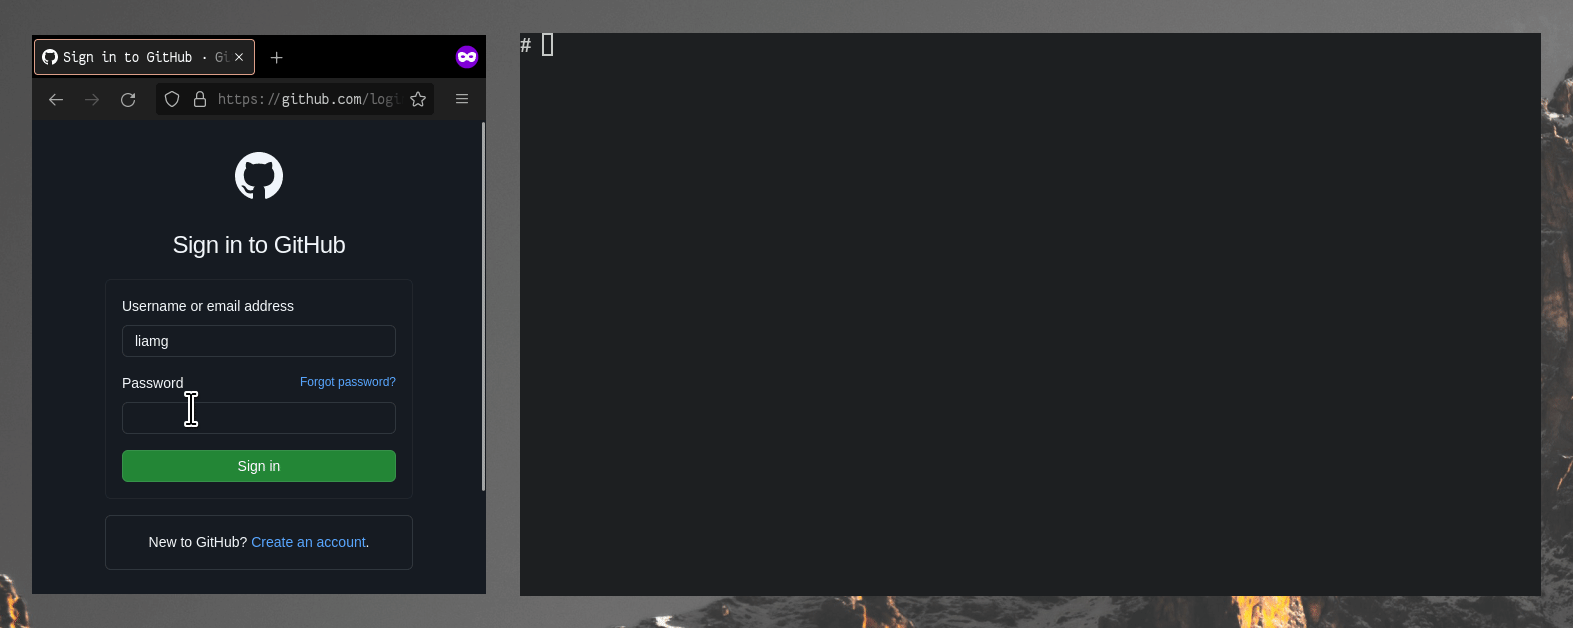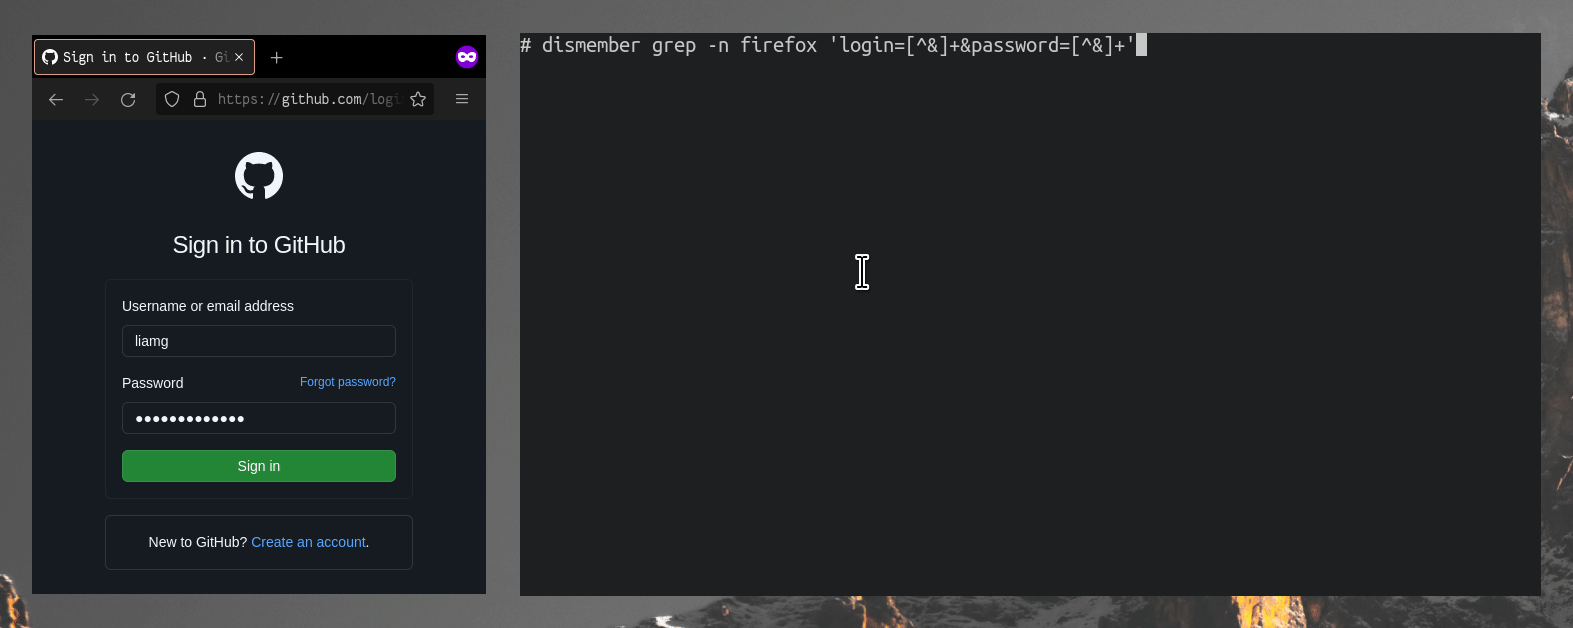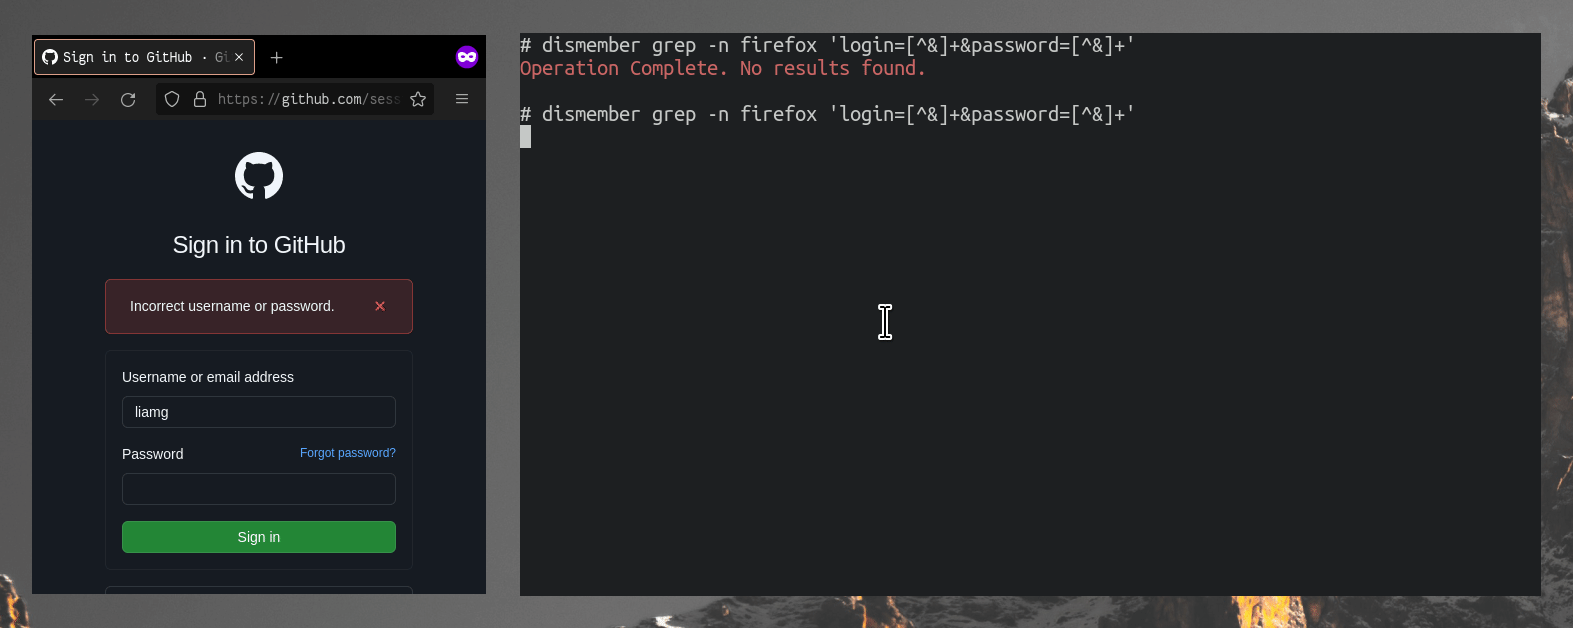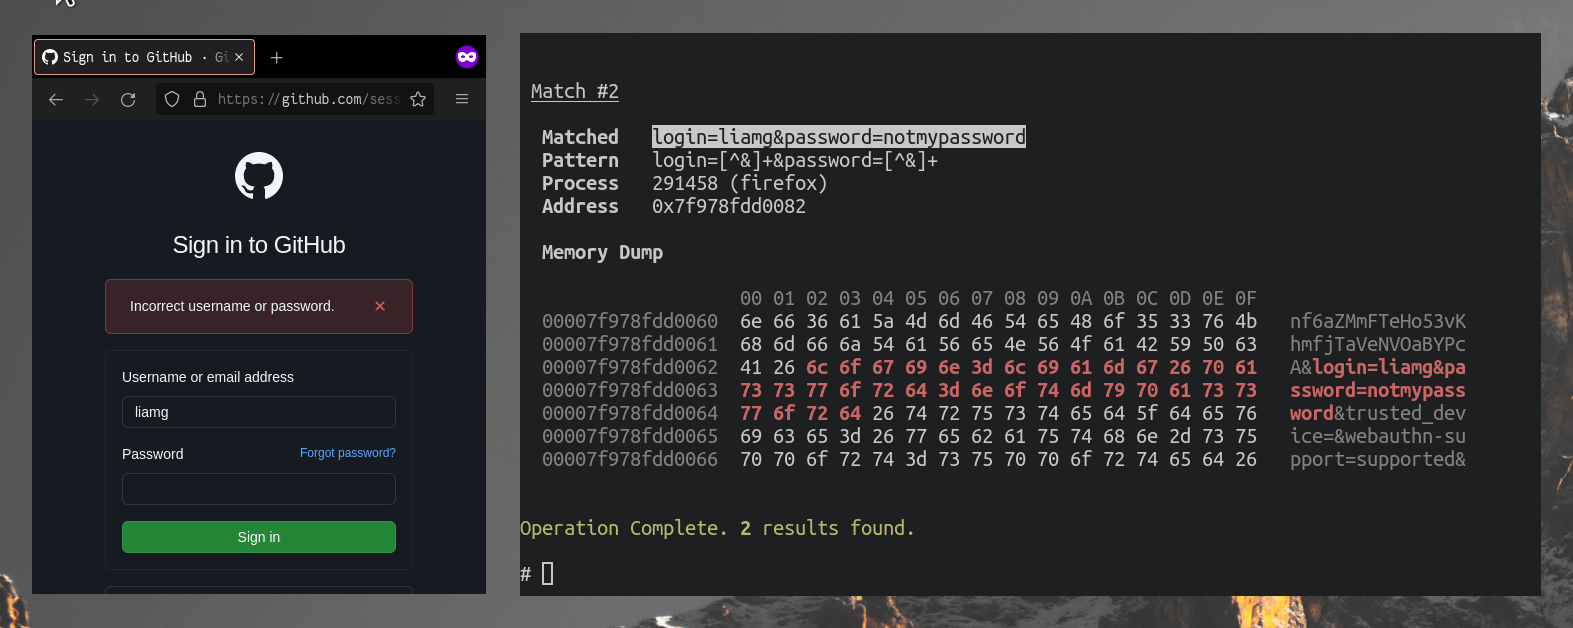
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.

ctfforensicsinformation-gathering+2
6774 years ago
visual-forensic-steganography preview

visual-forensic-steganography

GitHubmindcrypt/visual-forensic-steganography

Browser-based tool for visual steganography detection via LSB analysis on digital images, enabling forensic examination and stegomalware…
forensicsmalware-analysissteganography
84 years ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k2 years ago
auditd preview

auditd

GitHubneo23x0/auditd

Best Practice Auditd Configuration

configuration-auditingdefensive-toolsforensics+3
1.9k4 months ago
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts
digital-forensicsforensicsincident-response+2
3402 years ago
memOptix preview

memOptix

GitHubblueteam0ps/memoptix

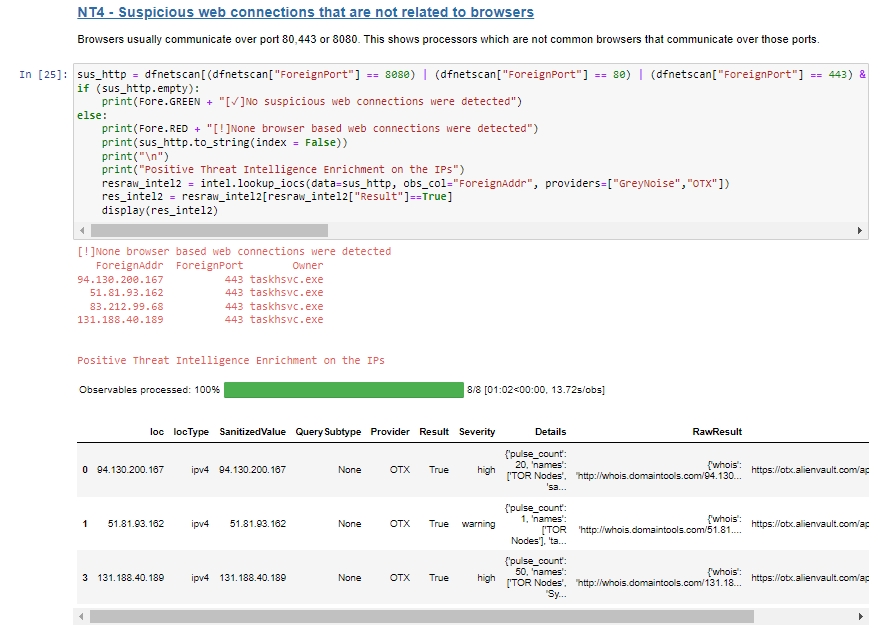
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
digital-forensicsforensicsincident-response+2
983 years ago
hashID preview

hashID

GitHubpsypanda/hashid

Software to identify the different types of hashes -

forensicshash-analysisinformation-gathering+3
1.5k11 years ago
Previous1234…28Next