
modo
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
ctfcurated-resourceseducation+9
192
mohshomis/modoCurated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
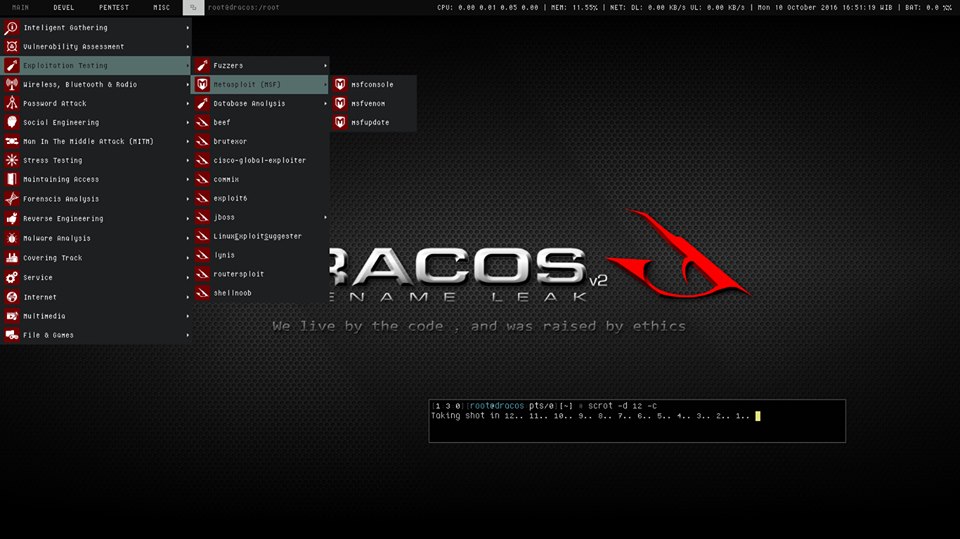 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
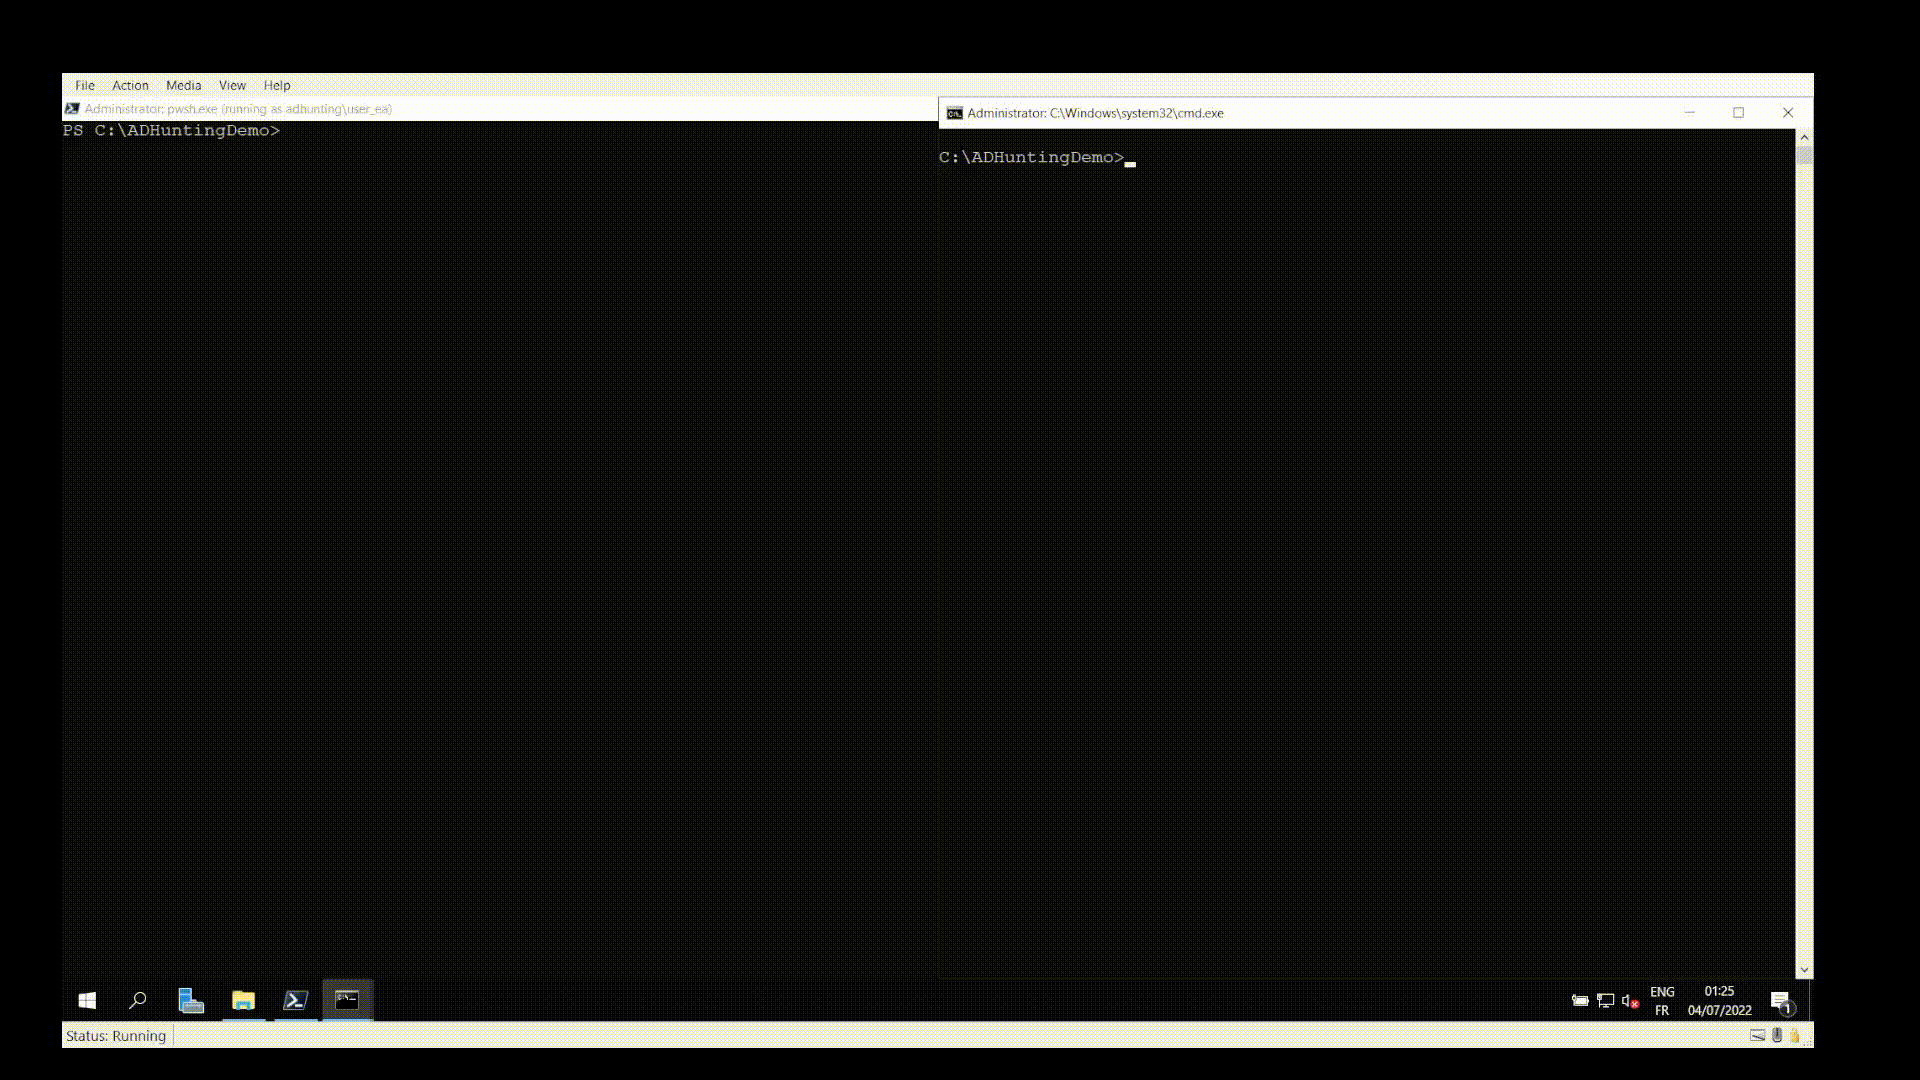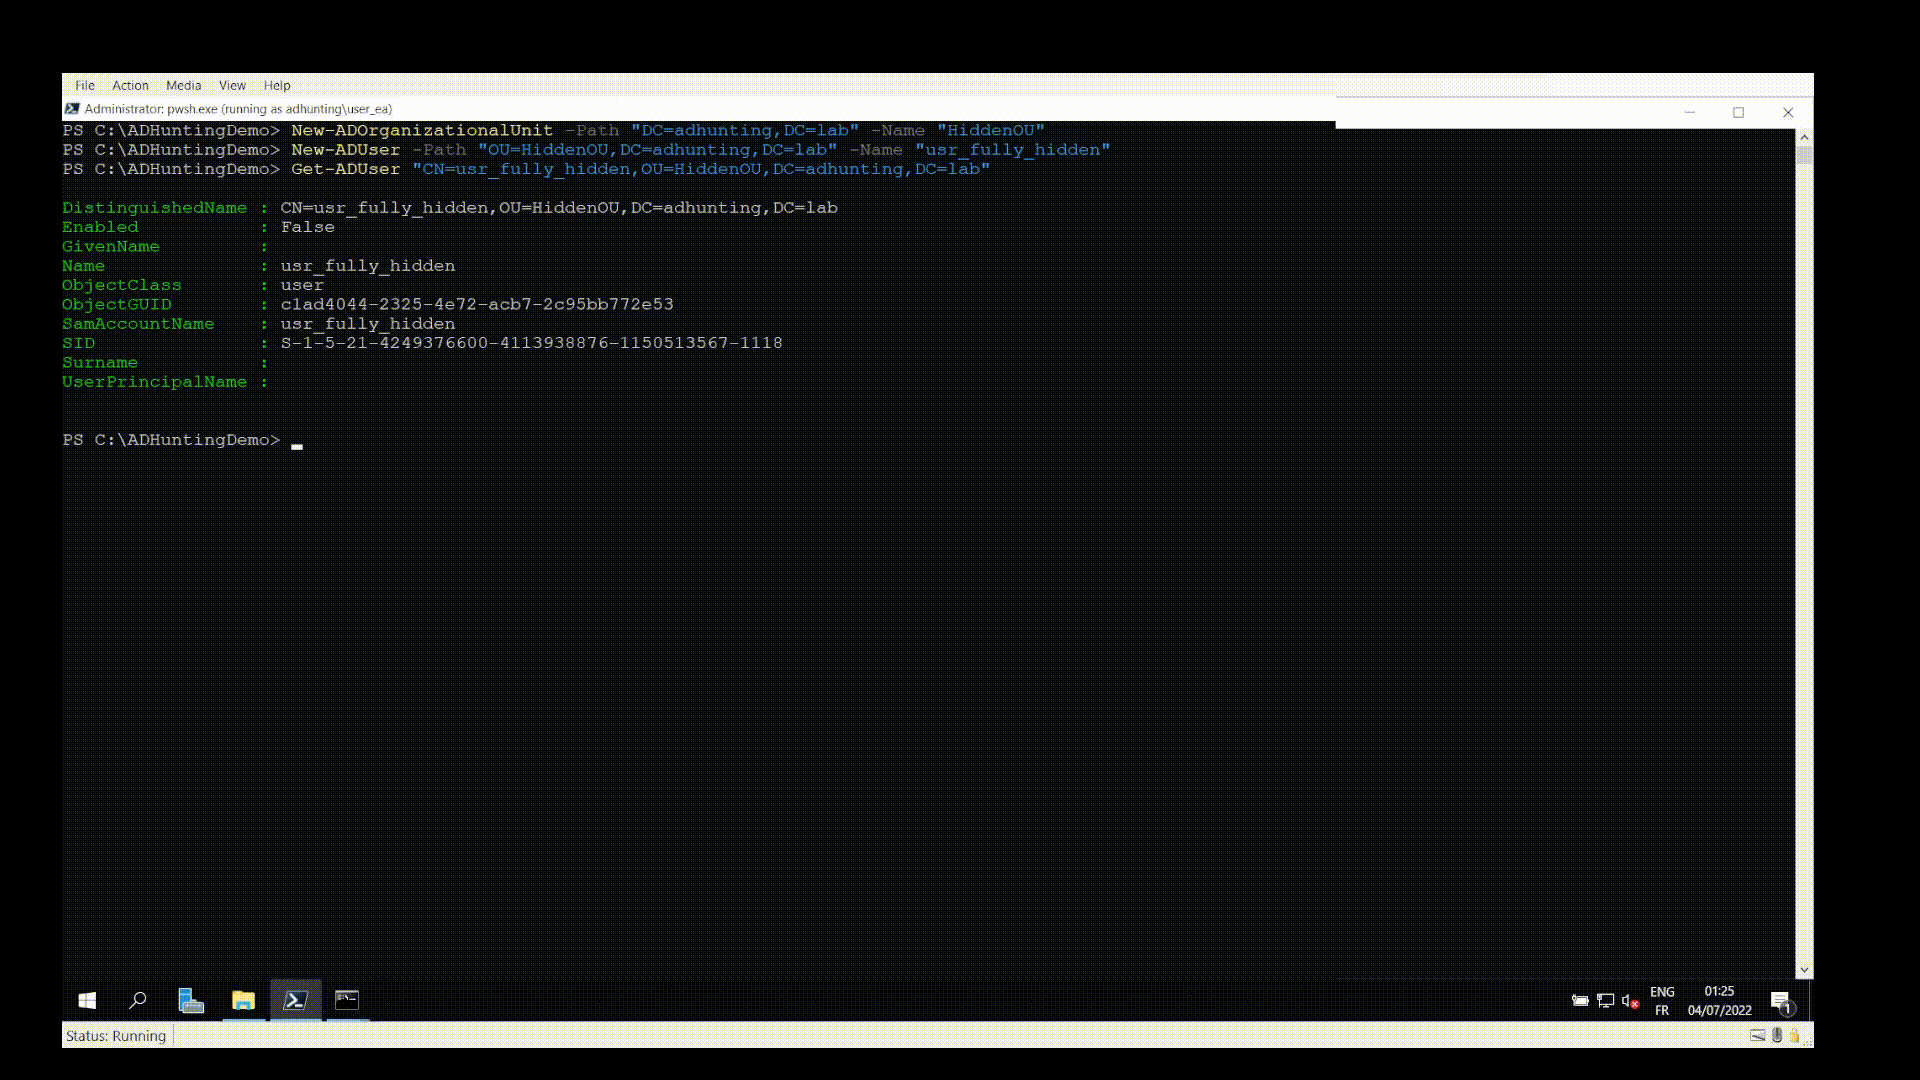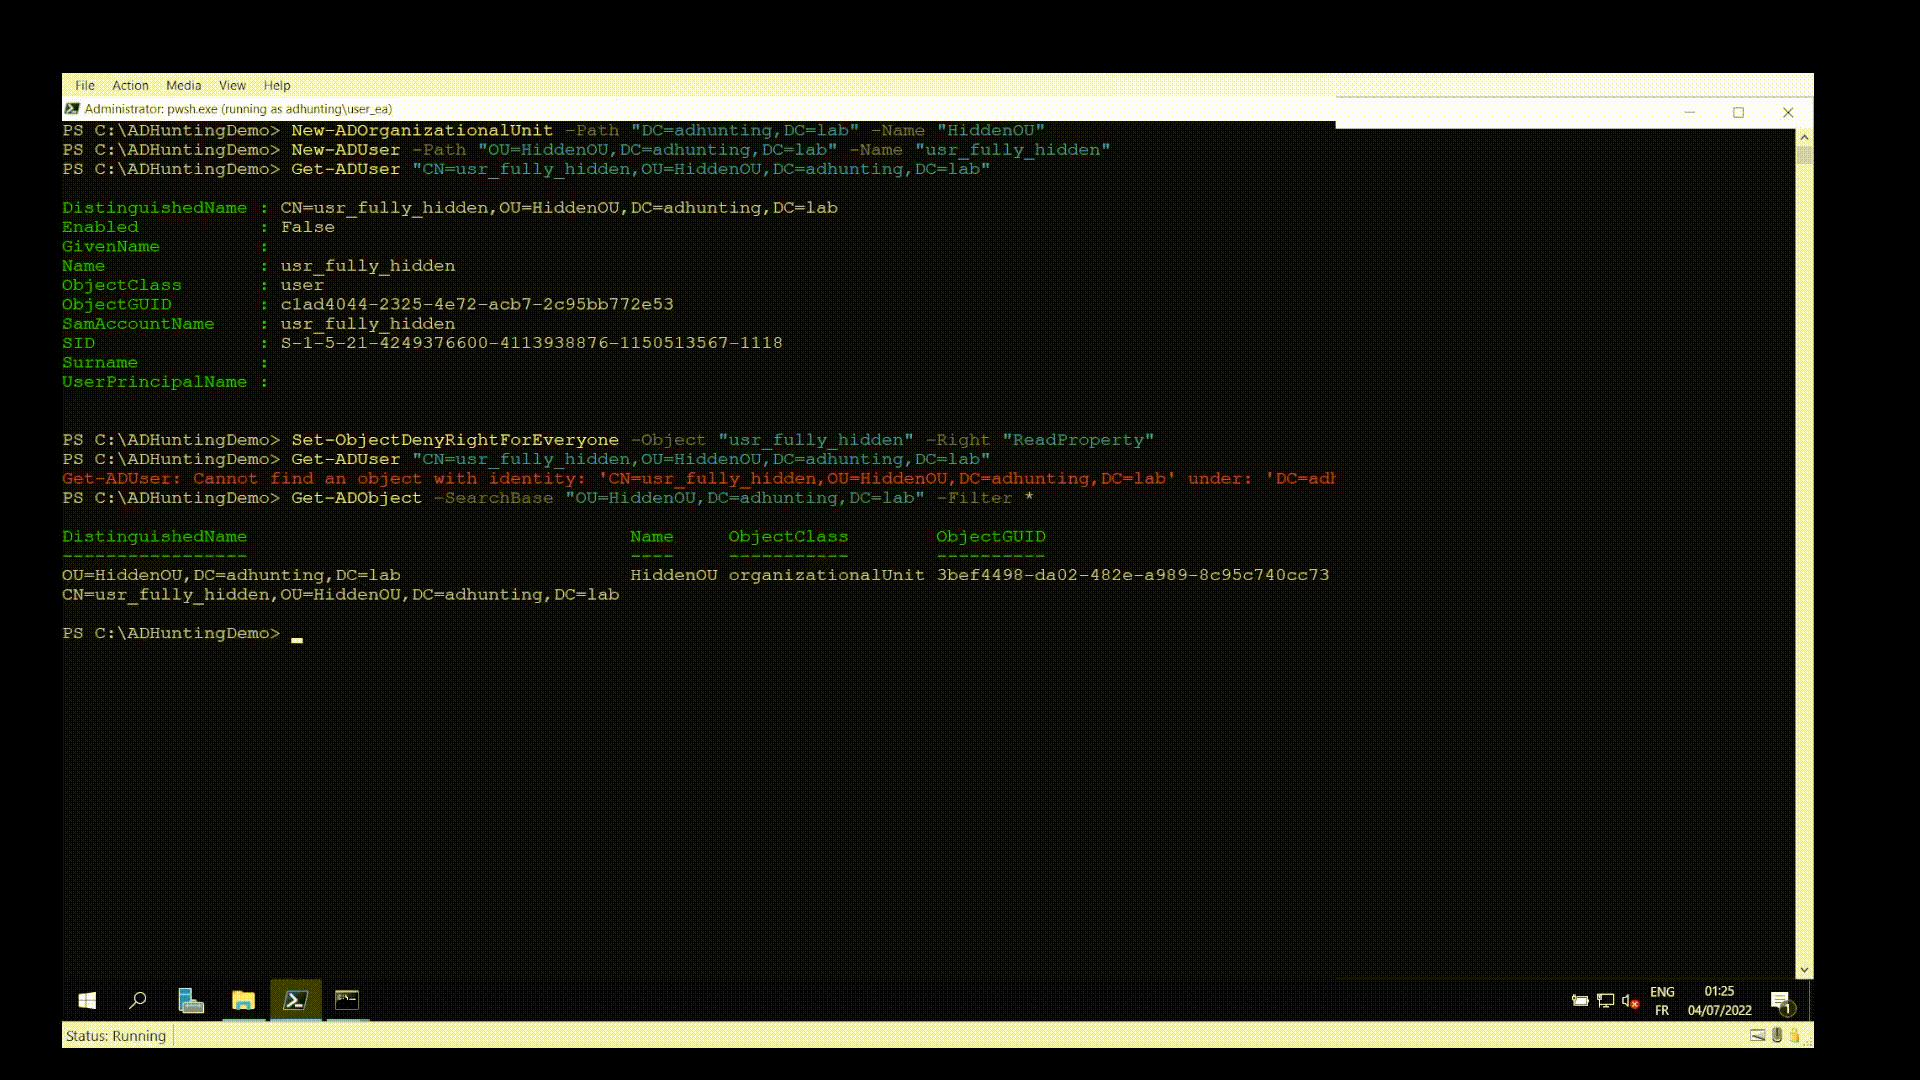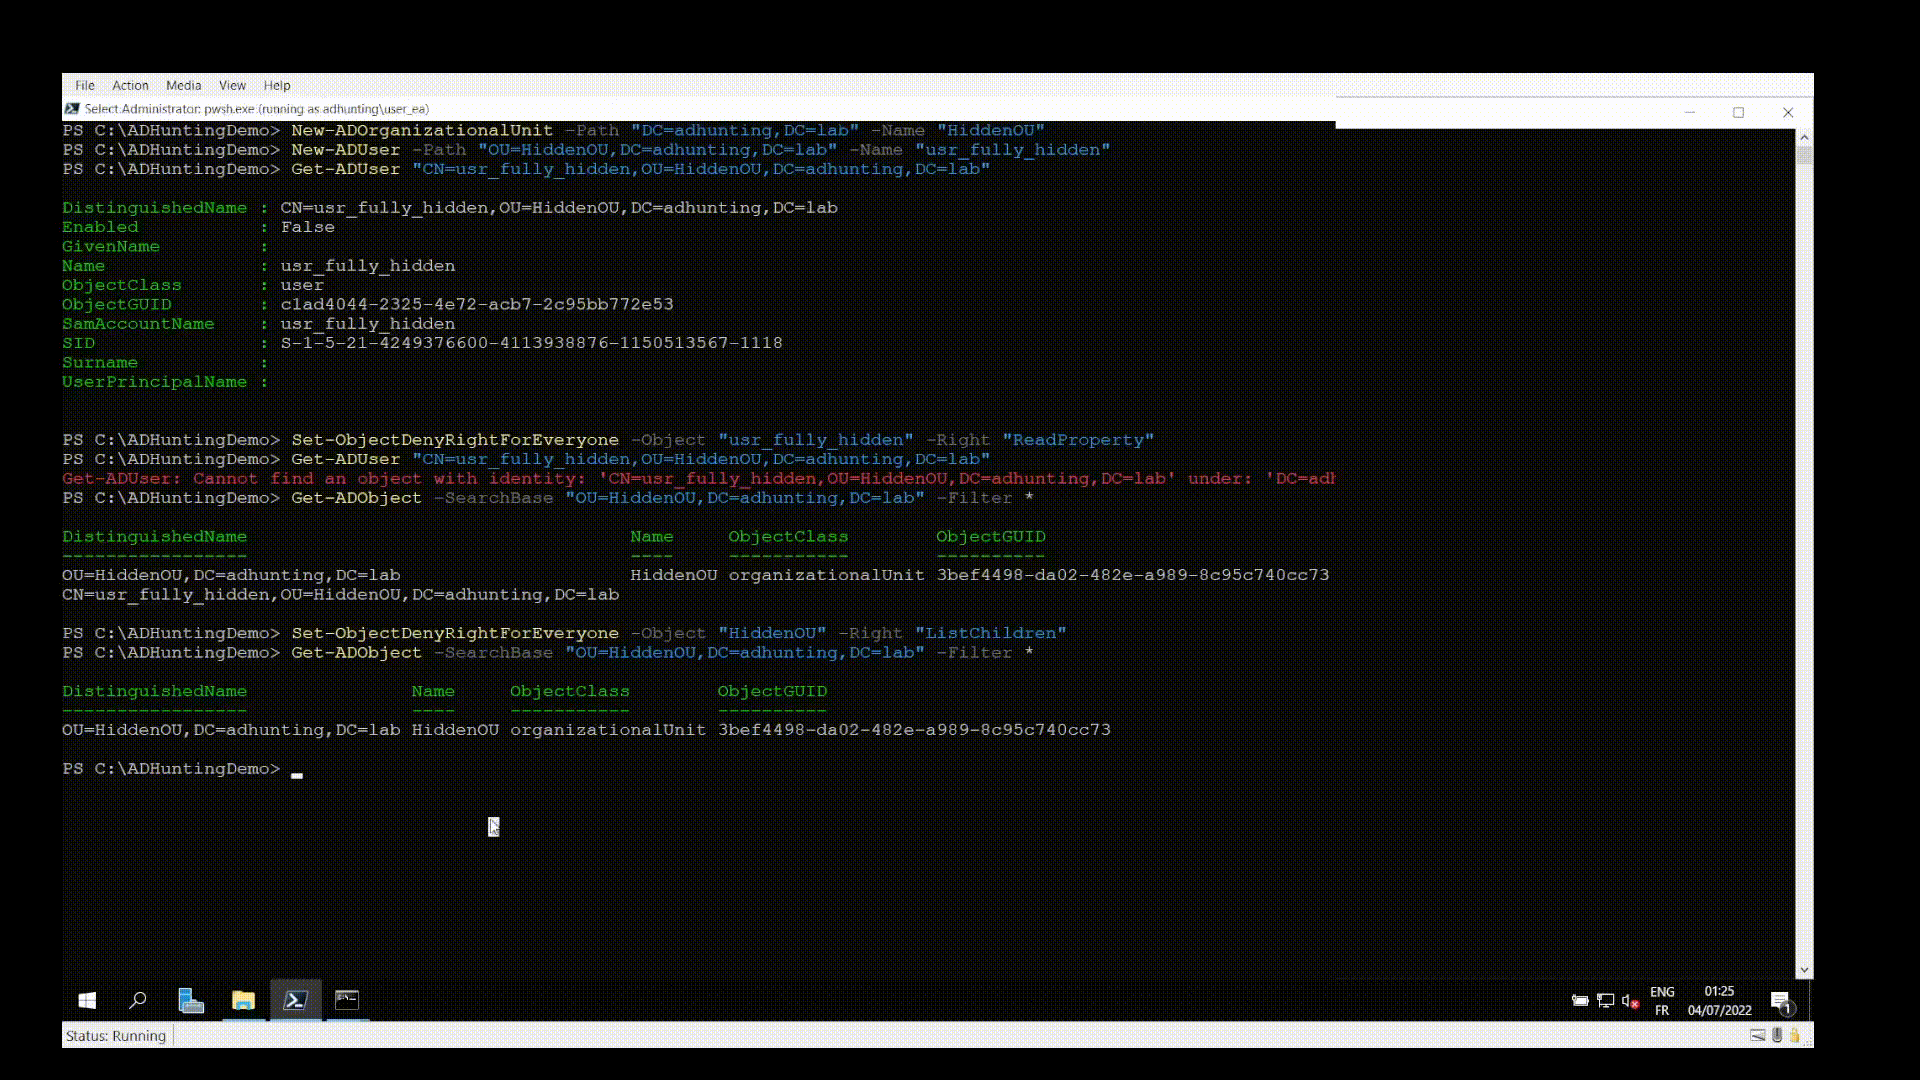 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 puckblush/tofu
Windows offline filesystem hacking tool for Linux
 thirdbyte/ssj
Your everyday Linux distribution gone Super Saiyan.
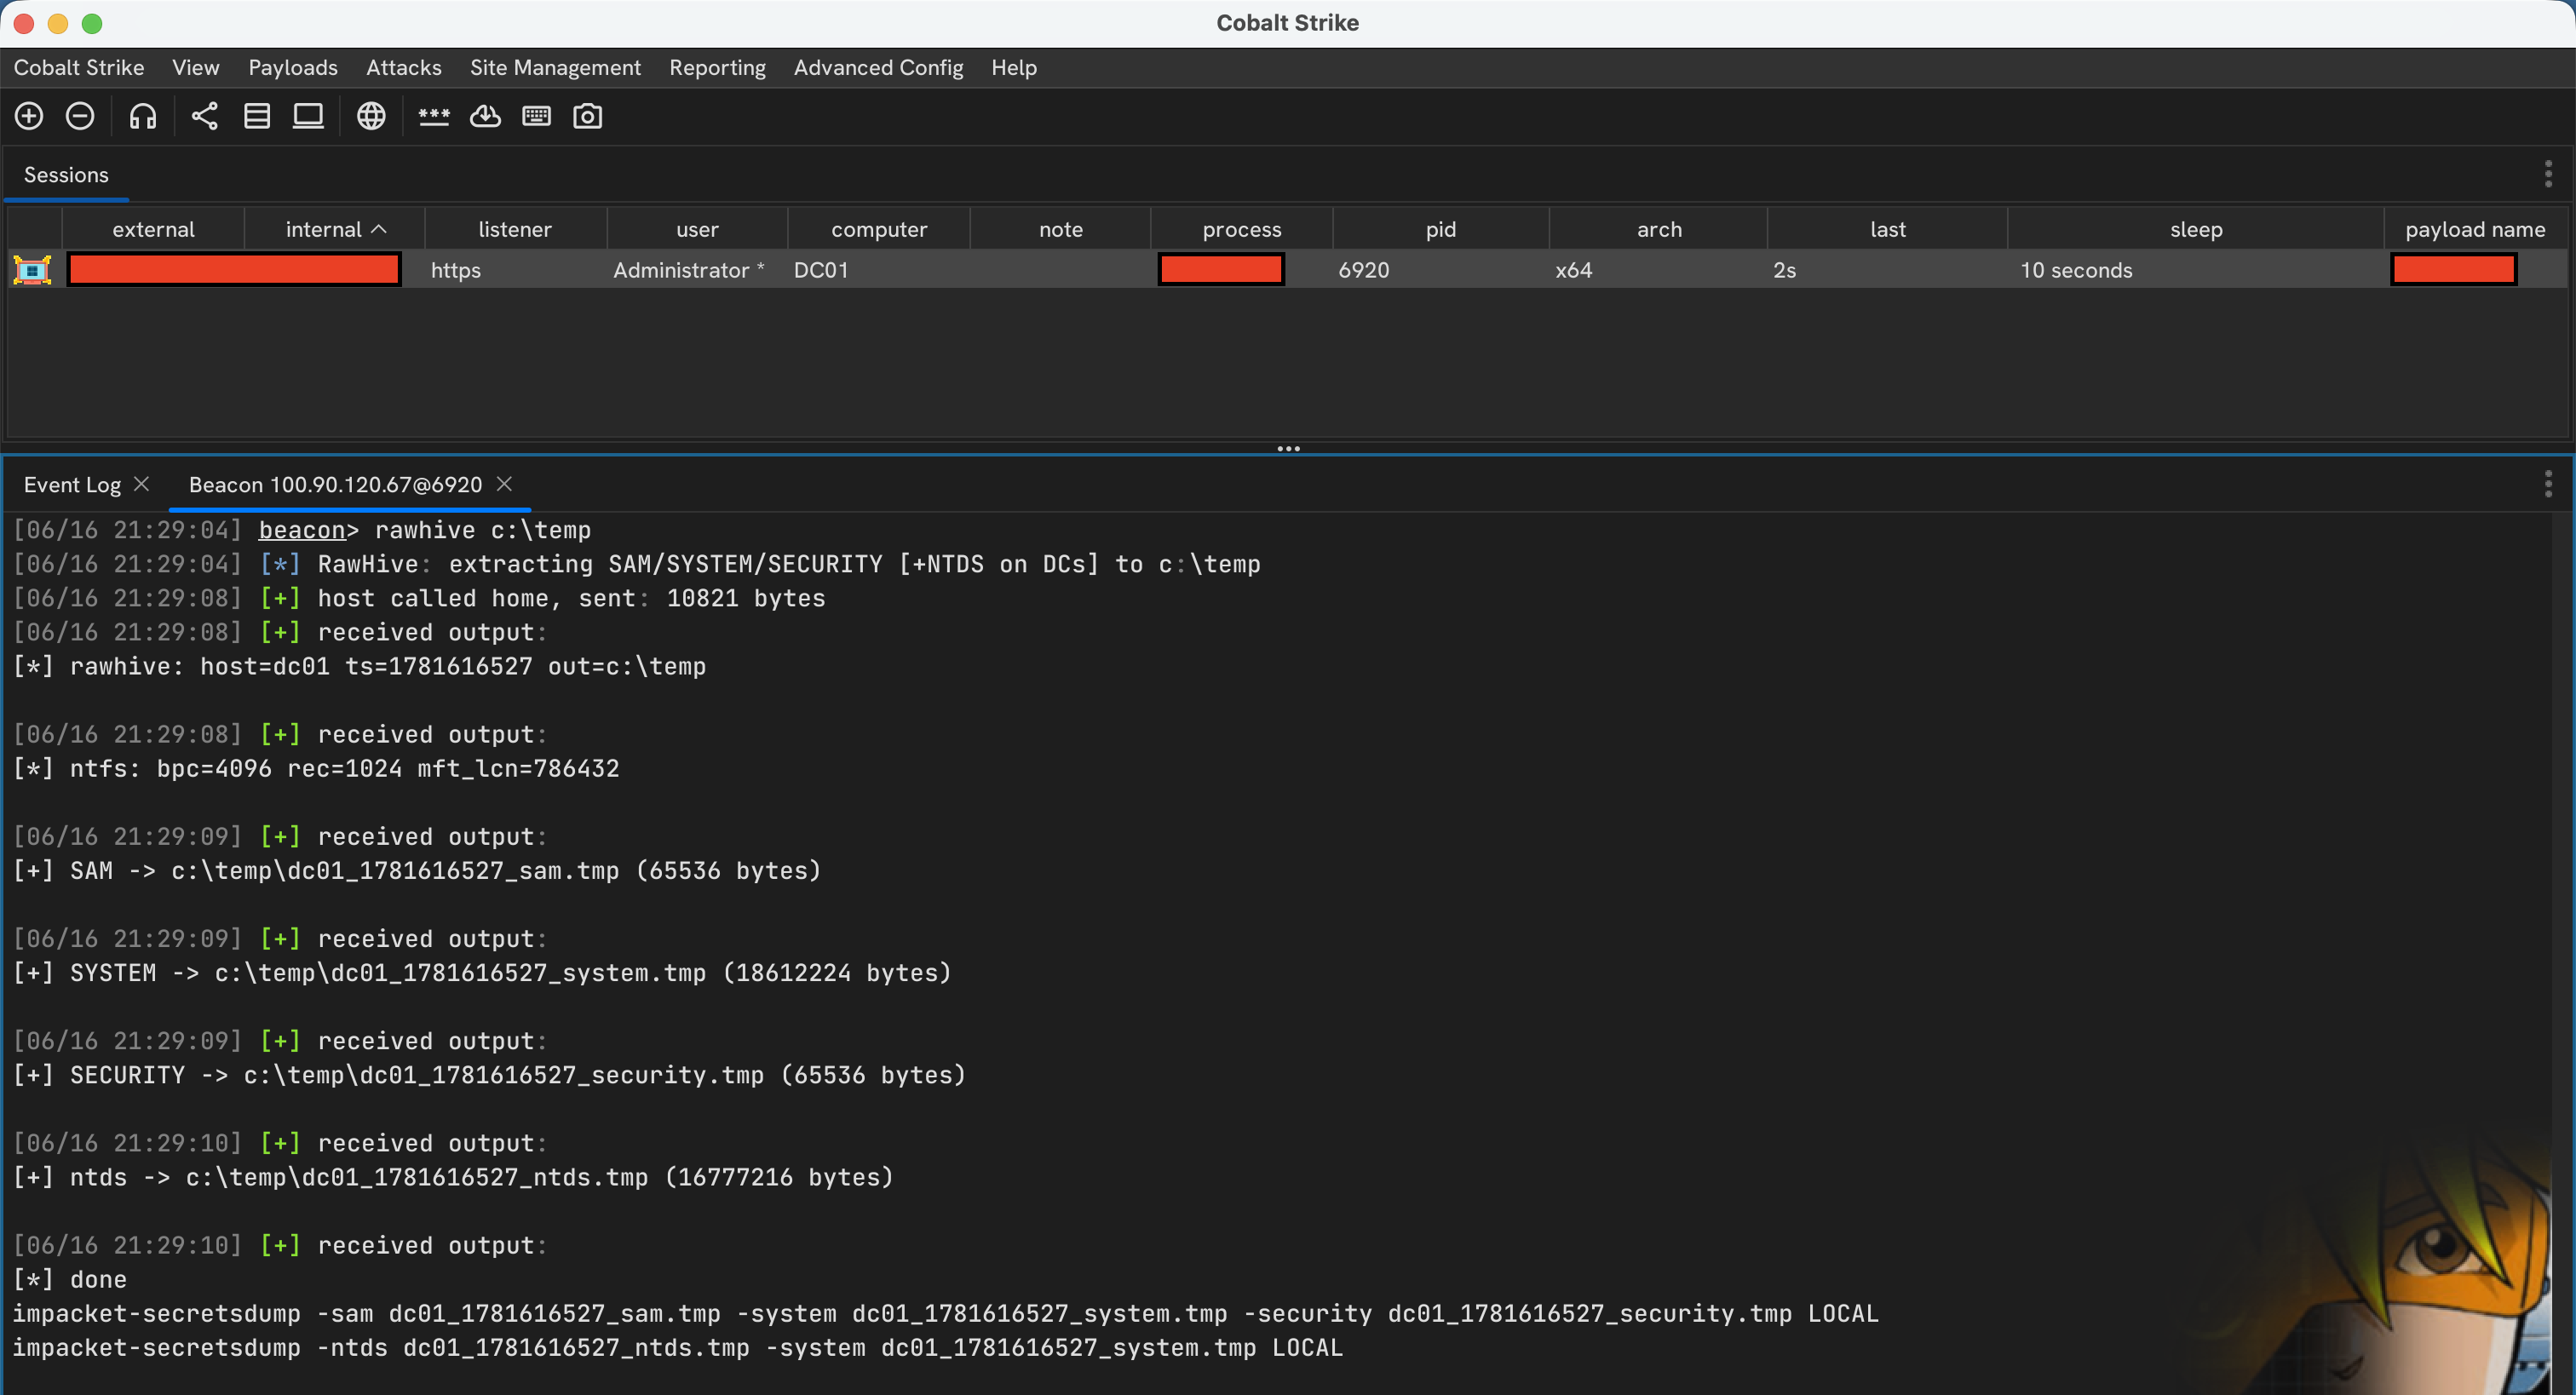 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 malwaretech/hiddendesktop
Create and enumerate hidden desktops.
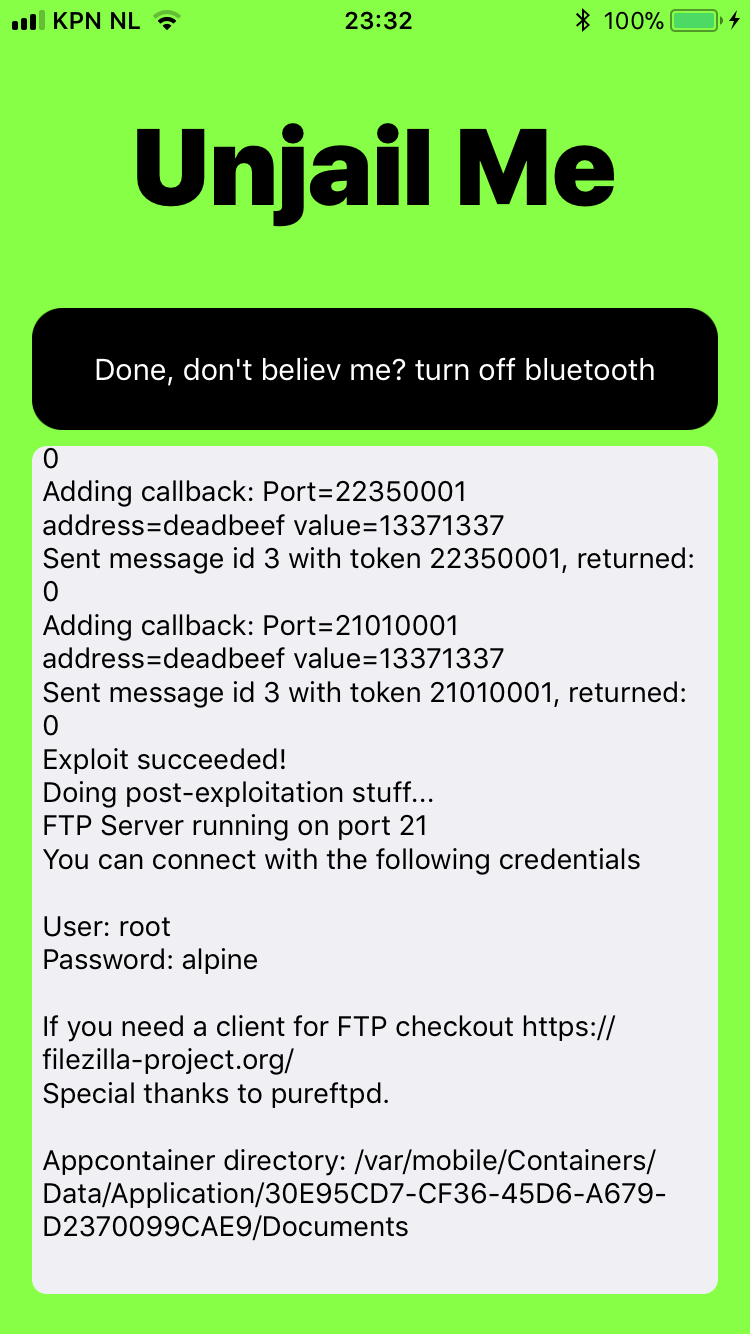 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script

