

Winshark
 airbus-cert/winshark
A wireshark plugin to instrument ETW
forensicslog-analysisnetwork-security+1
5934 years ago
airbus-cert/winsharkA wireshark plugin to instrument ETW
 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
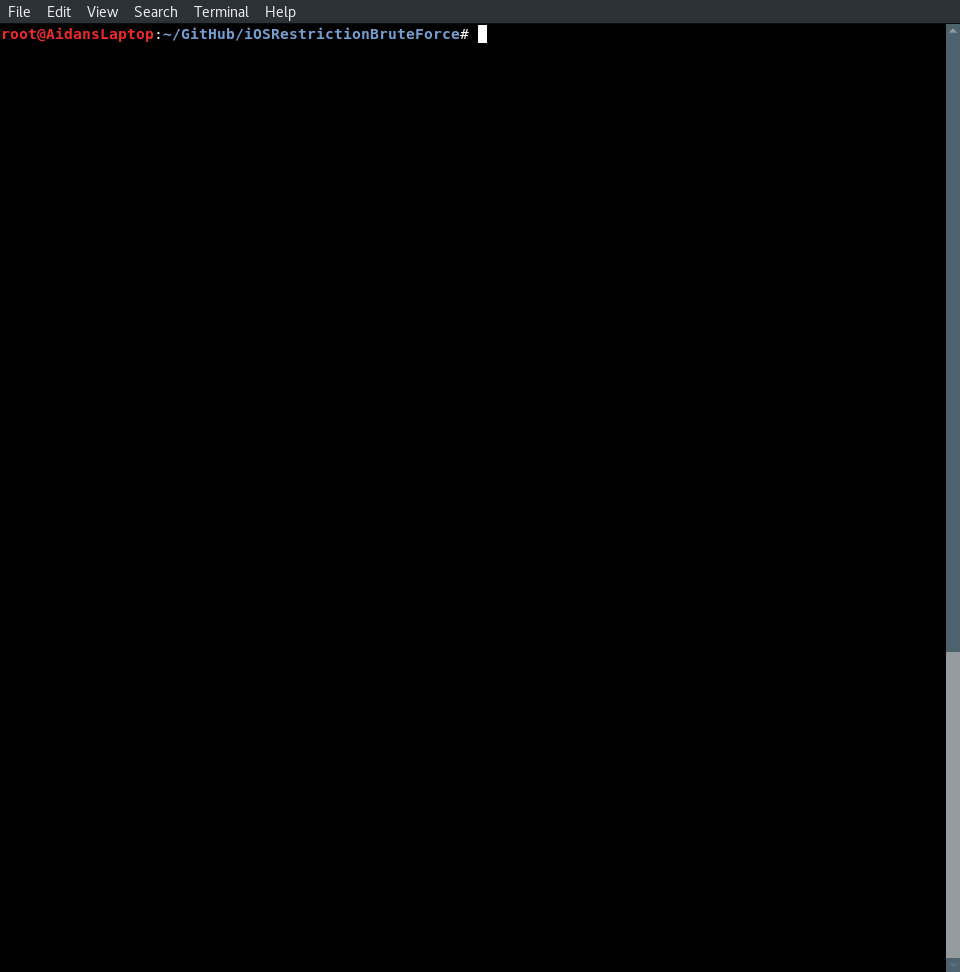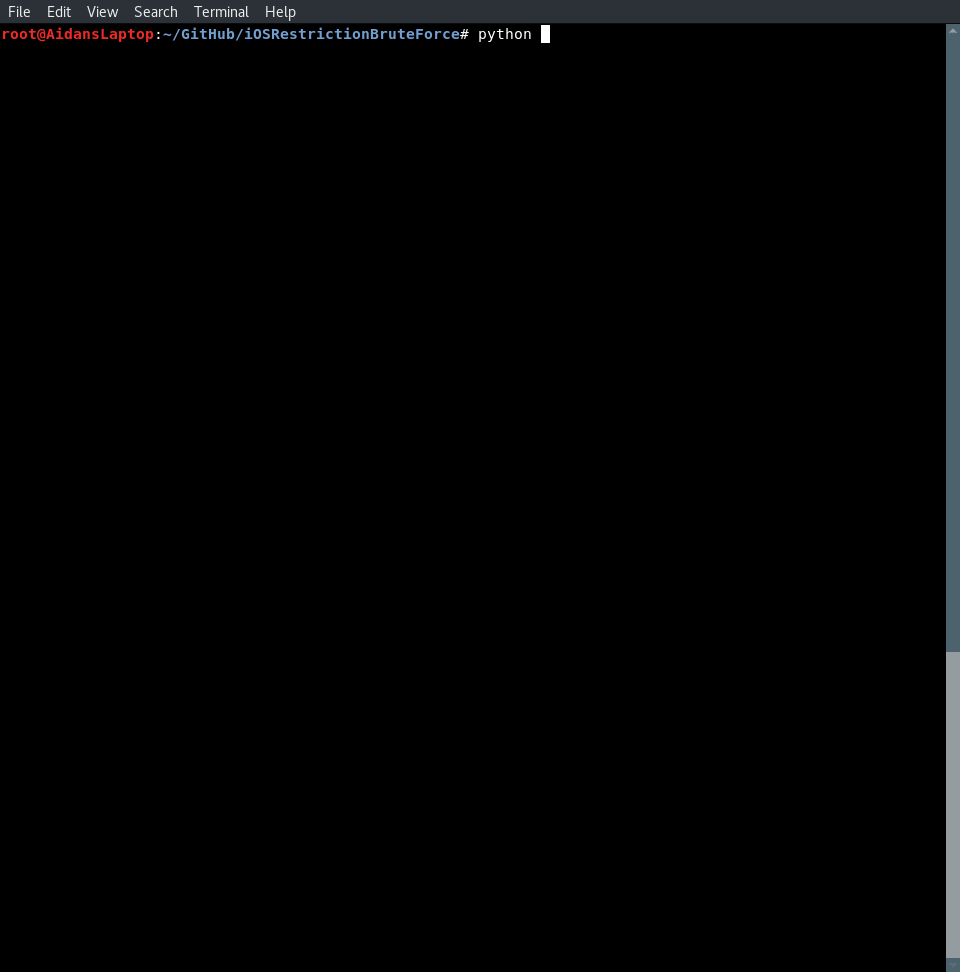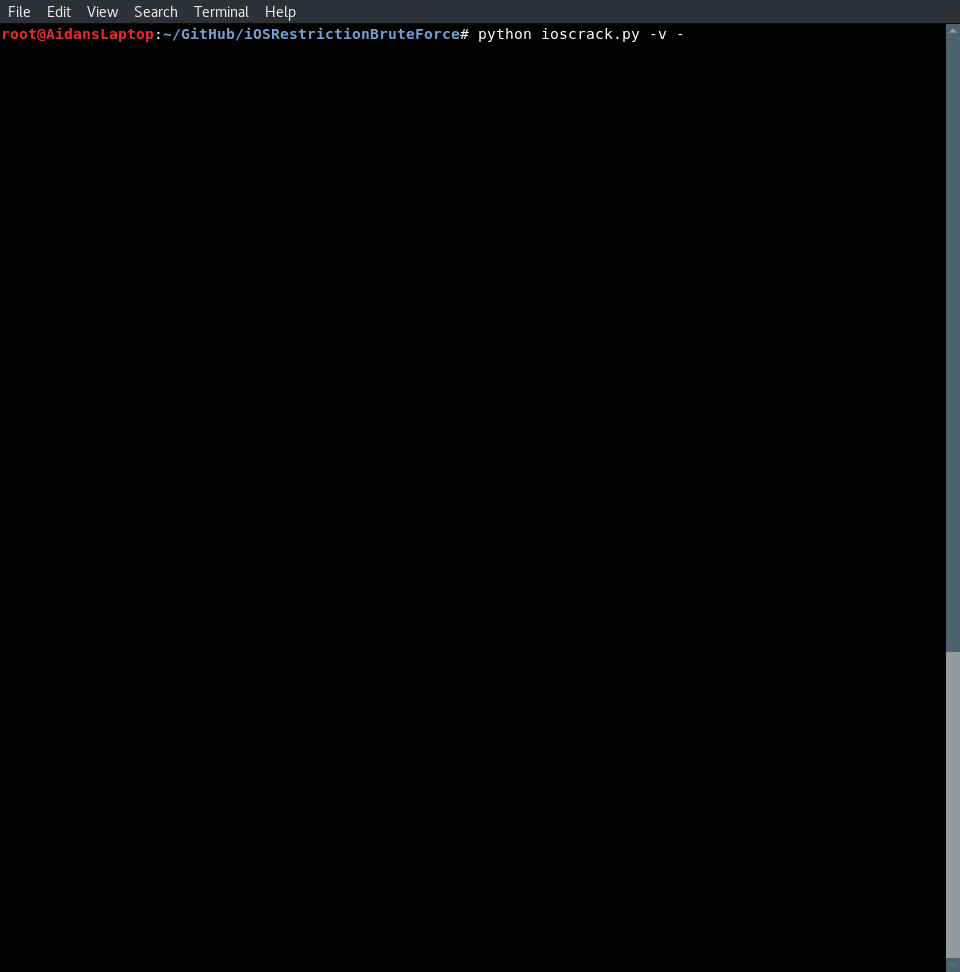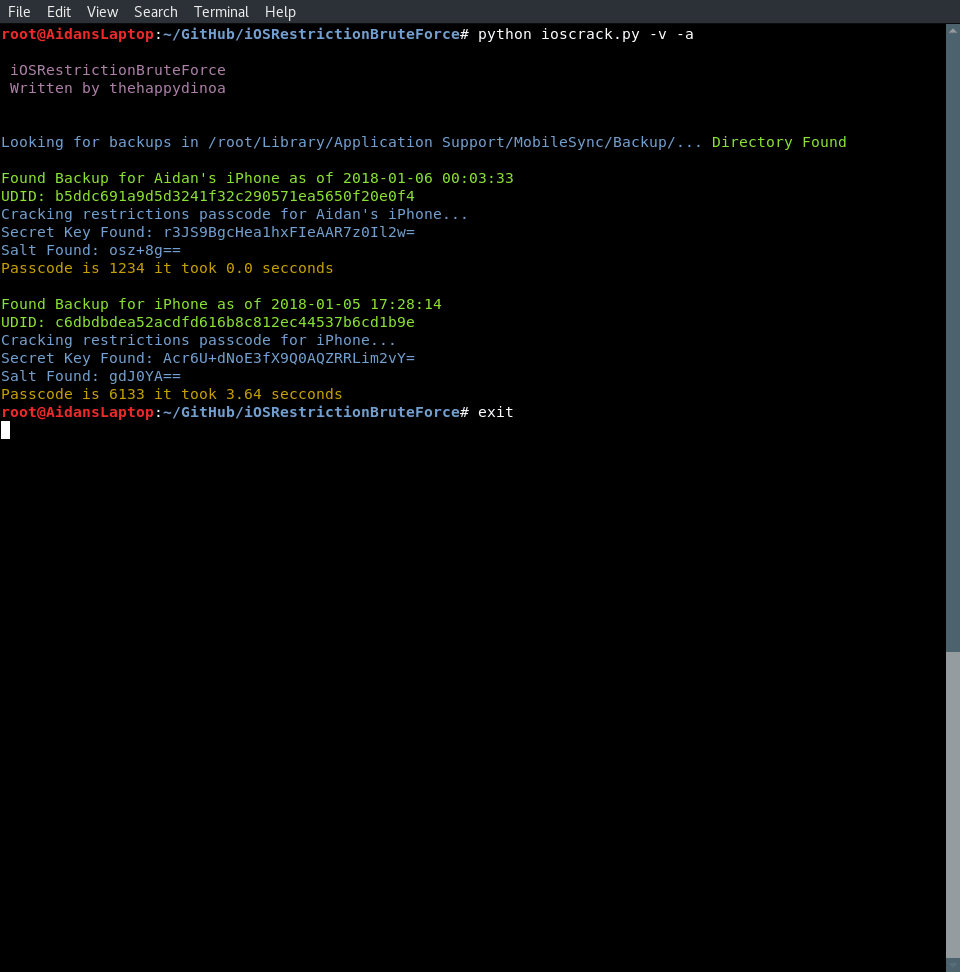 thehappydinoa/iosrestrictionbruteforce
Crack iOS Restriction Passcodes with Python
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 botherder/kraken
Cross-platform Yara scanner written in Go
 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder


 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.

 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 pinoywh1z/aoratoswin
A tool that removes traces of executed applications on Windows OS.