
Malcolm
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
digital-forensicsdns-analysisforensics+9
2.5k
cisagov/malcolmContainerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 circl/ail-framework
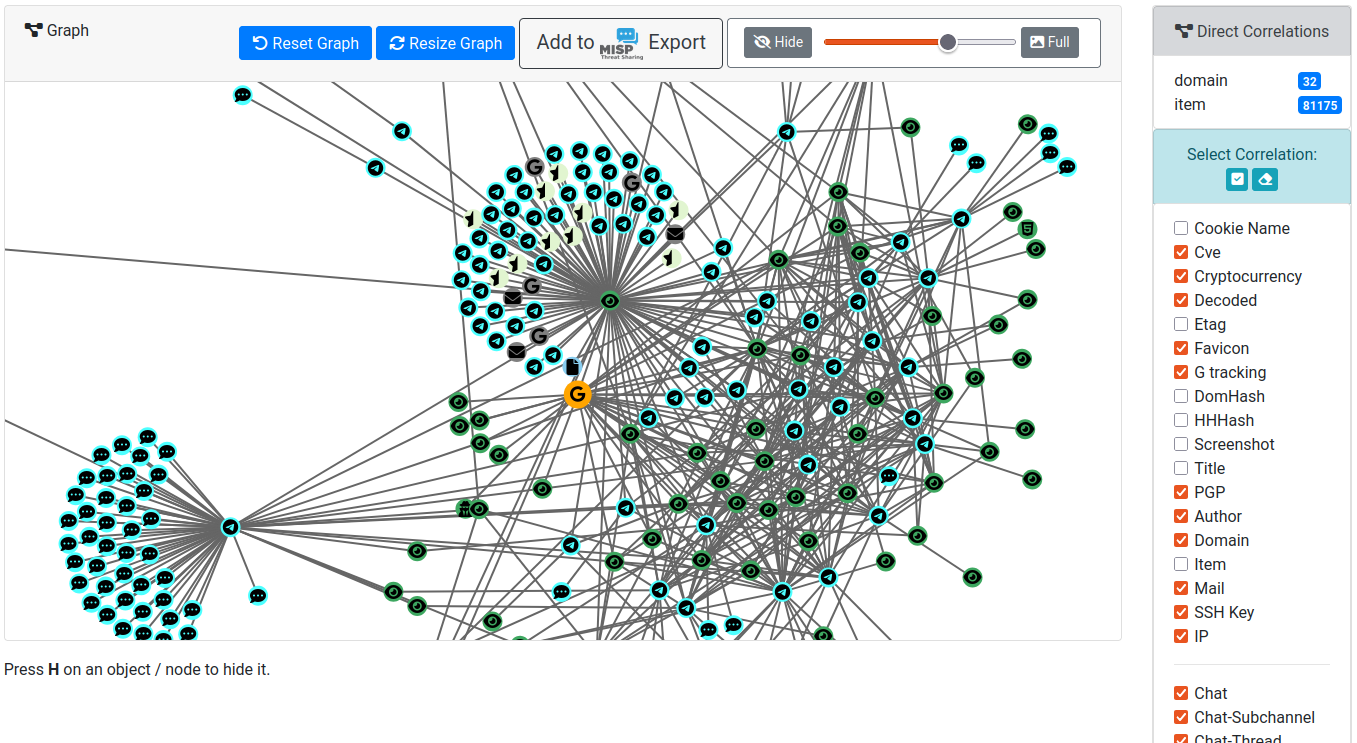
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 elevenpaths/foca
Tool to find metadata and hidden information in the documents.
 amnestytech/investigations
Indicators of Compromise from Amnesty International's cyber investigations
 lgandx/pcredz
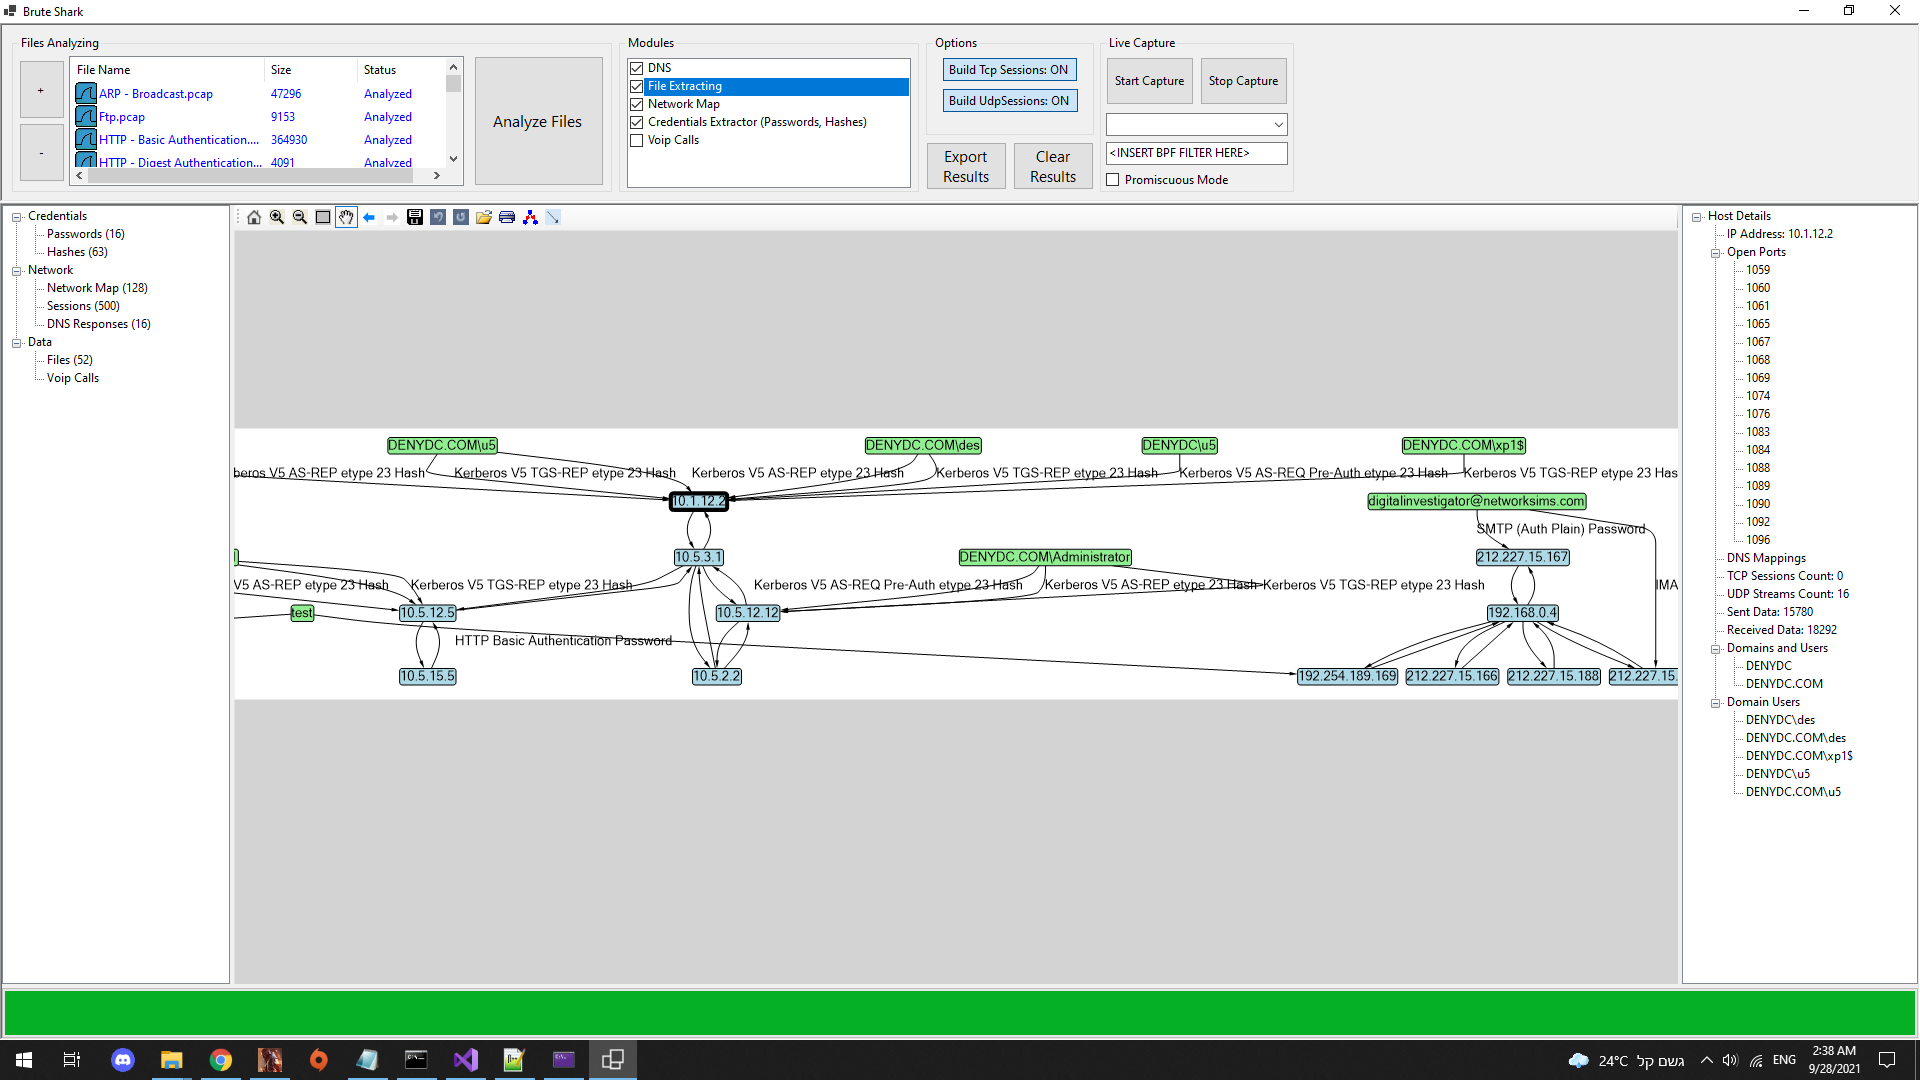
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 graniet/operative-framework
operative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
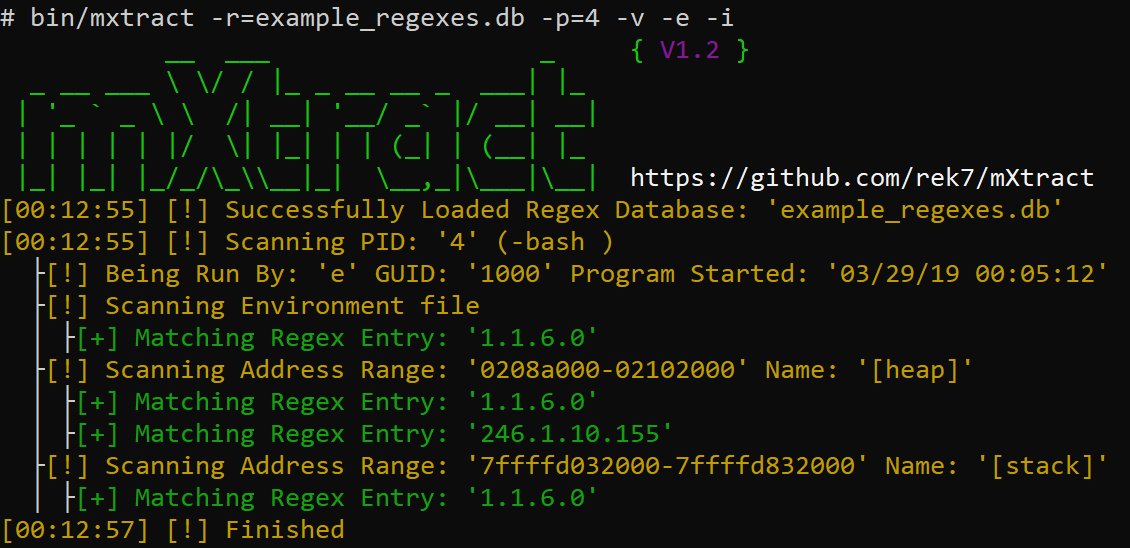 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
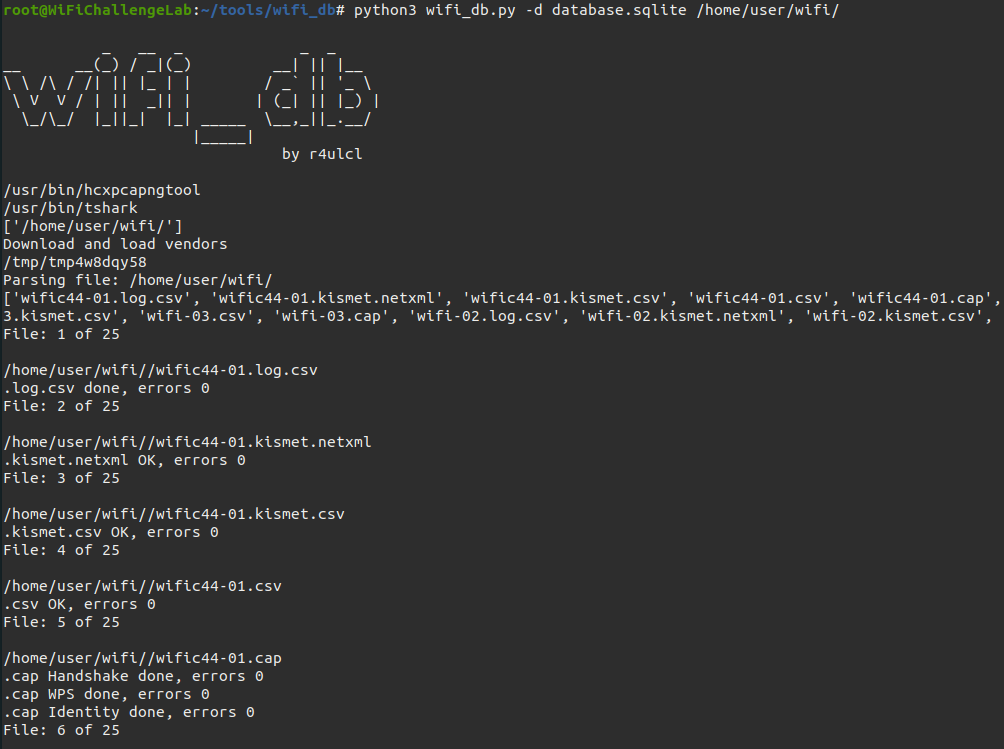 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark