IntelOwl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

Automated steganalysis platform that detects hidden data in images using 16 parallel analyzers, bit-layer visualization, and an in-app wiki for CTF…

Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…

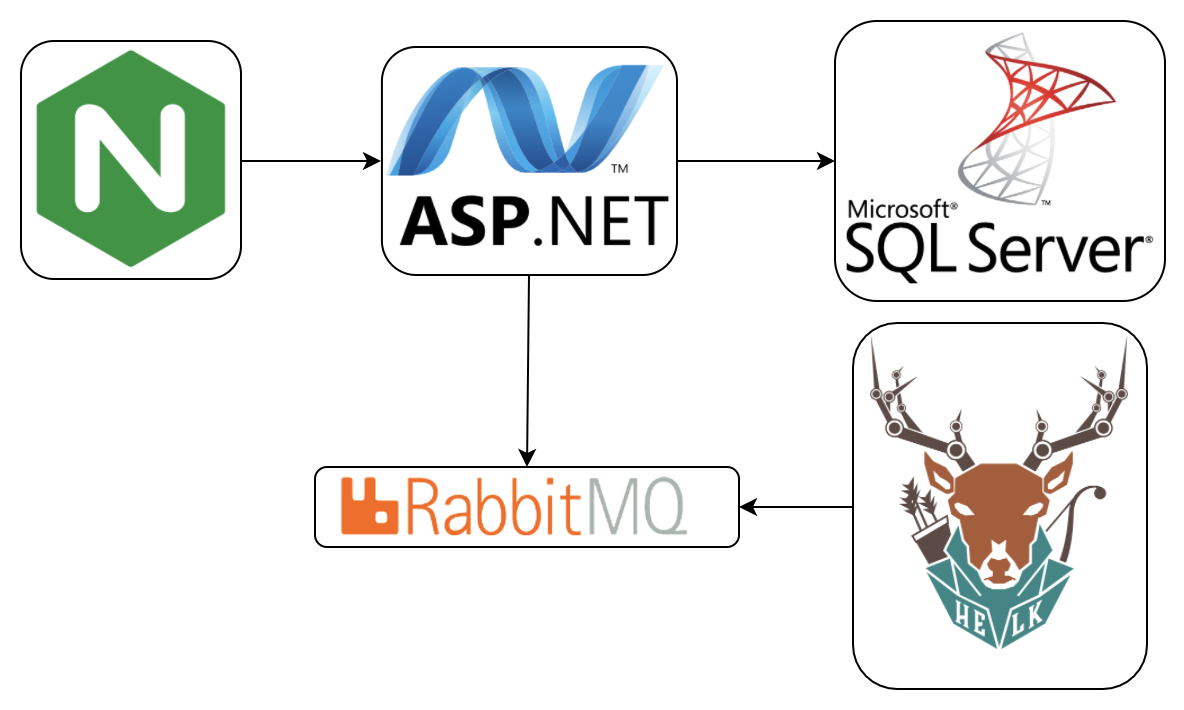
Automated, Collection, and Enrichment Platform

Incident Response collection and processing scripts with automated reporting scripts

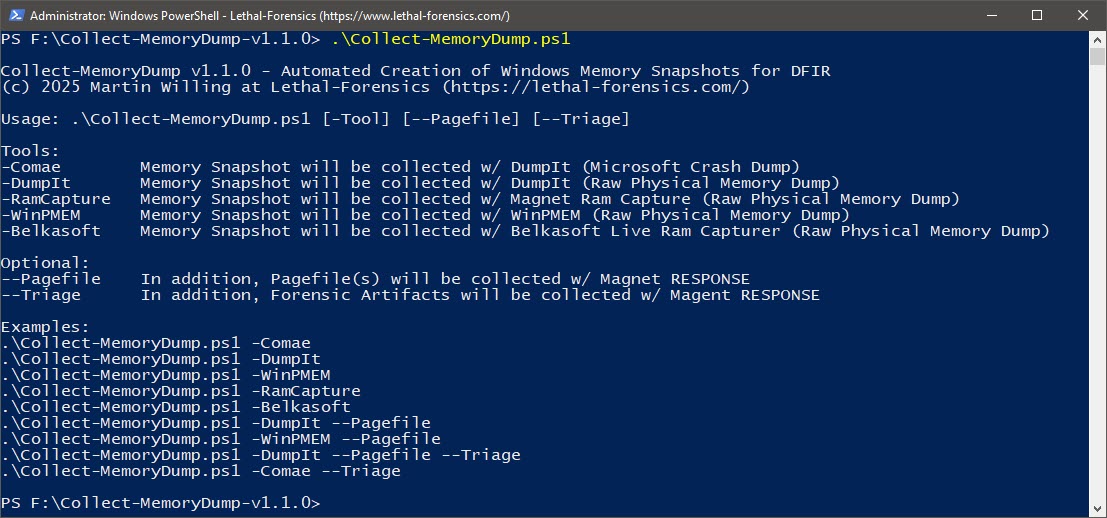
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

Automated YARA rule generation from the Cert Central compromised certificate database.

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.

Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)

Automated forensic script hunting for cve-2019-19781

Automated detection, assessment, and remediation toolkit for SharePoint CVE-2025-53770 (CVSS 9.8). Includes PowerShell scripts to verify patch…

The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…

Documented SOC automation workflow using Wazuh, N8N, Caldera, and Velociraptor

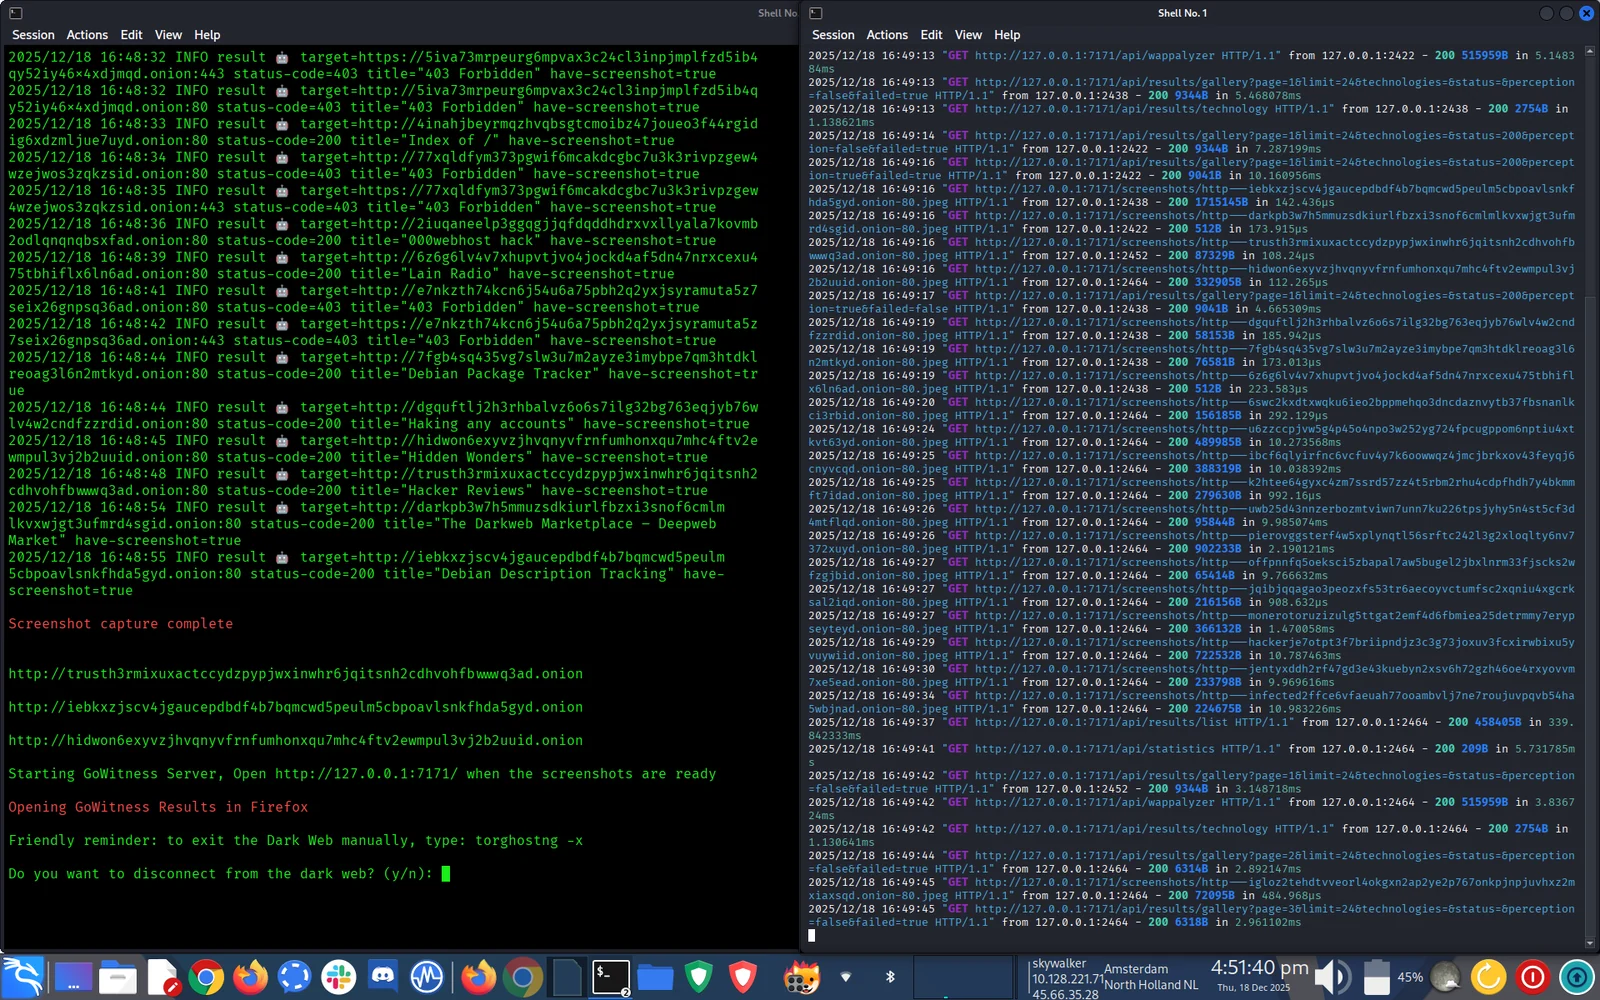
CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.