

RawHive
 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
digital-forensicsdisk-forensicsexploitation+4
112
nmht3t/rawhiveCobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
 keyuraghao/cve-2025-20260
Python-based exploit for CVE-2025-20260 that generates a malicious PDF file and includes core dump analysis capabilities for vulnerability…
 233laoliu/mt6985-cve-2026-43499
CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 malwaretech/hiddendesktop
Create and enumerate hidden desktops.
 viper-framework/viper
Binary analysis and management framework
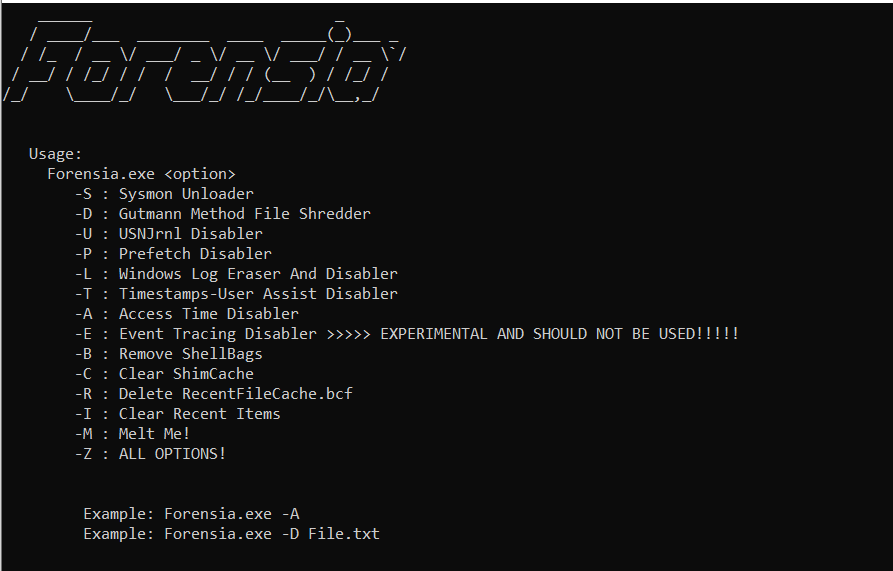 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
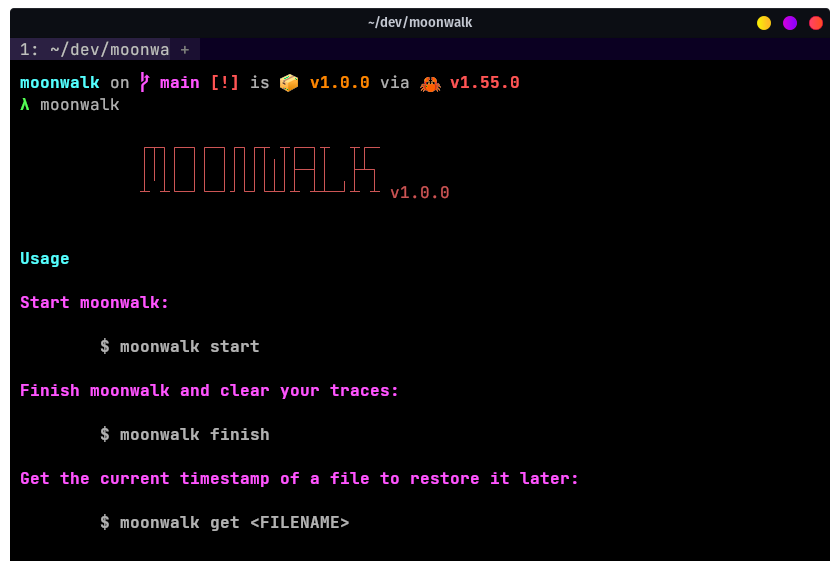 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
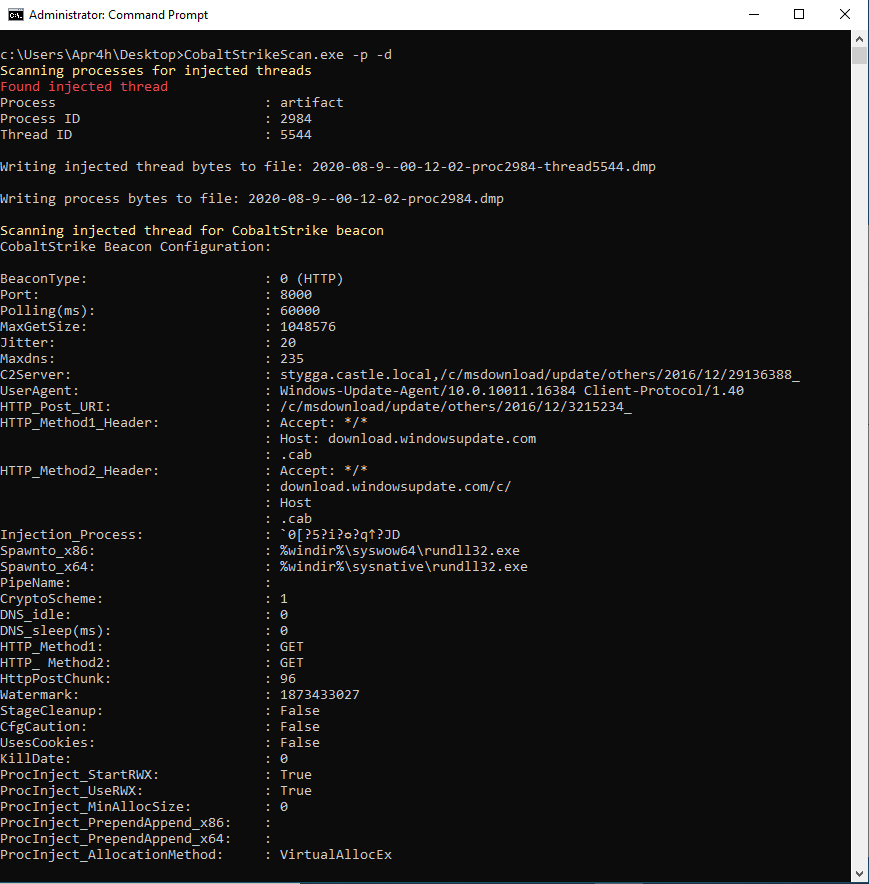 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 grishinpv/poc_cve-2021-36934
POC experiments with Volume Shadow copy Service (VSS)
 omriher/captipper
Malicious HTTP traffic explorer
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
 joydragon/detect-cve-2018-20250
Herramienta para revisar si es que un payload tiene componente malicioso de acuerdo a CVE-2018-20250
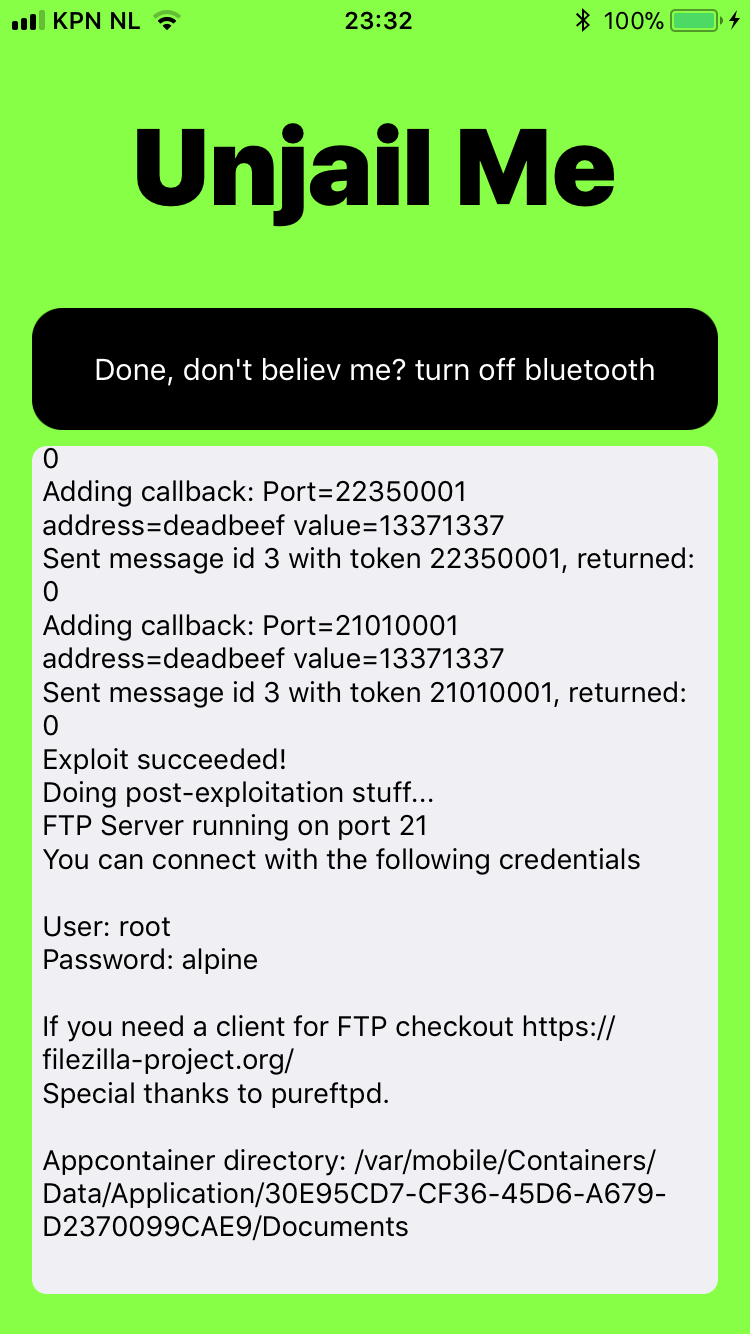 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
