
magika
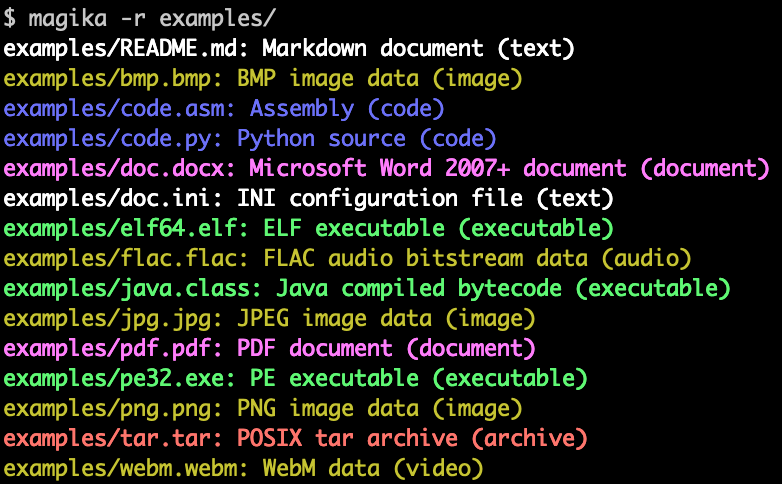
 google/magika
Fast and accurate AI powered file content types detection
code-analysisforensicsgeneral-purpose-utilities+3
17.9k1 day ago
google/magikaFast and accurate AI powered file content types detection
 threatray/threat-research
IoCs and YARA rules from Threatray's Threat Research

 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…

 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 rbidou/llm-forensics
Weight-level LLM forensics: diff model weights, detect fine-tunes, merges and disguised derivatives, and surface tokens a fine-tune promotes or…

 zardus/ctf-tools
Some setup scripts for security research tools.
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 chrislpjones/plex2shell-check
Read-only Linux check for Plex2Shell (CVE-2026-96652/-96654/-96655/-96656) exploitation and the XMRig/proxy payloads seen in the wild
 cristianzsh/amcache-evilhunter
:alien: Identifies suspicious executables in Amcache.hve; record filtering and VirusTotal integration
 eddyflores100-lang/taikotalent-phishing-iocs
IoCs, attack chain & detection for the taikotalent.xyz fake-Taiko-recruiter campaign delivering a self-deleting Bash trojan via the paste-in-terminal…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…