
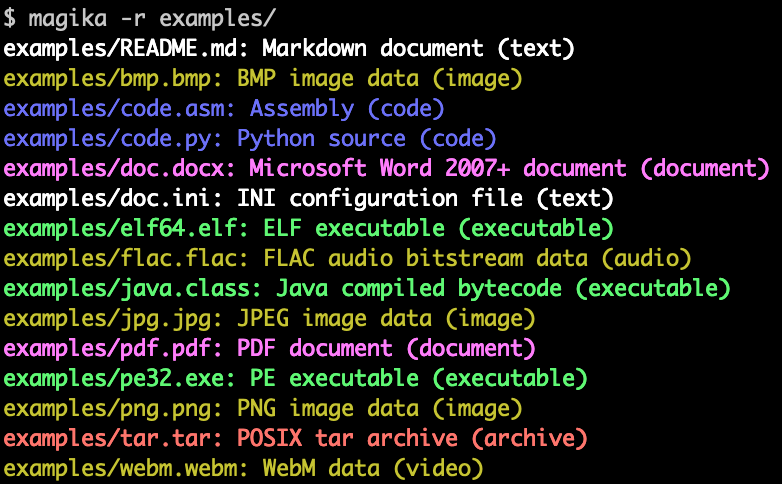
magika
 google/magika
Fast and accurate AI powered file content types detection
code-analysisforensicsgeneral-purpose-utilities+3
google/magikaFast and accurate AI powered file content types detection


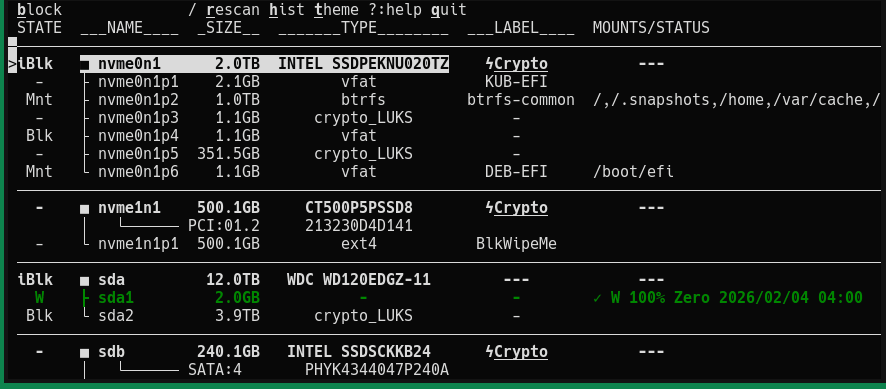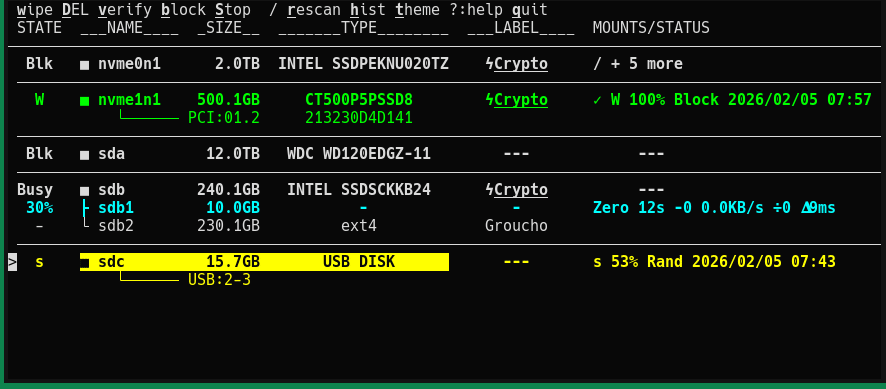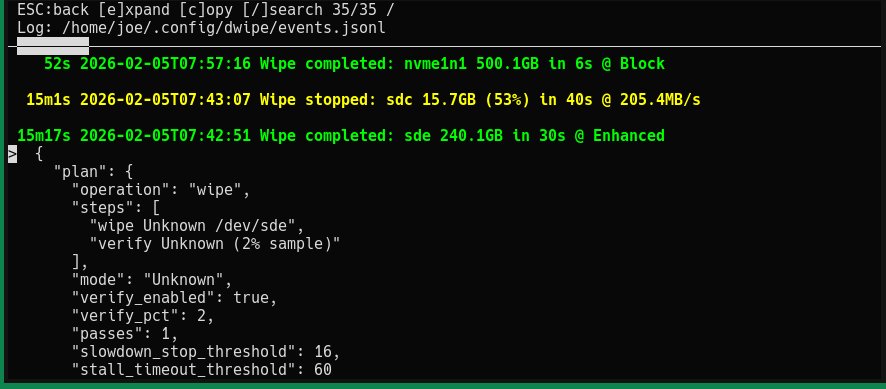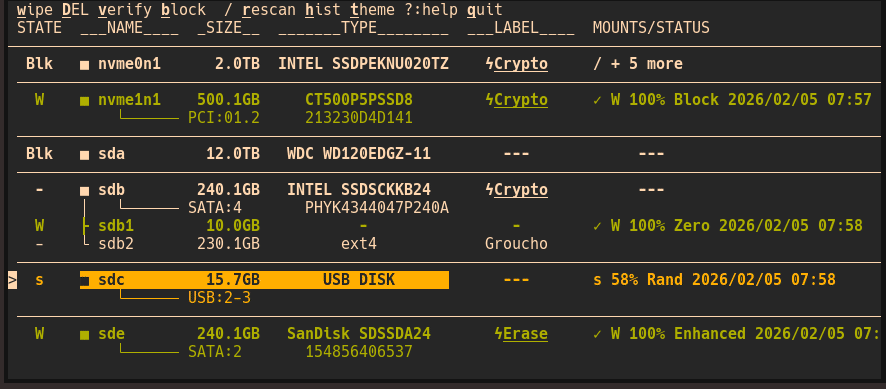 joedefen/dwipe
Tool to securely and efficiently wipe devices and partiitions for Linux
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 velocidex/winpmem
The multi-platform memory acquisition tool.
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 cleasbycode/jdvrif
Steganography Tool for JPG Images
 simsong/bulk_extractor
This is the development tree. Production downloads are at: