
pastokrapacefleciks
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
digital-forensicsforensicslog-analysis+2
nu11secur1ty/pastokrapacefleciksAnalyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 mhils/honeyproxy
This project is now part of @mitmproxy.
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 lgandx/pcredz
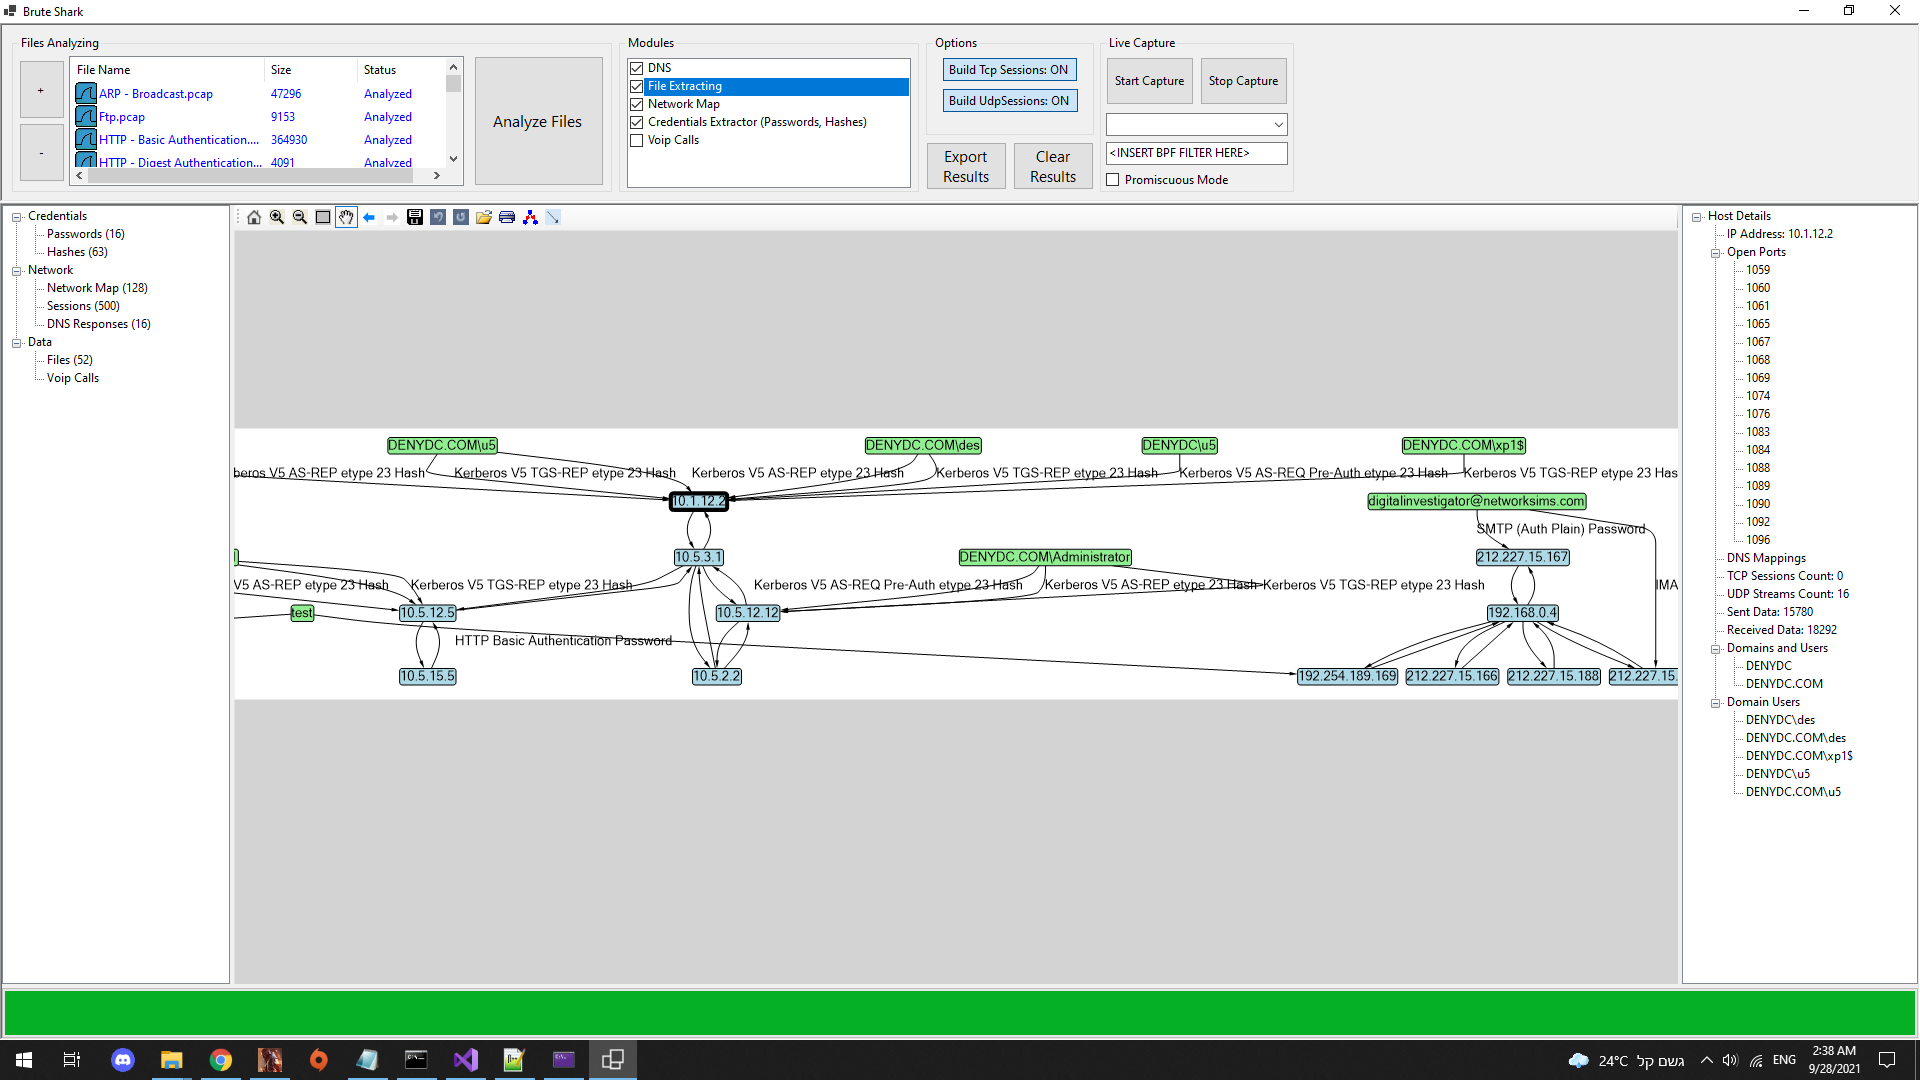
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 malejdj/cve-2026-30784-rustdesk-poc
CVE-2026-30784: RustDesk hbbs Traffic Amplification PoC & PCAP Analysis
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
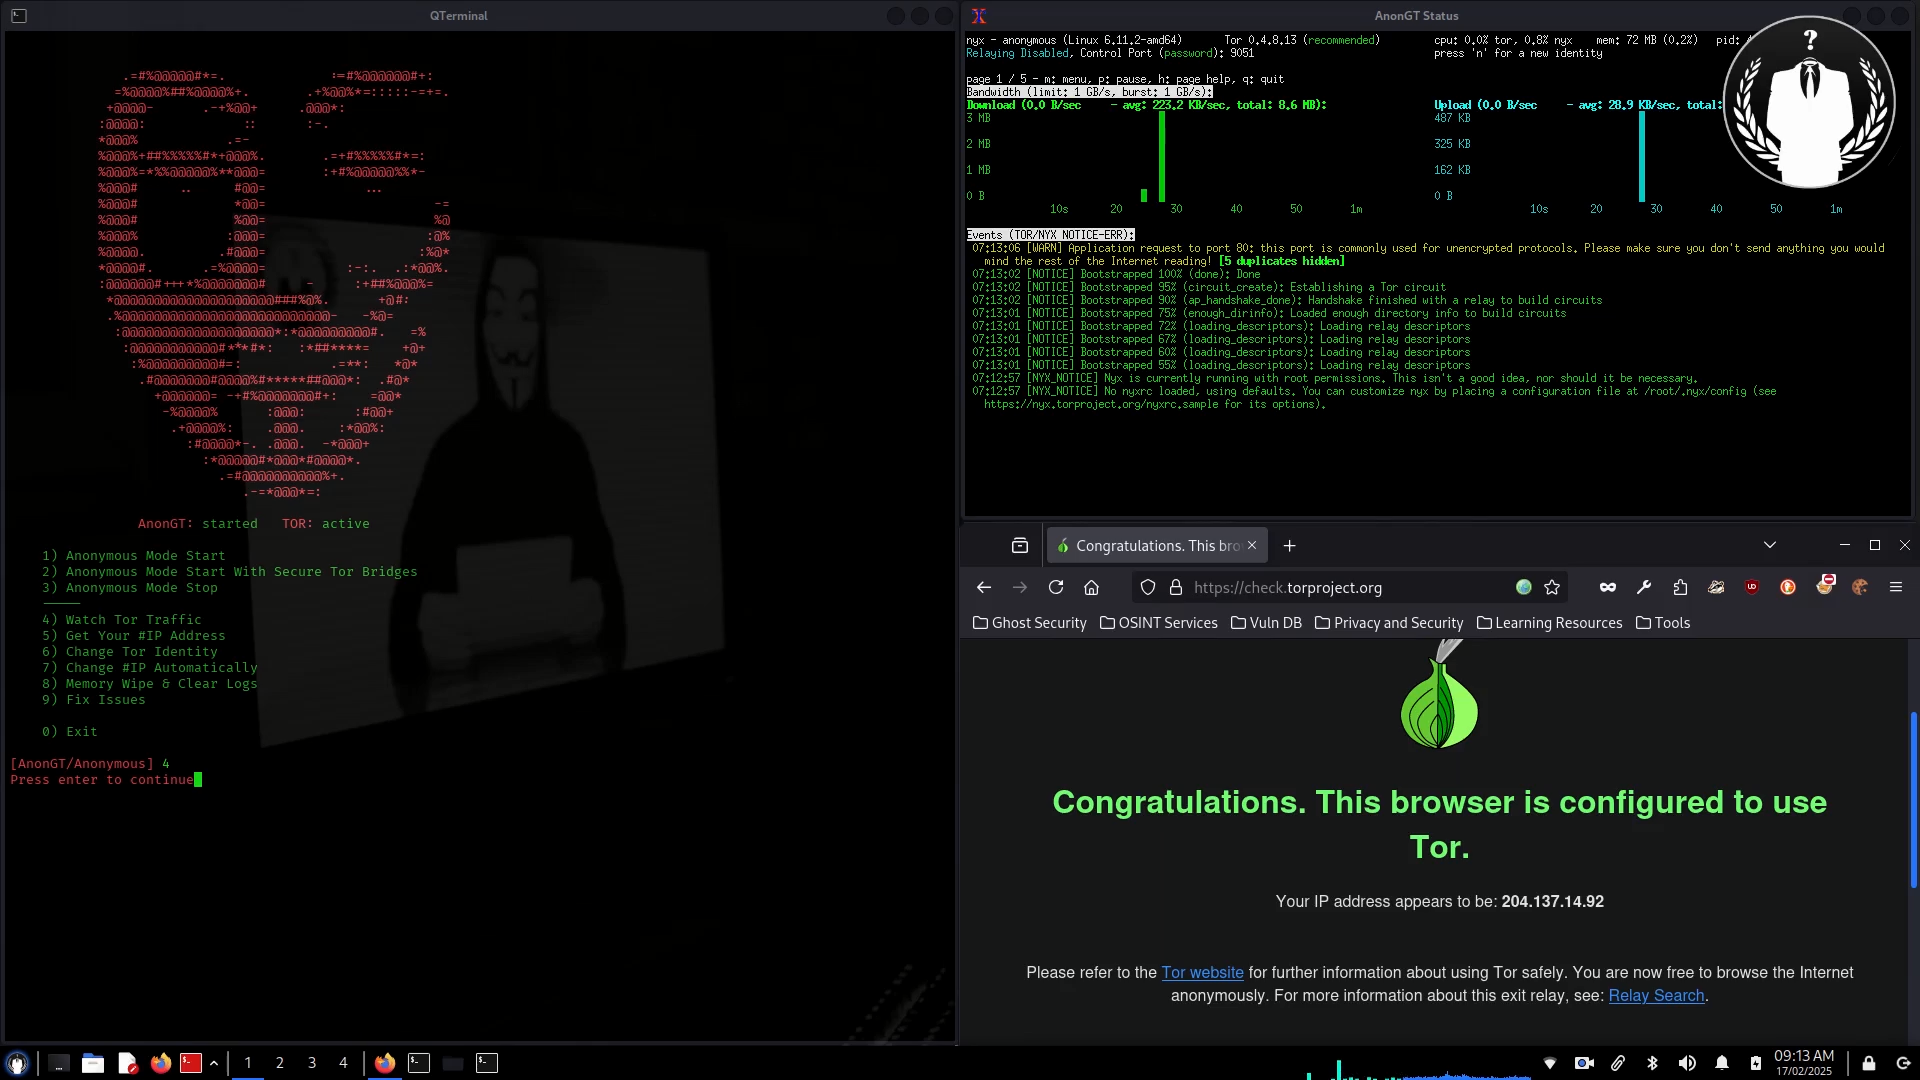 gt0day/anongt
Redirect All Traffic Through Tor Network For Kali Linux