

ptcpdump
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k
mozillazg/ptcpdumpeBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
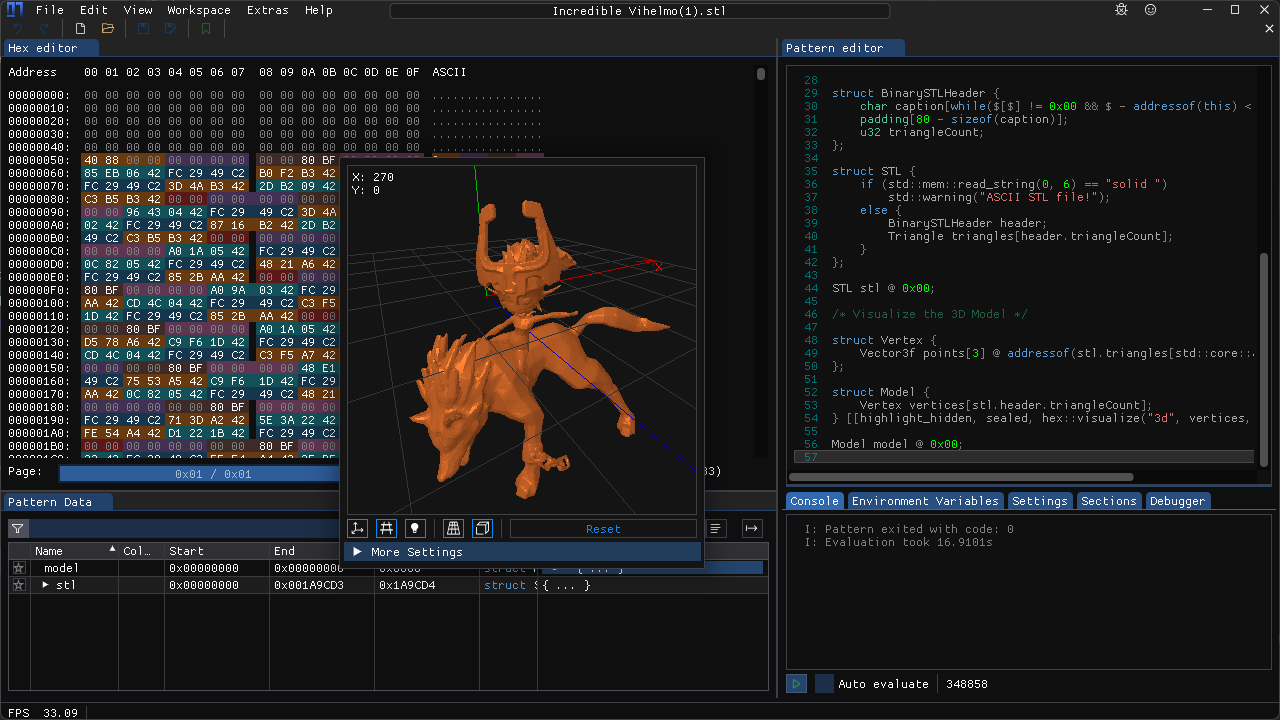 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 secrary/ssma
SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]
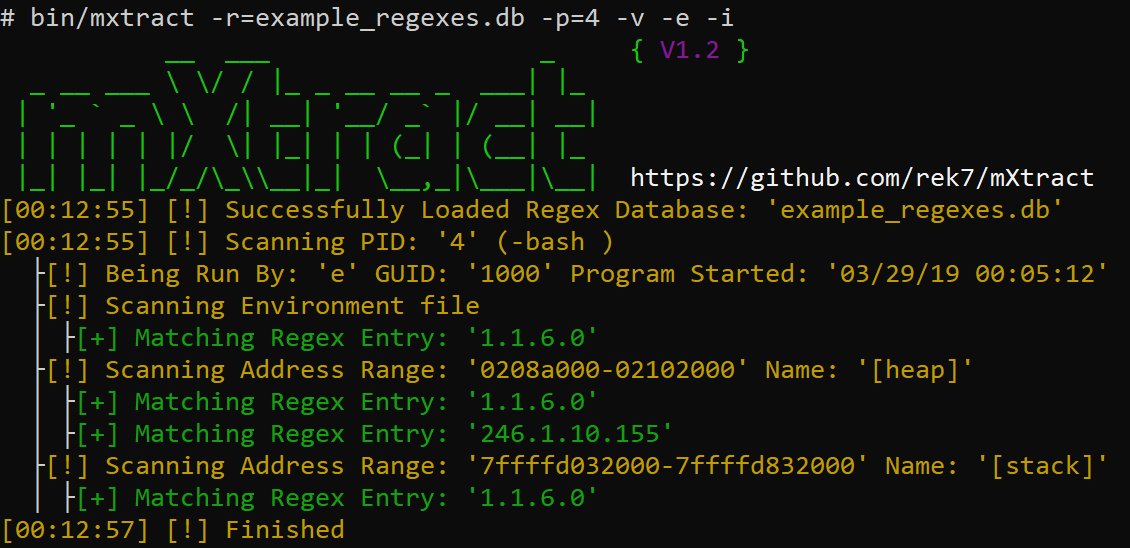 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 tstillz/webshell-analyzer
Web shell scanner and analyzer.
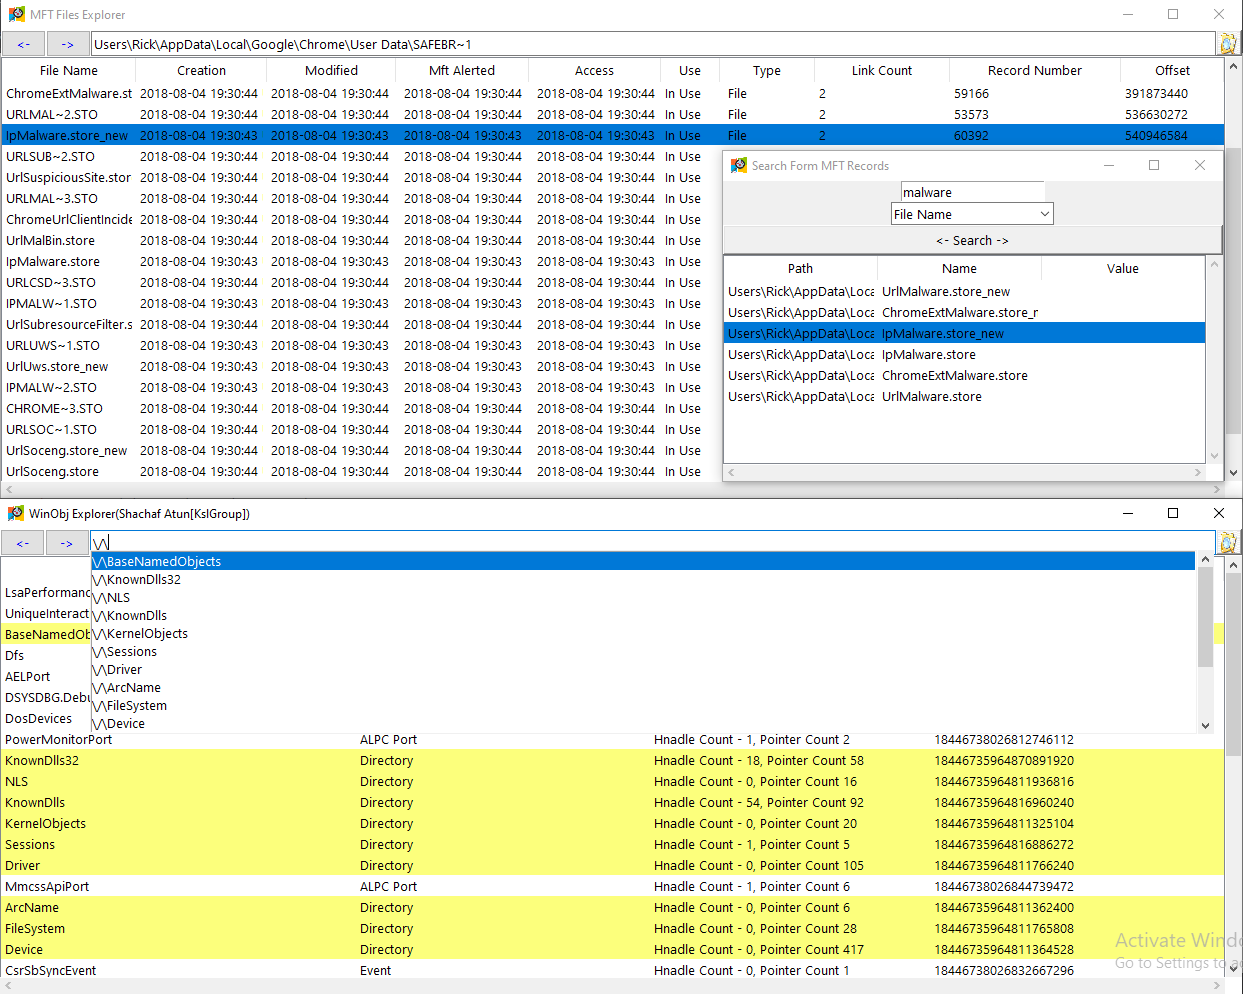 memoryforensics1/vol3xp
Volatility Explorer Suit (volatility 3)
 t-tani/yama-dev
Yet Another Memory Analyzer for malware detection
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…

 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…