Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
95 results
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
19716 days ago
volatility-plugins preview

volatility-plugins

GitHubwithsecurelabs/volatility-plugins

Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
digital-forensicsforensicsincident-response+2
118 years ago
memory-carving-scripts preview

memory-carving-scripts

GitHubwithsecurelabs/memory-carving-scripts

Scripts for extracting useful information from infected memory dumps
digital-forensicsforensicsincident-response+2
108 years ago
detect_CVE-2026-21509 preview

detect_CVE-2026-21509

GitHubdecalage2/detect_cve-2026-21509

YARA rule and python script to detect potential exploits for the CVE-2026-21509 vulnerability in MS Office


forensicsmalware-analysisvulnerability-analysis
38 months ago
refinery preview

refinery

GitHubbinref/refinery

High Octane Triage Analysis

binary-analysiscryptographyforensics+4
87810 days ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2684 years ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files
binary-analysisforensicsmalware-analysis+2
998 months ago
evtx-baseline preview

evtx-baseline

GitHubnextronsystems/evtx-baseline

A repository hosting example goodware evtx logs containing sample software installation and basic user interaction
curated-resourcesdigital-forensicseducation+2
932 years ago
PowerShellProfiler preview

PowerShellProfiler

GitHubal1ex/powershellprofiler

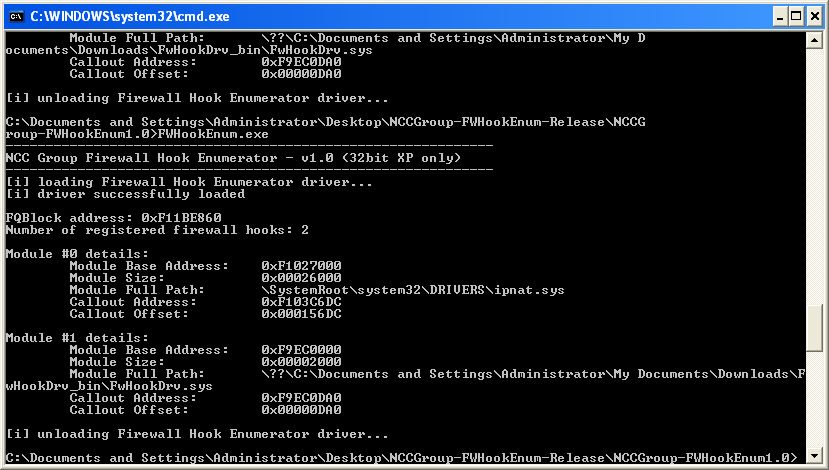
PowerShellProfiler
code-analysisforensicsmalware-analysis+2
5 years ago
WindowsFirewallHookDriverEnumeration preview

WindowsFirewallHookDriverEnumeration

GitHubnccgroup/windowsfirewallhookdriverenumeration

Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
digital-forensicsforensicsincident-response+2
2111 years ago
amcache-evilhunter preview

amcache-evilhunter

GitHubcristianzsh/amcache-evilhunter

Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
digital-forensicsforensicsincident-response+2
1144 days ago
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis
binary-analysiscryptographyforensics+3
908 years ago
Memory-analysis preview

Memory-analysis

GitHubbedazzlinghex/memory-analysis

Contains tools to perform malware and forensic analysis in Memory

digital-forensicsforensicsincident-response+3
48 years ago
flowinspect preview

flowinspect

GitHub7h3ram/flowinspect

A Network Inspection Tool

forensicsfuzzingintrusion-detection+5
829 years ago
hashID preview

hashID

GitHubpsypanda/hashid

Software to identify the different types of hashes -
forensicshash-analysisinformation-gathering+3
1.5k11 years ago
ramnit_traffic_parser preview

ramnit_traffic_parser

GitHubnao-sec/ramnit_traffic_parser

Parsing Ramnit's traffic
command-and-controldigital-forensicsforensics+3
48 years ago
yara preview

yara

GitHubvirustotal/yara

The pattern matching swiss knife

forensicsmalware-analysisstatic-analysis+2
10.0k0 days ago
Previous123456Next