Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
remove-ai-watermarks preview

remove-ai-watermarks

GitHubwiltodelta/remove-ai-watermarks

Remove visible and invisible AI watermarks and provenance metadata from images and video. Python library and CLI for SynthID, C2PA, EXIF, IPTC, XMP,…

cryptographydata-recoverydigital-forensics+6
5.9k
2 days ago
USB Spy preview

USB Spy

GitLabchristophe.duvernois/usb-spy

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…

digital-forensicsexploitationfirmware-analysis+6
32 months ago
ics-forensics-tools preview

ics-forensics-tools

GitHubmicrosoft/ics-forensics-tools

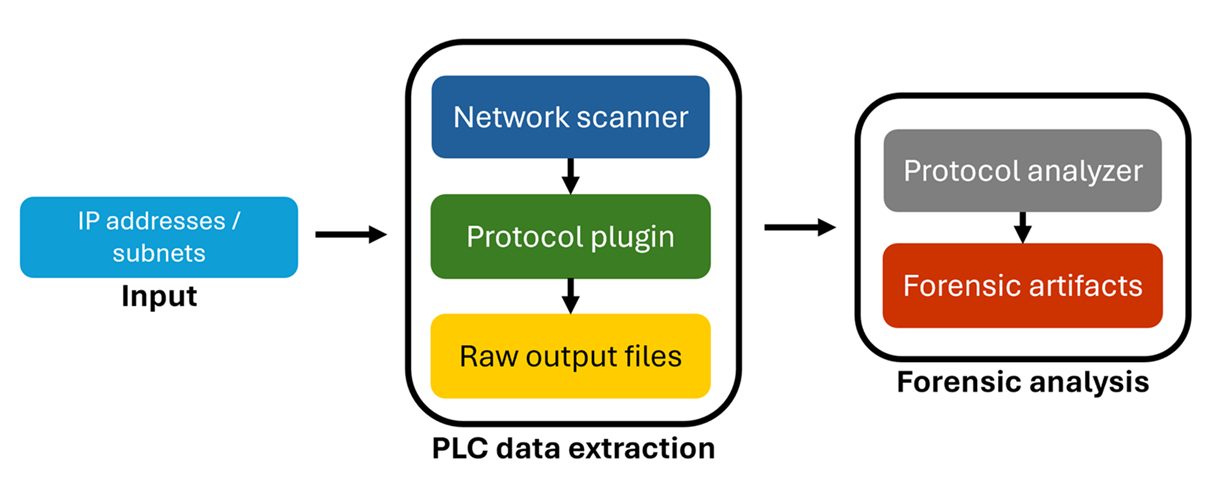
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…

digital-forensicsforensicsincident-response+2
3741 year ago
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…

cloud-securitycontainer-securitydigital-forensics+5
1.3k3 days ago
BurpMetaFinder preview

BurpMetaFinder

GitHubjosue87/burpmetafinder

Burp Suite extension for extracting metadata from files

forensicsinformation-gatheringosint+1
205 years ago
MongoBleed-DFIR-Triage-Script-CVE-2025-14847 preview

MongoBleed-DFIR-Triage-Script-CVE-2025-14847

GitHubjemhadar/mongobleed-dfir-triage-script-cve-2025-14847

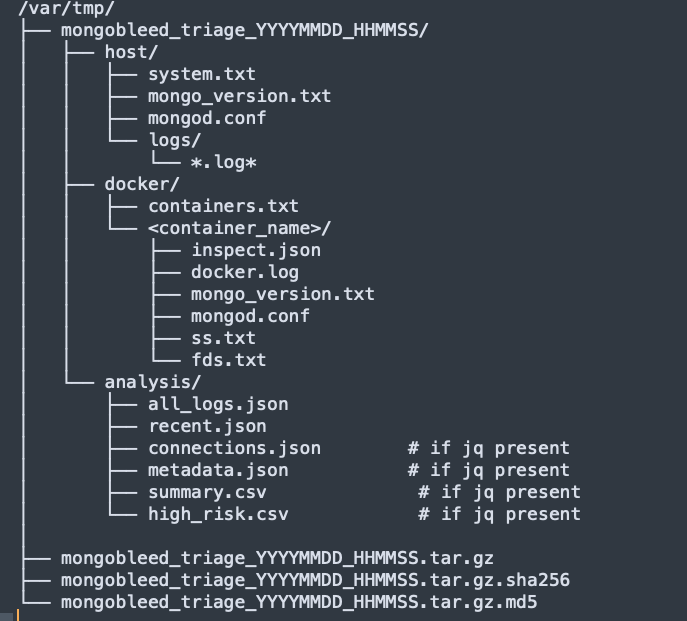
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

container-securitydatabase-securitydigital-forensics+5
9 months ago
LOLDrivers preview

LOLDrivers

GitHubmagicsword-io/loldrivers

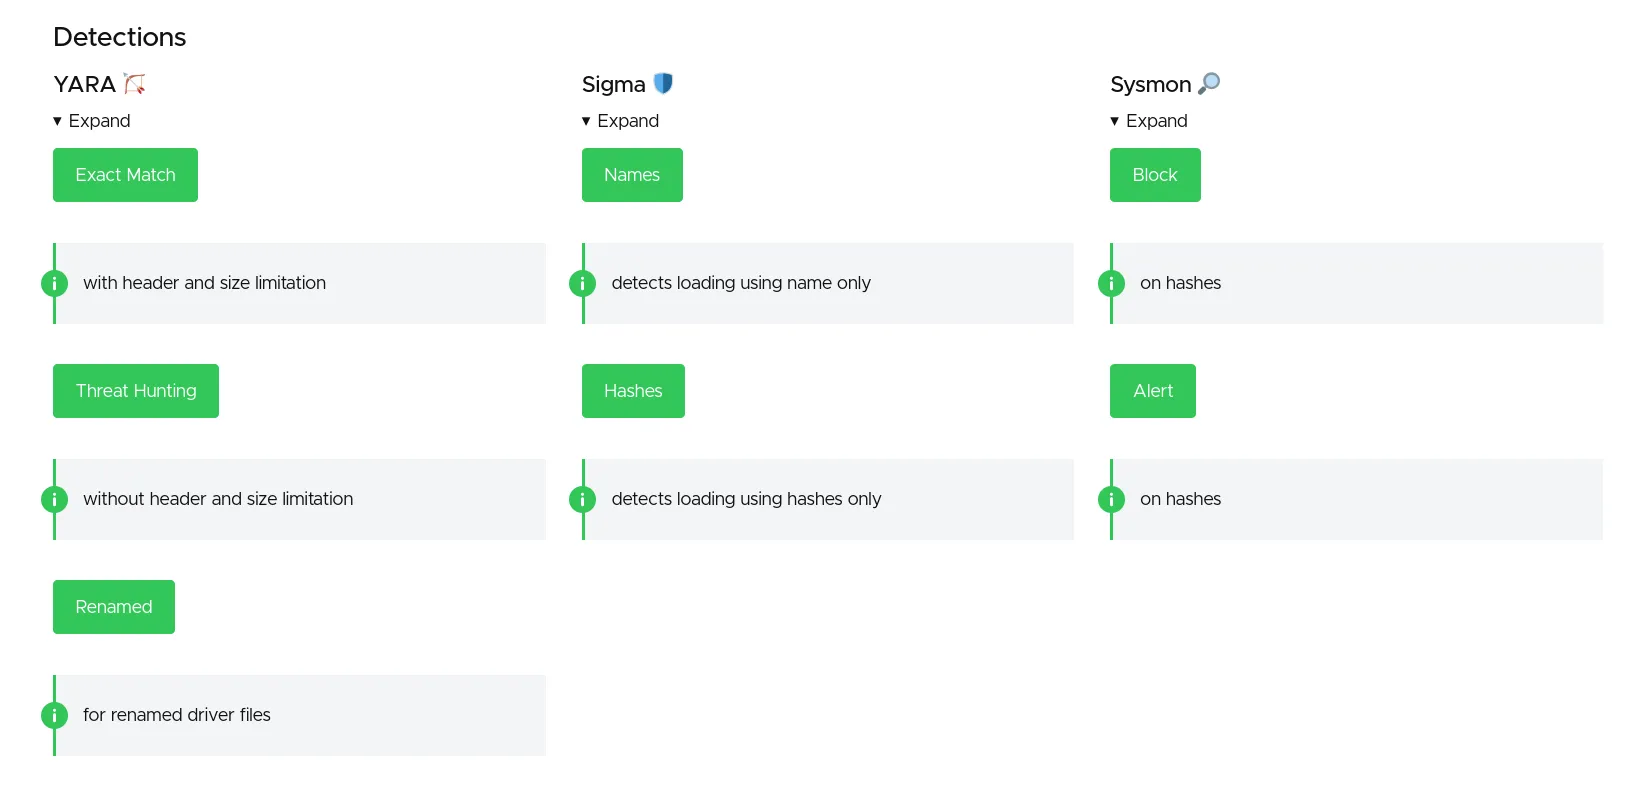
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…

curated-resourceseducationforensics+5
1.8k3 days ago
Stego-Lab preview

Stego-Lab

GitLabraithchr/stego-lab

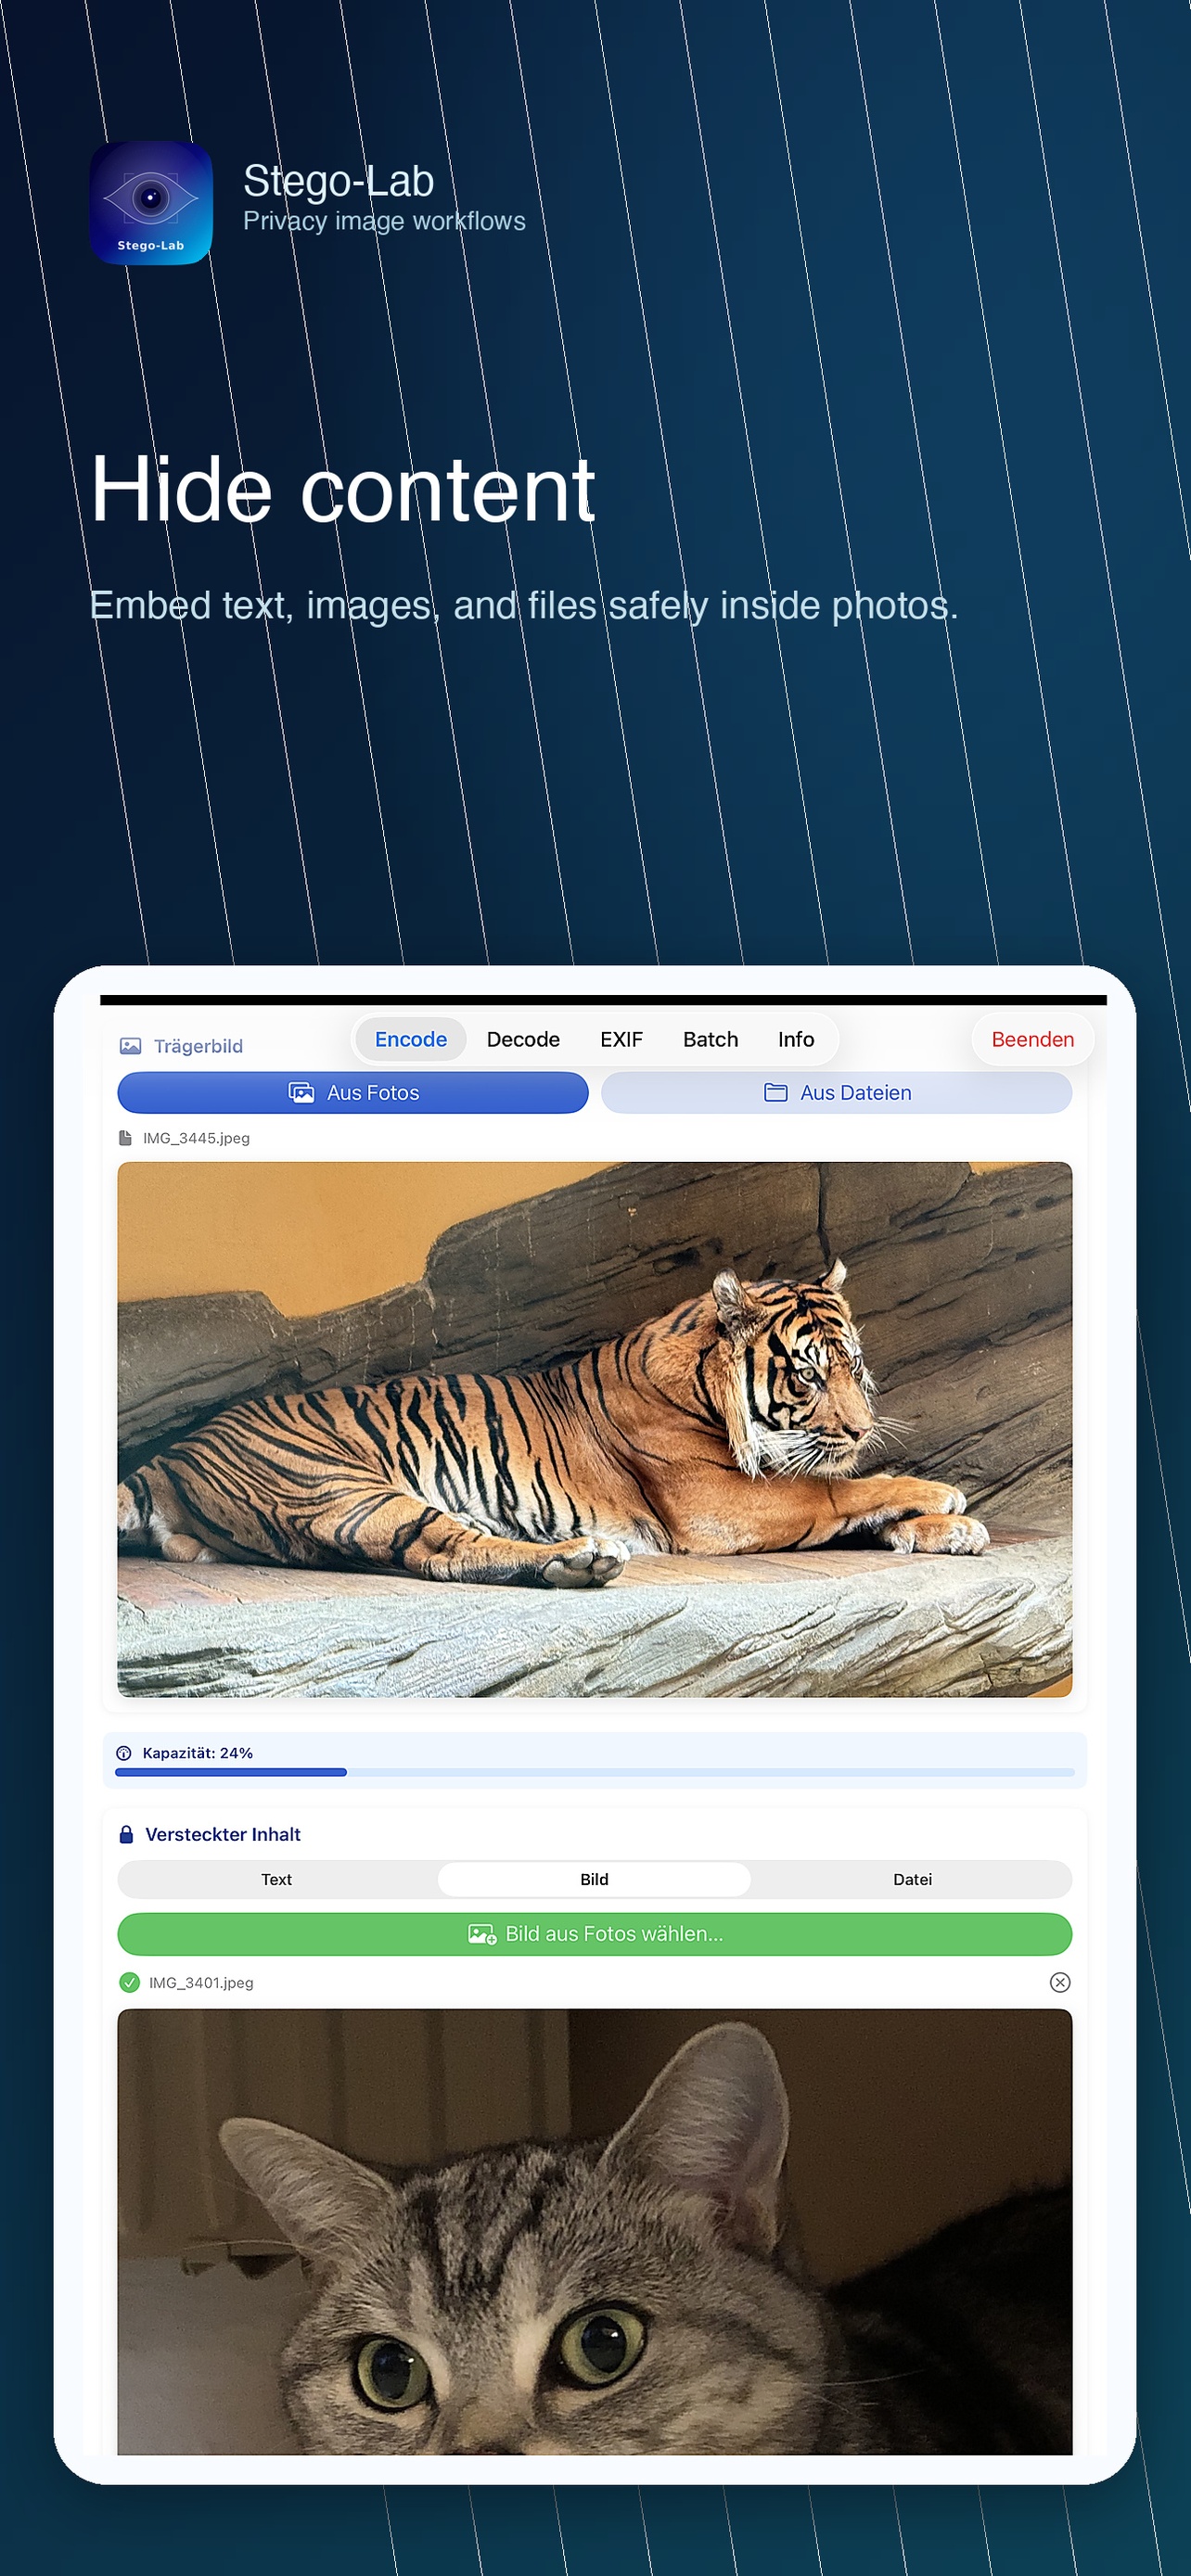
Local steganography app for hiding text, images, or files inside carrier images with AES-256 encryption, EXIF editing, watermarking, and batch…

encryption-decryption-toolsforensicsprivacy+2
14 days ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

debuggersdynamic-analysis-sandboxingforensics+1
2485 years ago
Snap-Scraper preview

Snap-Scraper

GitHubrhematt/snap-scraper

Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.

digital-forensicseducationforensics+3
1173 years ago
jdvrif preview

jdvrif

GitHubcleasbycode/jdvrif

Steganography Tool for JPG Images

cryptographydata-exfiltrationencryption-decryption-tools+3
7213 days ago
RawHive preview

RawHive

GitHubnmht3t/rawhive

Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…

digital-forensicsdisk-forensicsexploitation+4
963 months ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
252 months ago
Telegrip preview

Telegrip

GitHubtelegrip/telegrip

GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…

data-recoverydigital-forensicsforensics+1
194 years ago
dotnetfile preview

dotnetfile

GitHubpan-unit42/dotnetfile

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

binary-analysisforensicshash-analysis+4
1187 months ago
Honeypot-for-CVE-2025-59287-WSUS preview

Honeypot-for-CVE-2025-59287-WSUS

GitHublupovis/honeypot-for-cve-2025-59287-wsus

Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…

defensive-toolsforensicsincident-response+2
2611 months ago
sift preview

sift

GitHubteamdfir/sift

SIFT

cloud-securitydigital-forensicsdisk-forensics+3
5502 years ago
LogHound preview

LogHound

GitHubrnb-team/loghound

Post-Exploitation EVTX Analyzer for BloodHound Mapping

authenticationdigital-forensicsforensics+6
125 months ago
Previous12Next