Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.

Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)

Script for automating Linux memory capture and analysis

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

A helper script for unpacking and decompiling EXEs compiled from python code.

iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252


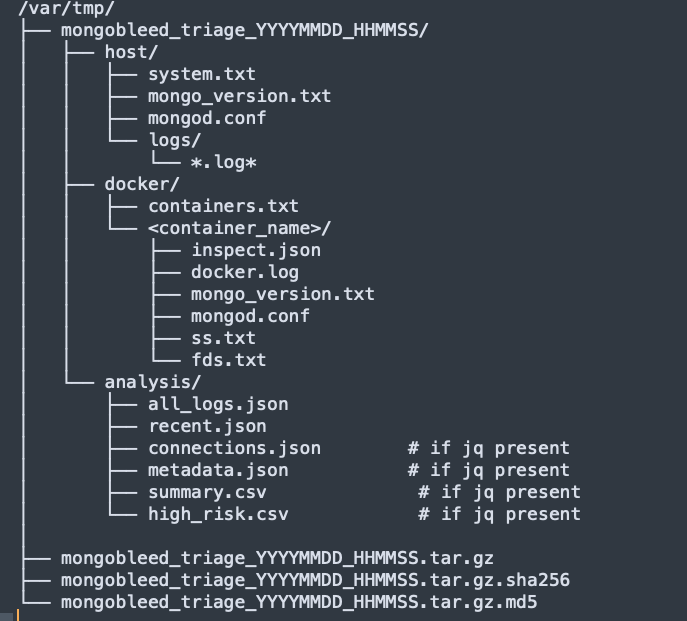
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

Your everyday Linux distribution gone Super Saiyan.

A forensic evidence collection & analysis toolkit for OS X

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.

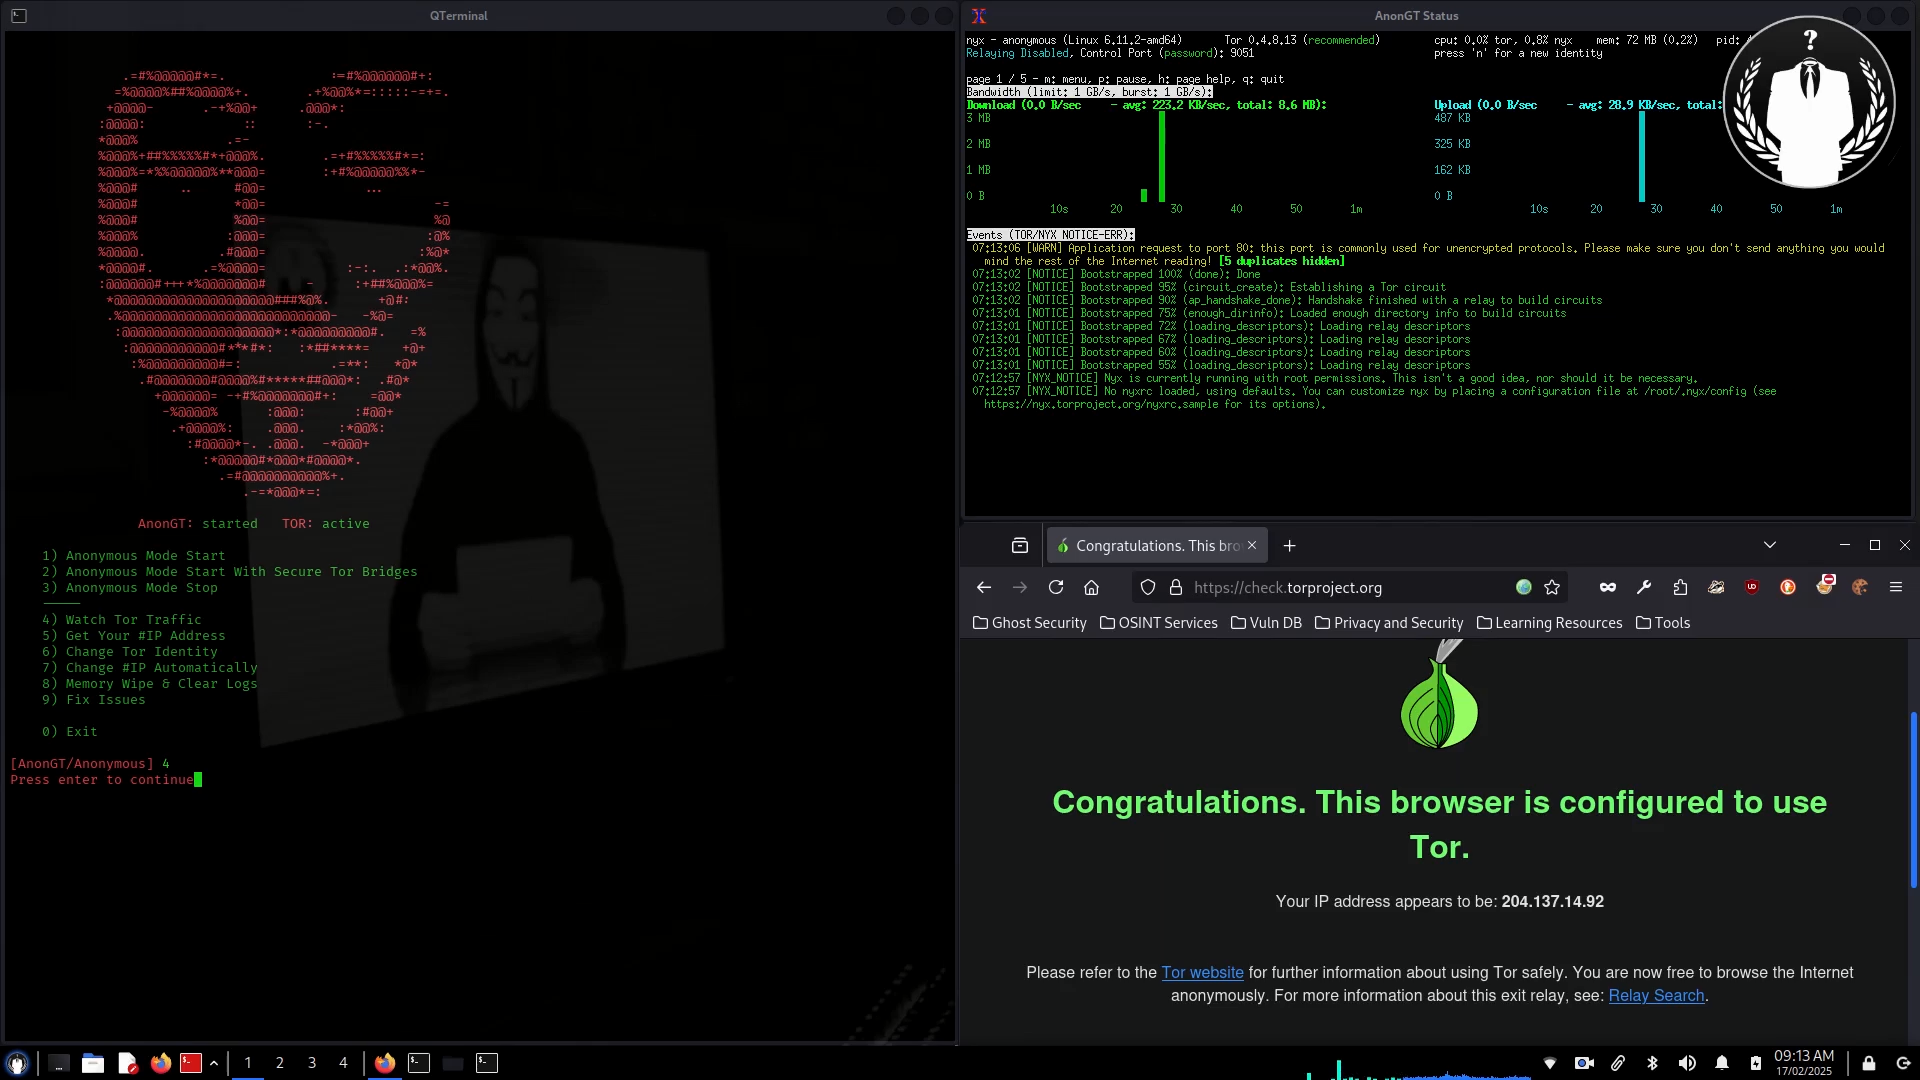
Redirect All Traffic Through Tor Network For Kali Linux

MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…

CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script