
TrueTree
 themittenmac/truetree
A command line tool for pstree-like output on macOS with additional pid capturing capabilities
digital-forensicsforensicsincident-response+1
2872 years ago
themittenmac/truetreeA command line tool for pstree-like output on macOS with additional pid capturing capabilities
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts

 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 psypanda/hashid
Software to identify the different types of hashes -
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 cado-security/dfir_resources_revil_kaseya
Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
 mfarshad-abdullah-khan/cve-2025-53770-research
🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…
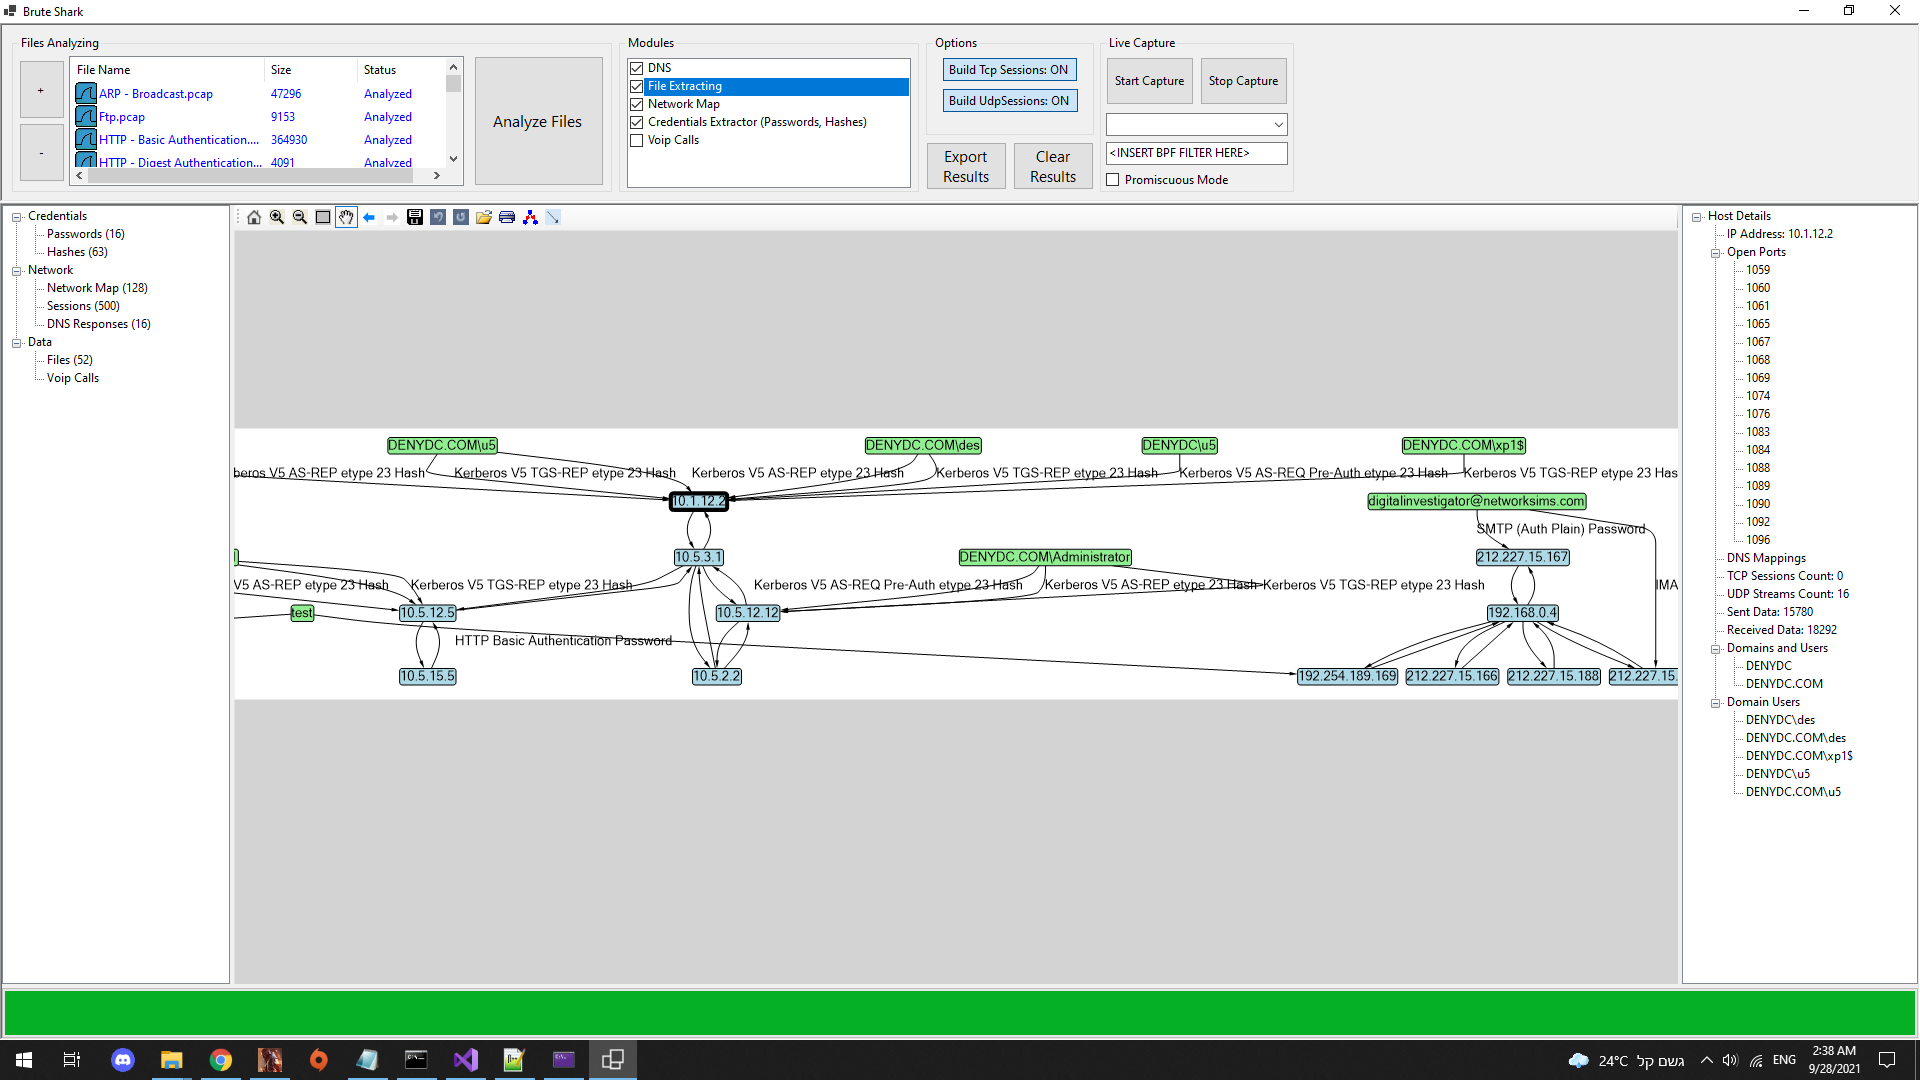
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 iyargross/smb-cve-2025-33073
Advanced SMB Honeypot: CVE-2025-33073 Research & Implementation

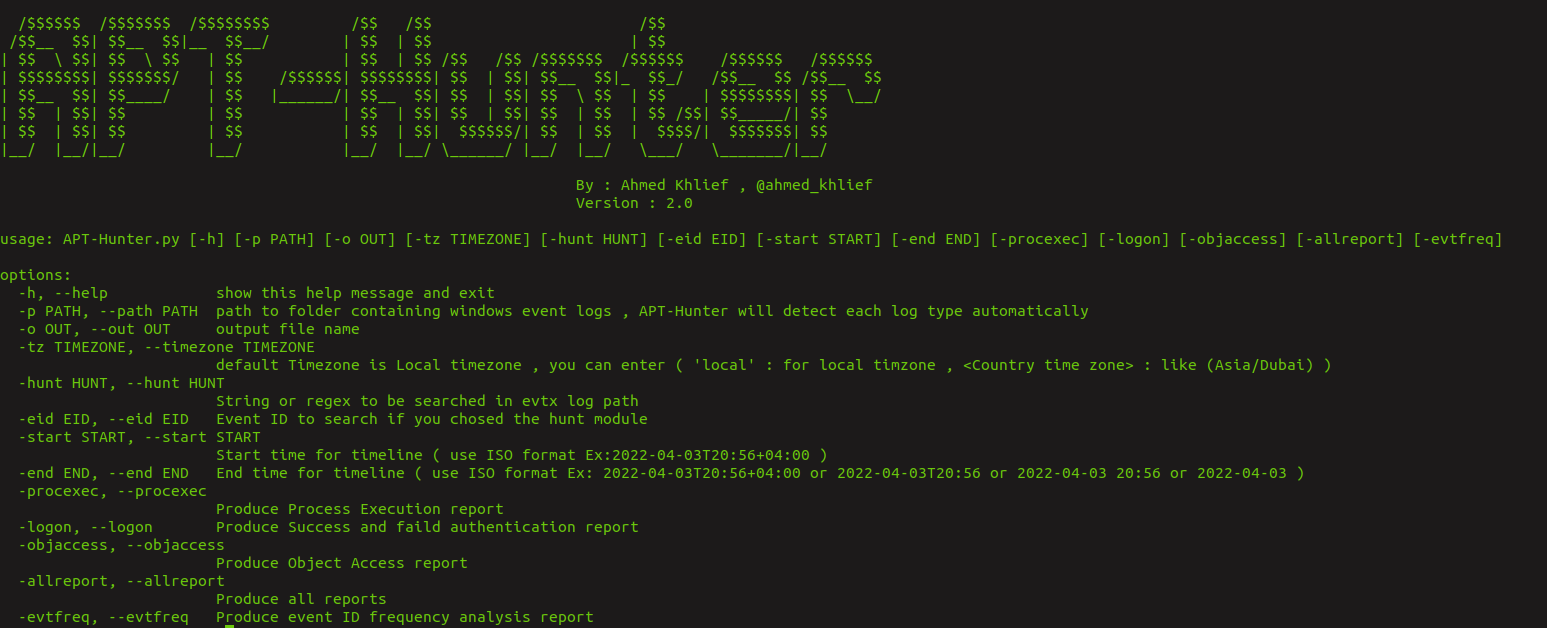 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…