
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
54 results
vulhunt preview

vulhunt

GitHubvulhunt-re/vulhunt

Vulnerability detection framework by Binarly's REsearch team
ai-assisted-reversingbinary-analysisfirmware-analysis+4
8901 month ago
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
binary-analysisembedded-systems-securityfirmware-analysis+3
4082 years ago
polypyus preview

polypyus

GitHubseemoo-lab/polypyus

Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
binary-analysisembedded-systems-securityfirmware-analysis+1
2335 years ago
rp2350_hacking_challenge preview

rp2350_hacking_challenge

GitHubraspberrypi/rp2350_hacking_challenge

Raspberry Pi RP2350 hacking challenge: extract a 128-bit OTP secret protected by secure boot and OTP lock, with setup scripts and firmware for Pico 2…

cryptographyctfeducation+5
2061 year ago
wolfCOSE preview

wolfCOSE

GitHubwolfssl/wolfcose

A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.

code-analysiscryptographyembedded-systems-security+7
762 days ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
binary-analysisdynamic-code-analysisfirmware-analysis+3
5421 days ago
attesor preview

attesor

GitHubinokinoki/attesor

AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…

ai-assisted-reversingbinary-analysiseducation+3
851 month ago
ODIS-project-explorer preview

ODIS-project-explorer

GitHubkartoffelpflanze/odis-project-explorer

Python dumper/explorer for MCD Runtime Projects used by ODIS

binary-analysisdebuggersembedded-systems-security+4
411 year ago
ME2-Writeup preview

ME2-Writeup

GitHubcoremaze/me2-writeup

Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface
binary-analysisdata-recoveryeducation+5
495 months ago
hcon2026hwctf preview

hcon2026hwctf

GitHubtherealdreg/hcon2026hwctf

Hardware Hacking CTF hcon2026hwctf - RISCV Hazard3 (@Wren6991) Exploiting by @b1n4ri0 @antoniovazquezblanco & @therealdreg
binary-exploitationctfeducation+6
245 months ago
netgear_r6700v3_circled preview

netgear_r6700v3_circled

GitHubcyber-defence-campus/netgear_r6700v3_circled

Demonstrate some functionalities of Morion by generating an exploit for CVE-2022-27646 (stack buffer overflow on Netgear R6700v3 routers).

binary-exploitationeducationembedded-systems-security+4
81 year ago
cve-2023-31355-poc preview

cve-2023-31355-poc

GitHubfreax13/cve-2023-31355-poc

Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
binary-exploitationencryption-decryption-toolsexploitation+4
82 years ago
IvantiInitrdDecryptor preview

IvantiInitrdDecryptor

GitHubwatchtowrlabs/ivantiinitrddecryptor

A tool for decrypting Ivanti device initrd images by reverse-engineering the kernel's bzImage to locate and use the embedded AES key.
cryptographyembedded-systems-securityfirmware-analysis+1
42 years ago
the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass preview

the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass

GitHubhunt-benito/the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass

Proof-of-concept demonstrating a firmware signature verification bypass in Phison S11 SSDs, allowing attackers to re-sign modified firmware by…
educationembedded-systems-securityexploitation+4
1 month ago
CVE-2025-4275 preview

CVE-2025-4275

GitHubthemalwareguardian/cve-2025-4275

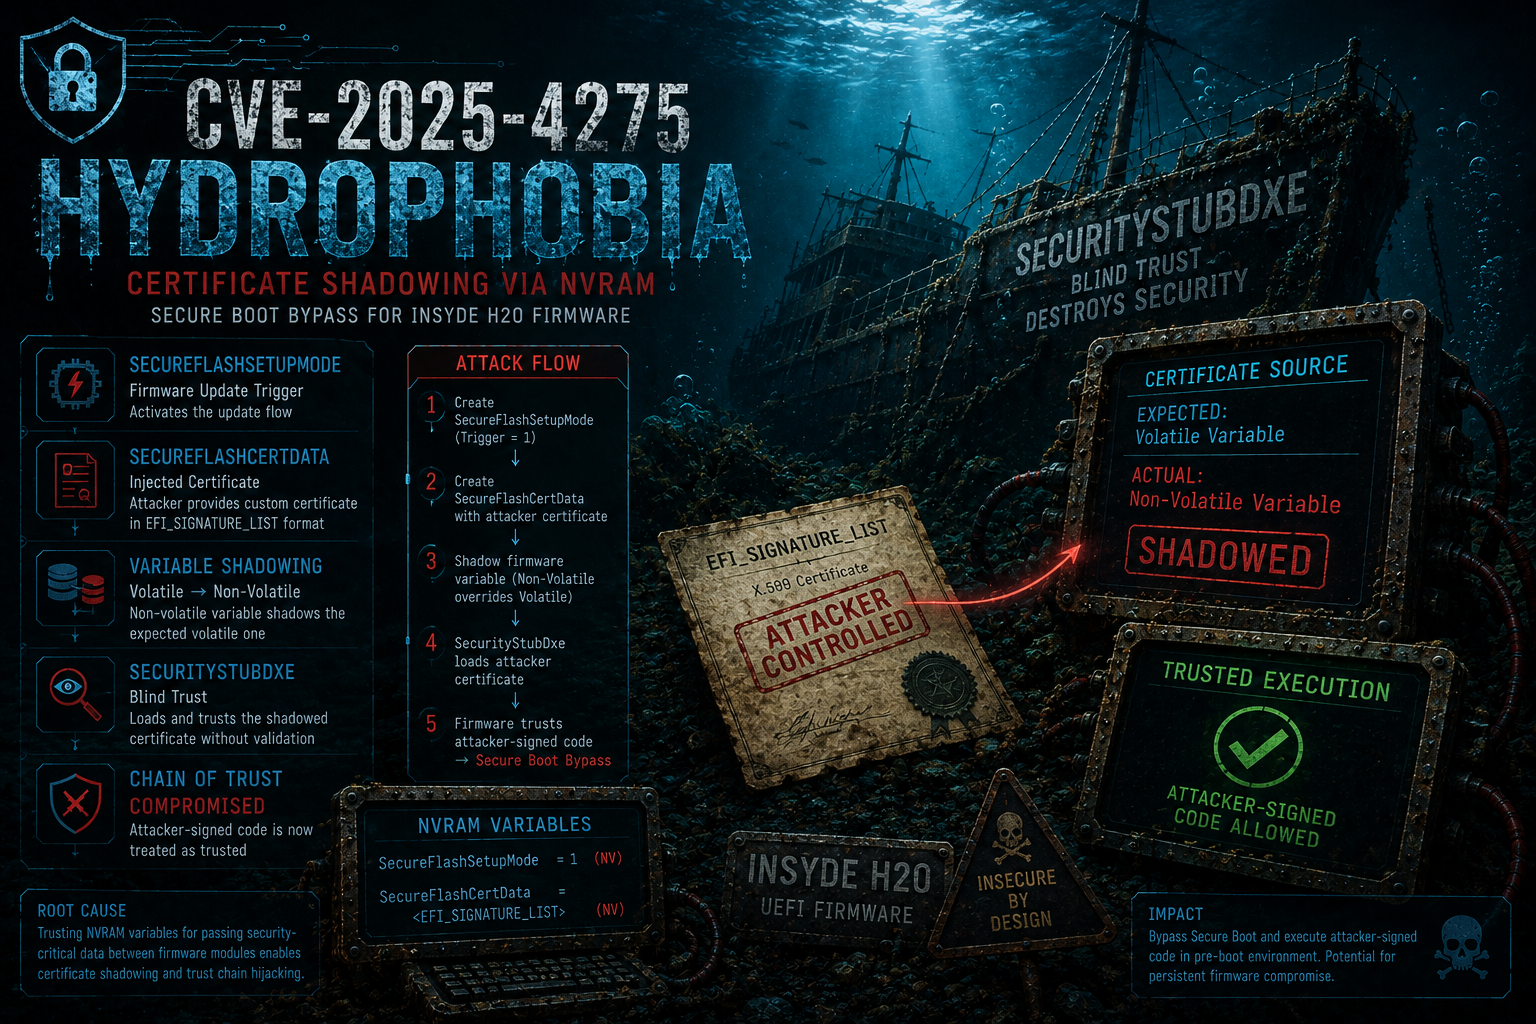
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
binary-analysiseducationexploitation+5
1 month ago
CVE-2024-7344 preview

CVE-2024-7344

GitHubthemalwareguardian/cve-2024-7344

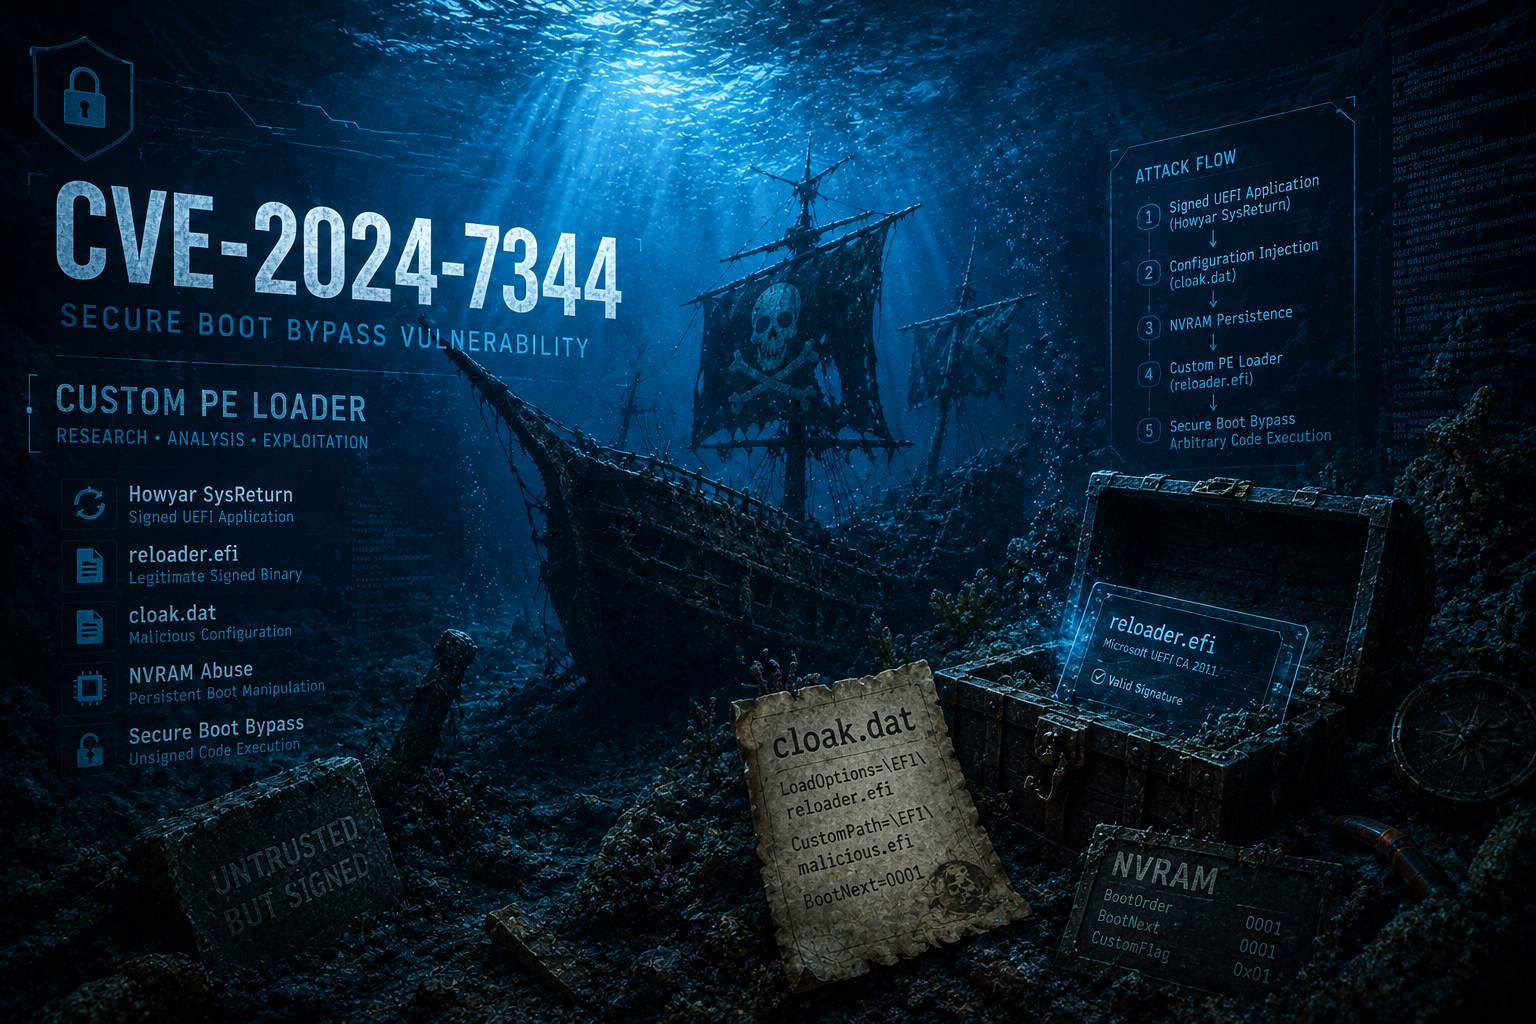
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
binary-analysiseducationexploitation+4
1 month ago
tapo-c260-rce preview

tapo-c260-rce

GitHubl0lsec/tapo-c260-rce

PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
command-and-controlembedded-systems-securityexploitation+7
27 months ago
secure-boot-cert-servicing preview

secure-boot-cert-servicing

GitHubets-mse/secure-boot-cert-servicing

Standalone assessment and servicing for the Secure Boot 2011 to 2023 certificate rollover (CVE-2023-24932 / KB5025885). Assess-only by default; no…

configuration-auditingfirmware-analysisvulnerability-analysis
2 months ago
Previous123Next