
CVE-2024-36877
 jjensn/cve-2024-36877
Proof-of-concept exploit for CVE-2024-36877 targeting firmware vulnerabilities, with detailed write-up and binary exploitation techniques.
binary-exploitationembedded-systems-securityexploitation+2
jjensn/cve-2024-36877Proof-of-concept exploit for CVE-2024-36877 targeting firmware vulnerabilities, with detailed write-up and binary exploitation techniques.
 abandon1337/cve-2024-0762
Proof-of-concept exploit for CVE-2024-0762, a buffer overflow vulnerability in UEFI firmware, demonstrating exploitation techniques for security…
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
 dgh05t/zer0con_2026_attacking_apple_dcp
Research repository detailing exploitation techniques against Apple's Display Co-Processor (DCP), including firmware analysis and hardware-level…
 quarkslab/conf-presentations
Quarkslab conference talks
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
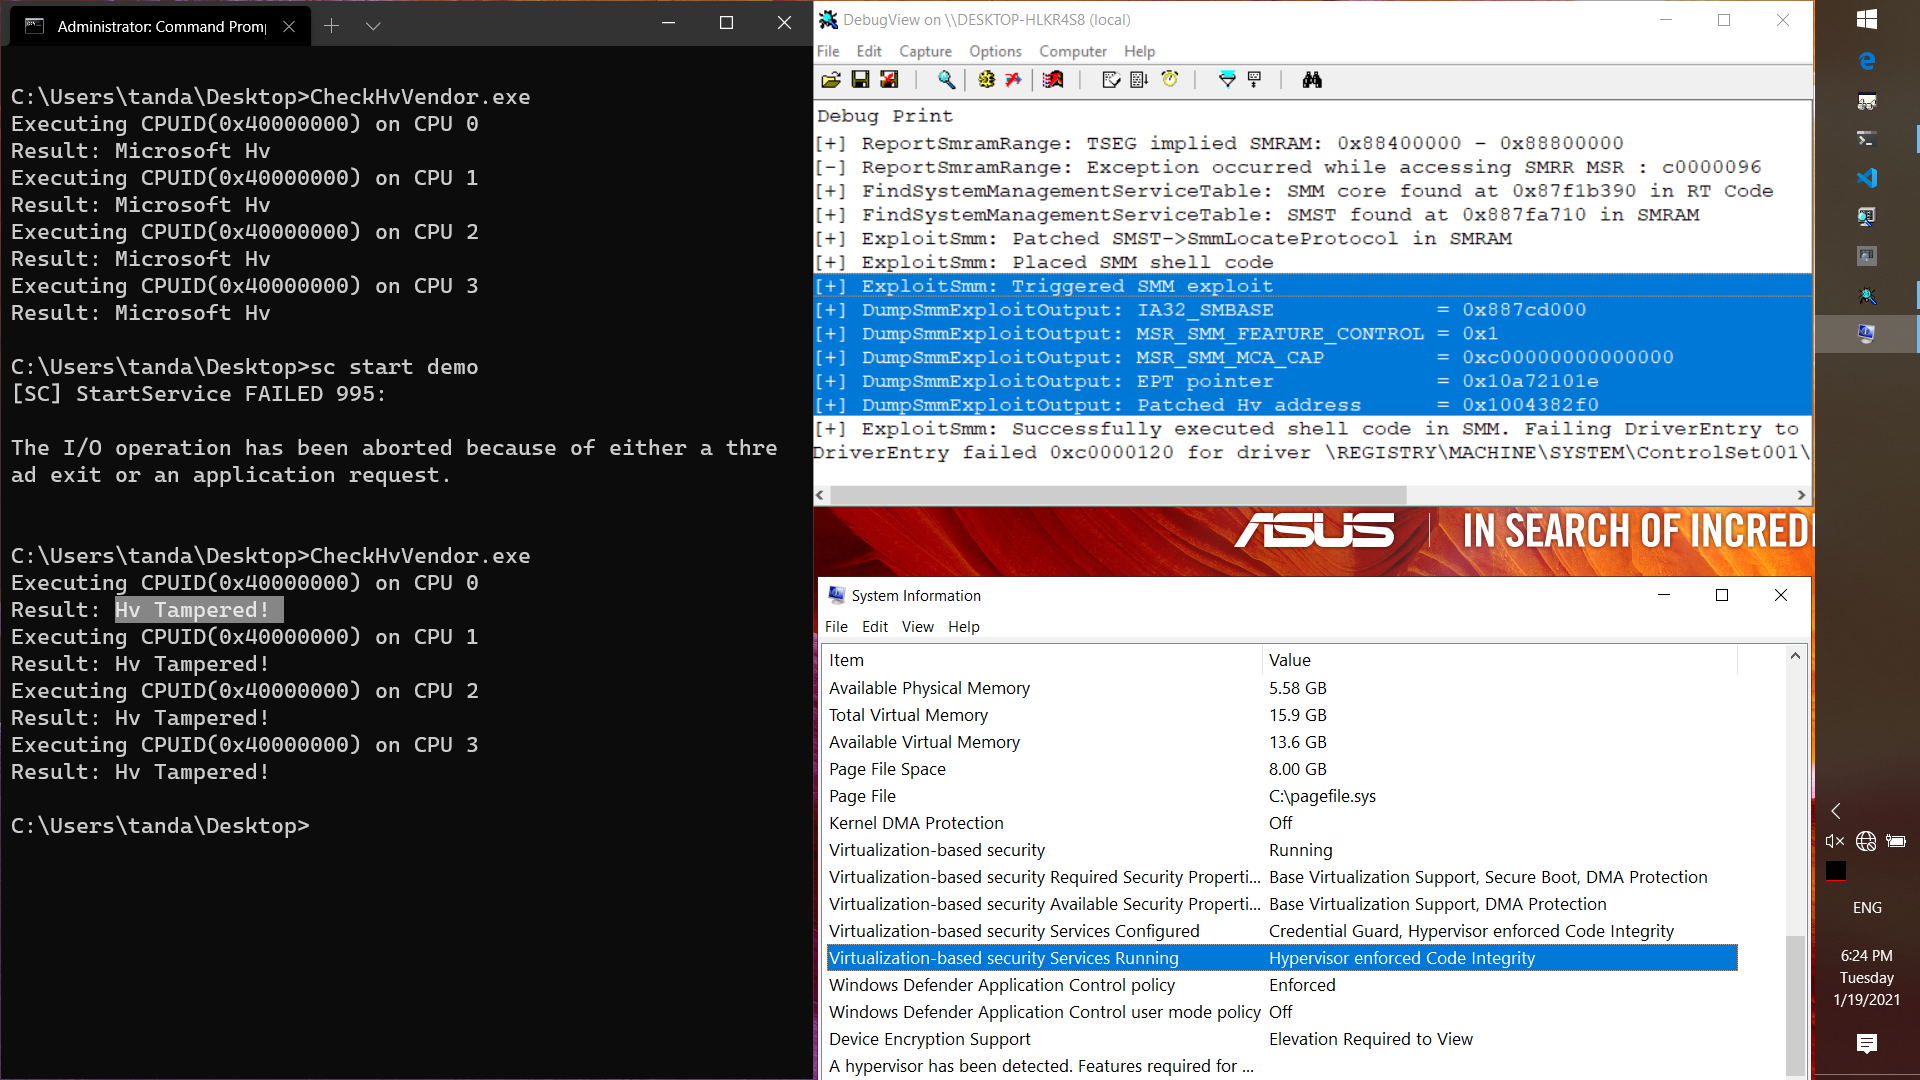 tandasat/smmexploit
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.
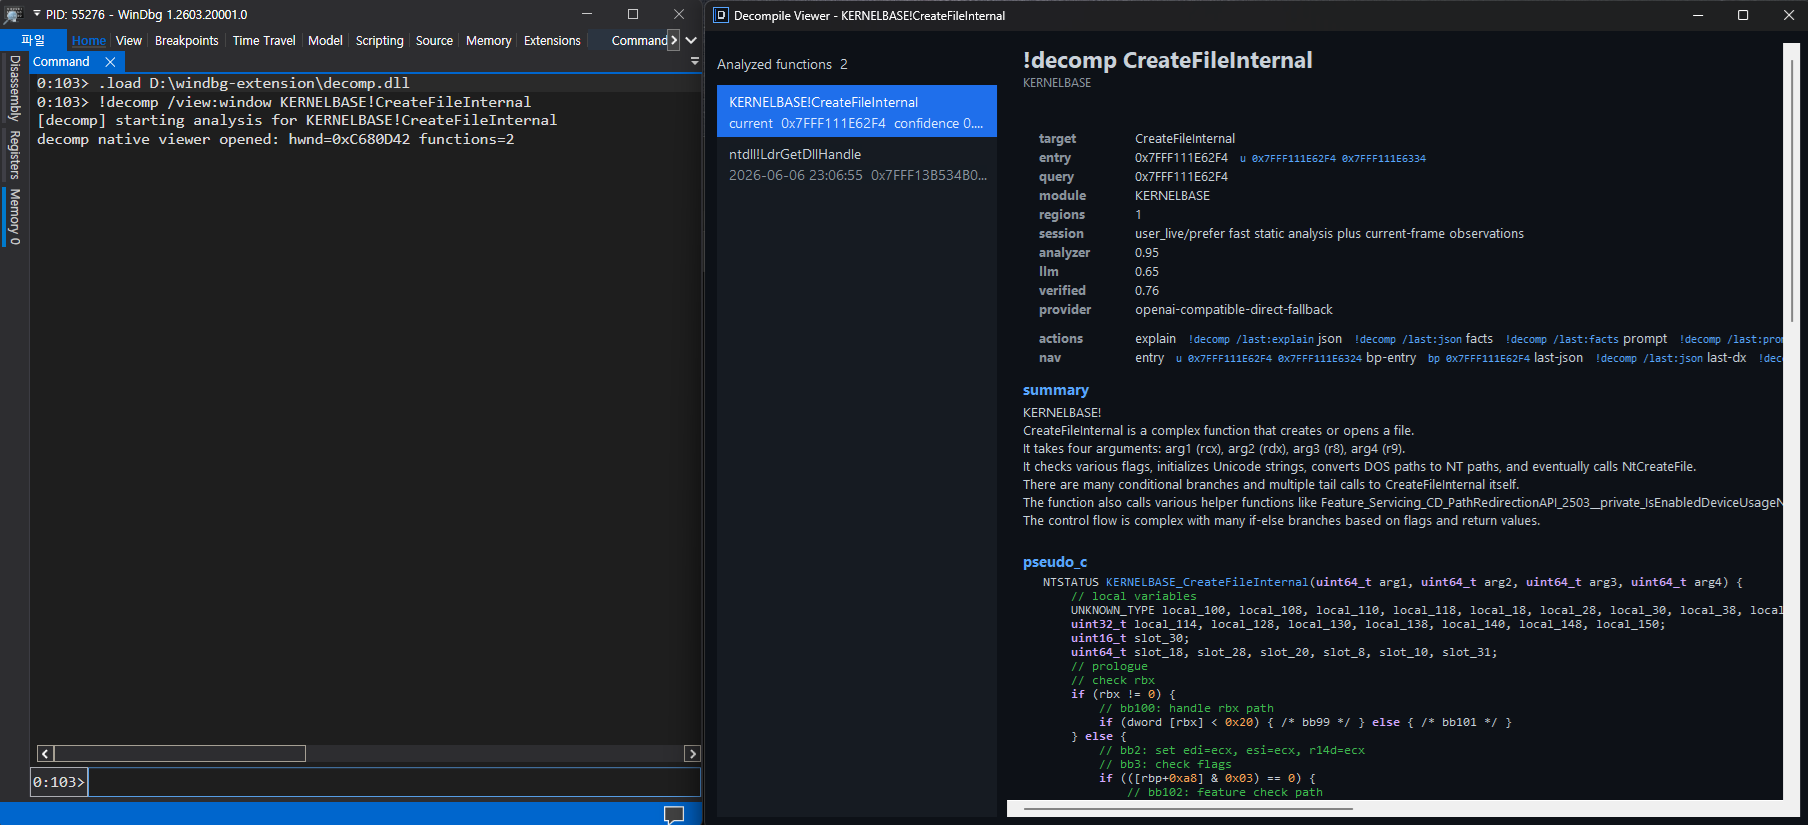 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
 daniel224455/katana
Let's hijack our bootchain - CVE-2021-30327