
st
 bahaabdelwahed/st
IoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…
firmware-analysisiot-securitynetwork-security+1
13
bahaabdelwahed/stIoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…
 teutekeune/ibssloader
Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…
 fans0n-fan/treck20-related
PoC for CVE-2020-11896 Treck TCP/IP stack and device asset investigation
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
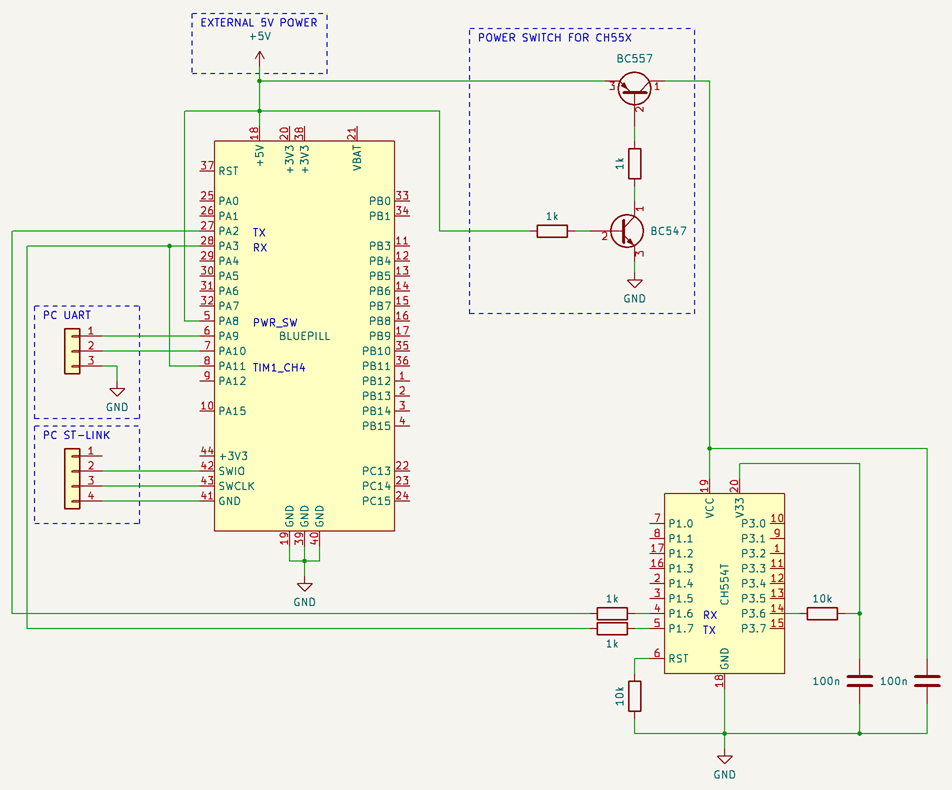 finngineering/ch55x_firmware_extractor
Firmware extractor for CH55x microprocessors
 supermagnum/galdralag-firmware
A cryptographic framework for Baochip-1x .
 20enderdude20/ghidra_v810_v830
Ghidra processor description module for NEC/Renesas v810 and v830 families
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 jiansiting/cve-2019-10915
Proof-of-concept exploit for CVE-2019-10915 targeting an authentication bypass in Siemens TIA Administrator, enabling remote command execution via…
 nccgroup/ghidra-mtk-loader
Ghidra loader for the MediaTek md1img modem firmware image format
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 dgh05t/zer0con_2026_attacking_apple_dcp
Research repository detailing exploitation techniques against Apple's Display Co-Processor (DCP), including firmware analysis and hardware-level…
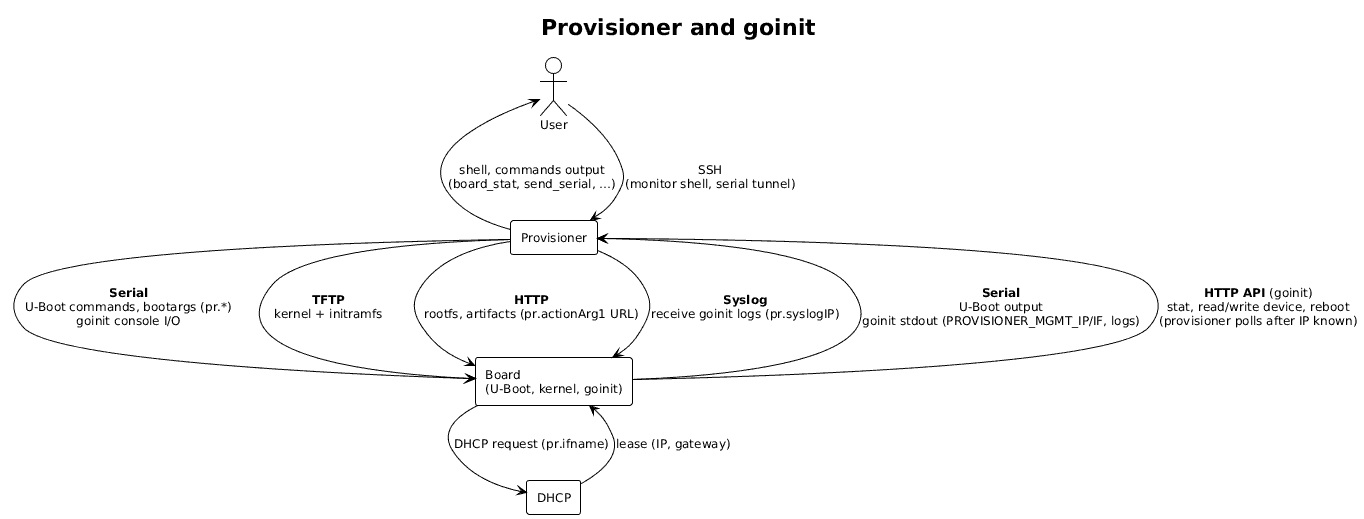 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 sunrayvision/vision-msi-thermal-control
MSI Modern 15H AI C1MGT-096IT Linux thermal management - Reverse engineered EC control with fan profiles and battery threshold
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…