cve-2015-1187-dir820l-firmware-reverse-engineering

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

In the Pixel cellular firmware, there is a possible out of bounds write due to a missing bounds check. This could lead to remote code execution with…

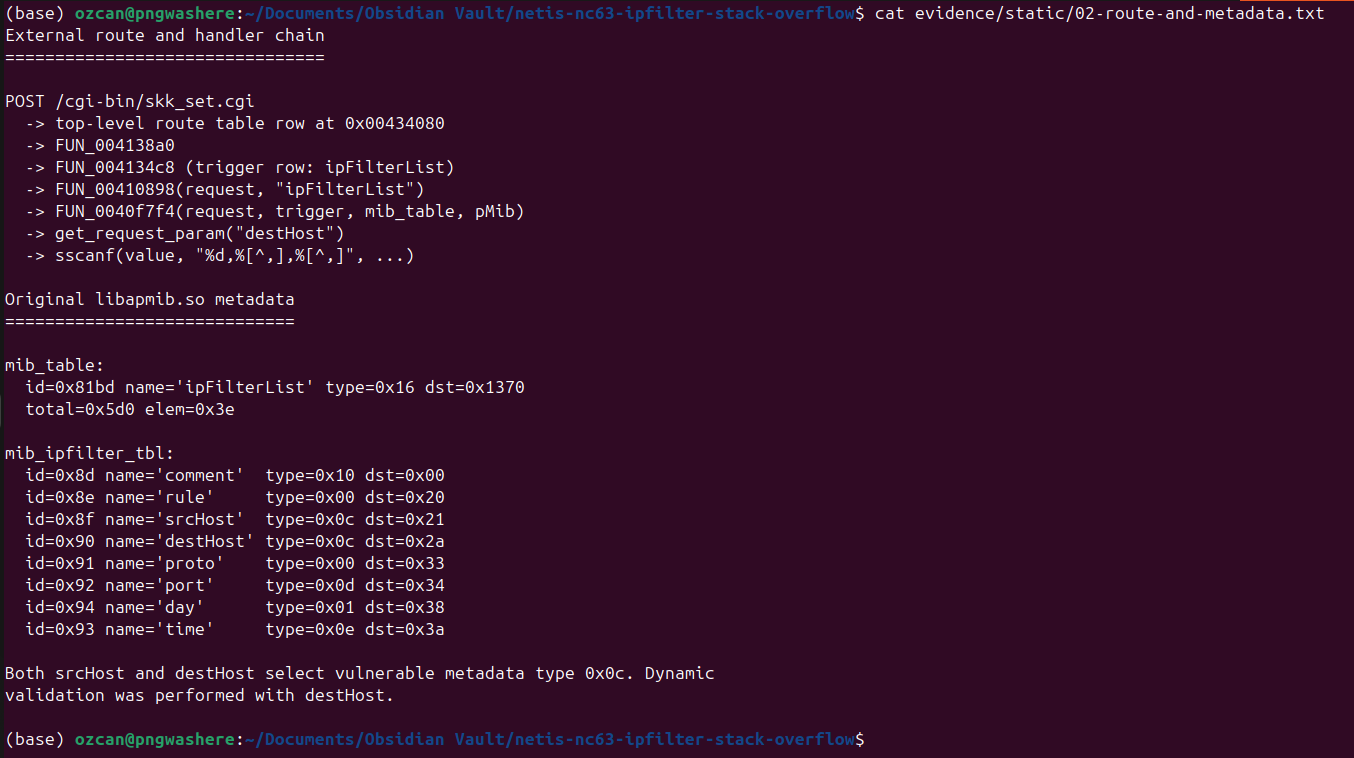
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler

PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…

Detection scripts and mitigation resources for the BootHole vulnerability (CVE-2020-10713), including PowerShell and Bash tools to audit EFI System…

RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory

Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…

Security issue in the hypervisor firmware of some older Qualcomm chipsets

CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…

Educational Python simulation demonstrating ECDSA nonce reuse in IoT firmware signing, showing how an attacker can recover private keys from two…

Security advisory for CVE-2025-65855 - Multiple vulnerabilities in HelpFlash IoT OTA update mechanism

Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…

Raspberry Pi RP2350 hacking challenge: extract a 128-bit OTP secret protected by secure boot and OTP lock, with setup scripts and firmware for Pico 2…

PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025

Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…

Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…

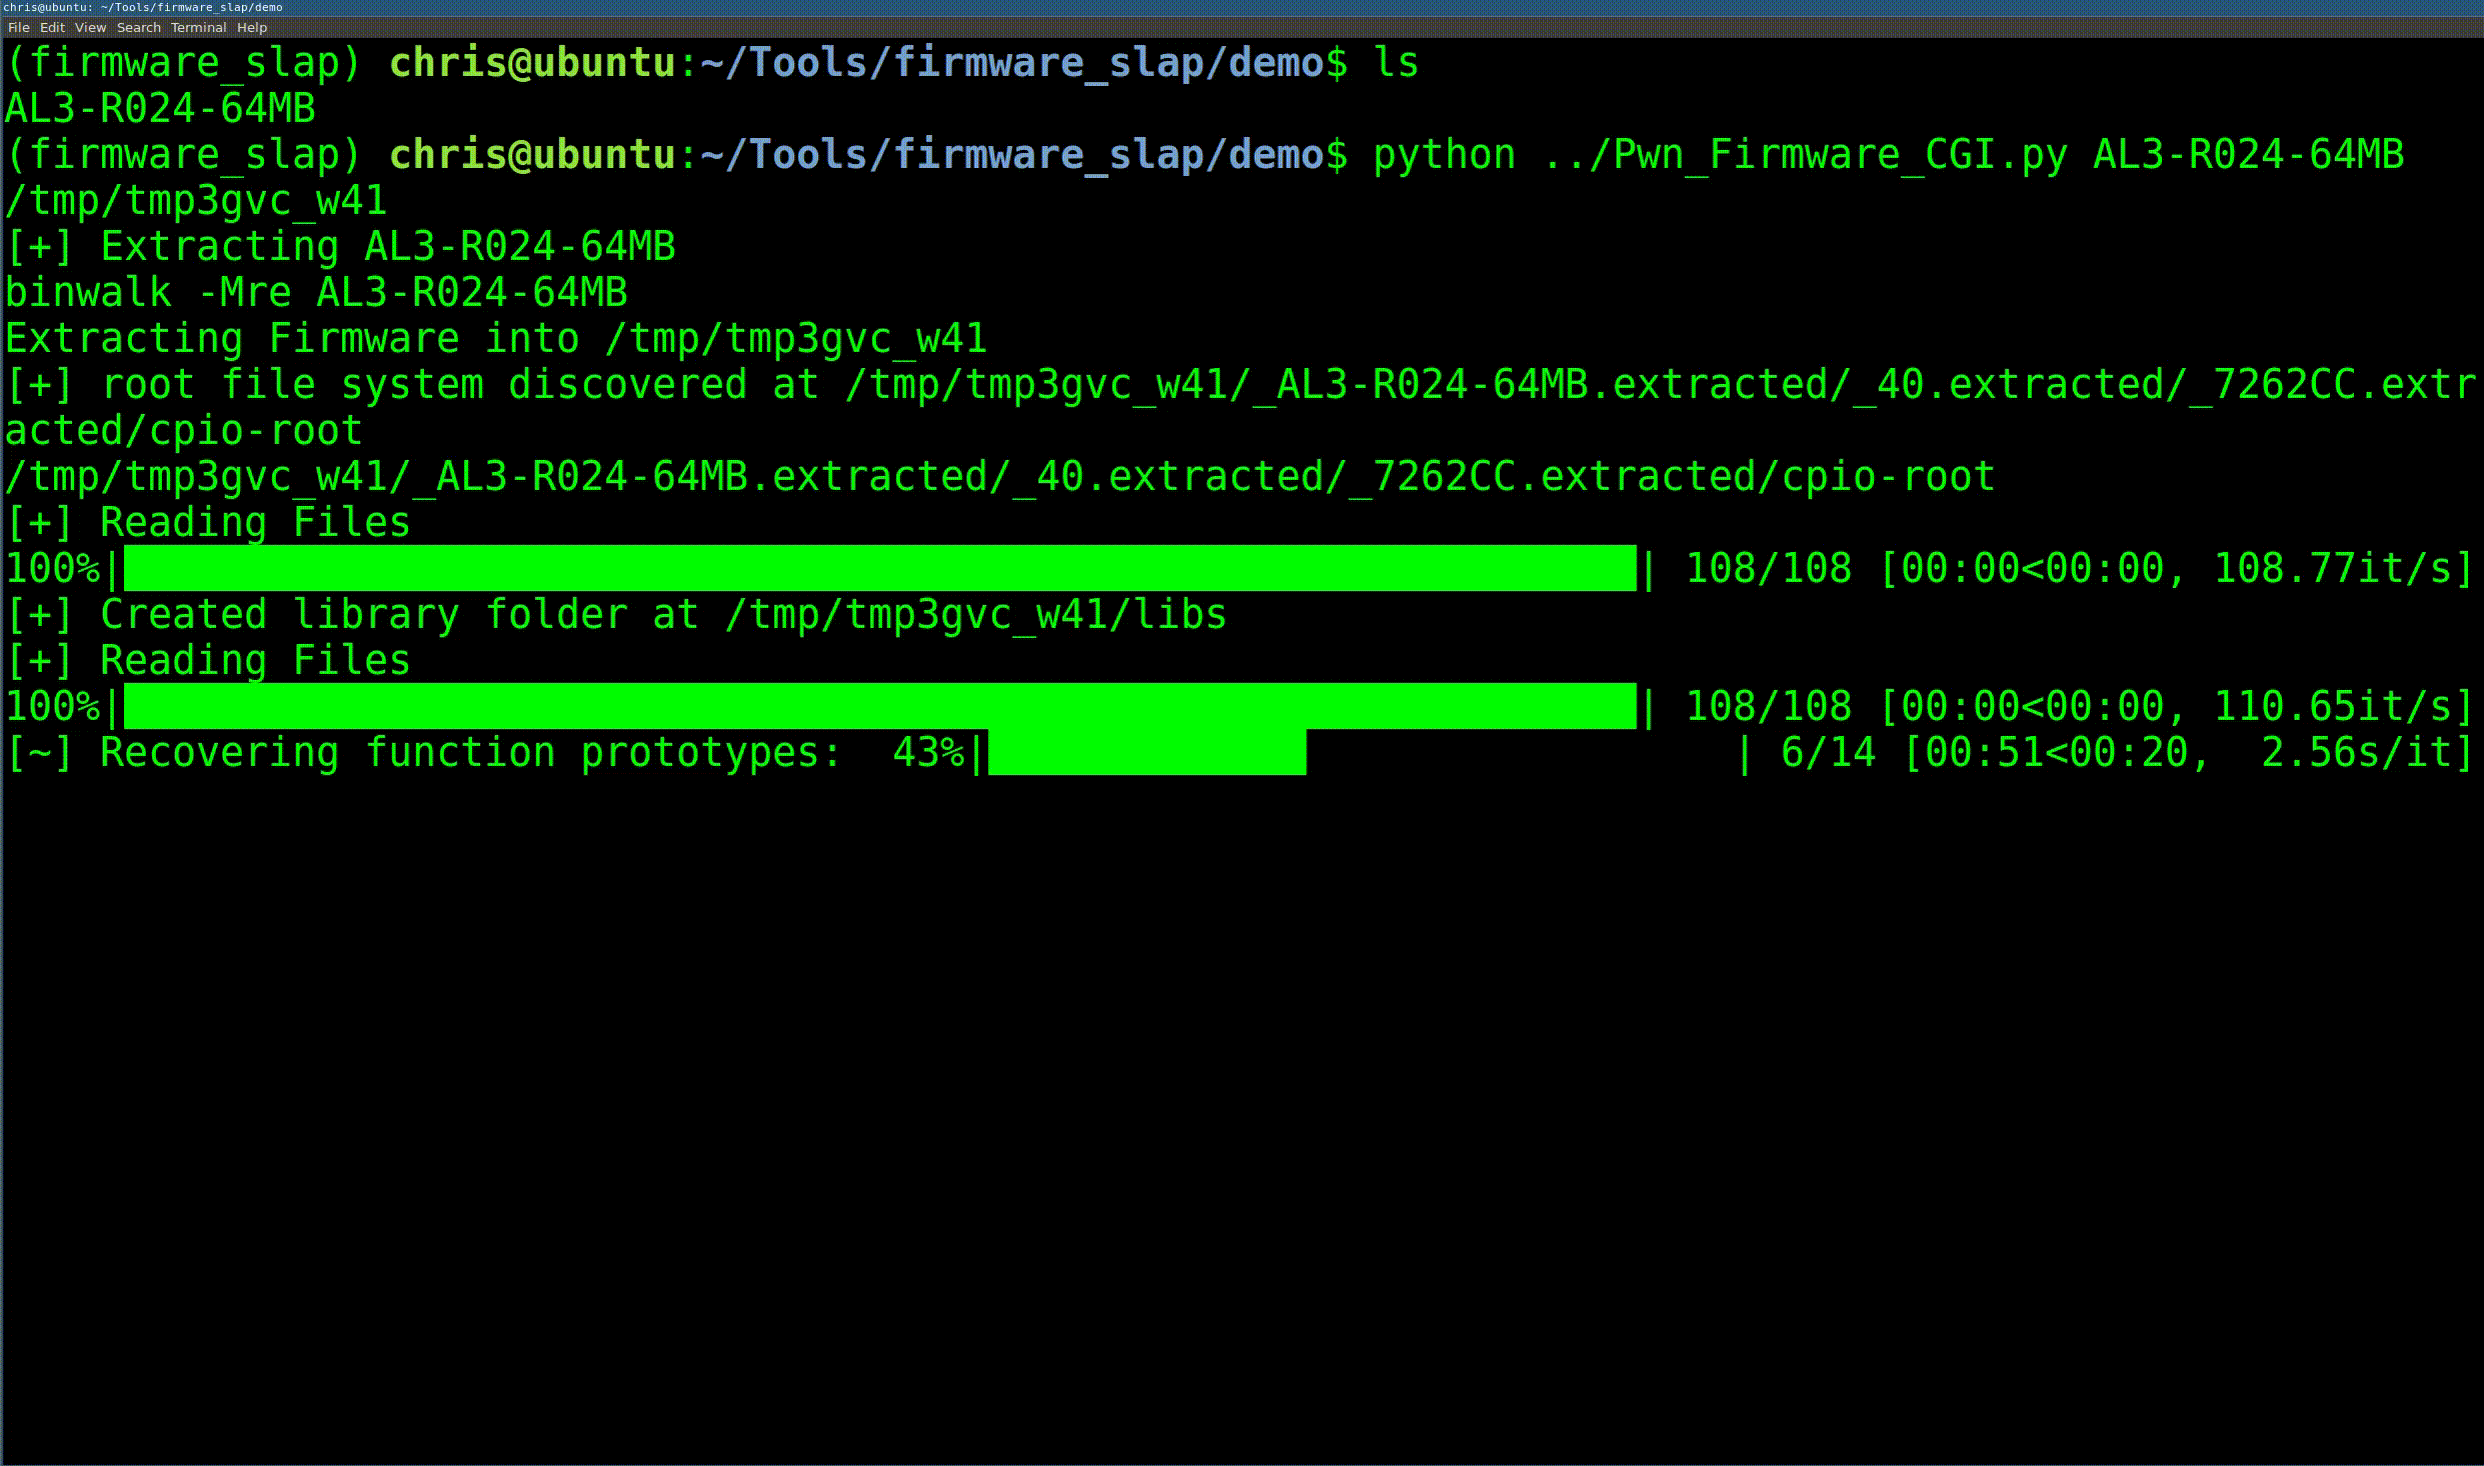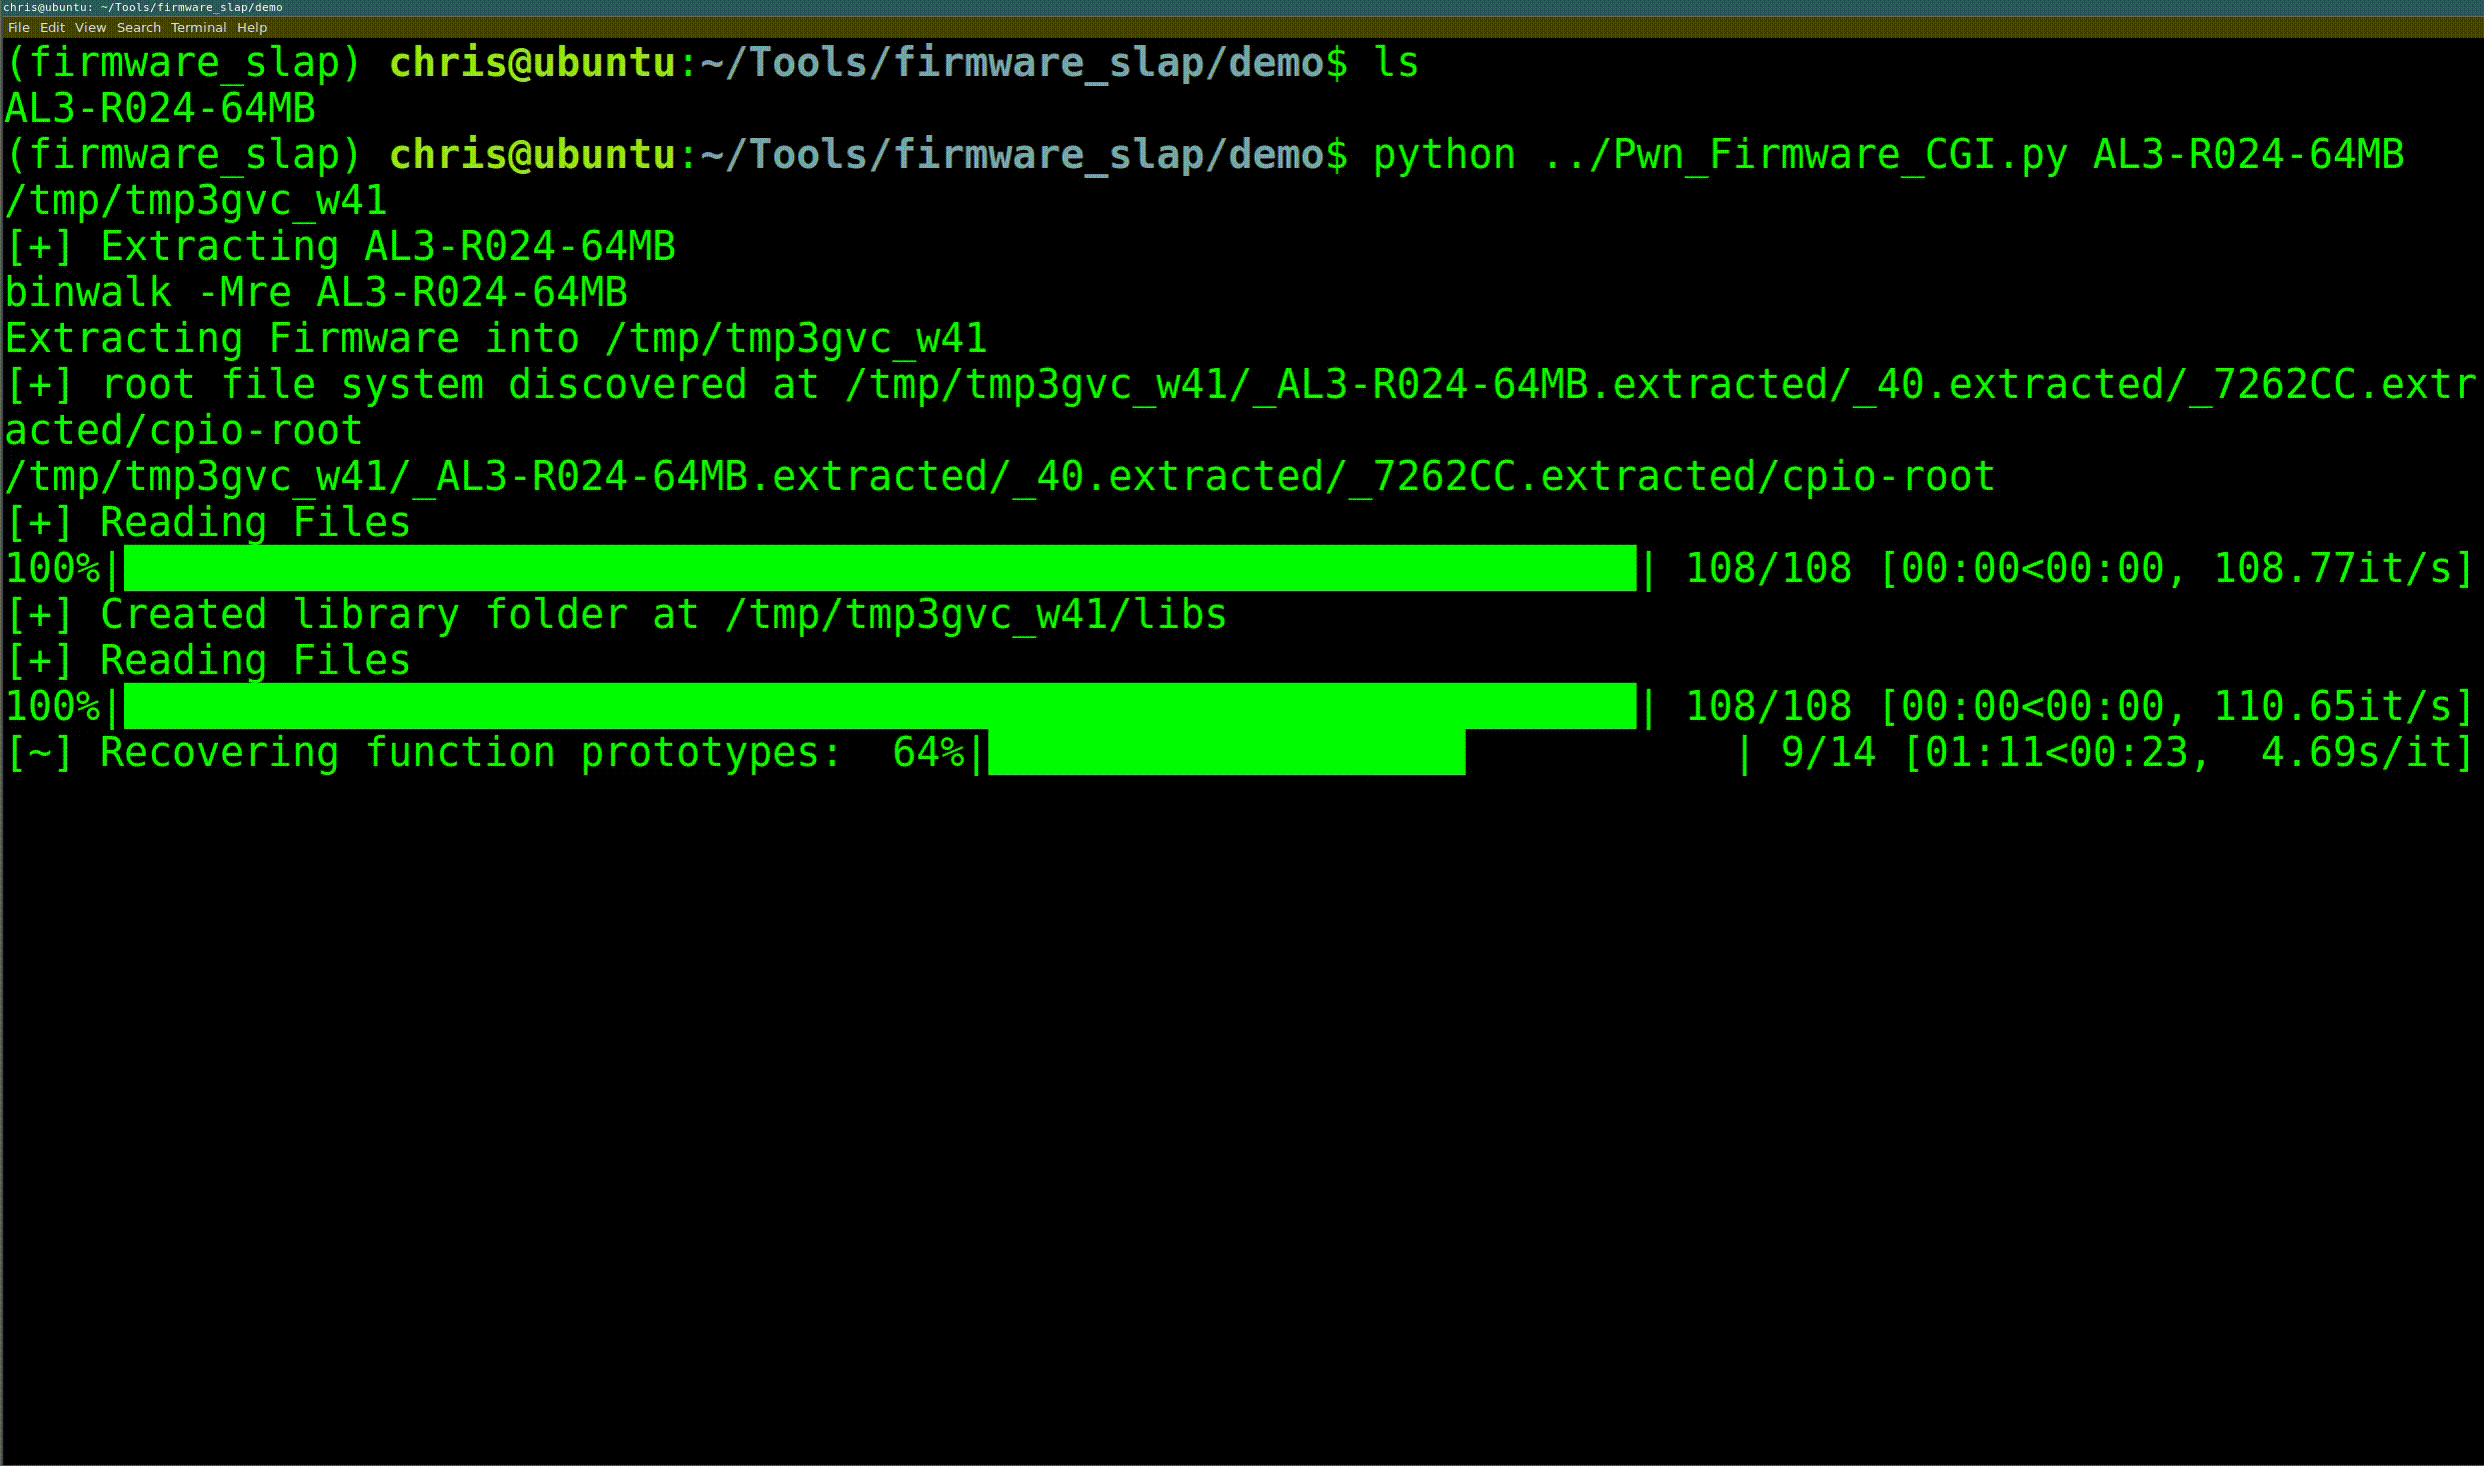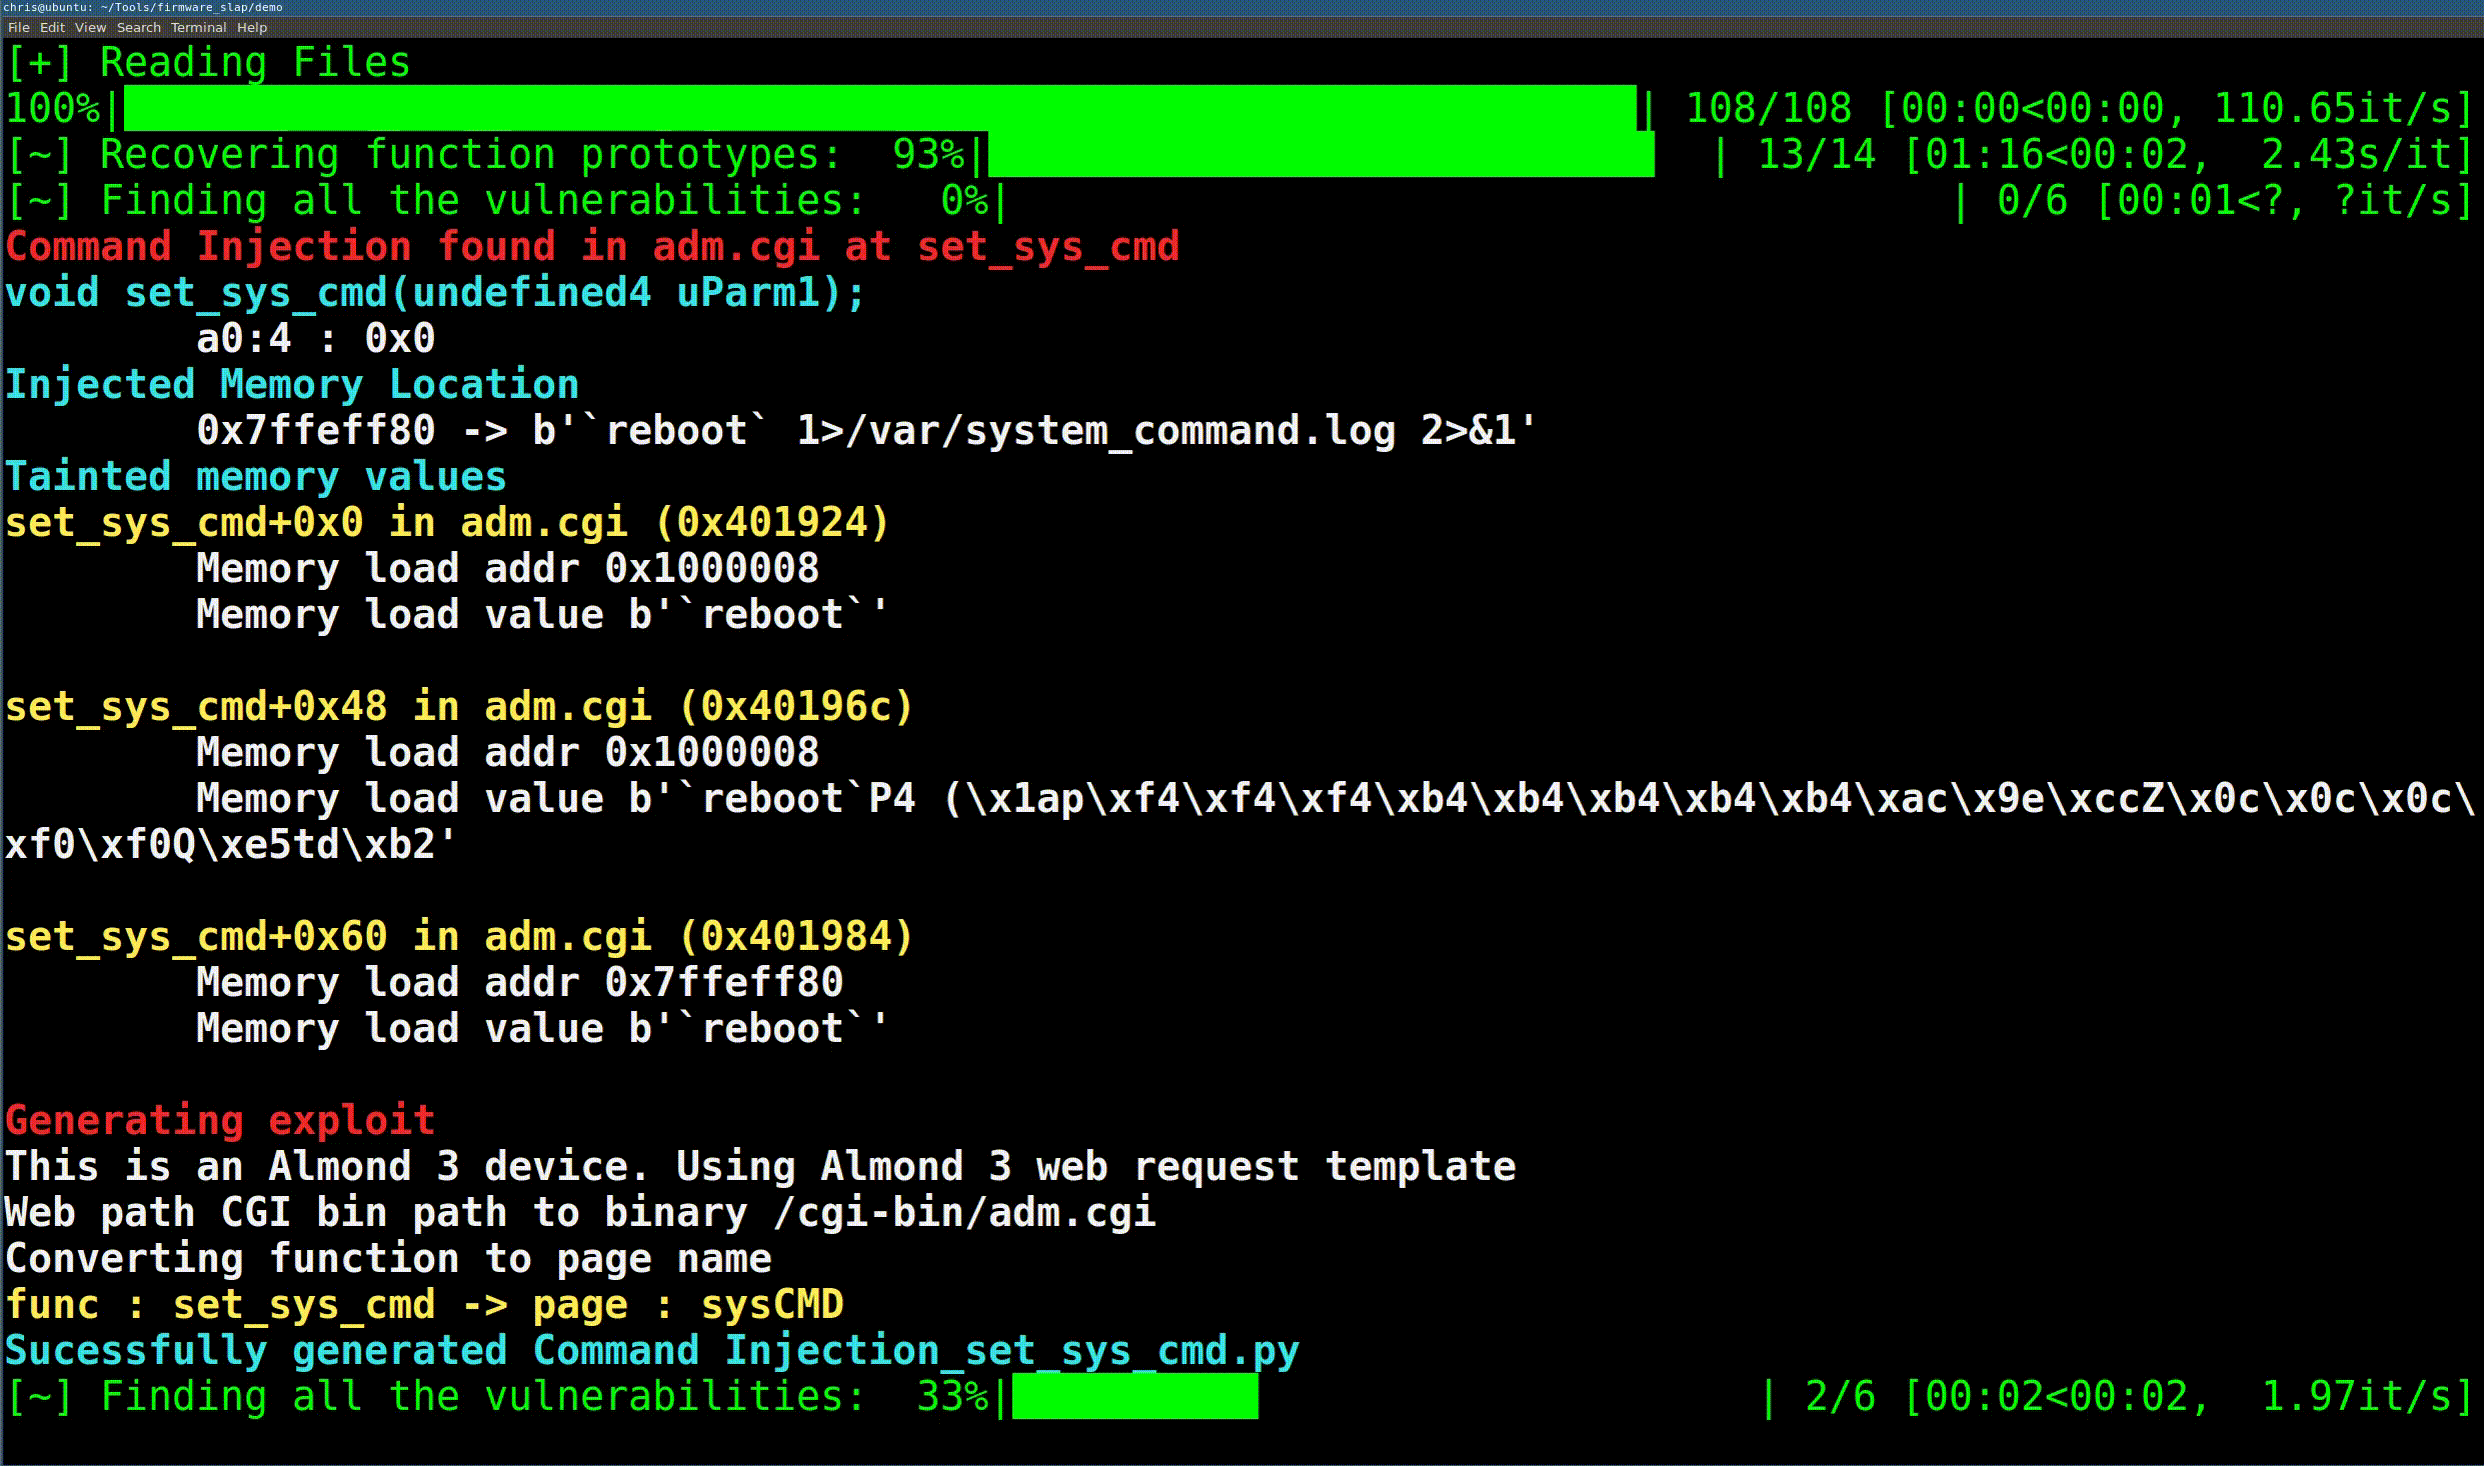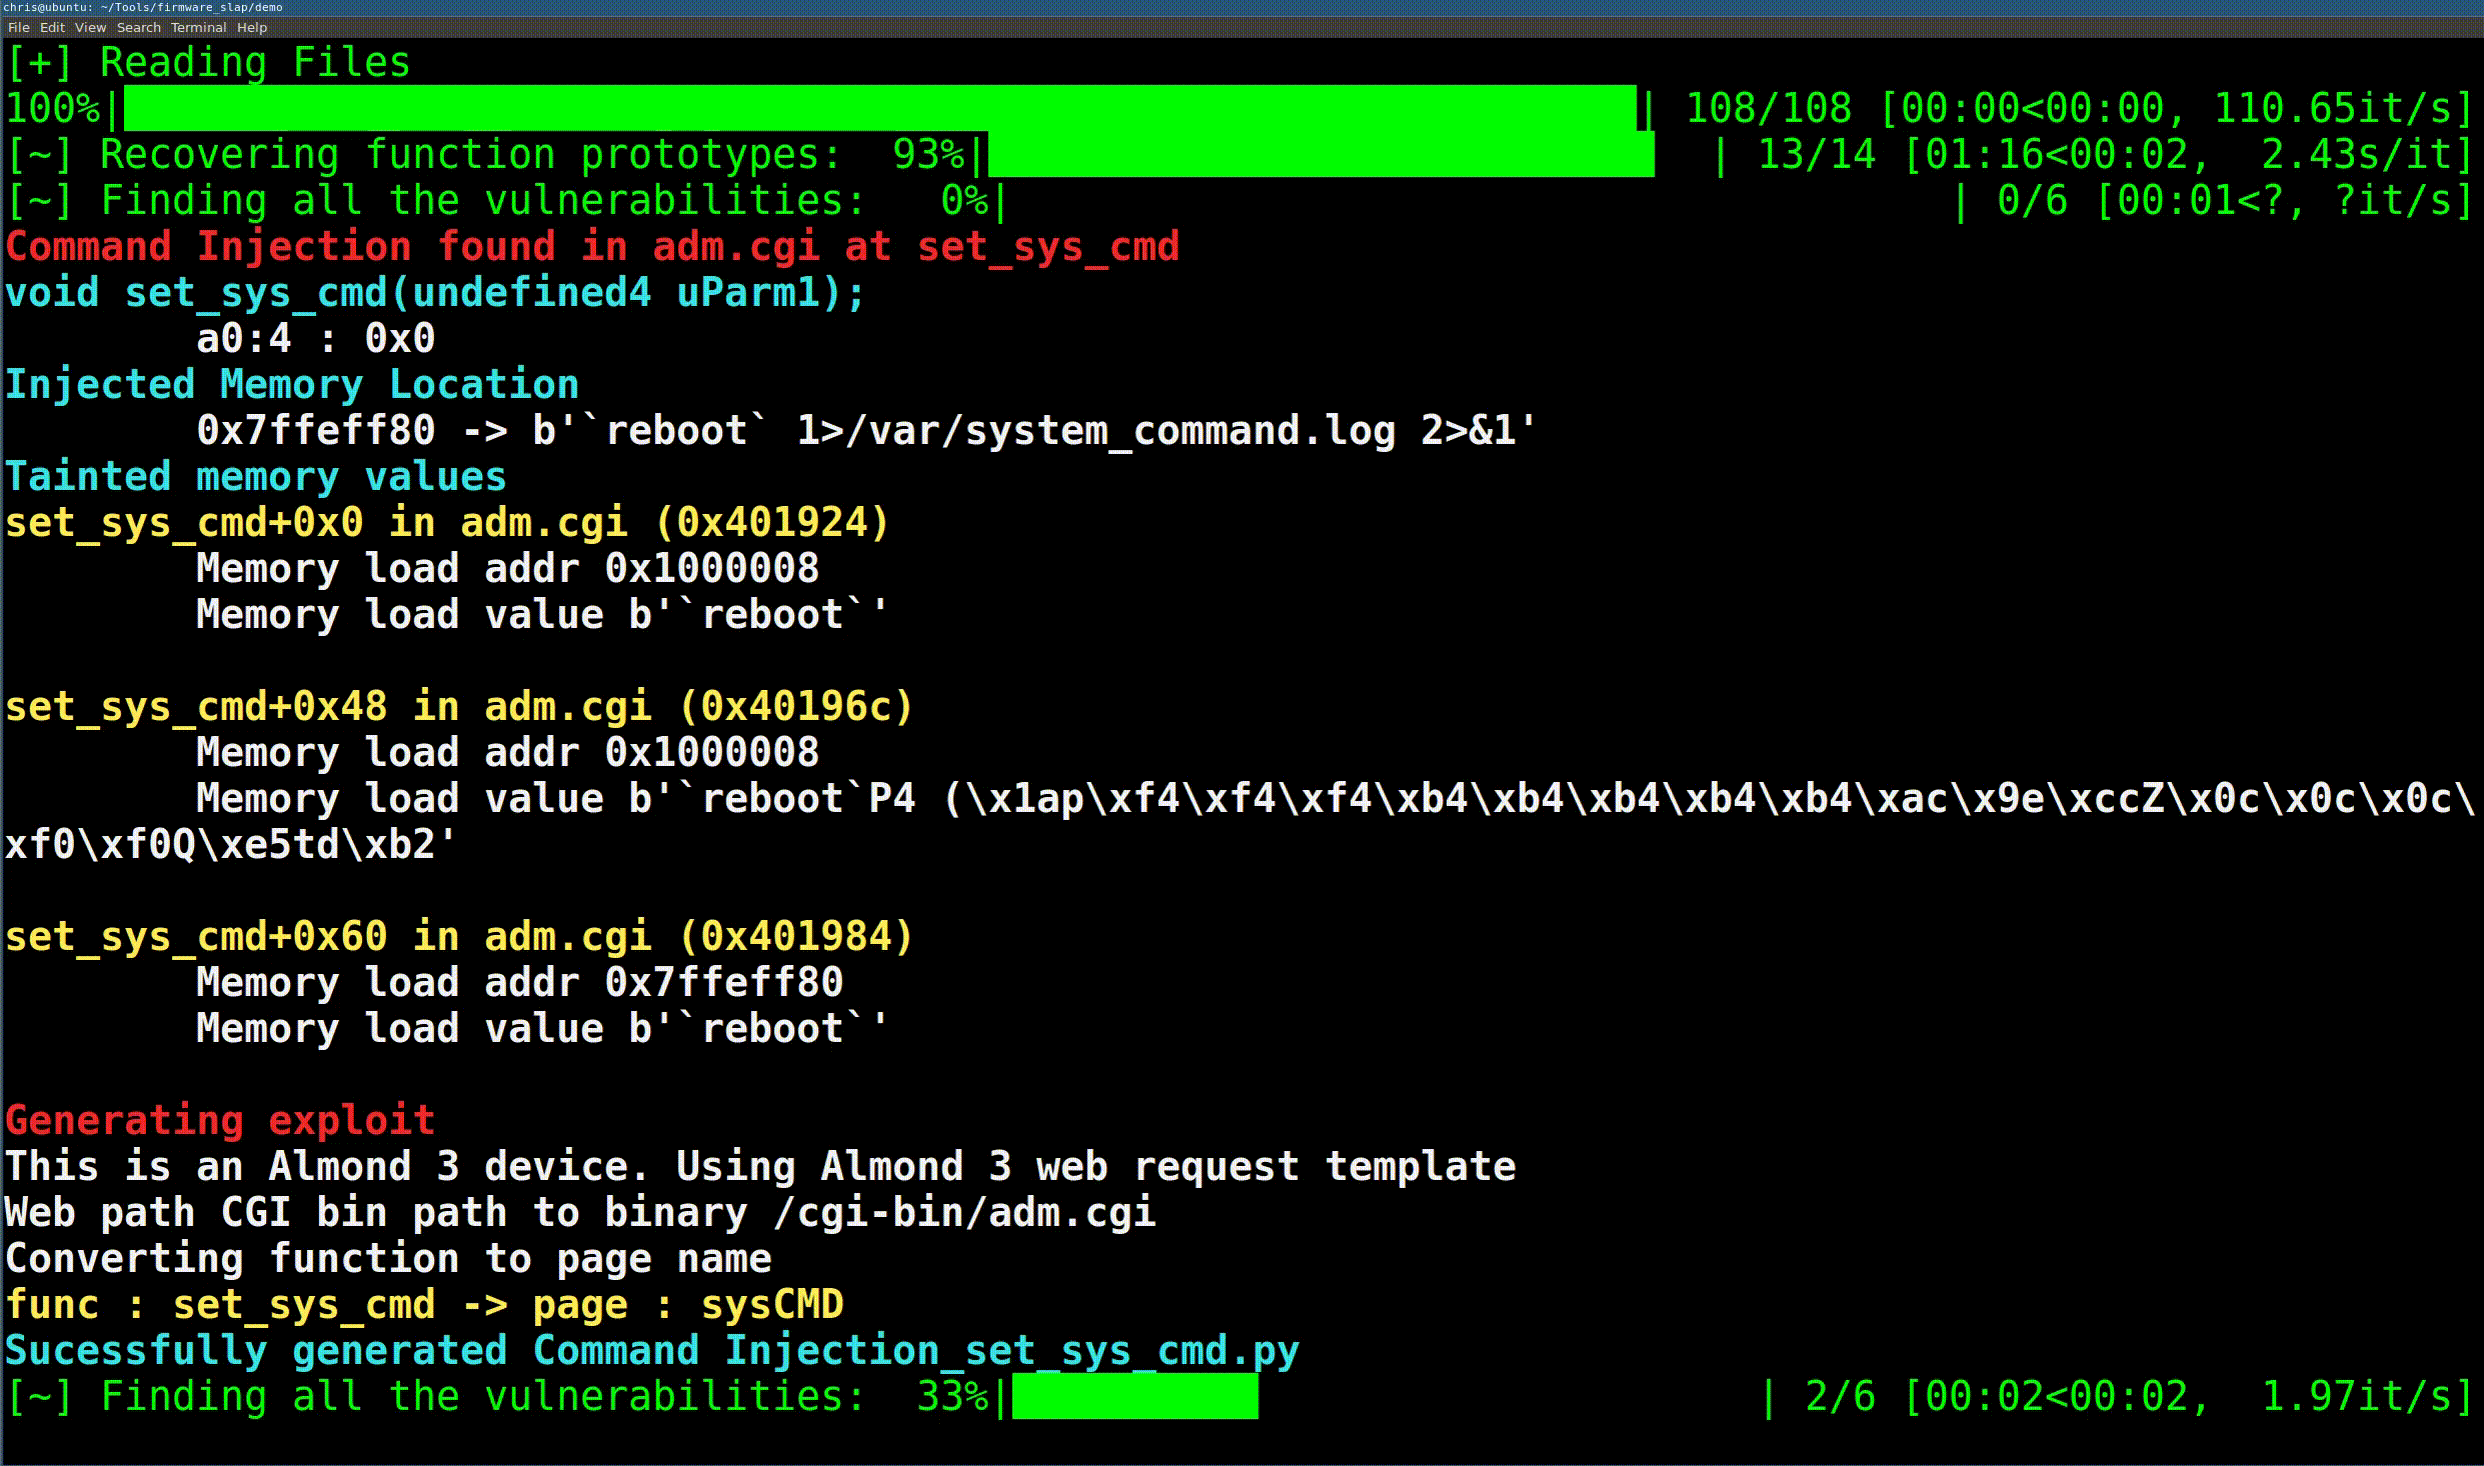
Discovering vulnerabilities in firmware through concolic analysis and function clustering.

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.