
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
454 results
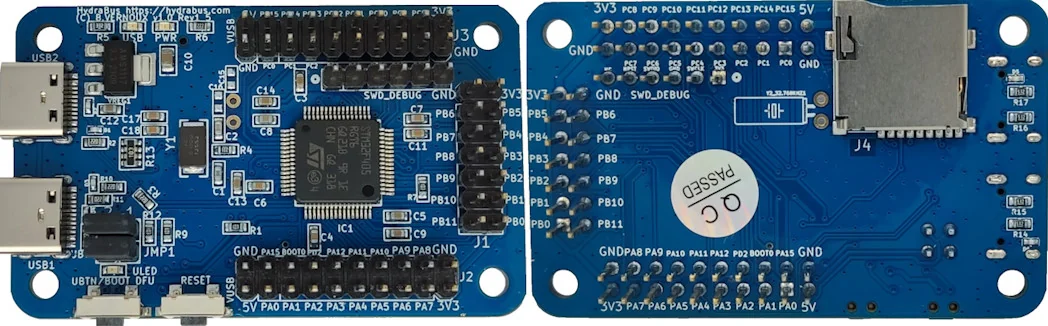
hydrafw preview

hydrafw

GitHubhydrabus/hydrafw

Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
debuggerseducationembedded-systems-security+6
448
7 months ago
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

binary-analysisembedded-systems-securityfirmware-analysis+3
4082 years ago
PrecIR preview

PrecIR

GitHubfurrtek/precir

Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
embedded-systems-securityfirmware-analysishardware-hacking+5
4556 months ago
firmware-reverse-engineering preview

firmware-reverse-engineering

GitHuborbitcurve/firmware-reverse-engineering

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

binary-analysiscurated-resourcesdynamic-analysis-sandboxing+5
18612 days ago
cerberus-re-skill preview

cerberus-re-skill

GitHubowenpawl/cerberus-re-skill

cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
binary-analysisdebuggersdynamic-analysis-sandboxing+7
19820 days ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
binary-analysisdynamic-analysis-sandboxingeducation+8
24214 days ago
project-memoria-detector preview

project-memoria-detector

GitHubforescout/project-memoria-detector

Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
embedded-systems-securityfirmware-analysisiot-security+2
3245 years ago
igvm preview

igvm

GitHubmicrosoft/igvm

Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…

cloud-securityembedded-systems-securityfirmware-analysis+2
15516 days ago
SupplyChainAttacks preview

SupplyChainAttacks

GitHubbinarly-io/supplychainattacks

Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
curated-resourceseducationfirmware-analysis+4
2831 year ago
device-modeling-language preview

device-modeling-language

GitHubintel/device-modeling-language

Domain-specific language for writing fast functional device models for virtual platforms. Compiles DML to C with API calls tailored for the Intel…

embedded-systems-securityfirmware-analysishardware-iot-security+2
13910 days ago
ghidralligator preview

ghidralligator

GitHubairbus-cyber/ghidralligator

Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+3
3302 years ago
bread preview

bread

GitHubtheldus/bread

Injectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…
binary-analysisdebuggersfirmware-analysis+2
32811 months ago
fwhunt-scan preview

fwhunt-scan

GitHubbinarly-io/fwhunt-scan

Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules
binary-analysisembedded-systems-securityfirmware-analysis+3
2451 year ago
sass-king preview

sass-king

GitHubflorianmattana/sass-king

Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
binary-analysiscode-analysiscurated-resources+8
3404 months ago
QuestStack preview

QuestStack

GitHubstarseed12345/queststack

Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
android-securitybinary-exploitationembedded-systems-security+5
19322 days ago
juniper-cve-2015-7755 preview

juniper-cve-2015-7755

GitHubhdm/juniper-cve-2015-7755

Notes, binaries, and related information from analysis of the CVE-2015-7755 & CVE-2015-7756 issues within Juniper ScreenOS
binary-analysiscryptographyexploitation+3
1055 years ago
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
command-and-controlembedded-systems-securityencryption-decryption-tools+8
2061 month ago
rpef preview

rpef

GitHubmncoppola/rpef

Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers

embedded-systems-securityexploitationfirmware-analysis+6
12412 years ago
Previous1…345…26Next