
attesor
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
ai-assisted-reversingbinary-analysiseducation+3
87
inokinoki/attesorAI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 onekey-sec/unblob
Extract files from any kind of container formats
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 cryptoadvocate/dcsgonefwbsp
The firmware board support package home of the Circuit Crafters first electronic badge project.
 kaleth4/cve-2025-0690
Technical analysis of CVE-2025-0690: integer overflow in GRUB2's read command leading to heap out-of-bounds write, arbitrary code execution, and…
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
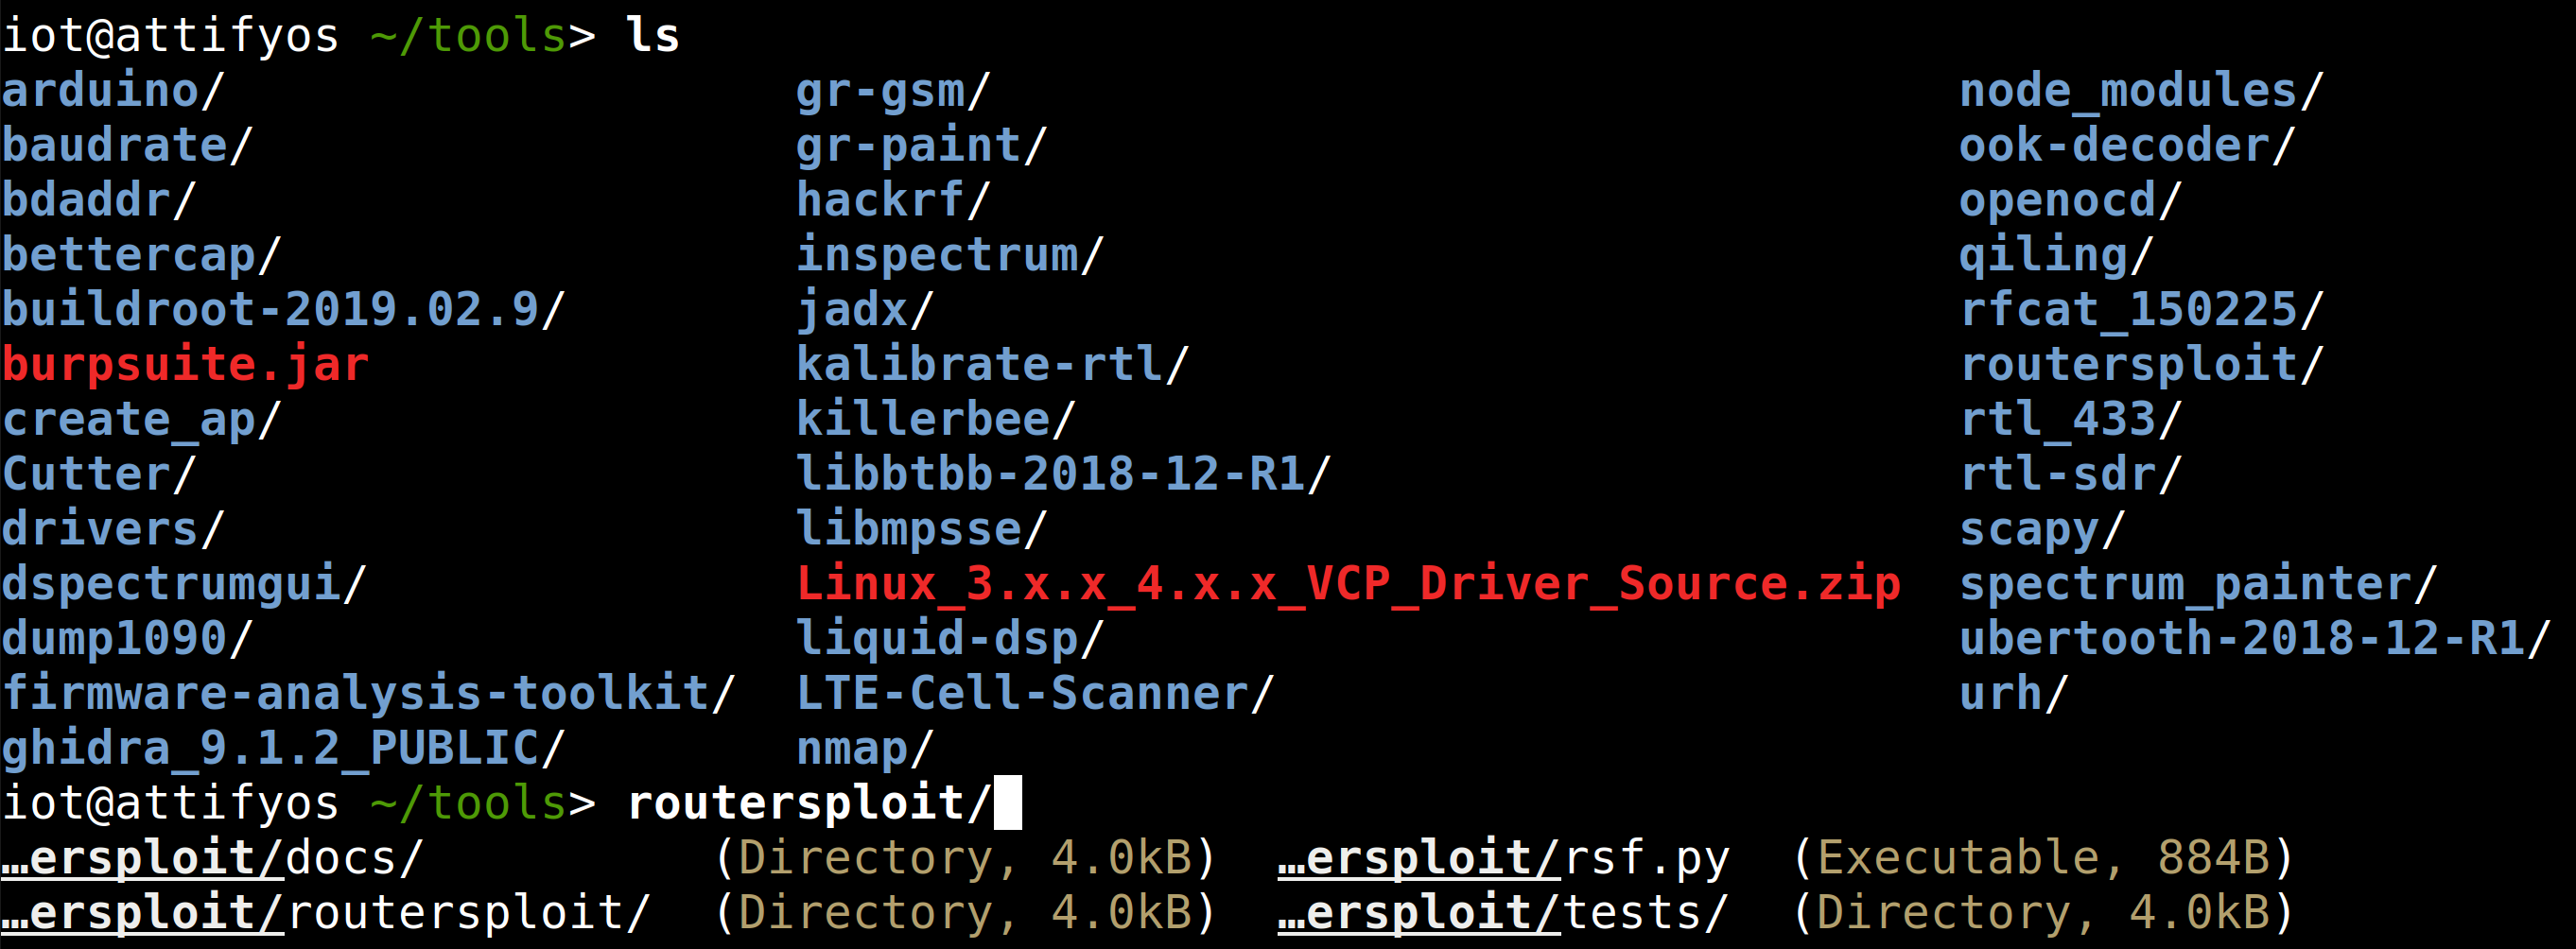 adi0x90/attifyos
Attify OS - Distro for pentesting IoT devices
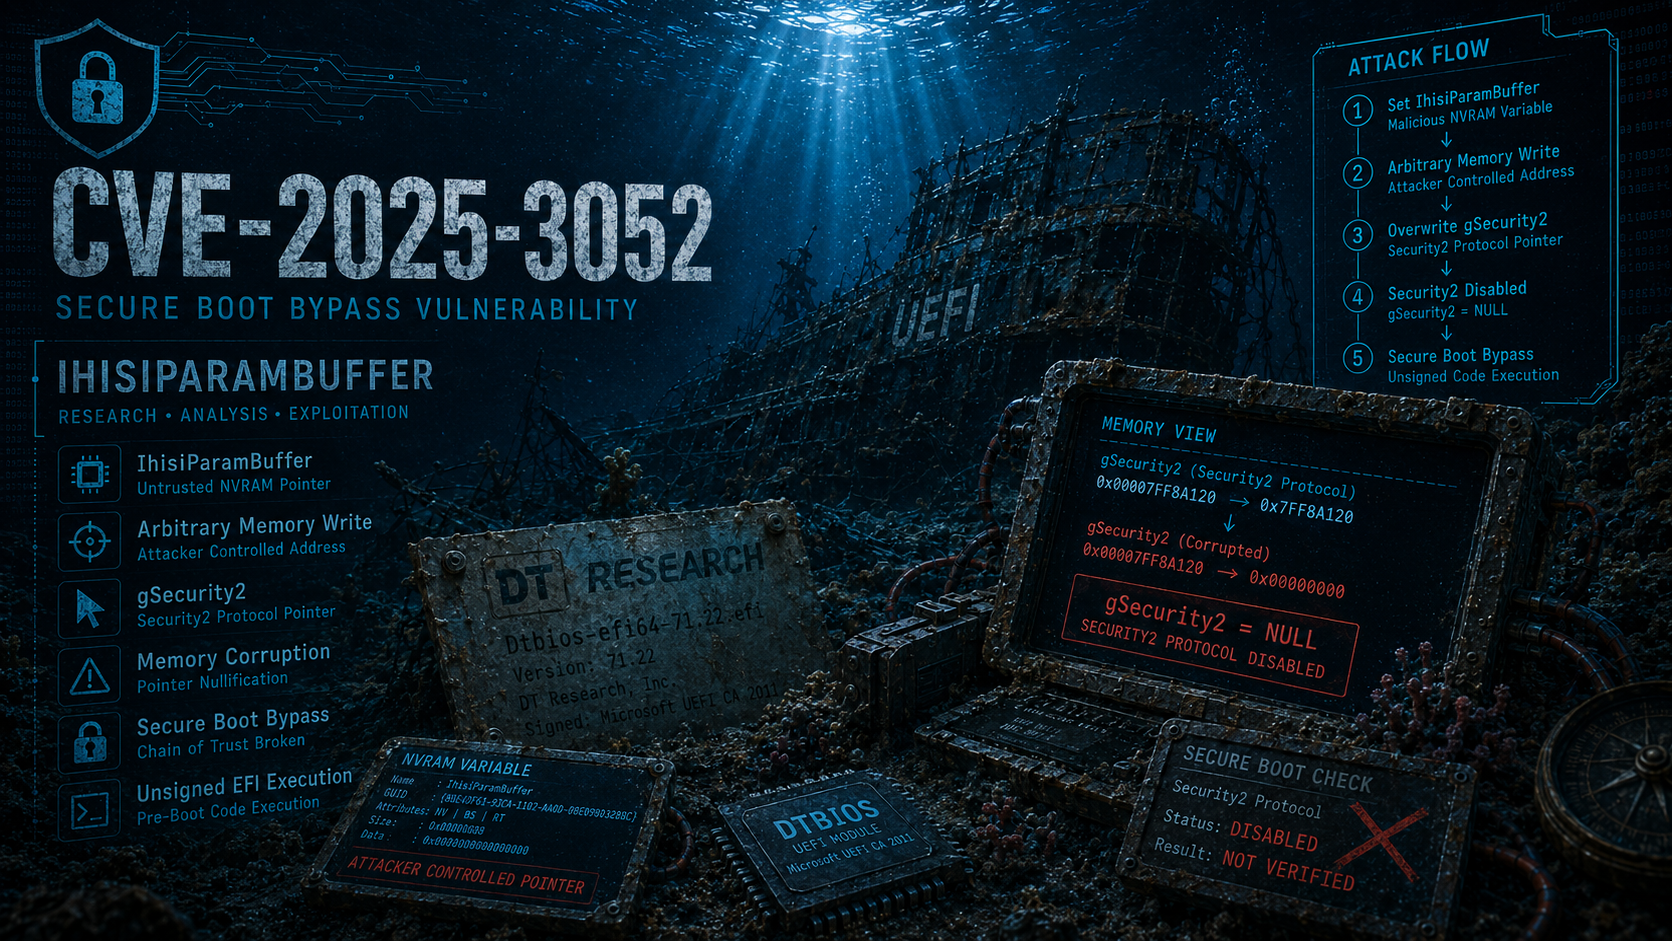 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 xairy/lights-out
Tools for controlling webcam LED on ThinkPad X230
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 risuxx/cve-2023-34853
Disclosure of CVE-2023-34853: a stack overflow vulnerability in Supermicro X12DPG-QR BIOS firmware allowing local privilege escalation to DXE Runtime…
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
 owasp/owasp-istg
The IoT Security Testing Guide (ISTG) provides a comprehensive methodology for penetration tests in the IoT field, offering flexibility to adapt…
 zb3/tiandy-research
This repository contains the results of my August 2020 research of Tiandy's IPC/NVR firmware. I found two vulnerabilities that could be used to…