
TEE-reversing
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
android-securitybinary-analysiscurated-resources+9
1.0k
enovella/tee-reversingA curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 pixel-props/build.prop
Bash script to build your own system.prop
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
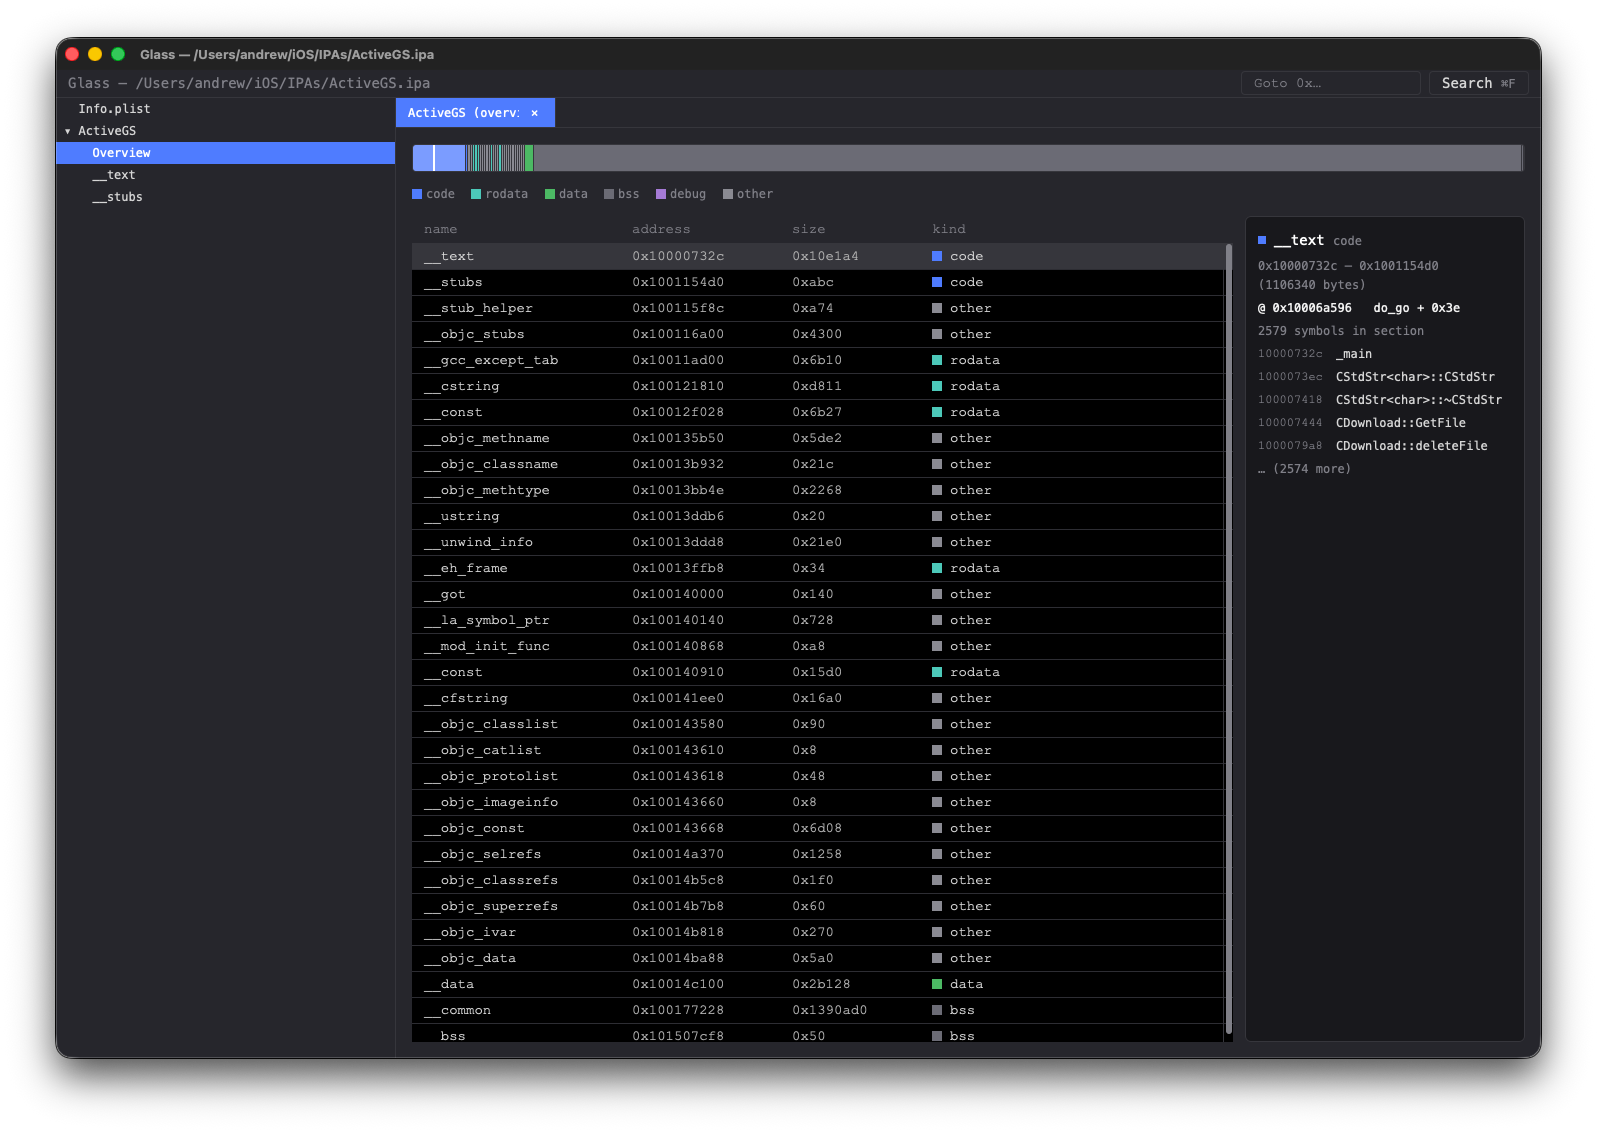 azw413/glass
Glass - a fast and free IDA Pro alternative
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 oneplusoss/android_kernel_modules_and_devicetree_oneplus_sm8550
Low-level kernel modules and device tree source for the OnePlus 11 (sm8550), enabling hardware bring-up, driver analysis, and embedded system…
 kasnria001/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 oscardagrach/cve-2019-5700
CVE-2019-5700
 xcracker000/cve-2024-56426
CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
 asarr22/root-my-galaxy-s938b
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.