
Root-My-Galaxy-S938B
 asarr22/root-my-galaxy-s938b
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
android-securityexploitationfirmware-analysis+4
1
asarr22/root-my-galaxy-s938bKSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 kaleth4/cve-2025-0690
Technical analysis of CVE-2025-0690: integer overflow in GRUB2's read command leading to heap out-of-bounds write, arbitrary code execution, and…
 mercul1ninna/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
 donfanning/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
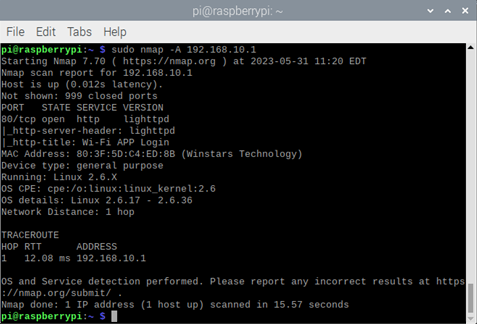 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 icycu123/cve-2024-1781
CVE-2024-1781
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
 linuxoid-cn/mi8e5-unlocker-by-cve-2026-43499
基于 CVE-2026-43499 的 8E5 机型自动化解锁辅助工具,仅限授权安全研究与自有设备使用。
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.