
wch-ch56x-lib
 hydrausb3/wch-ch56x-lib
Library for WCH CH56x-based boards with tested USB3/USB2/HSPI/SerDes drivers, logging and deferred interrupts
embedded-systems-securityfirmware-analysishardware-hacking+2
16
hydrausb3/wch-ch56x-libLibrary for WCH CH56x-based boards with tested USB3/USB2/HSPI/SerDes drivers, logging and deferred interrupts
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
 vl4dr/cve-2024-42642
Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…
 bahaabdelwahed/st
IoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…
 jaydcarlson/c2-printf
Print trace messages over a Silicon Labs C2 debugger connection
 20enderdude20/ghidra_v810_v830
Ghidra processor description module for NEC/Renesas v810 and v830 families
 finngineering/ch55x_firmware_extractor
Firmware extractor for CH55x microprocessors
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 heapframe/seetong-ts81xxd3x-rce
CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
 gadorach/vankyo-s30-bootloader-unlock
Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method
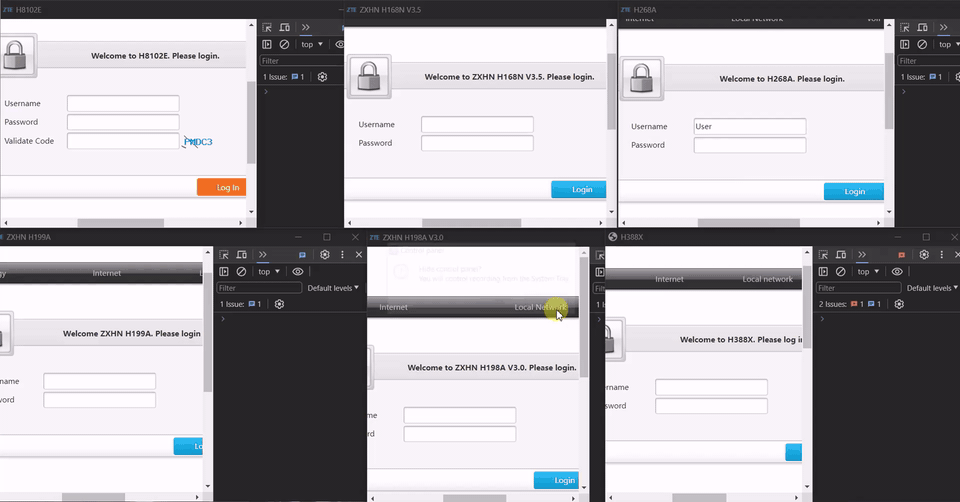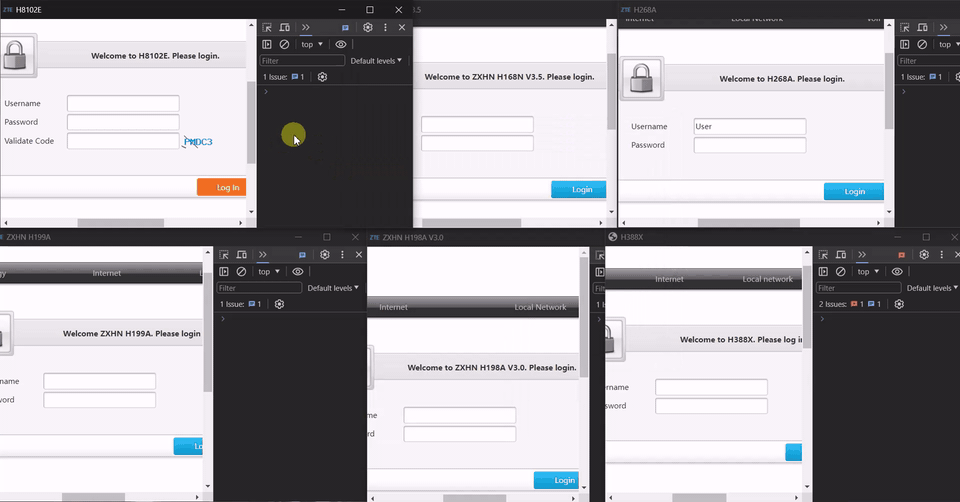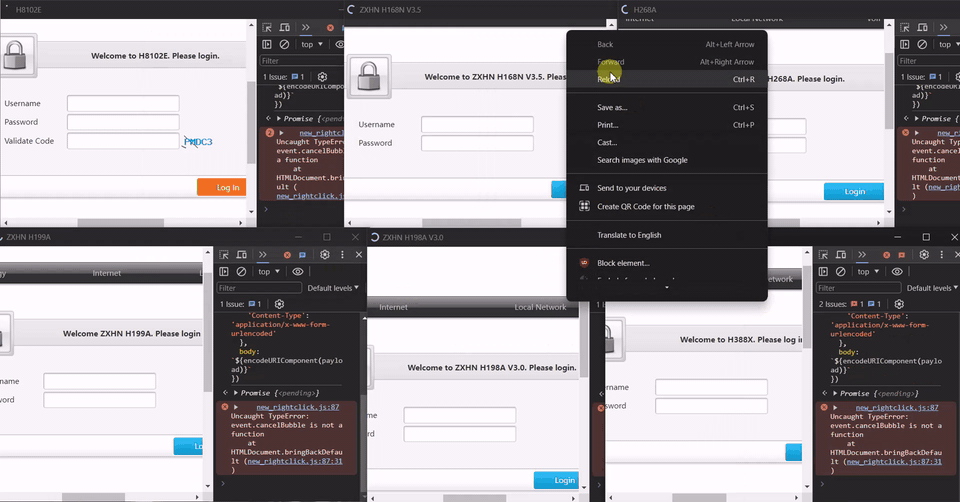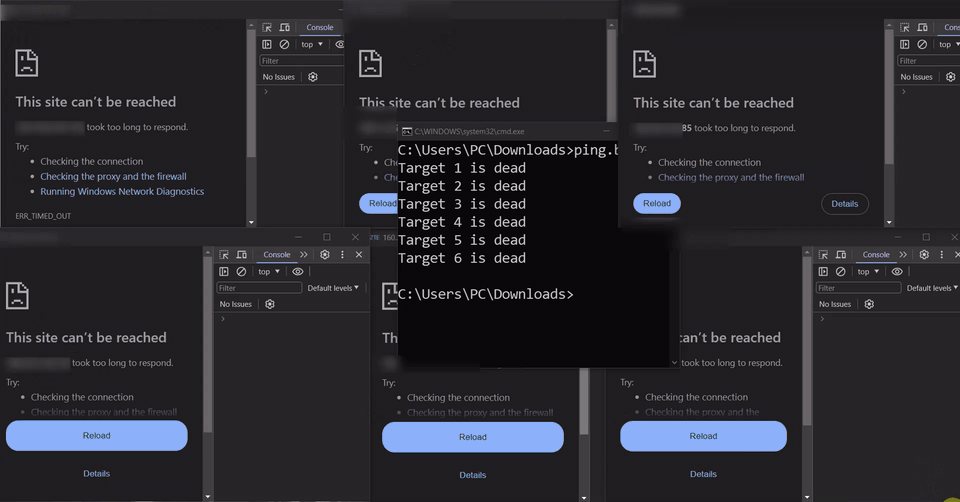 minanagehsalalma/cve-2026-34473-unauthenticated-dos-zte-routers
Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.
 fwnavy/rmasmoke
RMASmoke main repo. CVE-2025-1122
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 freax13/cve-2023-31346-poc
Proof-of-concept demonstrating memory leaks in AMD SEV-SNP firmware guest message headers and CPUID request, enabling extraction of sensitive guest…
 luismirandaacebedo/cve-2025-65855
Security advisory for CVE-2025-65855 - Multiple vulnerabilities in HelpFlash IoT OTA update mechanism
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…