

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
79.9k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
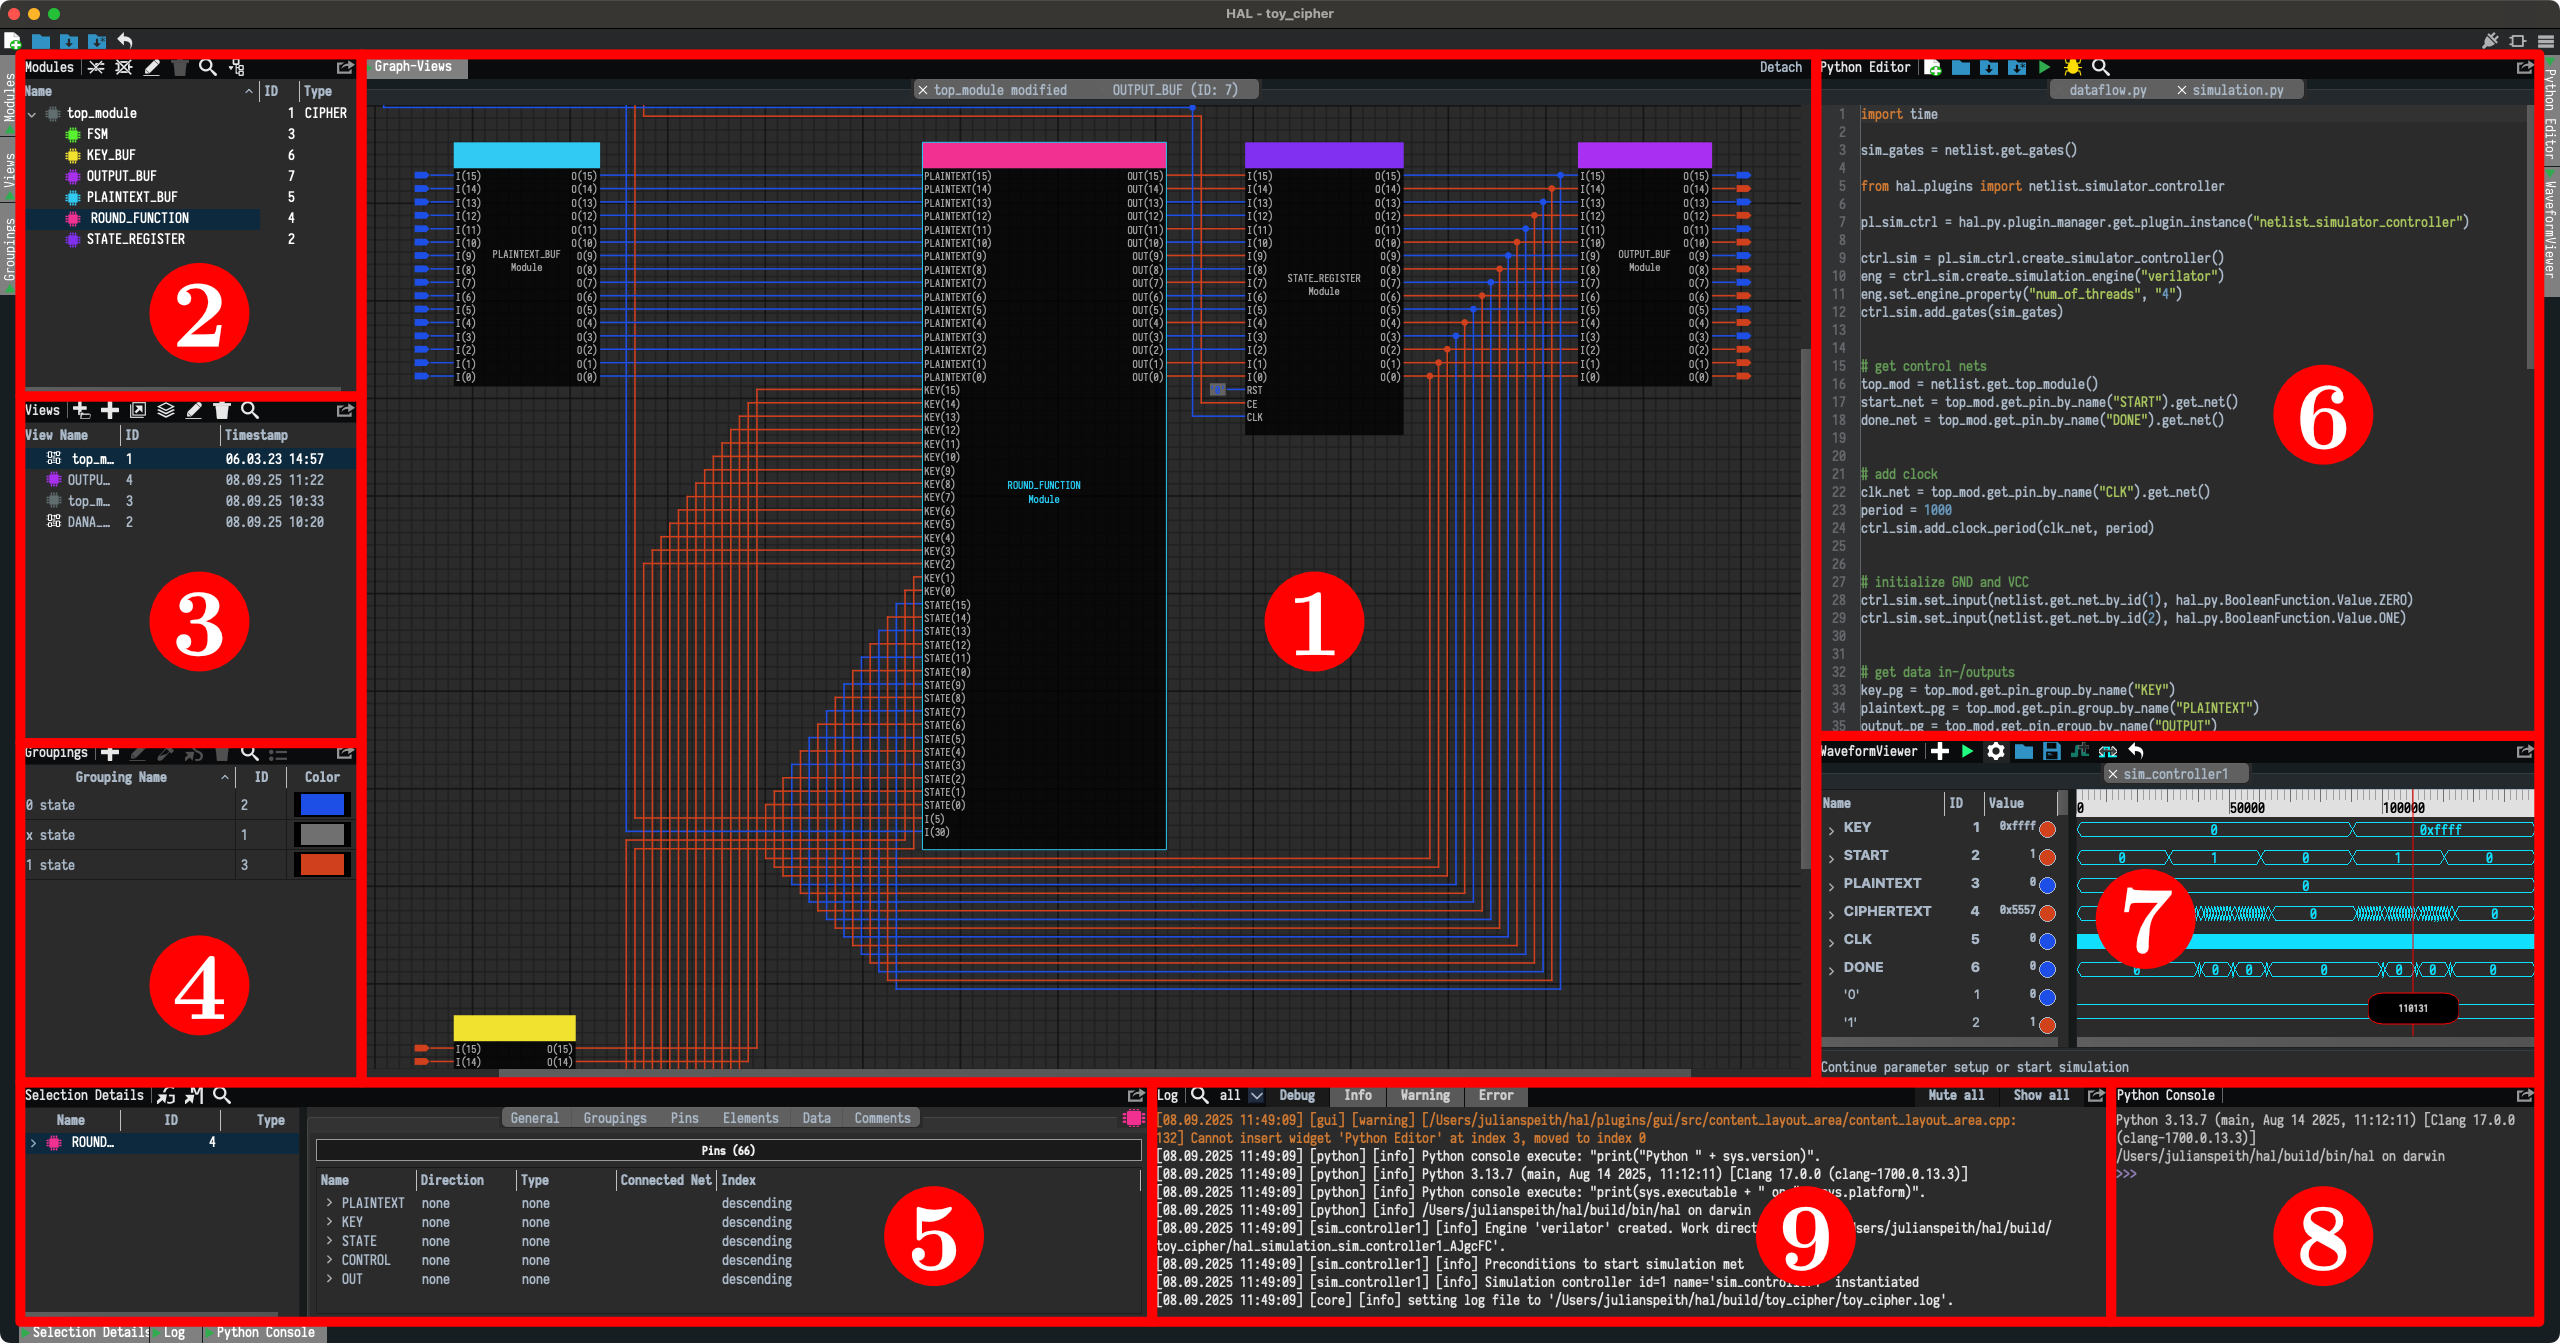
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
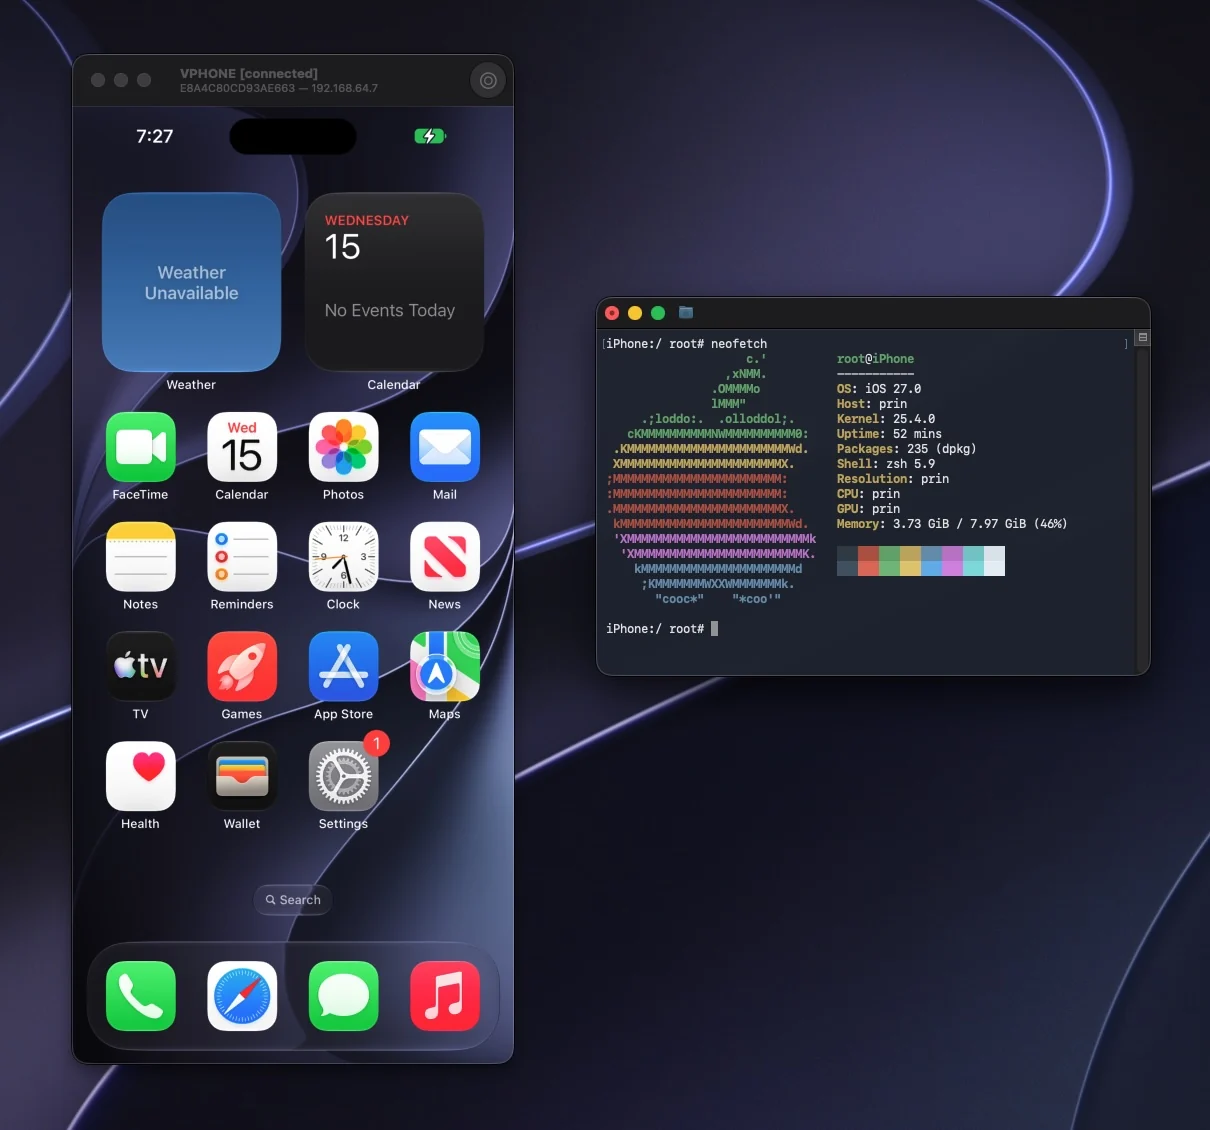 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 codykociemba/nolongerevil-thermostat
Breathe fresh life into your bricked Nest, now with 100% less evil!
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 intel/device-modeling-language
Domain-specific language for writing fast functional device models for virtual platforms. Compiles DML to C with API calls tailored for the Intel…
 microsoft/secureboot_objects
Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
 redballoonsecurity/ofrak
Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.