

qemu
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
embedded-systems-securityfirmware-analysisgeneral-purpose-utilities+2
13.4k
qemu/qemuOfficial QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 rianhanft/marauderbox
A fork of the marauder firmware with Nyan box capabilities
 george0papasotiriou/cve-2026-21009-ecdsa-nonce-reuse-in-iot-firmware-signing
Educational Python simulation demonstrating ECDSA nonce reuse in IoT firmware signing, showing how an attacker can recover private keys from two…
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
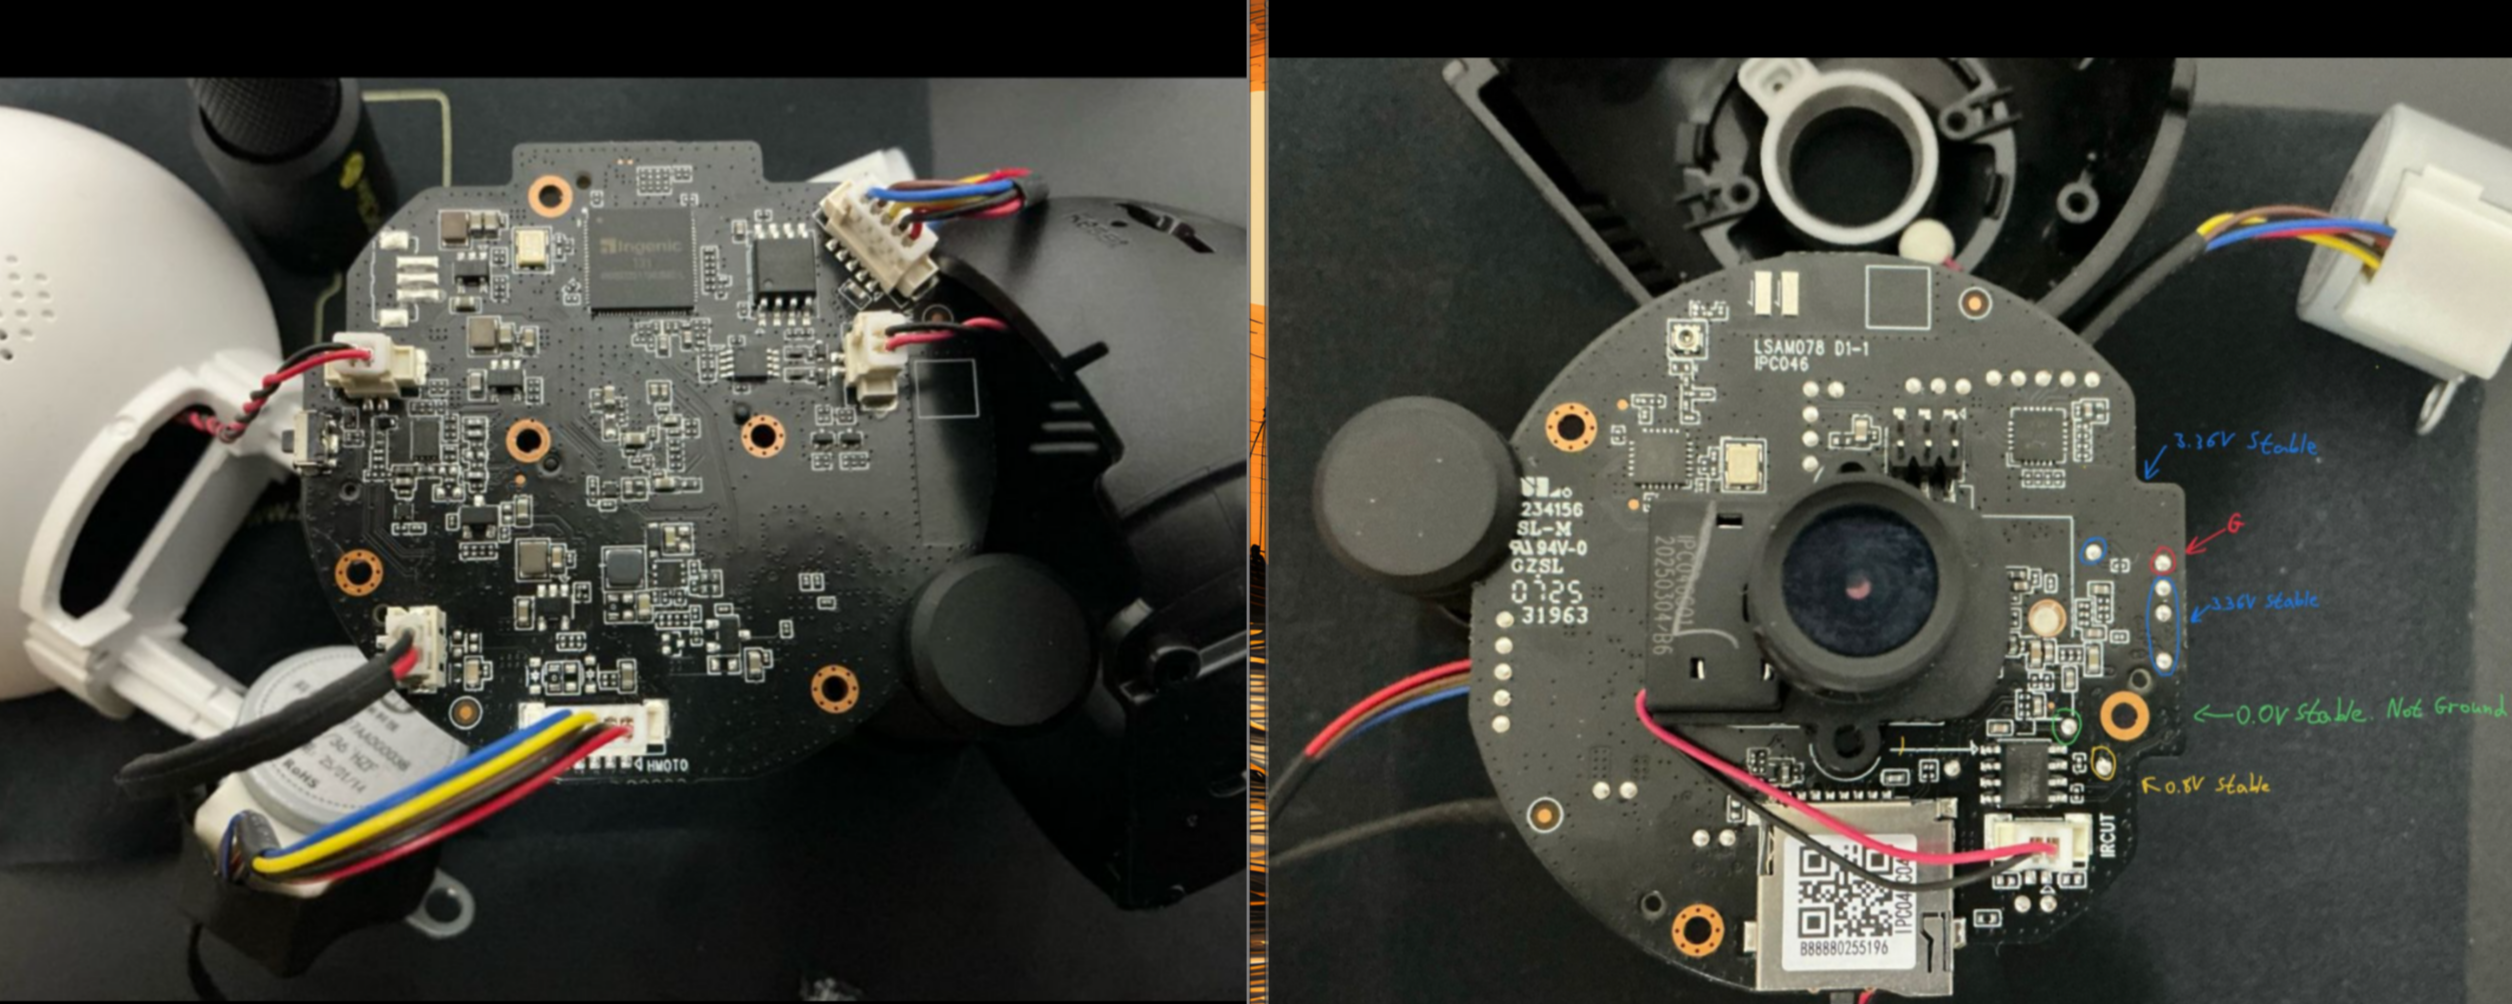 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 jaden-bowers/tenda-router-vr-and-exploit
Writeup for Tenda AC15 router firmware rehosting and remote command execution (CVE-2020-10987) exploit replication.
 ilgobbo00/cve-2023-6241-pixel7_adaptation
Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.