
pyghidra-mcp
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
ai-assisted-reversingbinary-analysiscode-analysis+7
40414h 48m ago
clearbluejar/pyghidra-mcpPython Command-Line Ghidra MCP
 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
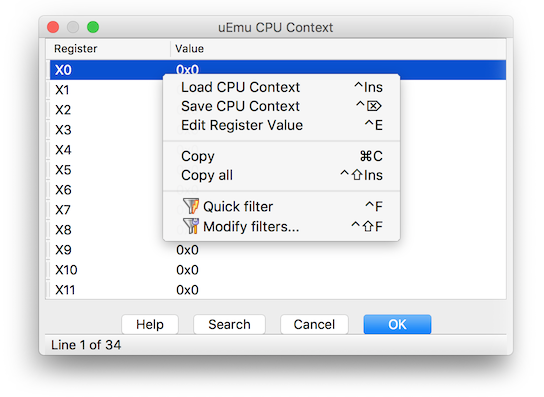 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 colton1skees/dna
LLVM based static binary analysis framework
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
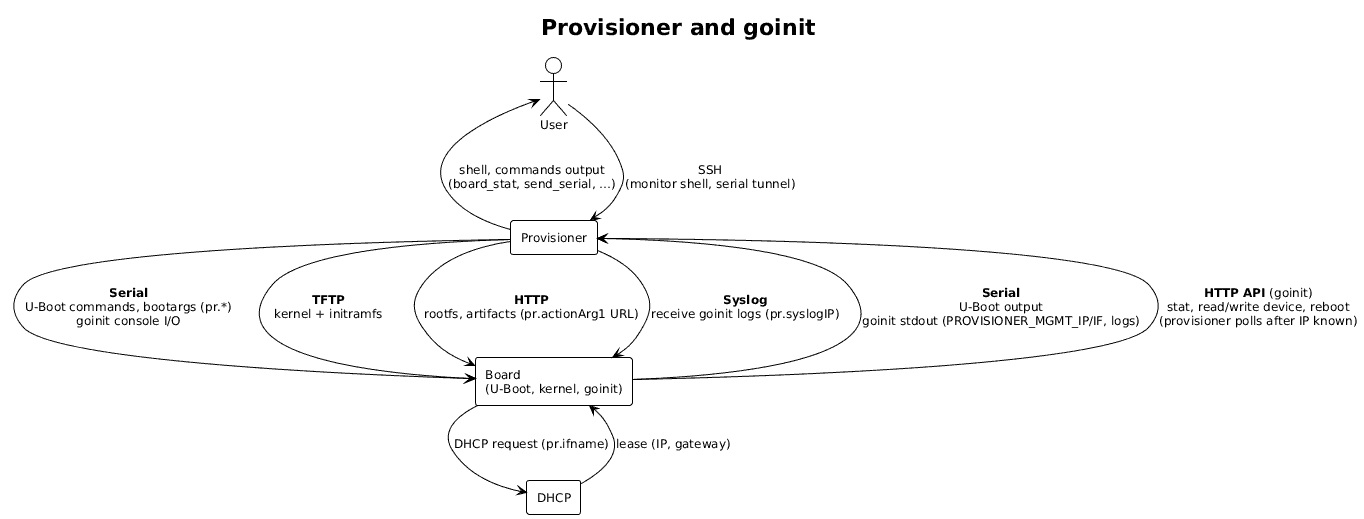 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 hydrausb3/wch-ch56x-lib
Library for WCH CH56x-based boards with tested USB3/USB2/HSPI/SerDes drivers, logging and deferred interrupts
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…