

vphone-cli
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
exploitationfirmware-analysisios-security+3
15.9k
lakr233/vphone-cliBoot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 jm00nj/hpe-aruba-aos8-vulnerabilities
ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 angr/angr
A powerful and user-friendly binary analysis platform!
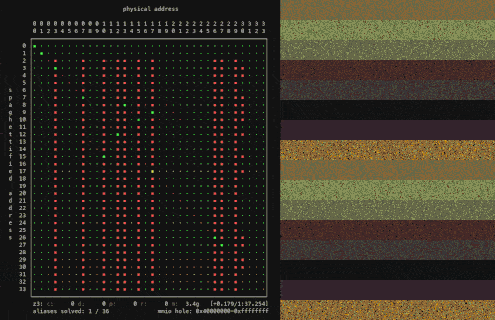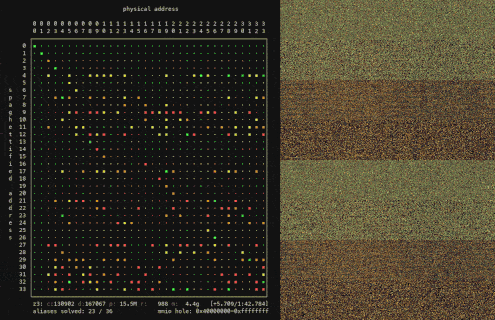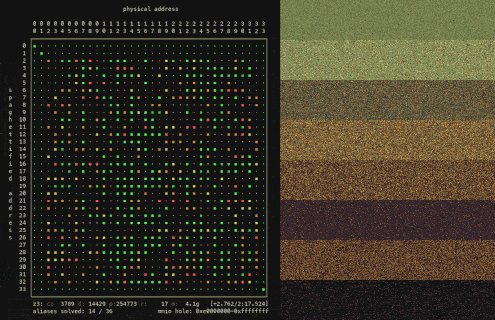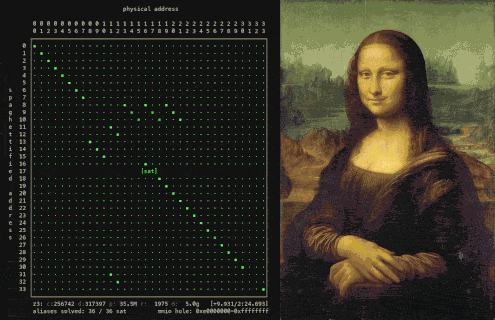 xoreaxeaxeax/skitter-creek-bath-salts
Unlocking _everything_ on the CPU with DRAM scrambling
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!