
vphone-cli
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
exploitationfirmware-analysisios-security+3
16.3k
lakr233/vphone-cliBoot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 onekey-sec/unblob
Extract files from any kind of container formats
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
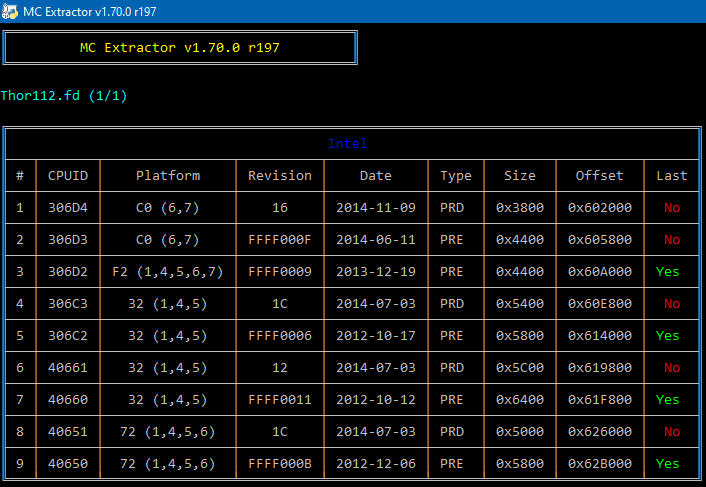 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…

 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
 infobyte/ezviz_lan_rce
PoC exploits and Docker build environment for CVE-2023-34551 and CVE-2023-34552 targeting EZVIZ IP cameras, with DEF CON 31 Hardware Hacking Village…
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…

 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
 redballoonsecurity/ofrak
Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.
 trungnguyen1909/qemu-t8030
iPhone 11 emulated on QEMU