
CVE-2022-4539
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
fingerprint-spoofingids-ips-evasionimpersonation-tools+3
abdurahmon3236/cve-2022-4539Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 d4vinci/scrapling
Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…
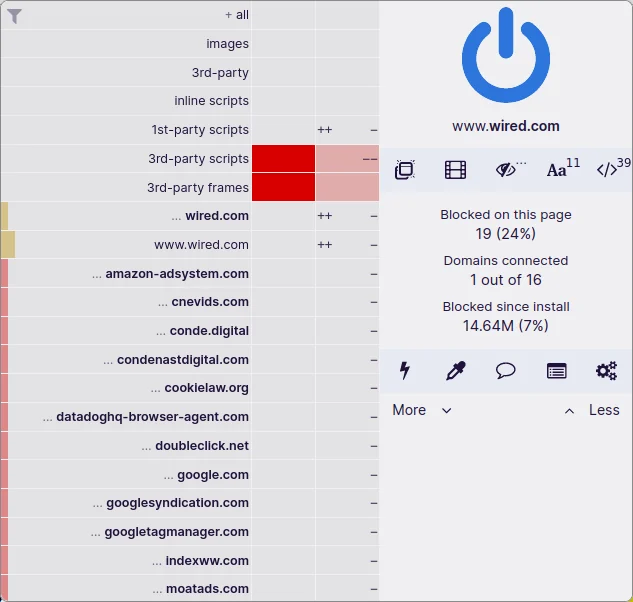 gorhill/ublock
Wide-spectrum content blocker for browsers that blocks ads, trackers, coin miners, and malicious sites using filter lists and customizable privacy…
 microsoft/playwright
Browser automation framework with a single API for Chromium, Firefox, and WebKit. Supports web testing, scraping, screenshots, and network…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 apify/crawlee
Node.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
 ultrafunkamsterdam/nodriver
Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
 bromite/bromite
Android Chromium fork with built-in ad blocking, anti-fingerprinting mitigations, DNS-over-HTTPS, and hardened privacy and security defaults.
 privacytests/privacytests
Automates browser privacy testing and renders human-readable results across fingerprinting, tracking, and data-leak vectors.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
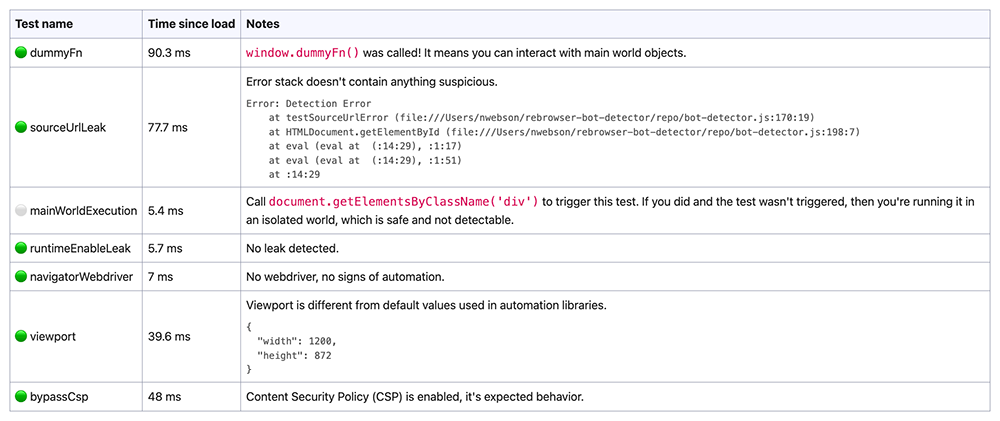 rebrowser/rebrowser-patches
Collection of patches for puppeteer and playwright to avoid automation detection and leaks. Helps to avoid Cloudflare and DataDome CAPTCHA pages.…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
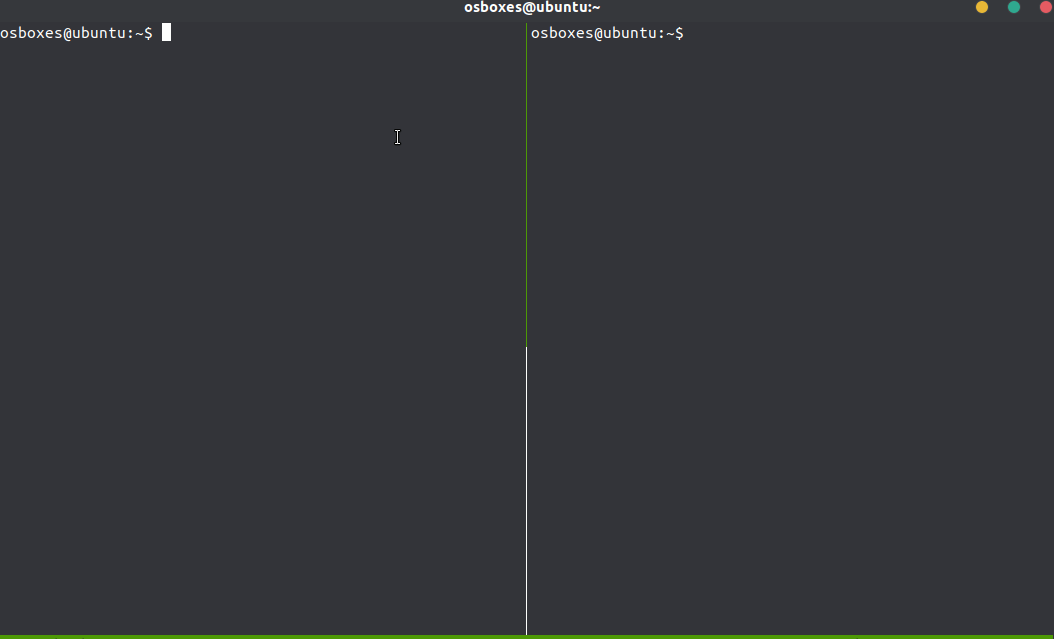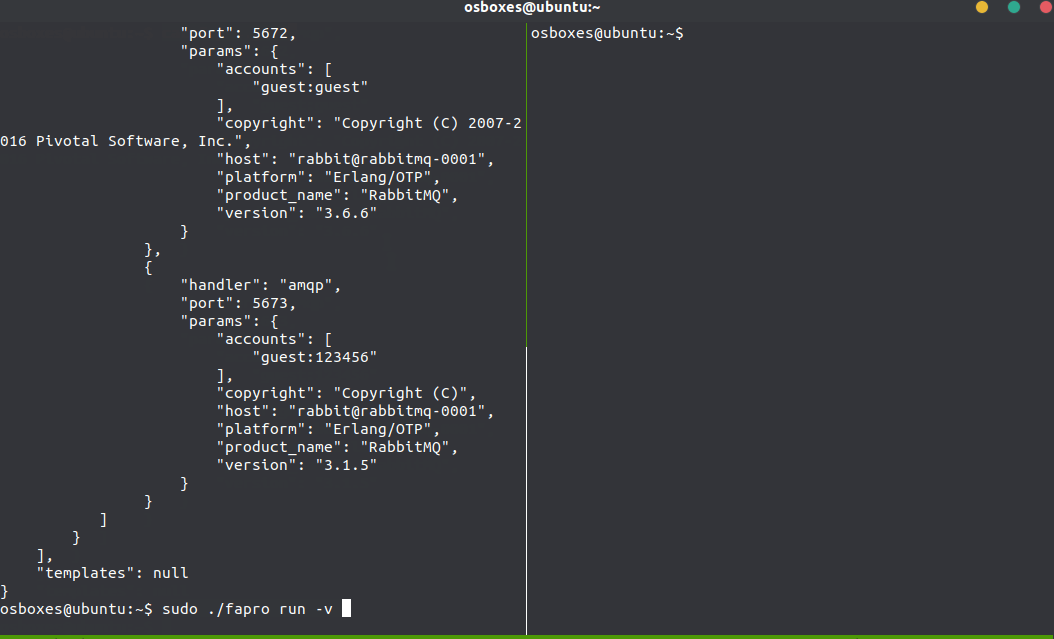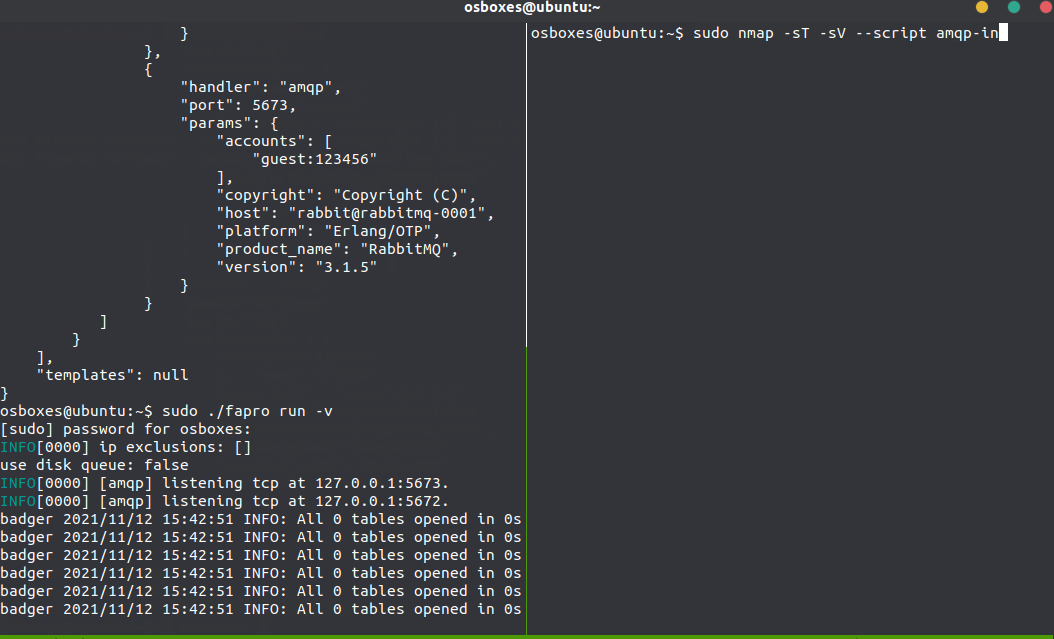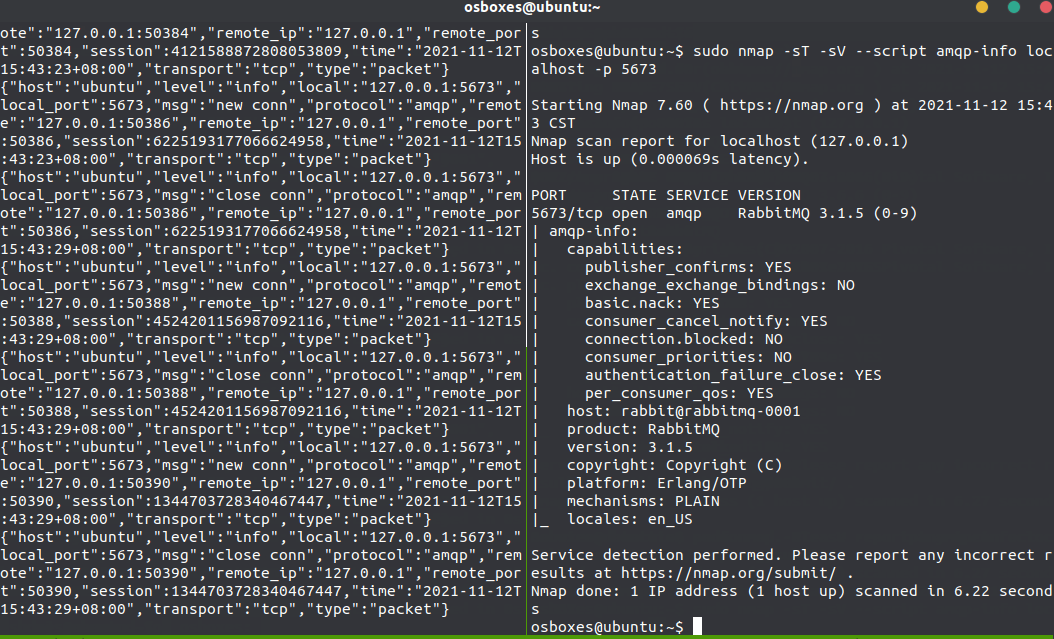 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
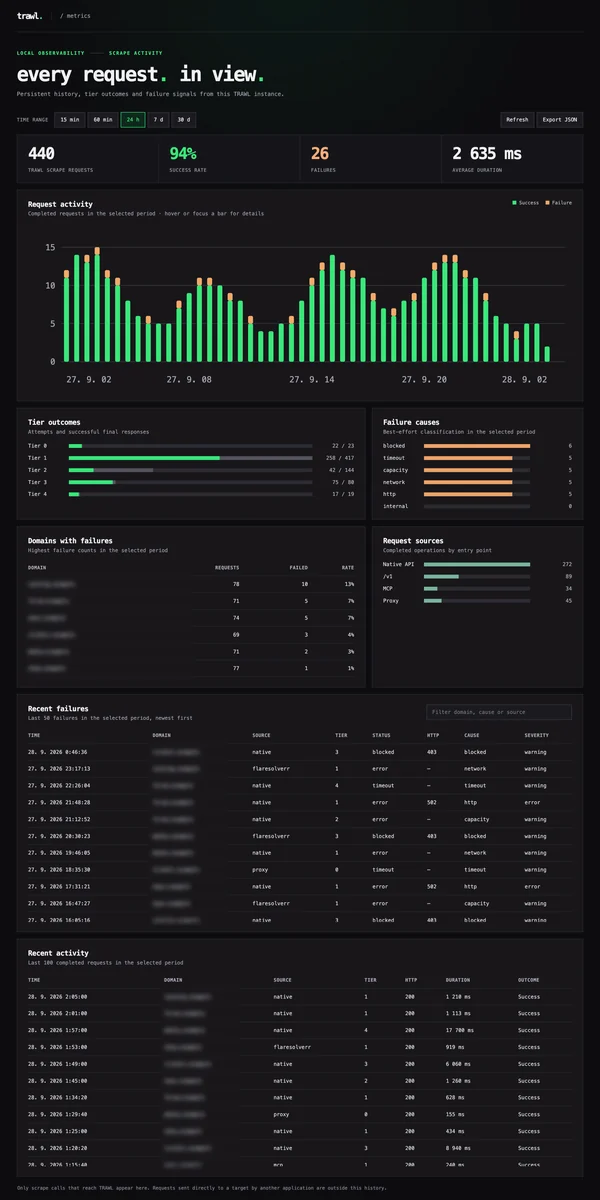 germondai/trawl
Self-hosted scraping engine — bypasses any JS challenge & captcha: Cloudflare, Turnstile, reCAPTCHA, hCaptcha, GeeTest. FlareSolverr & Byparr…