Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
79 results
WiFi-Pumpkin-deprecated preview
Archived

WiFi-Pumpkin-deprecated

GitHubp0cl4bs/wifi-pumpkin-deprecated

DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
captcha-bypasscommand-and-controldns-analysis+9
3.2k
6 years ago
CVE-2026-0073-Android-ADBD-bypass-POC preview

CVE-2026-0073-Android-ADBD-bypass-POC

GitHubmartinpsdev/cve-2026-0073-android-adbd-bypass-poc

CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

android-securityexploitationmobile-security+3
224 months ago
killosx preview

killosx

GitHubd4rkcat/killosx

use the Apple CoreText exploit (CVE-2012-3716) and launch an AP to affect all devices within wifi range

exploitationred-teamingvulnerability-analysis+2
2211 years ago
easy-exploits preview

easy-exploits

GitHubefchatz/easy-exploits

Curated collection of proof-of-concept exploits for 16 CVEs targeting web applications (ASUS, D-Link, Netgear, TP-Link, Xiaomi) and Wi-Fi WPA3-SAE,…
educationexploitationpenetration-testing+3
173 years ago
CVE-2020-28148 preview

CVE-2020-28148

GitHubfengchenzxc/cve-2020-28148

Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP…

authentication-authorizationexploitationnetwork-security+4
174 years ago
R7000_httpd_BOF_CVE-2020-15416 preview

R7000_httpd_BOF_CVE-2020-15416

GitHubk3vinlusec/r7000_httpd_bof_cve-2020-15416

Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…

binary-exploitationeducationembedded-systems-security+5
5 years ago
Packages_wpa_supplicant8_CVE-2021-0326 preview

Packages_wpa_supplicant8_CVE-2021-0326

GitHubnanopathi/packages_wpa_supplicant8_cve-2021-0326

Source code of wpa_supplicant and hostapd, focused on CVE-2021-0326 vulnerability for analysis, testing, and understanding of Wi-Fi security flaws.
exploitationnetwork-securityvulnerability-analysis+1
4 years ago
fragattacks preview

fragattacks

GitHubvanhoefm/fragattacks

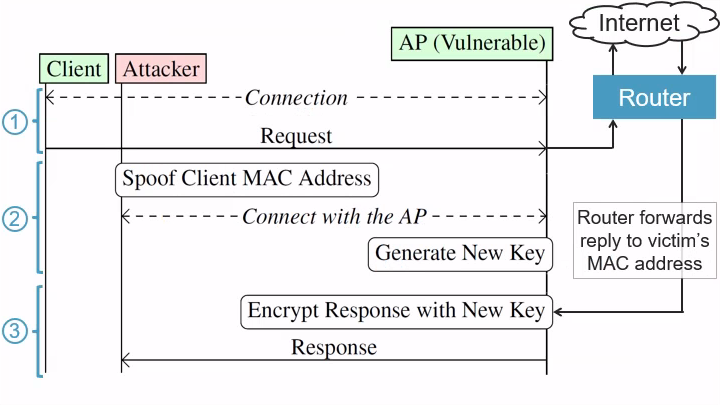
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
exploitationnetwork-securitypenetration-testing+3
1.3k1 year ago
macstealer preview

macstealer

GitHubvanhoefm/macstealer

MacStealer: Wi-Fi Client Isolation Bypass
exploitationinformation-gatheringnetwork-security+5
5599 months ago
external_wpa_supplicant_8_AOSP10_r33_CVE-2021-0516 preview

external_wpa_supplicant_8_AOSP10_r33_CVE-2021-0516

GitHubsatheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516

Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
android-securitybinary-exploitationexploitation+3
4 years ago
external_wpa_supplicant_8_AOSP10_r33CVE-2021-0326 preview

external_wpa_supplicant_8_AOSP10_r33CVE-2021-0326

GitHubshaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326

Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…
android-securityembedded-systems-securityexploitation+3
4 years ago
CVE-2019-13361 preview

CVE-2019-13361

GitHublodi-g/cve-2019-13361

Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
exploitationiot-securitypenetration-testing+2
7 years ago
blogpost_cve-2018-19987-analysis preview

blogpost_cve-2018-19987-analysis

GitHubnahueldsanchez/blogpost_cve-2018-19987-analysis

This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers

educationexploitationfirmware-analysis+4
25 years ago
eap_pwn preview

eap_pwn

GitHubhelica-core/eap_pwn

poc of CVE-2023-52160

exploitationpenetration-testingvulnerability-analysis+2
72 years ago
WEF preview

WEF

GitHubd3ext/wef

Wi-Fi Exploitation Framework

exploitationinformation-gatheringpenetration-testing+4
3.2k1 year ago
KTO preview

KTO

GitHubymsniper/kto

Automated Wi-Fi deauthentication tool that continuously scans for clients on a target SSID and kicks non-whitelisted devices. Features whitelist…
exploitationids-ips-evasionnetwork-security+4
2666 days ago
airpwn-ng preview

airpwn-ng

GitHubicsec/airpwn-ng

Packet injection for wifi; simplified.
exploitationpacket-sniffing-analysispenetration-testing+2
396 months ago
Bluetooth-Attacks-CVE-2025-27840 preview

Bluetooth-Attacks-CVE-2025-27840

GitHubdemining/bluetooth-attacks-cve-2025-27840

Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth

bluetooth-securitycryptographyeducation+7
121 year ago
Previous12345Next