metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

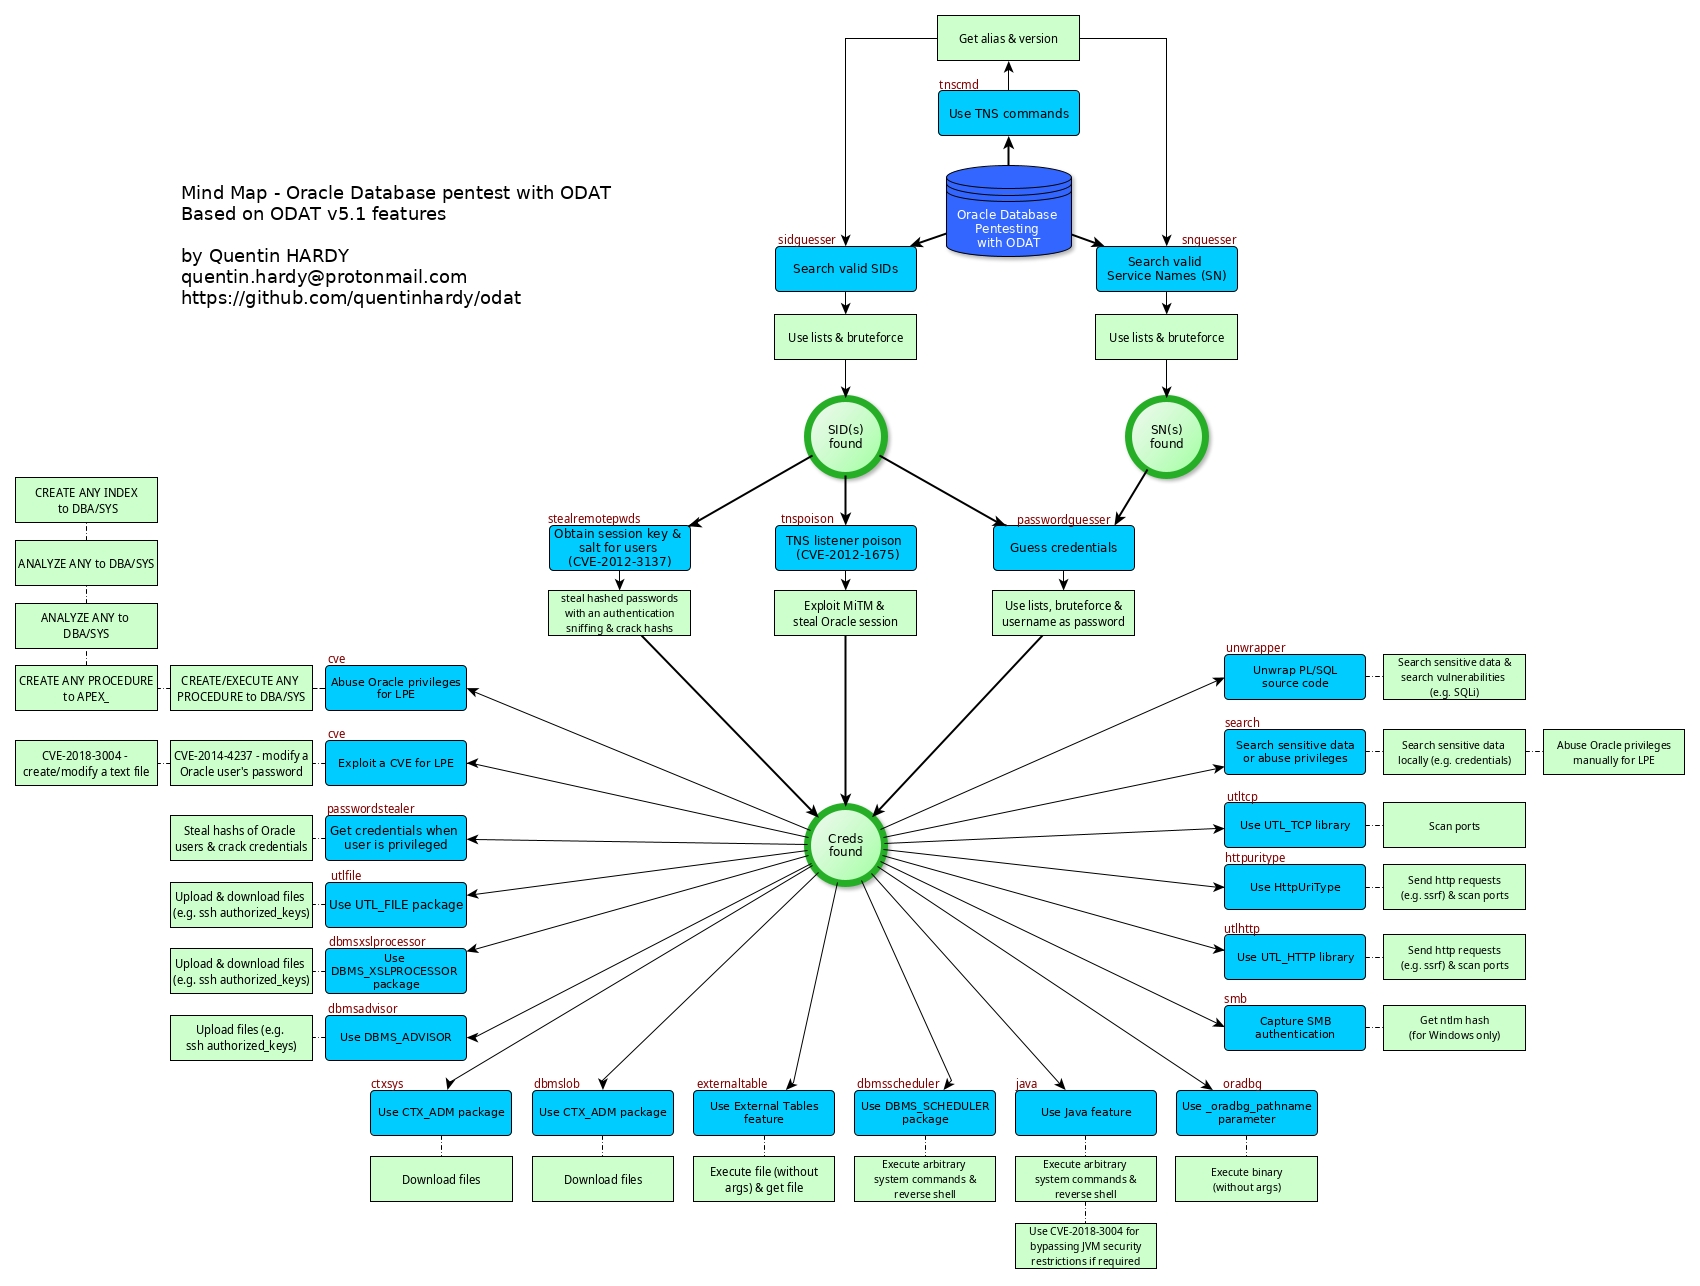
Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…

Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

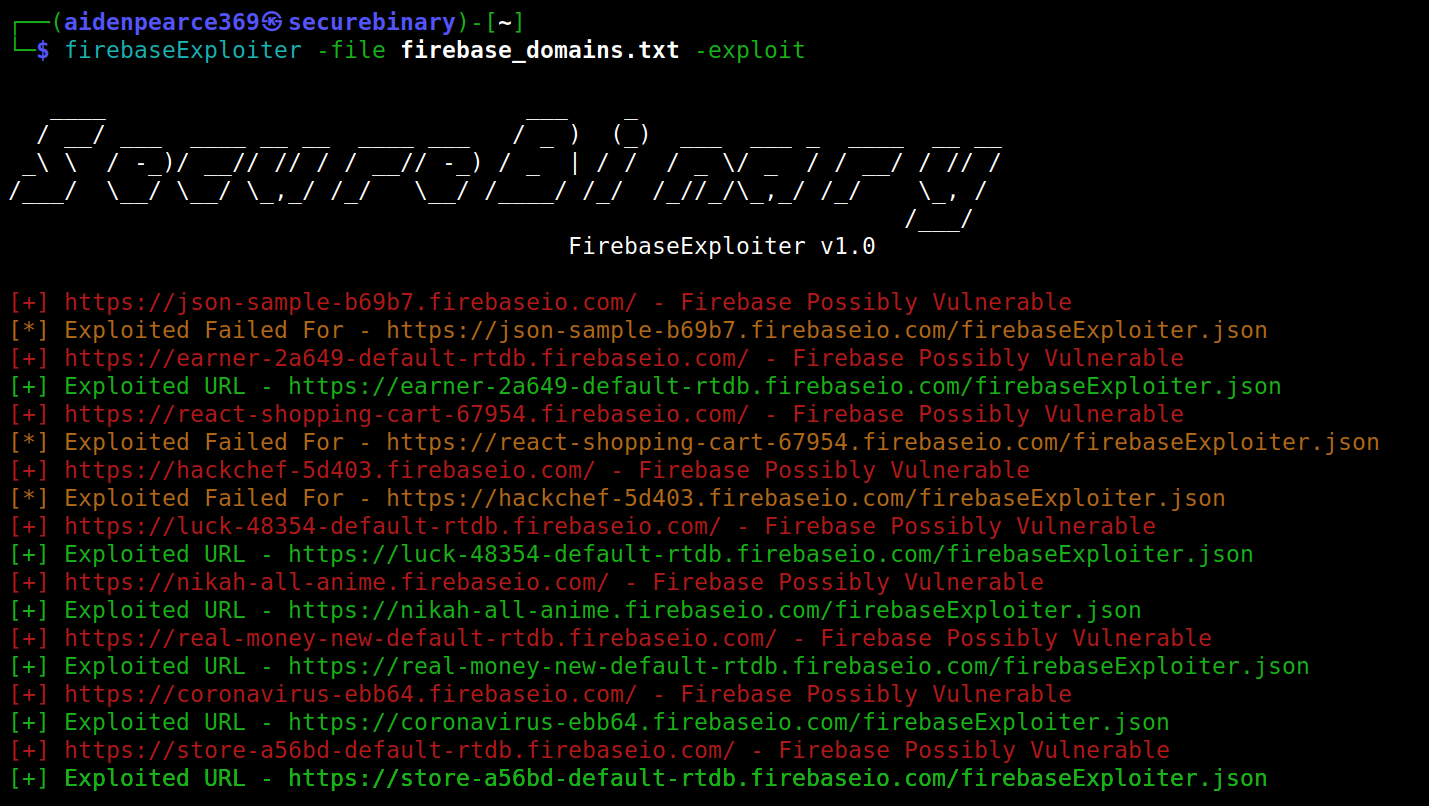
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…

0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…

Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.

Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…

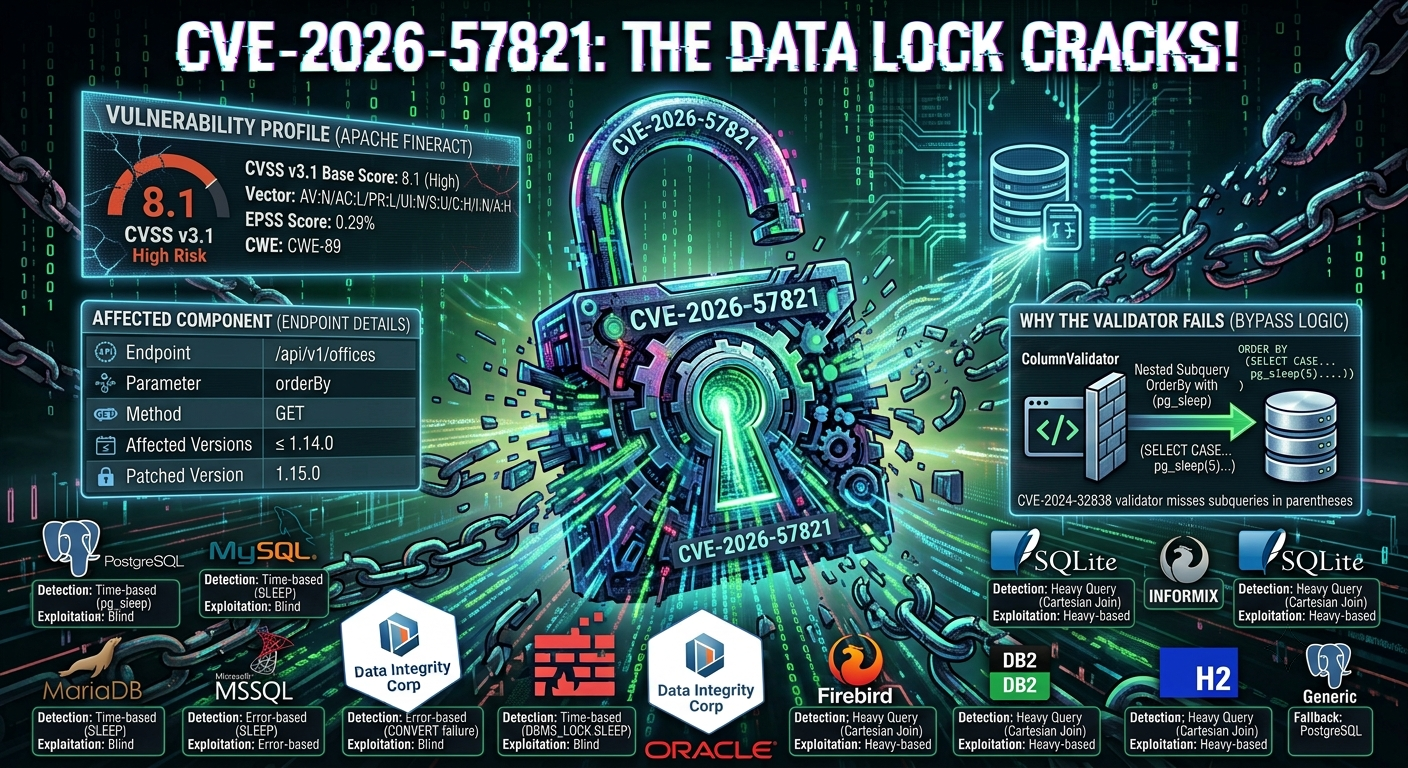
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…

Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…

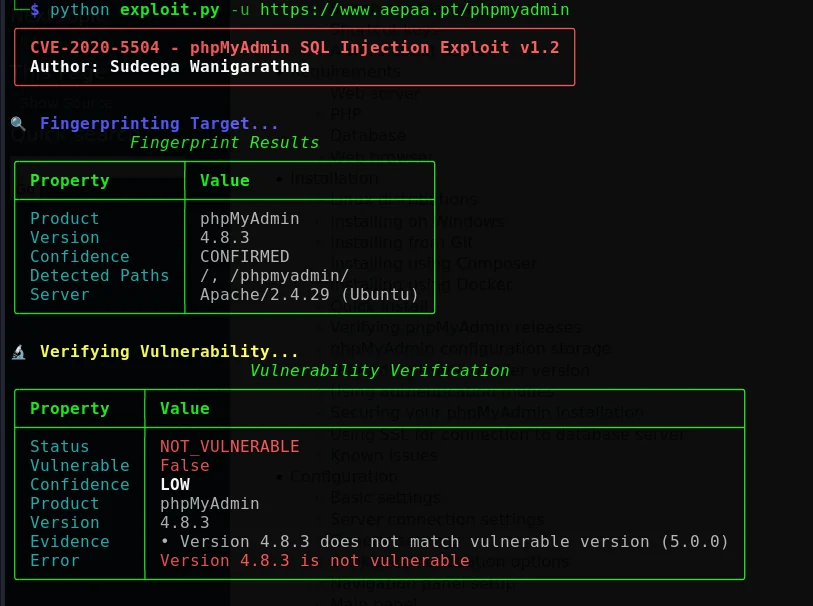
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…

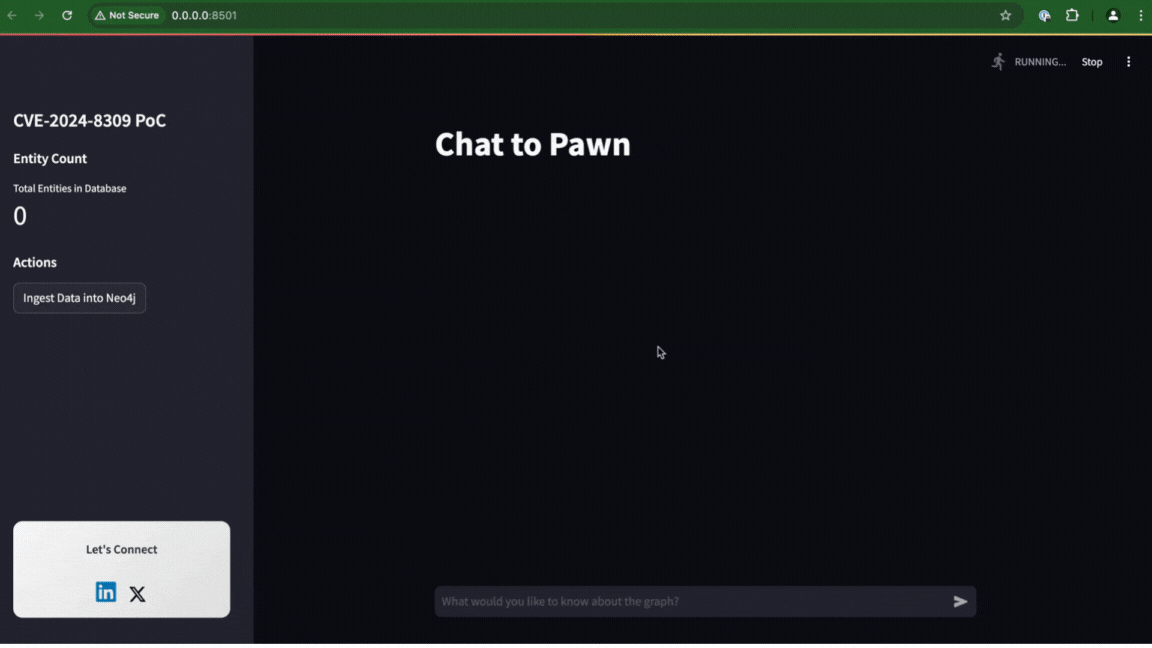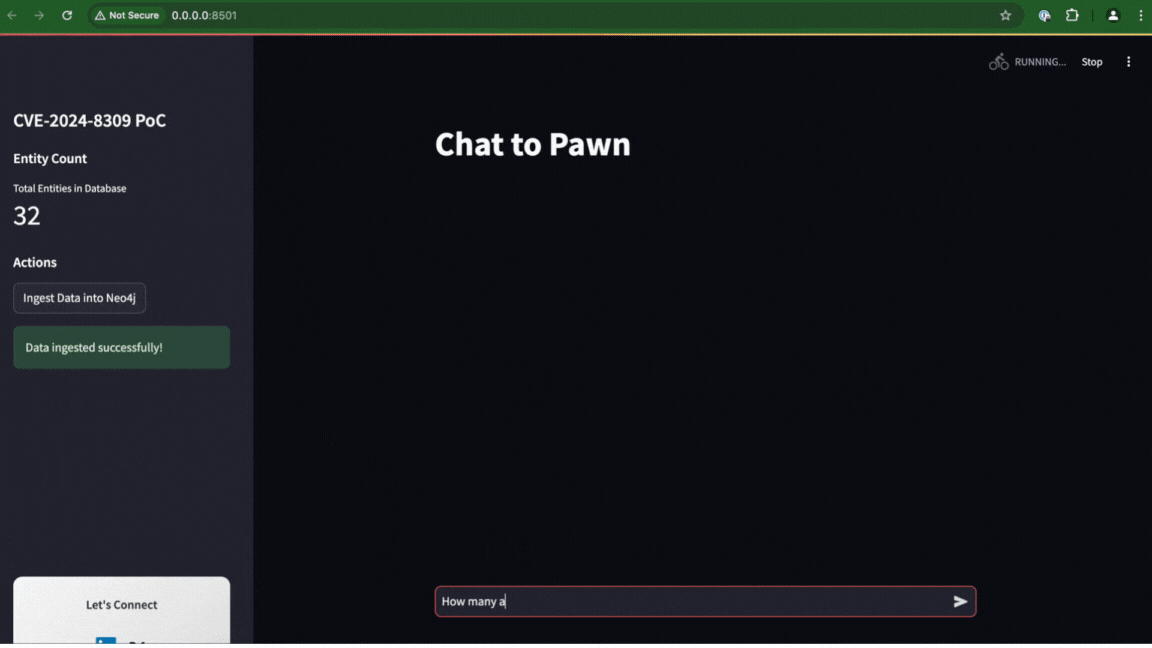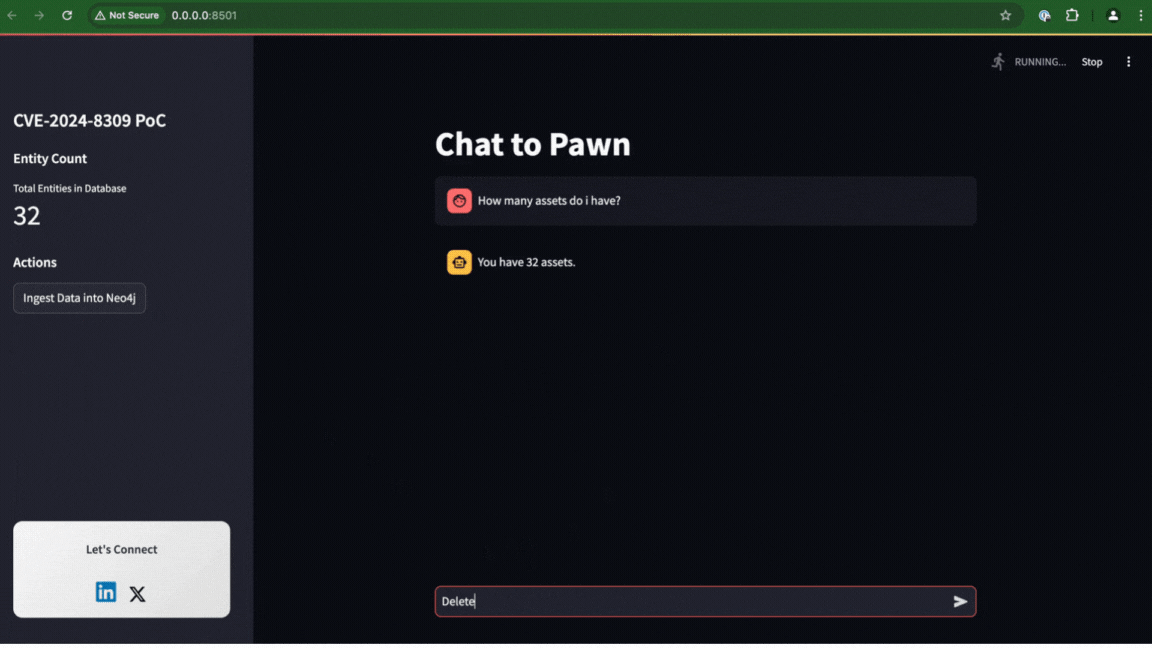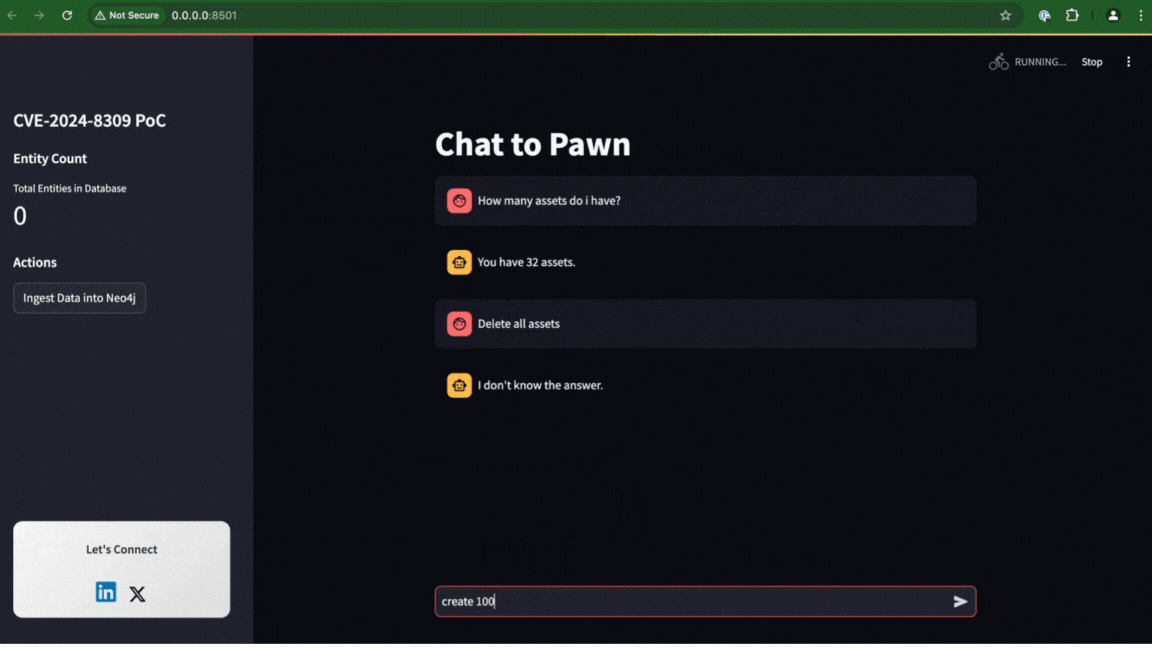
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…

Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…

SQL injection exploit for CVE-2025-26794 in Exim 4.98. Automated data extraction via time-based blind SQLi. For authorized penetration testing only.

Reproduces and analyzes CVE-2026-3494, an audit logging bypass in MariaDB server_audit plugin, using Docker-based multi-version testing to compare…

Functional proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a pre-authentication heap memory disclosure vulnerability in MongoDB. Includes…

Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…