

strutszeiro
 btamburi/strutszeiro
Telegram Bot to manage botnets created with struts vulnerability(CVE-2017-5638)
command-and-controlexploitationremote-access-tool+2
btamburi/strutszeiroTelegram Bot to manage botnets created with struts vulnerability(CVE-2017-5638)
 randomrobbiebf/cve-2024-9821
Bot for Telegram on WooCommerce <= 1.2.4 - Authenticated (Subscriber+) Telegram Bot Token Disclosure to Authentication Bypass
 thewhiteevil/cve-2025-51396
LiveHelperChat <=4.61 - Stored Cross Site Scripting (XSS) via Telegram Bot Username
 zeyad-azima/cve-2023-26818
CVE-2023-26818 Exploit MacOS TCC Bypass W/ Telegram
 bytereaper77/cve-2025-7753
PoC Exploit for CVE-2025-7753 — Time-Based SQL Injection in Online Appointment Booking System 1.0 via the username parameter. Exploit written in C…
 bibi1959/cve-2019-15514
telegram bug that discloses user's hidden phone number (still unpatched) (exploit included)
 dennisec/cve-2026-41940
Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 phamchie/cve-2023-3047
Proof-of-concept exploit for CVE-2023-3047 SQL injection vulnerability in TMT Lockcell. Demonstrates manual exploitation using cURL and Burp Suite to…
 cyberok-org/cve-2025-67887
Detailed analysis and PoC for CVE-2025-67887/86 RCE in 1C-Bitrix Translate module, including exploit chain, CVSS scoring, and mitigation…
 bytereaper77/cve-2025-7795
Proof-of-concept exploit for a buffer overflow vulnerability in Tenda routers. Sends crafted unauthenticated POST requests to trigger a crash and…
 bytereaper77/cve-2025-32429
Exploit for CVE-2025-32429 – SQLi in XWiki REST API (getdeleteddocuments.vm).
 0axz-tools/cve-2023-28121
Automated vulnerability scanner for CVE-2023-28121 that checks a list of targets concurrently and delivers results via Telegram notifications.
 sahalll/cve-2024-54916
Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…
 kartheeklade/canalyse
A vehicle network analysis and attack tool.
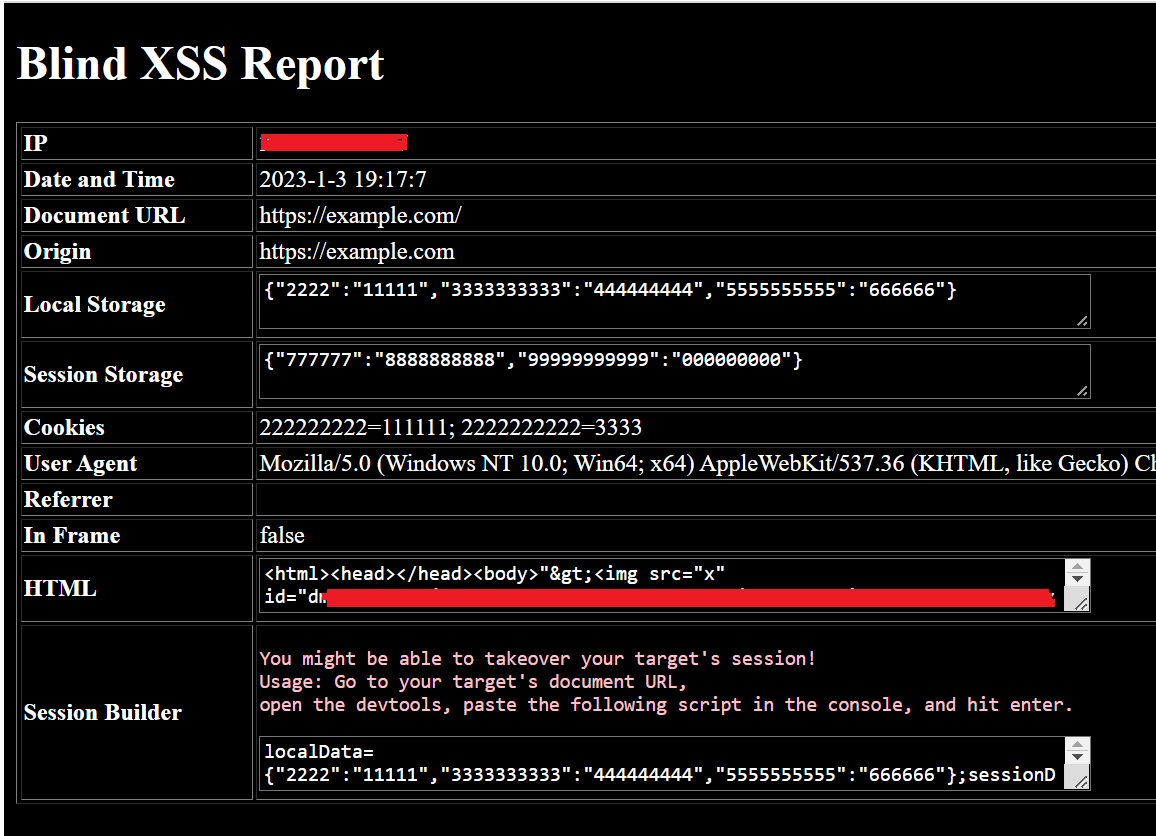 seifelsallamy/xssfire
A standalone Blind XSS Script.
 nxploited/cve-2025-11749
AI Engine <= 3.1.3 - Unauthenticated Sensitive Information Exposure to Privilege Escalation