
CVE-2023-45182
 afine-com/cve-2023-45182
IBM i Access Client Solutions < 1.1.9.4 - Weak password encryption
cryptographyencryption-decryption-toolsexploitation+2
afine-com/cve-2023-45182IBM i Access Client Solutions < 1.1.9.4 - Weak password encryption
 schwankner/cve-2005-2428-ibm-lotus-domino-r8-password-hash-extraction-exploit
IBM Lotus Domino <= R8 Password Hash Extraction Exploit
 copethomas/datapower-redis-rce-exploit
A POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)
 silentsignal/cve-2023-30990
CVE-2023-30990 exploits
 defrancescojp/cve-2013-2977
Proof-of-concept exploit for CVE-2013-2977: IBM Lotus Notes PNG integer overflow leading to arbitrary code execution when a malicious email is opened…
 ywh-jfellus/cve-2026-9198
Proof of Concept for CVE-2026-9198 - IBM Langflow Unauthenticated RCE via Auto-Login Bypass
 procjevt/cve-2026-9198
Exploit script for CVE-2026-9198 targeting IBM Langflow, providing proof-of-concept code to validate vulnerabilities and support authorized security…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 voidsec/tivoli-madness
Advisory for CVE-2020-28054 & stack based buffer overflow in IBM Tivoli Storage Manager
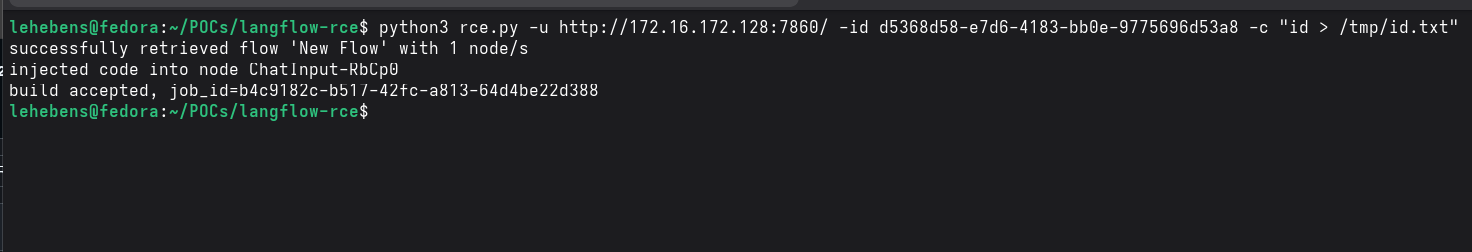 lukehebe/ibm-langflow-cve-2026-48519-poc
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.
 emcalv/tivoli-poc
Proof-of-concept exploit for CVE-2017-1635, a use-after-free vulnerability in IBM Tivoli Monitoring's KDH web server component enabling remote code…
 joaovicdev/exploit-cve-2026-9198
Proof-of-concept exploit for CVE-2026-9198, an unauthenticated RCE in IBM Langflow OSS, chaining auto_login and validate/code endpoints. Includes a…
 bytereaper77/cve-2025-36041
Exploit (C) of the CVE-2025-36041 vulnerability in IBM MQ
 mayaofveil/cve-2015-1986
Exploit PoC for Buffer overflow vulnerability in the server in IBM Tivoli Storage Manager FastBack 5.5.x and 6.x before 6.1.12.2 (tested in version…
 reverseclabs/ibm-sterling-b2b-integrator-poc
PoC code for the LPE and RCE (CVE-2024-31903) attacks against the IBM Sterling B2B Integrator
 watchtowrlabs/ibm-qradar-ajp_smuggling_cve-2022-26377_poc
Proof-of-concept exploit for CVE-2022-26377, an AJP smuggling vulnerability that poisons the HTTP response queue of IBM QRadar with a stored redirect.
 chessalekin/cve-2026-9198_exploit
Exploit for CVE-2026-9198, containing proof-of-concept payloads and validation steps for assessing the vulnerability in target environments.
 0xdak/cve-2026-9198_exploit
Unauthenticated RCE exploit for Langflow OSS chaining auto_login JWT bypass with validate/code exec() to achieve remote command execution and reverse…