
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
310 results
KsDumper preview

KsDumper

GitHubequifox/ksdumper

Dumping processes using the power of kernel space !
binary-analysiseducationexploitation+2
1.1k3 years ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
2225 days ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
exploitationmemory-forensicspayload-development+2
3.4k4 years ago
herpaderping preview

herpaderping

GitHubjxy-s/herpaderping

Process Herpaderping proof of concept, tool, and technical deep dive. Process Herpaderping bypasses security products by obscuring the intentions of…
defensive-toolsexploitationpenetration-testing
1.2k3 years ago
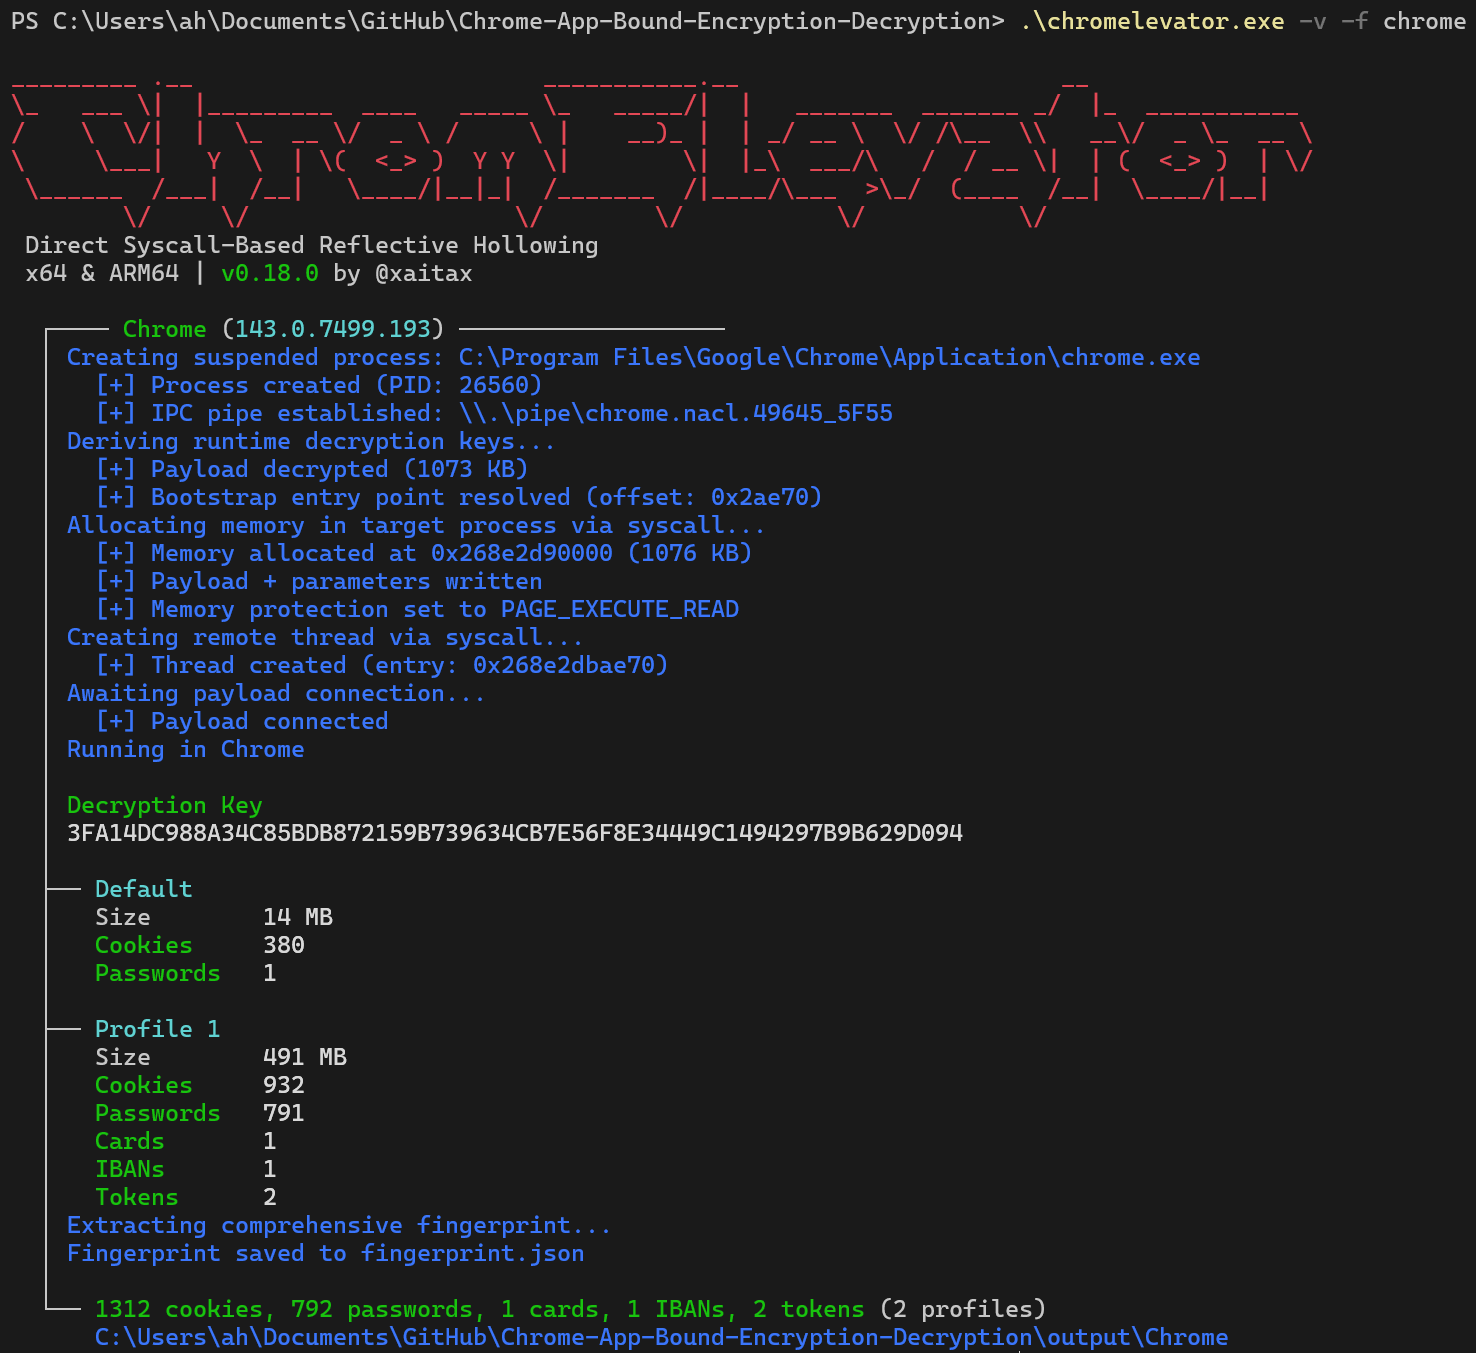
Chrome-App-Bound-Encryption-Decryption preview

Chrome-App-Bound-Encryption-Decryption

GitHubxaitax/chrome-app-bound-encryption-decryption

Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
cryptographydata-exfiltrationencryption-decryption-tools+5
1.8k7 months ago
ProcessInjection preview

ProcessInjection

GitHub3xpl01tc0d3r/processinjection

This program is designed to demonstrate various process injection techniques
binary-exploitationeducationencryption-decryption-tools+5
1.3k1 year ago
ShellGhost preview

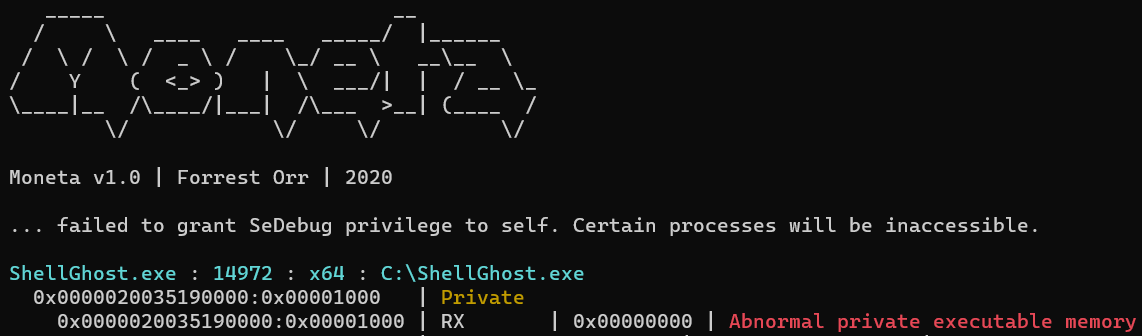
ShellGhost

GitHublem0nsec/shellghost

A memory-based evasion technique which makes shellcode invisible from process start to end.

binary-analysisencryption-decryption-toolsexploitation+4
1.2k2 years ago
pinjectra preview

pinjectra

GitHubsafebreach-labs/pinjectra

Pinjectra is a C/C++ OOP-like library that implements Process Injection techniques (with focus on Windows 10 64-bit)

binary-exploitationexploitationred-teaming
8267 years ago
DarkWidow preview

DarkWidow

GitHubreveng007/darkwidow

Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…

binary-analysiseducationexploitation+6
8098 months ago
dlinject preview

dlinject

GitHubdavidbuchanan314/dlinject

Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
exploitationred-teamingshellcode
8301 year ago
PoolParty preview

PoolParty

GitHubsafebreach-labs/poolparty

A set of fully-undetectable process injection techniques abusing Windows Thread Pools
exploitationpayload-developmentpost-exploitation+3
1.3k2 years ago
kasld preview

kasld

GitHubbcoles/kasld

KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
binary-exploitationctfexploitation+3
55420h 7m ago
EDR-Freeze preview

EDR-Freeze

GitHubtwosevenonet/edr-freeze

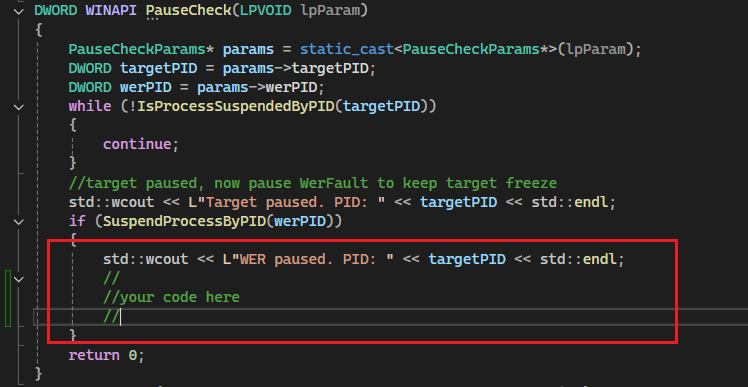
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.

exploitationids-ips-evasionpost-exploitation+1
8734 months ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
5995 years ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
binary-exploitationexploitationpersistence-mechanisms+2
5555 years ago
Windows_LPE_AFD_CVE-2023-21768 preview

Windows_LPE_AFD_CVE-2023-21768

GitHubchompie1337/windows_lpe_afd_cve-2023-21768

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
binary-exploitationexploitationpayload-development+3
5063 years ago
Crassus preview

Crassus

GitHubvu-ls/crassus

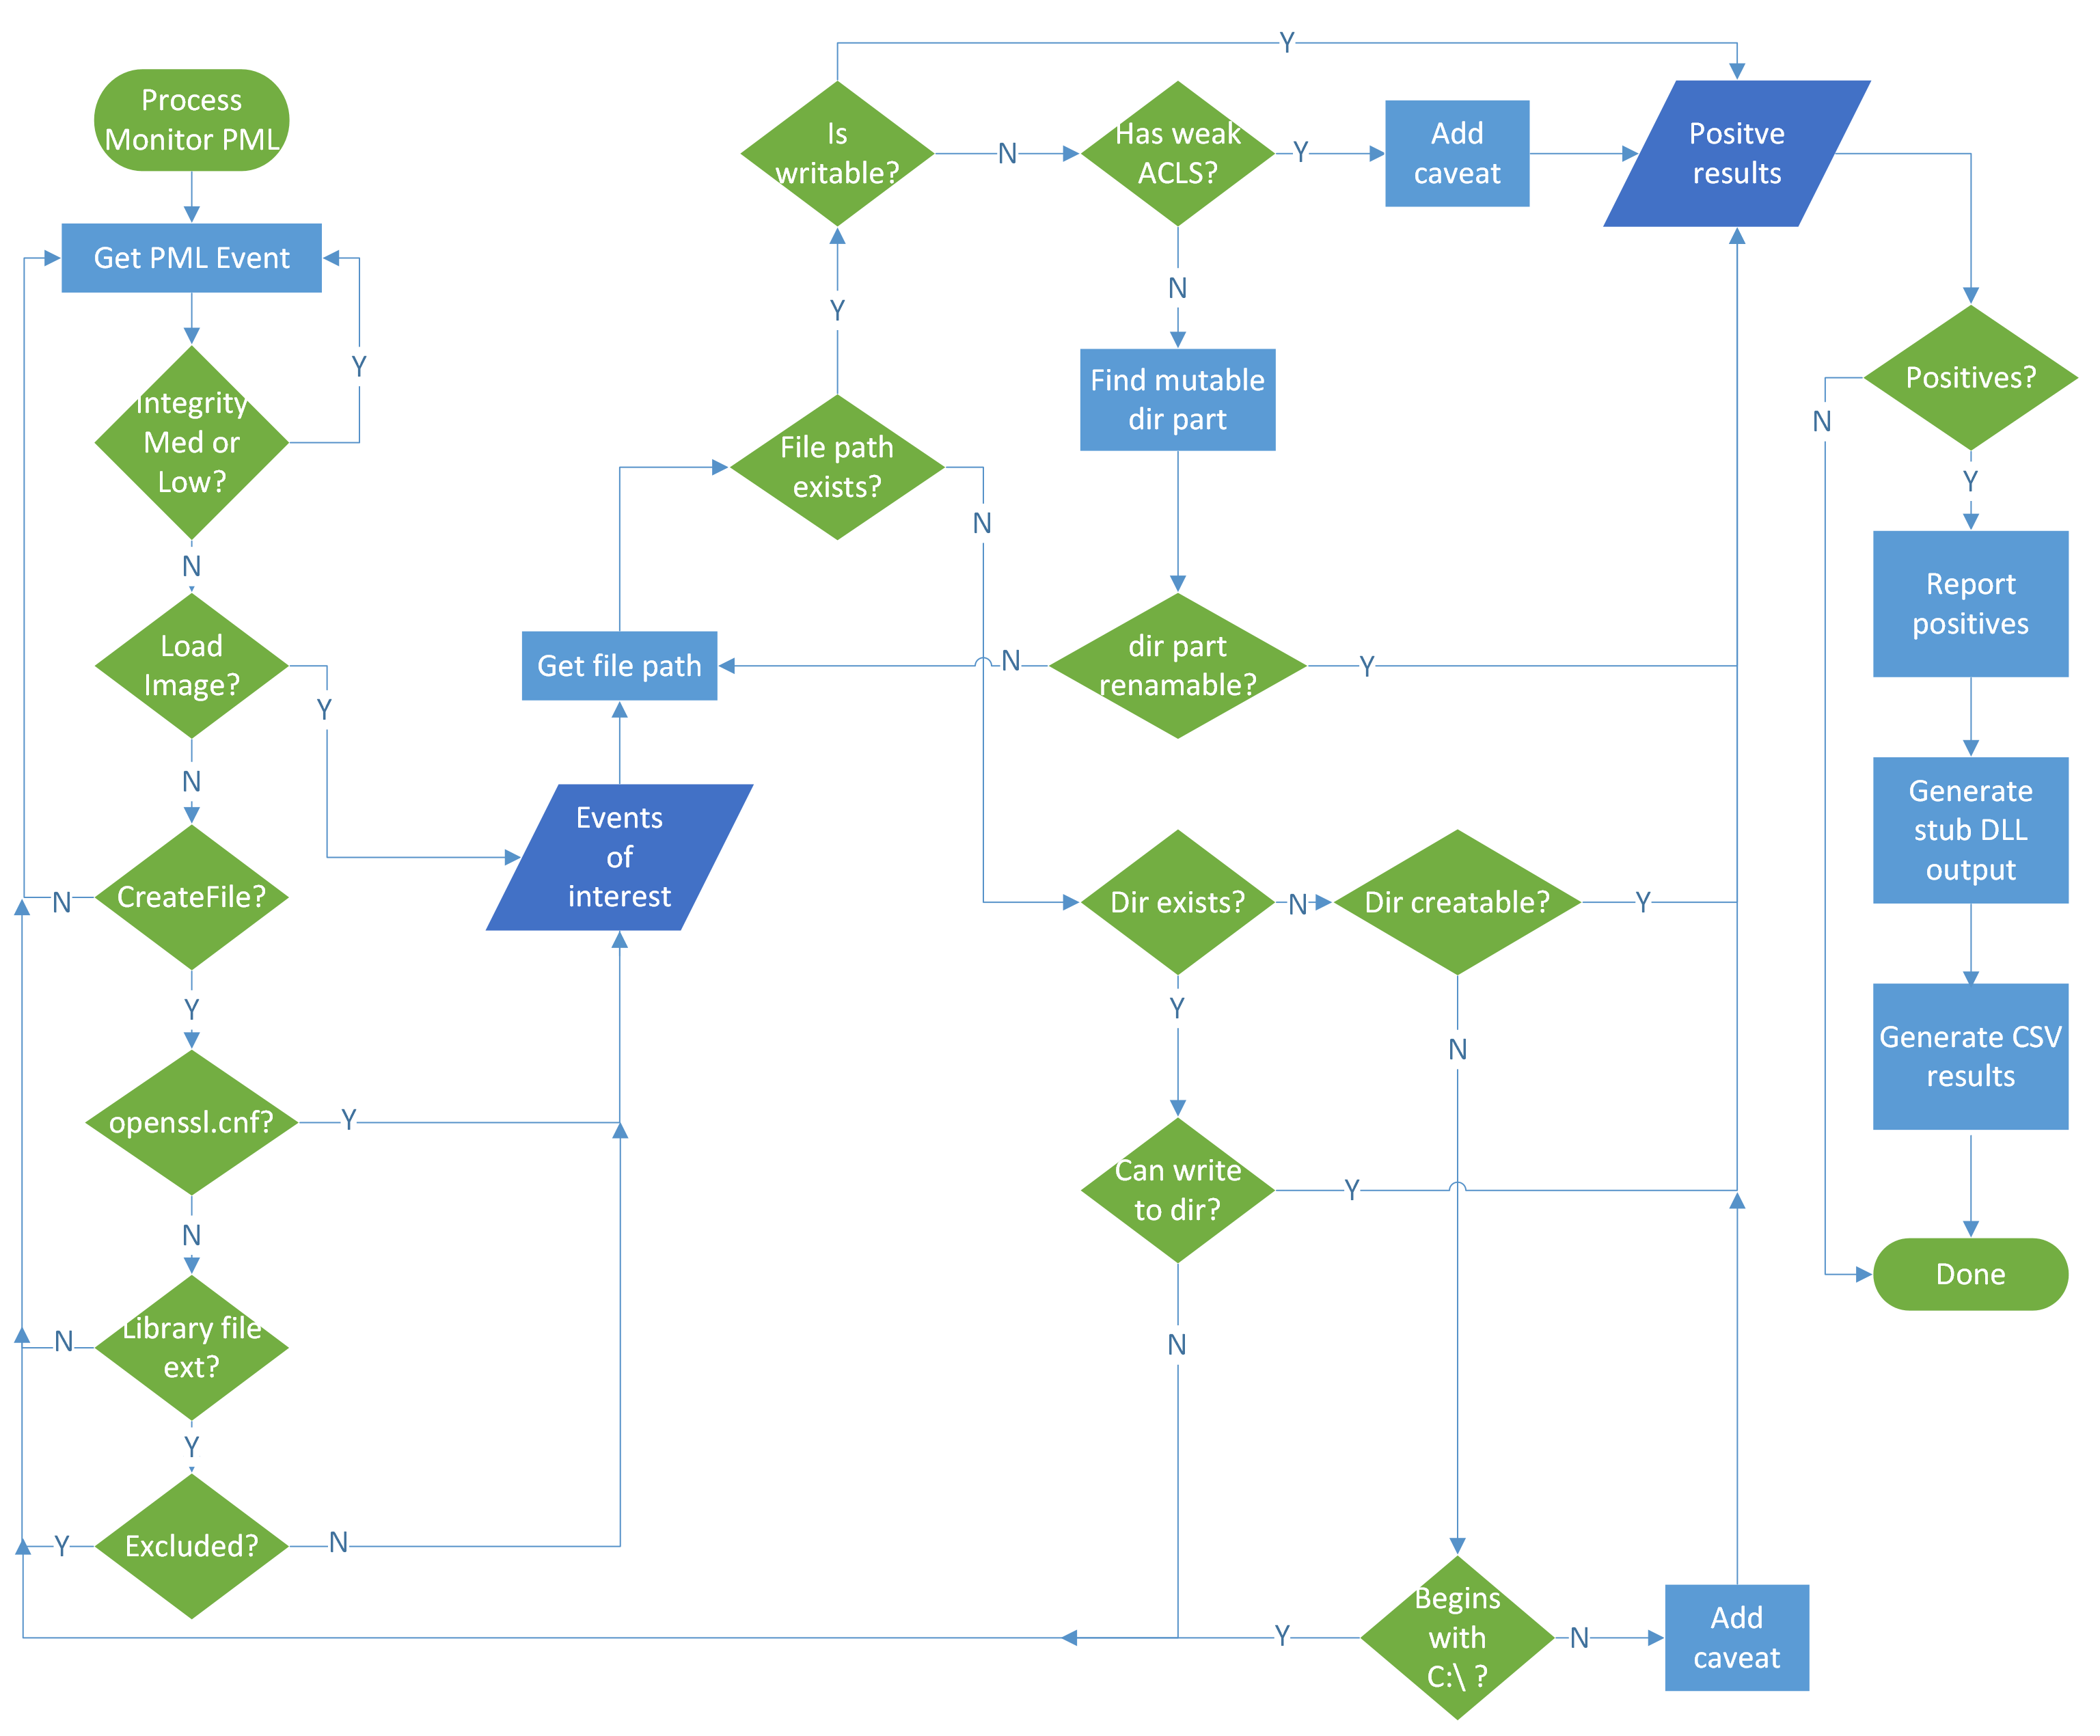
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
6318 months ago
WinDefenderKiller preview

WinDefenderKiller

GitHubs12cybersecurity/windefenderkiller

Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)

adversarial-attackexploitationids-ips-evasion+3
5606 months ago
Previous12…18Next