Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
330 results
metasploitavevasion preview

metasploitavevasion

GitHubnccgroup/metasploitavevasion

Metasploit AV Evasion Tool

command-and-controlexploitationids-ips-evasion+4
256
10 years ago
CVE-2017-0199 preview

CVE-2017-0199

GitHubexploit-install/cve-2017-0199

Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…

command-and-controlexploitationpayload-development+3
79 years ago
CVE-2017-7494_SambaCry preview

CVE-2017-7494_SambaCry

GitHubd3fudd/cve-2017-7494_sambacry

SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit
exploitationpayload-developmentpenetration-testing+3
73 years ago
SharpZipRunner preview

SharpZipRunner

GitHubjfmaes/sharpziprunner

Executes position independent shellcode from an encrypted zip
exploitationpayload-developmentpayload-generation+3
3035 years ago
CVE-2019-8943 preview

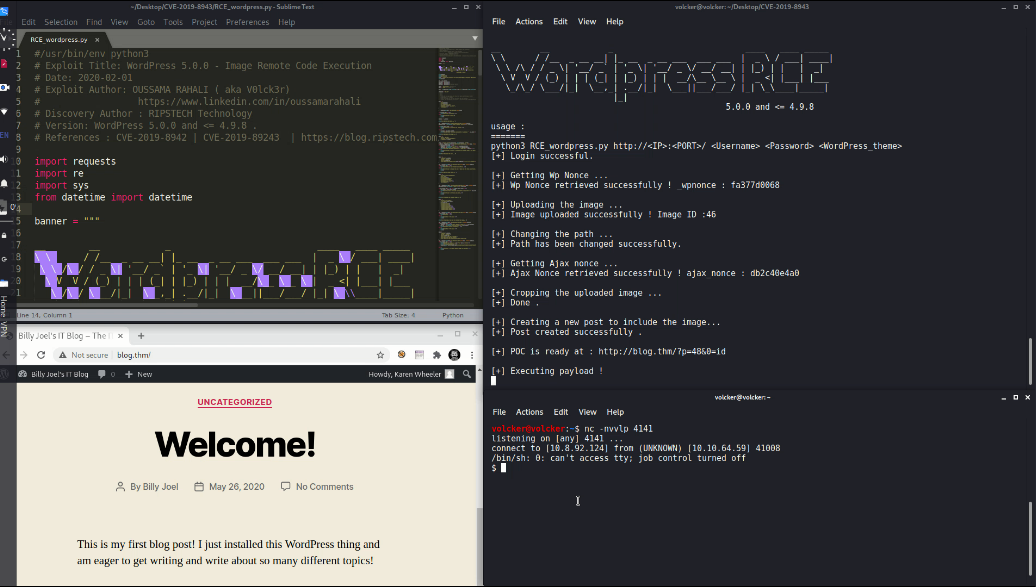
CVE-2019-8943

GitHuboussama-rahali/cve-2019-8943

Exploit of CVE-2019-8942 and CVE-2019-8943

exploitationpayload-developmentpenetration-testing+3
245 years ago
GhostDriver preview

GhostDriver

GitHubblacksnufkin/ghostdriver

yet another AV killer tool using BYOVD
defensive-toolsexploitationids-ips-evasion+4
3142 years ago
PolyEngine preview

PolyEngine

GitHublongwayhomie/polyengine

PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…

anti-botbinary-analysisctf+6
1631 month ago
Shellcode-Injection-Techniques preview

Shellcode-Injection-Techniques

GitHubplackyhacker/shellcode-injection-techniques

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
exploitationpost-exploitationred-teaming+1
4654 years ago
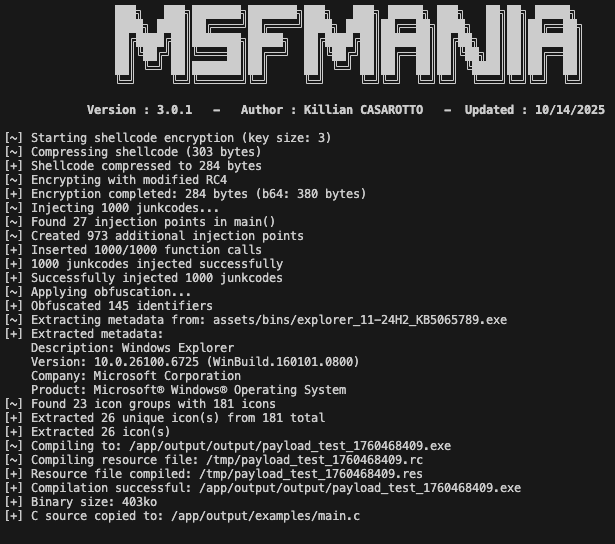
MsfMania preview

MsfMania

GitHublepotekil/msfmania

Python AV Evasion Tools
binary-analysiseducationencryption-decryption-tools+9
51711 months ago
PhantomCtx preview

PhantomCtx

GitHubr3xmax/phantomctx

Activation Context Hijacking Evasion Tool
binary-exploitationexploitationpayload-development+3
3053 months ago
Fritter preview

Fritter

GitHub0xrootpls/fritter

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

binary-exploitationexploitationpayload-development+5
2531 month ago
PE-Obfuscator preview

PE-Obfuscator

GitHubsaadahla/pe-obfuscator

PE obfuscator with Evasion in mind

adversarial-attackexploitationpayload-development+2
2113 years ago
elfpack preview

elfpack

GitHubdsnezhkov/elfpack

ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
binary-analysisexploitationmalware-analysis+4
514 years ago
AVBypass preview

AVBypass

GitHubkira2040k/avbypass

golang script for bypass AV and work only in windows platform
command-and-controlexploitationpayload-development+4
275 years ago
CS-MemoryEvasion preview

CS-MemoryEvasion

GitHubgmh5225/cs-memoryevasion

A Cobalt Strike memory evasion loader for redteamers
exploitationmalware-analysispayload-development+2
13 years ago
talkingBen preview

talkingBen

GitHubm4rm0k/talkingben

UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
command-and-controlexploitationmalware-analysis+4
10 months ago
ImgBackdoor preview

ImgBackdoor

GitHubtsuyoken/imgbackdoor

Hide your payload into .jpg file

command-and-controlexploitationpayload-development+3
3934 years ago
0xM0nCrush preview

0xM0nCrush

GitHubdeathshotxd/0xm0ncrush

Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.

defensive-toolsexploitationpayload-development+4
7714 days ago
Previous12…19Next