
CVE-2026-30048
 0xn4no/cve-2026-30048
Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
exploitationpapers-researchvulnerability-analysis+2
0xn4no/cve-2026-30048Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
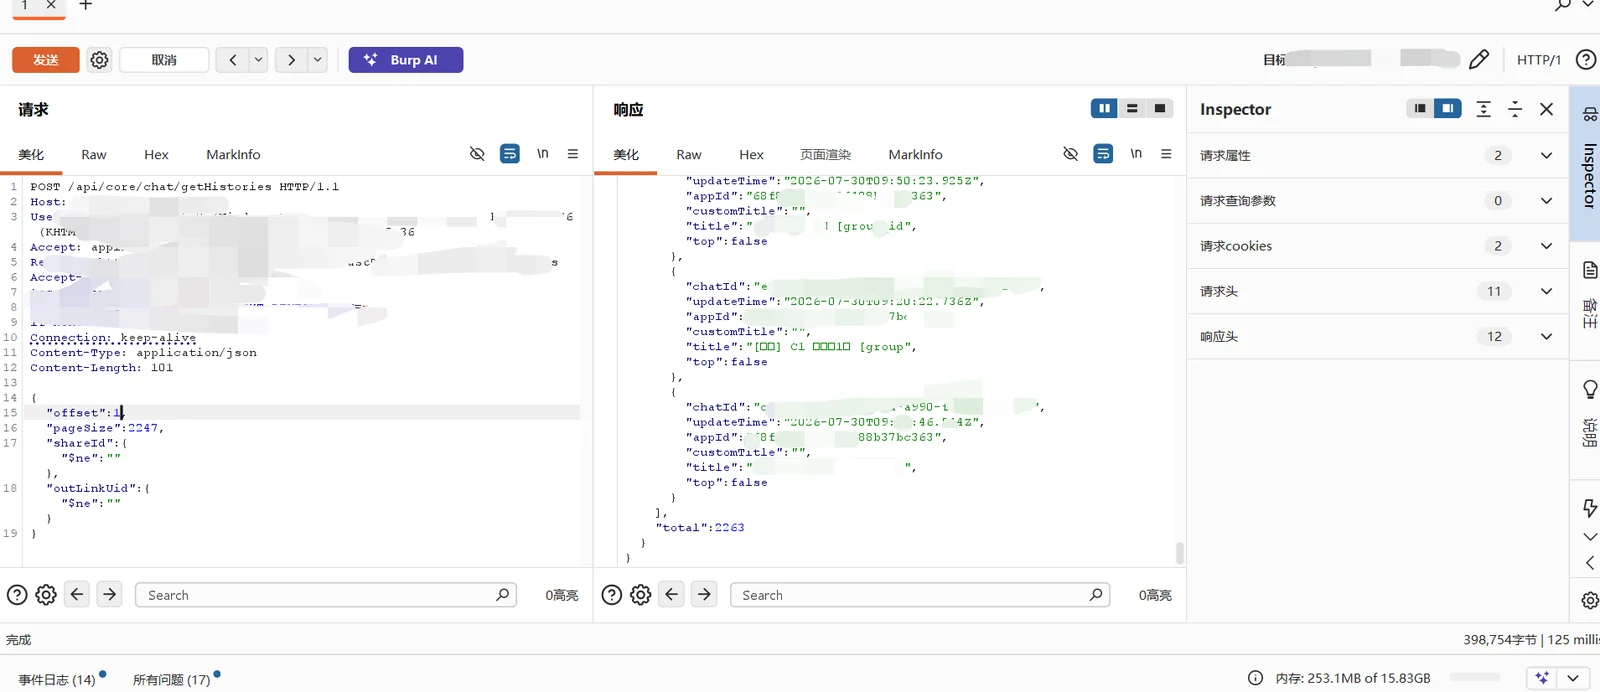 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
 secsys-fdu/cve-2025-51860
Detailed analysis of a Stored XSS vulnerability in TelegAI, including attack vectors, impact, and proof-of-concept for session token theft and…
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 csenox/cve-2021-22911
Pre-Auth Blind NoSQL Injection leading to Remote Code Execution in Rocket Chat 3.12.1
 emirpolatt/cve-2022-31188
Proof-of-concept exploit for CVE-2022-31188, an SSRF vulnerability in OpenCV CVAT that allows authenticated users with Task Create permissions to…
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
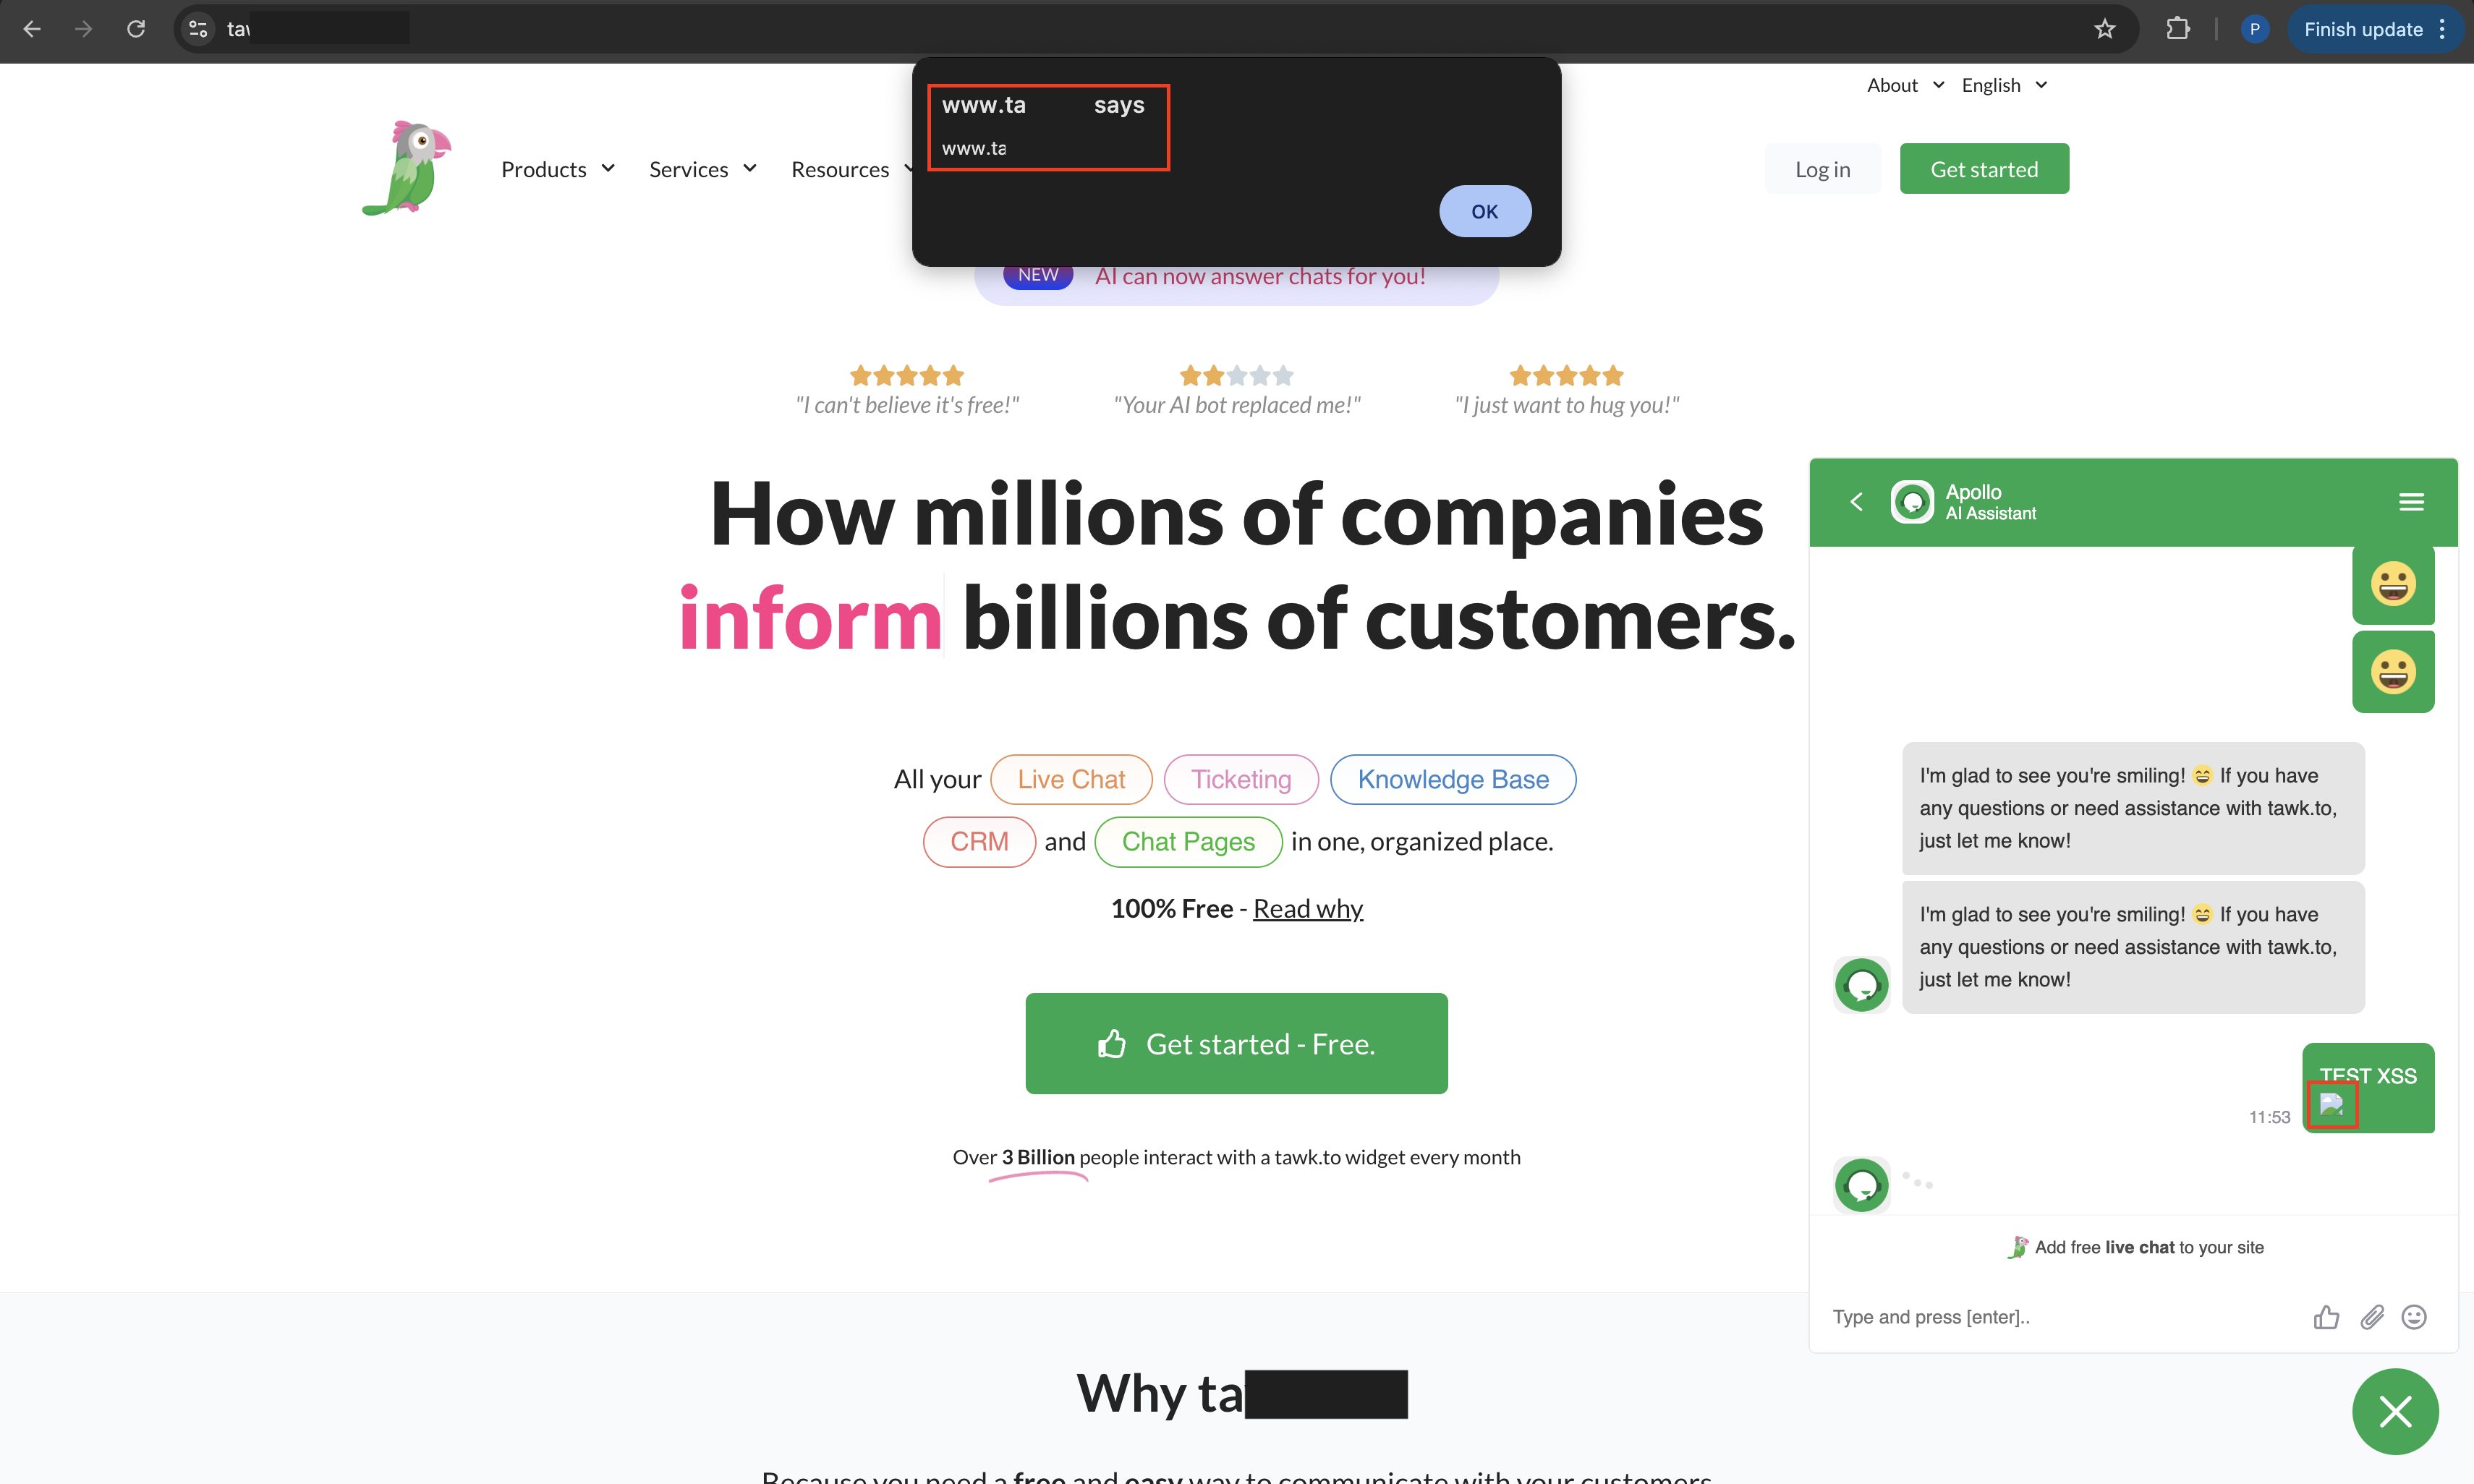 pracharapol/cve-2025-45960
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in tawk.to Live Chat 1.6.1, demonstrating JavaScript injection via unsanitized…
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 rudsarkar/cve-2026-42228
Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…
 nullbyte8080/cve-2026-36228
Proof-of-concept for CVE-2026-36228 demonstrating a denial-of-service vulnerability in Easy Chat Server 3.1 via oversized mtowho parameter. Dry-run…
 nullbyte8080/cve-2026-36227
Benign proof-of-concept for CVE-2026-36227, a path traversal vulnerability in Easy Chat Server 3.1 user registration. Demonstrates unauthorized file…
 secsys-fdu/cve-2025-51858
Documentation of CVE-2025-51858, a self-XSS vulnerability in ChatPlayground.ai enabling JWT theft and account hijacking, combined with an IDOR in…
 thewhiteevil/cve-2025-51401
LiveHelperChat <=4.61 - Stored Cross Site Scripting (XSS) via Operator Chat Name Field Triggers on Chat Owner Transfer
 secsys-fdu/cve-2025-51862
Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…
 jainil-89/cve
Xss In Tawk.to Live Chat Support (CVE-2025-57483)
 secsys-fdu/cve-2025-51859
Proof-of-concept demonstrating stored XSS and IDOR in Chaindesk AI agent chat, enabling session token theft and account hijacking.